Fertility App Sued Over Non-Consensual Data Sharing
Fertility App Sued Over Non-Consensual Data Sharing

The Illinois company behind a popular fertility app is being sued for allegedly sharing user data with third-party companies without first securing users’ consent. 

Easy Healthcare Corp, based in Burr Ridge, is the developer of ovulation tracking app Premom, which helps users to identify the days on which they are most likely to conceive. 

lawsuit filed against the company alleges that a variety of sensitive data belonging to app users was shared non-consensually with at least three different firms located in the People’s Republic of China (PRC).

Information allegedly shared includes sensitive healthcare information, device activity data, geolocation data, user and advertiser IDs, and device hardware identifiers. 

Among the identifiers allegedly shared were Wi-Fi media access controls or MAC addresses, router MAC/BSSID addresses, and router SSID (Service Set IDs). Because the identifiers do not change, they can be combined with other data to gather information on app users’ religion, health, political views, interests, and other sensitive data. 

The plaintiff bringing the suit said she discovered that Easy Healthcare Corp had shared her data with Jiguang (Aurora Mobile Ltd), Umeng, and UMSNS, an activity analysis, precision marketing, financial risk control, and location-based analysis services provider. 

According to the suit, the plaintiff’s data was shared with the Chinese companies for three years without her knowledge or consent and is now stored on servers in China, where it is at risk of being seized by the Chinese government.

It is further alleged that Easy Healthcare profited from sharing the data with the Chinese firms and that the company misrepresented its data-sharing practices. 

According to the lawsuit, the Premom privacy policy states, “We will not share or sell your personal data to advertising platforms, data brokers, or information resellers,” so sharing such data would be a direct policy violation.

The plaintiff also claims that user data is recorded every time Premom users unlock or use their phone, regardless of whether they are using the Premom app. If true, this violates Google Play’s developer policies.

An attorney representing Easy Healthcare told Information Security Media Group: “The allegations are without merit, and Easy Healthcare is confident it will prevail.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Fraudsters Ramped Up Account Takeover Attacks in 2020

Fraudsters Ramped Up Account Takeover Attacks in 2020

Account takeover incidents as a share of fraudulent activity in the financial services industry rose by 19 percentage points in 2020 compared with 2019, according to new figures from Kaspersky.

Kaspersky Fraud Prevention detected that attacks of this nature surged from 34% in 2019 to 54% in 2020 of all incidents. The cybersecurity firm believes the growing use of digital financial services and e-commerce last year as a result of COVID-19 social distancing restrictions is behind this shift, with cyber-criminals able to target a much higher number of users and online accounts through social engineering attacks.

The researchers noted there were two particularly common tactics used by cyber-villains to gain access to accounts – known as ‘the rescuer’ and ‘the investor.’ In the first, scammers pose as security experts and call customers to report suspicious charges or payments and offer their help. Customers may then be asked to verify their identity through a code sent in a text message or push notification to stop a suspicious transaction or transfer money to a ‘secure account.’

In the second, cyber-criminals masquerade as an investor, calling customers to persuade them to invest in cryptocurrency or shares directly from the client’s account. As with ‘the rescuer,’ the victim will then be asked for a code received in a text message or push notification.

The study also revealed that legitimate remote administration tools (RAT), such as TeamViewer, were misused in order to gain access in 12% of fraudulent incidents.

Claire Hatcher, head of business development at Kaspersky Fraud Prevention, commented: “Bank clients always place a high value on ease of access to their accounts and performance of usual financial operations. Now this has become especially important. That is why we believe that solutions for the financial industry should provide a high level of security measures – including protection against fraud – which are seamlessly integrated into the user experience. Of course, it’s worth regularly reminding clients about fraudsters’ techniques, so that they are likely to notice something.”

Yesterday, Barclays released data showing that the number of scams last year reached unprecedented levels.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
OBIE Launches Free Tool to Fight Open Banking Fraud

OBIE Launches Free Tool to Fight Open Banking Fraud

The Open Banking Implementation Entity (OBIE) has launched a new online tool to help firms prevent and fight open banking fraud.

The Counter-Fraud Maturity Self-Assessment tool has been collaboratively developed by the OBIE Security & Fraud Working Group, Accenture, Cifas, the University of Portsmouth Center for Counter Fraud Studies and the Cabinet Office Fraud, Error and Debt Team.

The tool, freely available to all firms enrolled in the OBIE Directory, enables open banking companies to assess the maturity of their fraud defenses and seeks to further strengthen the resilience of the open banking ecosystem.

Key benefits of the tool outlined by the OBIE include:

  • A point-in-time visual snapshot of a firms’ fraud control maturity
  • The identification of areas of potential risk that may not have previously been considered
  • Users can track the evolving maturity of their counter-fraud defenses

Bronwyn Boyle, head of security and counter-fraud at the OBIE, said: “Security is at the heart of open banking, which allows more than 2.5 million active users each month to safely and securely use their financial data to access better deals. As open banking adoption continues to grow and the technology becomes part of our daily lives, it is more important than ever that firms take steps to maintain the integrity of their fraud controls.”

The OBIE Counter-Fraud Maturity Self-Assessment tool supports firms within the OBIE ecosystem in taking proactive, preventative steps to protect their businesses and their customers, she added.

“By gaining a better awareness of their own risk profiles, firms can feel confident that they have robust counter-fraud controls in place.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Data on Thousands of Foxtons Customers Posted Online

Data on Thousands of Foxtons Customers Posted Online

Estate agent Foxtons Group is under pressure after a daily newspaper claimed that thousands of customers’ card and personal details have been uploaded to a dark web site.

A customer found over 16,000 card details, addresses and private messages on October 12 last year, according to publication i.

The report claimed that the data relates to customers from before 2010, although testing of a small sample apparently revealed that around a fifth of the cards are still active.

Only a small percentage of personal data is said to have been published on the dark web, but it’s unclear exactly how many customers have been affected. Cyber-criminals often showcase their haul to would-be buyers by publishing a small sample online, before selling privately.

According to the report, the publicly available files have been viewed over 15,000 times in the three months or so they have been online.

The customer who discovered them told the newspaper that they notified Foxtons three weeks ago of the privacy snafu, but that the firm had not taken action to notify customers or the authorities.

A statement from the nationwide estate agent sent to Infosecurity said that its Alexander Hall mortgage broking business was hit by malware in October 2020 in an attack affecting a number of other organizations. Although some IT systems were affected for several days, it said they were restored without significant disruption to customers.

“We have forensically been through all the stolen data and confirm it is both old and incomplete therefore not useable by a third party and not possible for it to cause financial loss or harm to those affected customers,” the statement continued.

“All necessary disclosures have been made and full details of the attack were provided to the FCA and ICO at the time. We are satisfied that the attack did not result in the loss of any data that could be damaging to customers and believe that the FCA and ICO are satisfied with our response.”

Stephen Kapp, CTO of Cortex Insight, commented: “It is safe to assume the worst and Foxton customers should look to protect themselves from identity fraud and card fraud as a result of this breach. With both personal information and payment card information lost, Foxtons customers should take some time to validate payments and potential credit history interactions since October and flag anything suspicious to their bank.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
US Payroll Agency Targeted in Separate SolarWinds Attack – Report

US Payroll Agency Targeted in Separate SolarWinds Attack – Report

Suspected Chinese state-backed threat actors exploited a SolarWinds Orion bug to compromise a US government payroll agency, a new report has claimed.

The campaign took place last year and was separate to the successful Russian cyber-espionage plot to spy on multiple government departments, five people familiar with the matter told Reuters.

Although the report was unable to clarify how many organizations were targeted, it claimed that the National Finance Center, a federal payroll agency inside the US Department of Agriculture (USDA), was one.

This alone could represent a serious national security risk, as the agency apparently handles personal and financial information on employees of the FBI, State Department, Homeland Security Department and Treasury Department, among others.

“Depending on what data were compromised, this could be an extremely serious breach of security,” former Department of Homeland Security official, Tom Warrick, told Reuters. “It could allow adversaries to know more about US officials, improving their ability to collect intelligence.”

Sources claimed that the attackers used hacking infrastructure and tools deployed in the past by Chinese state-backed threat groups. The Chinese government said in a statement that it opposes any cyber-attacks and urged those making the allegations to provide supporting evidence.

Unlike the Russians, who compromised an Orion update to gain a foothold in victim systems, among other tactics, these attackers were already inside victim networks when they exploited a bug in the software to move laterally, according to the report.

Bizarrely, the USDA both confirmed the breach with Reuters and then, following publication of the story, denied it.

A SolarWinds spokesperson sent the following statement to Infosecurity:

“The customer’s network was compromised in a way that was unrelated to SolarWinds. That breach enabled the attackers to add the malicious Supernova code to Orion software on the customer’s network. We are aware of one instance of this happening and there is no reason to believe these attackers were inside the SolarWinds environment at any time. This is separate from the broad and sophisticated attack that targeted multiple software companies as vectors.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Over Three Million US Drivers Exposed in Data Breach

Over Three Million US Drivers Exposed in Data Breach

Over three million customers of a US car company have had their details compromised after a cyber-criminal posted them to a dark web forum, according to Risk Based Security.

The security vendor spotted multiple databases uploaded to a hacking forum on January 4 this year, although the data dump apparently took place on December 19 2020.

It traced them back to DriveSure, an Illinois-based business owned by car dealership service provider Krex. Its website explains that the firm helps its clients to build strong customer relationships to encourage drivers back to dealerships for vehicle service and unplanned repairs.

On discovering the forum post, Risk Based Security dug deeper to validate the data from multiple databases. This included names, home and email addresses, phone numbers, car and damage details, text and email messages with dealerships, and over 93,000 bcrypt hashed passwords.

Although stronger than SHA1 and MD5, bcrypt could still be brute-forced if password strength is poor, said Risk Based Security.

The range of data exposed by the attacker appeared to be extensive.

“One leaked folder totalled 22GB and included the company’s MySQL databases, exposing 91 sensitive databases. The databases range from detailed dealership and inventory information, revenue data, reports, claims,and client data,” Risk Based Security explained.

“Separately, the second compromised folder contained 11,474 files in 105 folders and amassed to 5.93GB. Self-identified as ‘parser files,’ they appear to be logs and backups of their databases and contain the same information listed in the previously mentioned SQL databases, adding to the trove of data.”

A third folder contained a 1.5GB customer SQL database with nearly 3.3 million email addresses, including almost 16,000 .mil and .gov addresses, as well as over 5000 linked to S&P 100 companies, the vendor claimed.

“The information leaked in these databases is prime for exploitation by threat actors, and in particular for insurance scams. Criminals can use personally identifiable information, damage claims, extended car details and dealer and warranty information to target insurance companies and policyholders,” it concluded.

“Moreover, user credentials are used by threat actors to break into other valuable platforms such as bank accounts, personal email accounts and corporate systems. The diverse set of user data can also be used to guess and crack security questions often used by companies to reset passwords. Commercial email addresses can even be targets for spear-phishing or extortion.”

DriveSure responded promptly to Risk Based Security and reportedly said it is investigating the incident.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Infosecurity Industry’s White Hat Event Raises £66,000 for Childline

Infosecurity Industry’s White Hat Event Raises £66,000 for Childline

The Infosecurity industry came together virtually on January 29 2021 to raise money for the NSPCC’s Childline Service. 

The White Hat Ball, which is normally hosted at the Royal Lancaster Hotel in London, is now in its 16th year and has raised more than £2m for Childline. 

This year’s virtual format, White Hat’s Unforgettable Day, with headline sponsor KPMG, raised an impressive £66,000. 

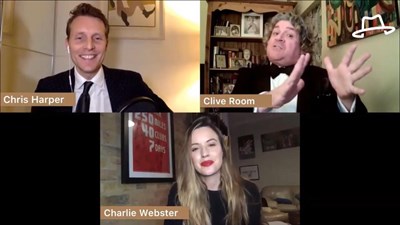
Hosted by actor Graham Cole, the event saw guest appearances from journalist Charlie Webster, Coronation Street Actress Chris Harper, Peter Andre, Jane Asher and Dame Esther Rantzen. 

The money raised will help Childline ensure that it can support as many children as possible who are at risk of abuse or neglect. Lilly O’Brien, NSPCC special events manager, said: “Since the start of the pandemic, Childline has supported thousands of young people across the country and events like this enable our dedicated staff and volunteers to continue to provide this life-changing service.

We’d like to thank the White Hat Committee for their hard work and dedication in organizing this great event and for their continued support throughout this difficult year.”

Stephen Khan, chair of the White Hat Committee, said: “White Hat Unforgettable day was amazing. As Chairman, I was truly humbled by the number of people that attended, and how our industry rallied behind a great cause to support vulnerable young people.”

If you would like to donate to this worthy cause, or watch the event, you can do so here. 

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk