The flaw in the free-source library could have been ported to multiple applications.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Andrew Appel discusses Georgia’s voting machines, how the paper ballots facilitated a recount, and the problem with automatic ballot-marking devices:
Suppose the polling-place optical scanners had been hacked (enough to change the outcome). Then this would have been detected in the audit, and (in principle) Georgia would have been able to recover by doing a full recount. That’s what we mean when we say optical-scan voting machines have “strong software independence”you can obtain a trustworthy result even if you’re not sure about the software in the machine on election day.
If Georgia had still been using the paperless touchscreen DRE voting machines that they used from 2003 to 2019, then there would have been no paper ballots to recount, and no way to disprove the allegations that the election was hacked. That would have been a nightmare scenario. I’ll bet that Secretary of State Raffensperger now appreciates why the Federal Court forced him to stop using those DRE machines (Curling v. Raffensperger, Case 1:17-cv-02989-AT Document 579).
I have long advocated voter-verifiable paper ballots, and this is an example of why.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Authorities in the United Kingdom have arrested a 20-year-old man for allegedly operating an online service for sending high-volume phishing campaigns via mobile text messages. The service, marketed in the underground under the name “SMS Bandits,” has been responsible for blasting out huge volumes of phishing lures spoofing everything from COVID-19 pandemic relief efforts to PayPal, telecommunications providers and tax revenue agencies.
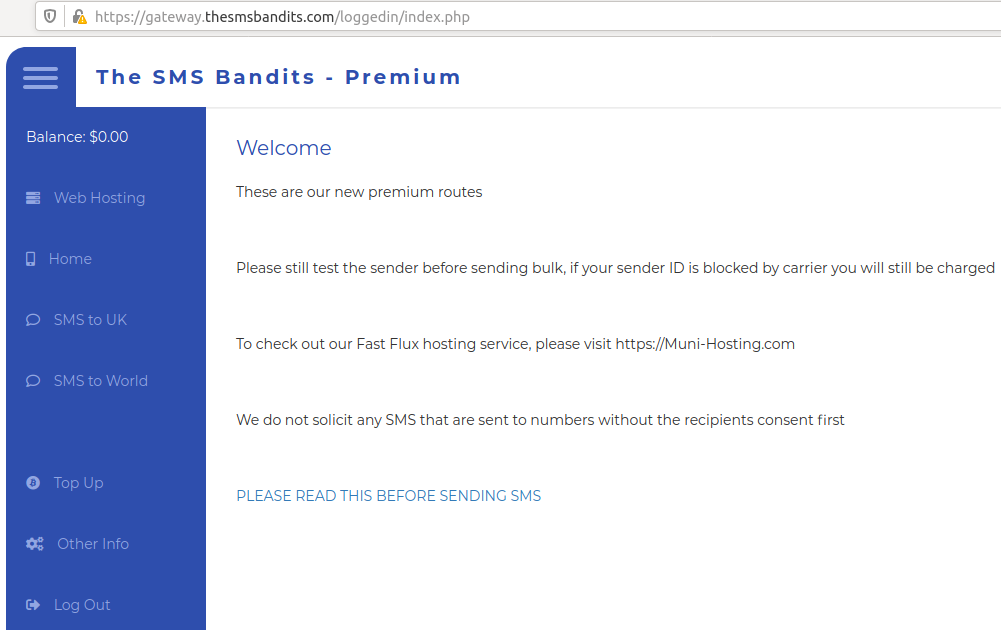
The U.K.’s National Crime Agency (NCA) declined to name the suspect, but confirmed that the Metropolitan Police Service’s cyber crime unit had detained an individual from Birmingham in connection to a business that supplied “criminal services related to phishing offenses.”
The proprietors of the phishing service were variously known on cybercrime forums under handles such as SMSBandits, “Gmuni,” “Bamit9,” and “Uncle Munis.” SMS Bandits offered an SMS phishing (a.k.a. “smishing”) service for the mass sending of text messages designed to phish account credentials for different popular websites and steal personal and financial data for resale.
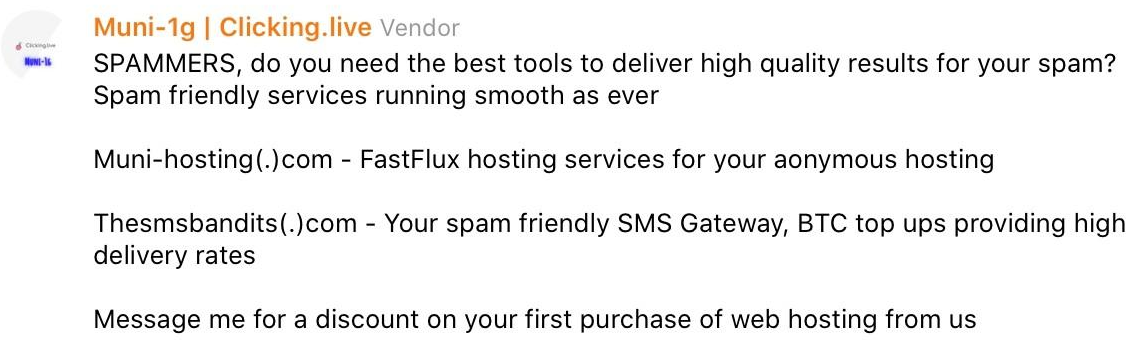
Image: osint.fans
Sasha Angus is a partner at Scylla Intel, a cyber intelligence startup that did a great deal of research into the SMS Bandits leading up to the arrest. Angus said the phishing lures sent by the SMS Bandits were unusually well-done and free of grammar and spelling mistakes that often make it easy to spot a phony message.
“Just by virtue of these guys being native English speakers, the quality of their phishing kits and lures were considerably better than most,” Angus said.
According to Scylla, the SMS Bandits made a number of operational security (or “opsec”) mistakes that made it relatively easy to find out who they were in real life, but the technical side SMS Bandits’ operation was rather advanced.
“They were launching fairly high-volume smishing campaigns from SMS gateways, but overall their opsec was fairly lousy,” Angus said. “But on the telecom front they were using fairly sophisticated tactics.”
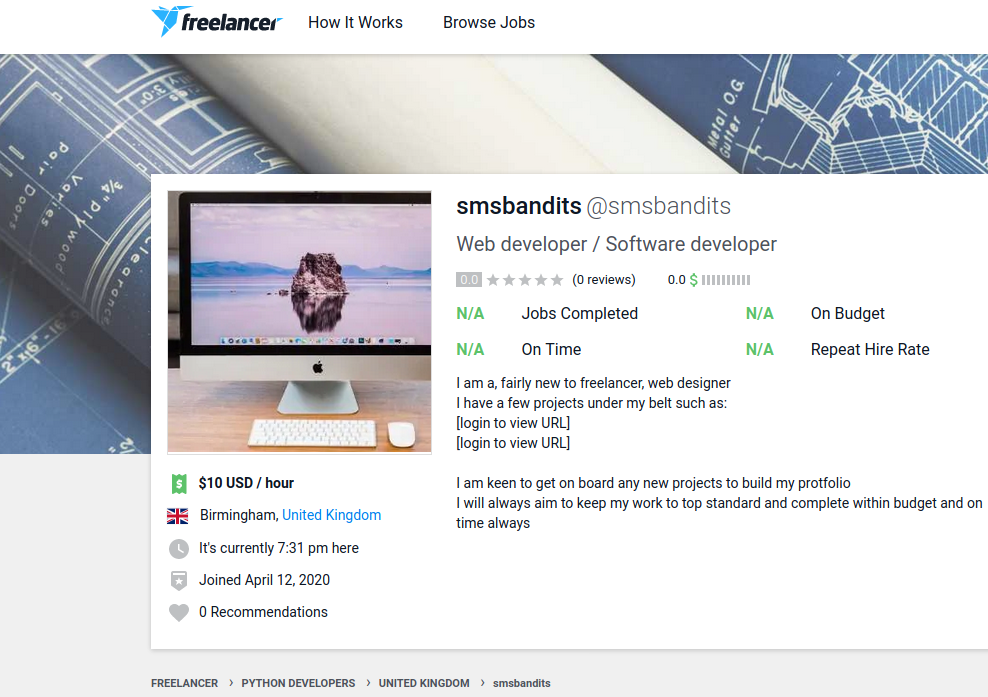
The proprietor of the SMS Bandits, telling the world he lives in Birmingham.
For example, the SMS Bandits automated systems to check whether the phone number list provided by their customers was indeed tied to actual mobile numbers, and not landlines that might tip off telecommunications companies about mass spam campaigns.
“The telcos are monitoring for malicious SMS messages on a number of fronts,” Angus said. “One way to tip off an SMS gateway or wireless provider is to start blasting text messages to phone numbers that can’t receive them.”
Scylla gathered reams of evidence showing the SMS Bandits used email addresses and passwords stolen through its services to validate a variety of account credentials — from PayPal to bank accounts and utilities providers. They would then offload the working credentials onto marketplaces they controlled, and to third-party vendors. One of SMS Bandits’ key offerings: An “auto-shop” web panel for selling stolen account credentials.
SMS Bandits also provided their own “bulletproof hosting” service advertised as a platform that supported “freedom of speach” [sic] where customers could “host any content without restriction.” Invariably, that content constituted sites designed to phish credentials from users of various online services.
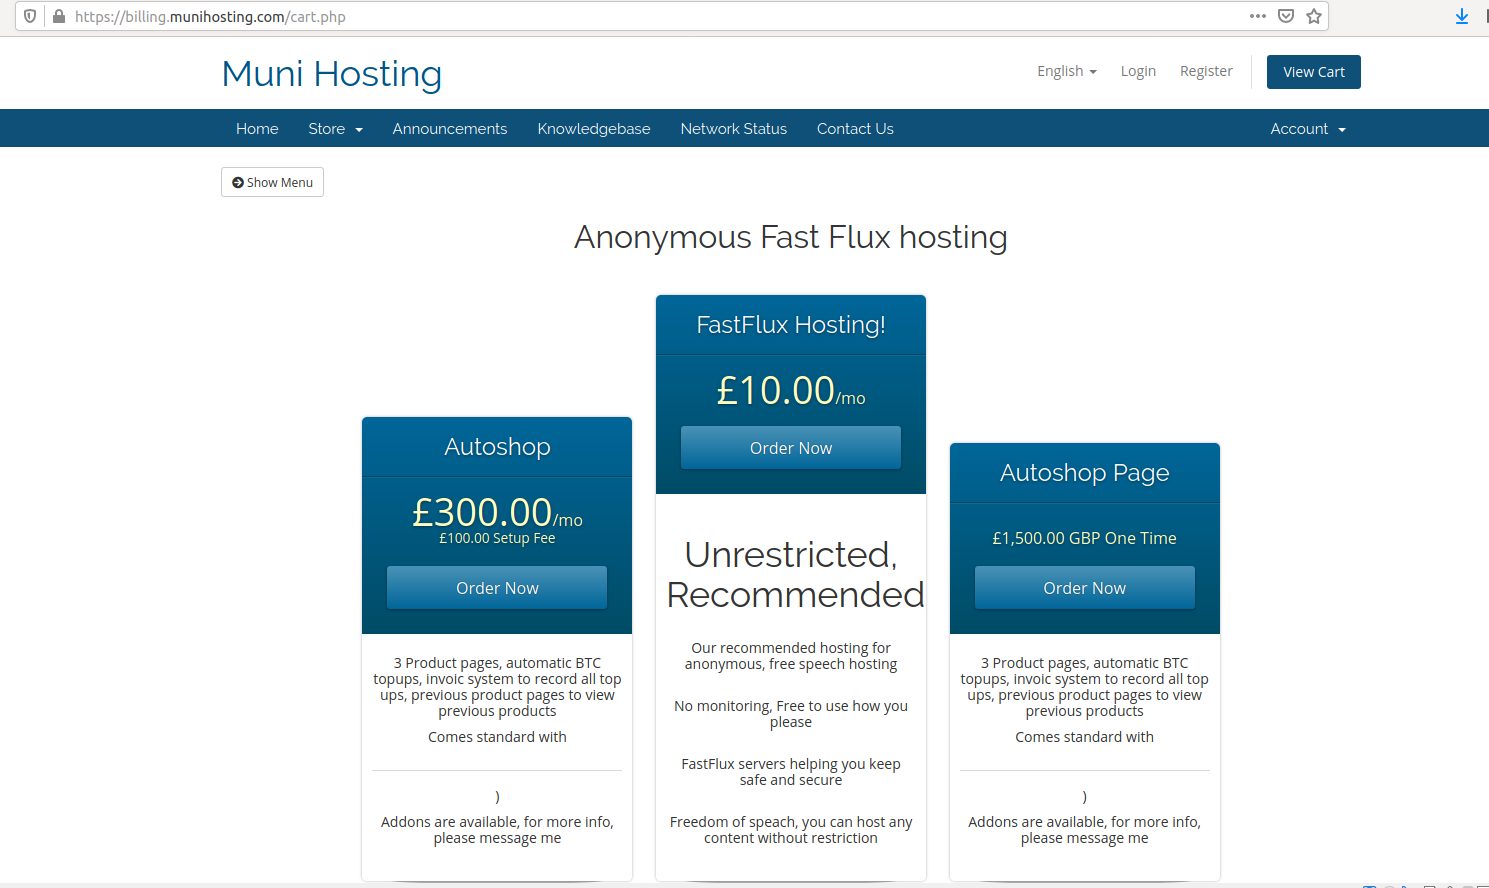
The “bulletproof” offerings of Muni Hosting (pronounced “Money Hosting”).
The SMS Bandits phishing service is tied to another crime-friendly service called “OTP Agency,” a bulk SMS provider that appears catered to phishers: The service’s administrator stated on multiple forums that he worked directly with the SMS Bandits.
Otp[.]agency advertises a service designed to help intercept one-time passwords needed to log in to various websites. The customer enters the target’s phone number and name, and OTP Agency will initiate an automated phone call to the target that alerts them about unauthorized activity on their account.
The call prompts the target to enter a one-time password generated by their phone’s mobile app, and that code is then relayed back to the scammer’s user panel at the OTP Agency website.
“We call the holder with an automatic calling bot, with a very believable script, they enter the OTP on the phone, and you’ll see it in real time,” OTP Agency explained on their Telegram channel. The service, which costs anywhere from $40 to $125 per week, advertises unlimited international calling, as well as multiple call scripts and voice accents.
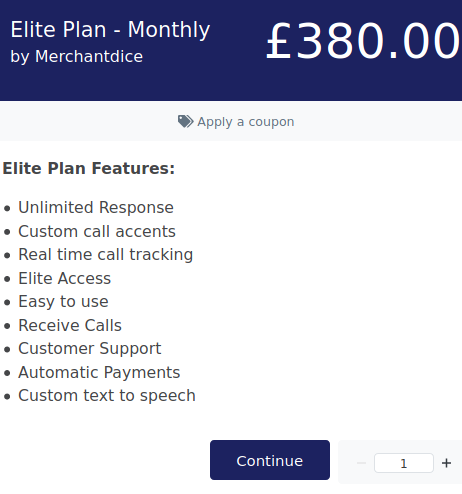
One of the pricing plans available to OTP Agency users.
The volume of SMS-based phishing skyrocketed in 2020 — by more than 328 percent — according to a recent report from Proofpoint, a security firm that processes more than 80 percent of North America’s mobile messages [Full disclosure: Proofpoint is currently an advertiser on this site].
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
A retired Nevada cop who headed up a Cyber Crimes Unit has been charged with burglary, bigamy, and forgery.
Former Washoe County Sheriff’s deputy Dennis Carry was arrested on Tuesday on seven different felony counts following a two-year investigation by the Reno Police Department.
The 46-year-old was previously in charge of the Cyber Crimes Unit at the Washoe County Sheriff’s Office before being placed on administrative leave in March 2019. During the course of the investigation by Reno police, Carry formally retired from WCSO.
Court documents show that Carry was already married when he walked down the aisle with Carla Baldwin, a federal magistrate judge for the United States District Court for the District of Nevada.
Carry wed his first wife, Wendy, in South Lake Tahoe in 1996. Then, in late May 2018, Carry tied the knot with Baldwin in California despite not having obtained a divorce from his first wife.
In March 2019, both of the former deputy’s wives sought to sever their matrimonial bonds with Carry. Wendy filed for divorce about two weeks after Baldwin formally began annulment proceedings.
In July 2019, former Washoe County family court judge David Humke said that RPD investigators had spoken to him concerning allegations that Carry had broken into his office and hacked into his computer. The RPD were looking into claims that Carry had illegally accessed Humke’s computer in order to create fake court documents he could use to convince Baldwin that he was no longer married to his first wife.
The allegedly forged documents, dated May 9, 2018, divided up Wendy and Dennis Carry’s mortgage debt while assigning the bulk of the couple’s credit card debt to Dennis Carry.
No mention is made in the allegedly fake paperwork of the 2018 Tesla or the $608k home that Carla Baldwin Carry and Dennis Carry bought months before Wendy Carry filed for divorce. Wendy Carry’s attorneys are claiming for both these purchases since they were made while Dennis Carry was still married to her.
WCSO spokesperson Bob Harmon said in July 2019 that he didn’t know if the department was aware that their former deputy was simultaneously going through two separate marriage-ending proceedings.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
The organizers of an English beauty pageant established over nine decades ago are being held to ransom by cyber-criminals.
The Daily Mail reports that malicious hackers targeted the organizers of Miss England on Tuesday night with a sophisticated online scam.
Pageant organizer and former Miss England Angie Beasley was sent what appeared to be an authentic message from the administrators of the social media app Instagram informing her that she had violated the app’s rules and asking her to confirm her phone number.
“The message said I had broken rules and they were going to close the account down. It included a link you could click to appeal the decision,” said Beasley.
“I had no idea what it was all about as we only put good things and charity appeals on there. I clicked on the link and got another message saying it could see I was trying to access the appeal form and could I confirm my phone number, which I did.
“I got sent a code which I then gave to them and then everything just went. The next thing I knew the whole account whizzed in front of me on my phone and the account was taken over.”
By clicking on the link, Beasley unwittingly gave the hackers access to the pageant’s Instagram account, which has over 20,000 followers. After gaining access to the account, the hackers changed the password and locked Beasley out.
The next day, Beasley received a message on her cell phone asking her if she wanted to “make a deal” to recover the locked account.
Beasley contacted Action Fraud, the UK’s national reporting center for fraud and cybercrime, who reached out to local police in Leicestershire, where Miss England is headquartered.
Instagram’s owners, Facebook, said that the hacked Miss England account has now been secured and restored to the account owner.
In 2020 the Miss England pageant was cancelled because of the global outbreak of Covid-19. The last woman to win the Miss England title was Bhasha Mukherjee in 2019.
Mukherjee, a junior doctor who holds two degrees, cut her overseas work as a charity ambassador short last year to continue her career as a doctor in the UK amid the coronavirus pandemic.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
An end-to-end multicloud technology solutions company based in Texas has been recognized for achieving workplace equality for a fourth consecutive year.
Rackspace Technology announced today that it received a score of 100 on the Human Rights Campaign (HRC) Foundation’s 2021 Corporate Equality Index (CEI) and was named as one of the “Best Places to Work for LGBTQ Equality.”
The HRC Foundation’s CEI was established nearly two decades ago to be a primary driving force for workplace inclusion. It provides companies with a national benchmarking tool against which to measure corporate policies, practices, and benefits pertinent to lesbian, gay, bisexual, transgender, and queer (LGBTQ) employees.
A total of 1,142 companies participated in the CEI 2021 Survey, including 233 Fortune 500 employers and 149 Law Magazine 200 law firms.
Headquartered in Windcrest, Rackspace designs, builds, and operates cloud environments across all major technology platforms, irrespective of technology stack or deployment model. In addition to this recent accolade, the company has been named a best place to work by Great Place to Work Institute, Fortune, Forbes, Glassdoor, and Military Times.
“Rackspace Technology is honored to be recognized by the Human Rights Campaign for our commitment to fostering a diverse and inclusive workforce. We are dedicated to creating a workplace where Rackers can be their authentic selves and leverage their diverse perspectives to spark innovation,” said Chinten Parikh, senior director of global diversity, inclusion, and belonging at Rackspace Technology.
“This recognition celebrates our progress and challenges us to climb even higher.”
The CEI rates companies on detailed criteria under the categories of non-discrimination policies across business entities; equitable benefits for LGBTQ workers and their families; supporting an inclusive culture; and corporate social responsibility.
“From the previously unimaginable impact of the COVID-19 pandemic, to a long overdue reckoning with racial injustice, 2020 was an unprecedented year. Yet, many businesses across the nation stepped up and continued to prioritize and champion LGBTQ equality,” said HRC president Alphonso David.
“Our participating companies know that building an LGBTQ-inclusive workplace is not just the right thing to do, it is also the best business decision, allowing companies to attract, retain and engage top talent.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk