Thales and TT Electronics Partner to Enable OT Cybersecurity Initiatives and Research

Thales and TT Electronics Partner to Enable OT Cybersecurity Initiatives and Research

Multinational technology company Thales and global provider of engineered electronics for performance critical applications TT Electronics have announced a partnership to enable the development of operational technology cybersecurity initiatives and research.

These programs will be delivered out of the National Digital Exploitation Center (NDEC) in South Wales, which offers cyber-skills and knowledge to the region. The partnership brings together Thales’ expertise in securing critical systems with TT Electronics’ innovative approach to electronics manufacturing for high-reliability markets.

“Thales and TT Electronics have very complementary and synergistic technologies,” said Perry Duffill, VP/GM, TT Electronics Global Manufacturing Solutions. “This collaboration enables TT to provide an additional level of security assurance for our aerospace and defense, medical and industrial customers who rely on us to manufacture highly complex systems for mission critical applications.”

Gareth Williams, VP, secure communications and information systems at Thales, added that the agreement is the next logical step in the long-standing relationship between the two companies.

“While we have previously worked together at the NDEC – with TT Electronics sitting on the steering group – this agreement enables a much more intimate level of collaboration between the two companies, with a clear goal of secure and resilient operational technology.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Joker’s Stash Carding Site to Close in February

Joker’s Stash Carding Site to Close in February

The largest carding marketplace on the dark web has announced it is shutting down for good, although experts warned that this will have little impact on the overall cybercrime economy.

The administrator of the Joker’s Stash site posted the news on Friday, claiming that the marketplace would remain open until February 15 this year before they go on a “well-deserved retirement.”

Experts at threat intelligence firm Gemini Advisory speculated that the announcement may be linked to October news posted by “JokerStash” that the site had recently been disrupted after they had to spend over a week in hospital with COVID-19.

They also questioned whether the recent spike in the value of Bitcoin had made the site admin now rich enough to retire.

Having been in operation since 2014, Joker’s Stash added 40 million stolen records and generated an estimated $1bn in revenue. However, the site apparently suffered a decline in the volume and quality of cards it was able to offer over the past six months.

“Most other top-tier carding marketplaces actually increased their posted data during this time. However, Joker’s Stash has received numerous user complaints alleging that card data validity is low, which even prompted the administrator to upload proof of validity through a card-testing service,” noted Gemini Advisory.

“Additionally, JokerStash’s tactics, techniques and procedures (TTPs) involved advertising in advance and then posting high-profile major breaches. The threat actor leveraged media coverage of these breaches to boast about their ability to compromise even major corporations. Most dark web marketplaces eschew such TTPs because they attract undue attention from security researchers and law enforcement; JokerStash actually celebrated such attention.”

In a sign of the adaptability of the cybercrime underground, it is predicted that JokerStash’s retirement won’t have a significant impact on the industry.

Threat actors tend to split the sale of data across multiple marketplaces anyway, so they’ll simply pivot to other sites in the future, argued Gemini Advisory.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Environmental Regulator Suffers Ransomware Blow

Environmental Regulator Suffers Ransomware Blow

The Scottish Environment Protection Agency (SEPA) has warned that it could take a “significant period” of time before systems and services are fully restored after it was hit by ransomware on Christmas Eve.

In a lengthy update late last week, the agency claimed that “a number” of its IT systems will remain “badly affected for some time,” and in some cases will need to be replaced completely.

“The agency confirmed that email, staff schedules, a number of specialist reporting tools, systems and databases remain unavailable with the potential for access to a series of systems and tools to be unavailable for a protracted period,” it continued.

One of these systems is a service for online reporting and enquiries about pollution. Although now restored, any information submitted to the service during the early days of the attack is not accessible.

On the plus side, SEPA said that its main regulatory, monitoring, flood forecasting and warning services continue to operate. Contact center and online self-help services are being slowly restored, including SEPA’s Floodline, 24-hour pollution hotline and environmental event reporting.

However, attackers also stole 1.2GB of data from the agency including information on procurement, commercial projects and SEPA staff, as well as its corporate plans, priorities and change programs. Some, but not all, is thought to have been publicly available.

“Whilst the actions of serious and organized criminals means that for the moment we’ve lost access to our systems and had information stolen, what we’ve not lost is the expertise of over 1200 staff who day in, day out work tirelessly to protect Scotland’s environment,” said SEPA CEO Terry A’Hearn.

“Sadly we’re not the first and won’t be the last national organization targeted by likely international criminals. Cybercrime is a growing trend. Our focus is on supporting our people, our partners, protecting Scotland’s environment and, in time, following a review, sharing any learnings with wider public, private and voluntary sector partners.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Leaked #COVID19 Vaccine Data “Manipulated” to Mislead Public

Leaked #COVID19 Vaccine Data “Manipulated” to Mislead Public

Official COVID-19 vaccine data stolen and leaked online by threat actors had been changed prior to publication in what could be a deliberate attempt to sow disinformation, a medical regulator has claimed.

The European Medicines Agency (EMA) first revealed the data breach back in December. Although at the time it refused to clarify what was stolen, German biotechnology company BioNTech revealed that it was one of the firms affected.

“Some documents relating to the regulatory submission for Pfizer and BioNTech’s COVID-19 vaccine candidate, BNT162b2, which has been stored on an EMA server, had been unlawfully accessed,” it said at the time.

Last week the EMA claimed some of the stolen data was released online by the attackers, although it was unclear what their motives were.

However, in an update on Friday, the agency indicated that the end goal may have been to spread fake news.

“The ongoing investigation of the cyber-attack on EMA revealed that some of the unlawfully accessed documents related to COVID-19 medicines and vaccines have been leaked on the internet,” it noted.

“This included internal/confidential email correspondence dating from November, relating to evaluation processes for COVID-19 vaccines. Some of the correspondence has been manipulated by the perpetrators prior to publication in a way which could undermine trust in vaccines.”

Attempts to manipulate public perception of events could indicate the hand of state-sponsored threat actors. Both Russia and China have developed rival vaccines to the Pfizer/BioNTech effort, and are looking to build their soft power by striking deals to supply other countries in a “vaccine diplomacy” push.

Anything that casts doubt on the efficacy of the Pfizer jab could therefore work in their favor. Alternatively, it may simply be the work of hacktivists appealing to a growing anti-vaxxer movement.

For its part, the EMA sought to reassure the public in its statement on the matter.

“Amid the high infection rate in the EU, there is an urgent public health need to make vaccines available to EU citizens as soon as possible,” it said.

“Despite this urgency, there has always been consensus across the EU not to compromise the high quality standards and to base any recommendation on the strength of the scientific evidence on a vaccine’s safety, quality and efficacy, and nothing else.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Joker’s Stash Carding Market to Call it Quits

Joker’s Stash, by some accounts the largest underground shop for selling stolen credit card and identity data, says it’s closing up shop effective mid-February 2021. The announcement came on the heels of a turbulent year for the major cybercrime store, and just weeks after U.S. and European authorities seized a number of its servers.
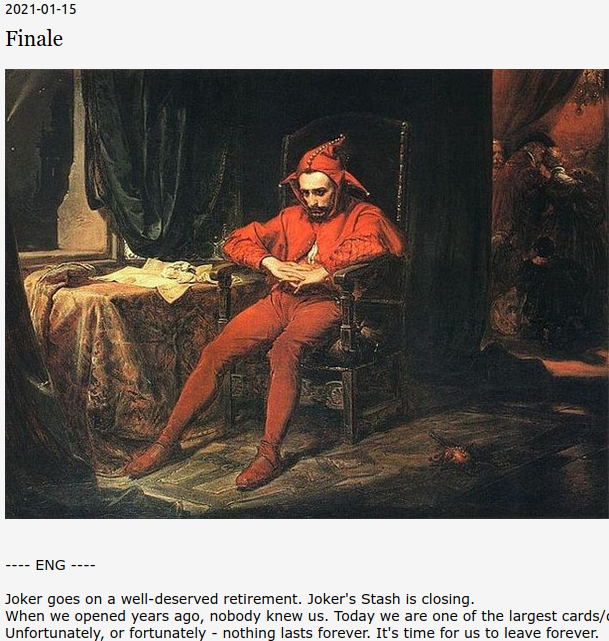
A farewell message posted by Joker’s Stash admin on Jan. 15, 2021.

The Russian and English language carding store first opened in October 2014, and quickly became a major source of “dumps” — information stolen from compromised payment cards that thieves can buy and use to create physical counterfeit copies of the cards.

But 2020 turned out to be a tough year for Joker’s Stash. As cyber intelligence firm Intel 471 notes, the curator of the store announced in October that he’d contracted COVID-19, spending a week in the hospital. Around that time, Intel 471 says many of Joker’s loyal customers started complaining that the shop’s payment card data quality was increasingly poor.

“The condition impacted the site’s forums, inventory replenishments and other operations,” Intel 471 said.
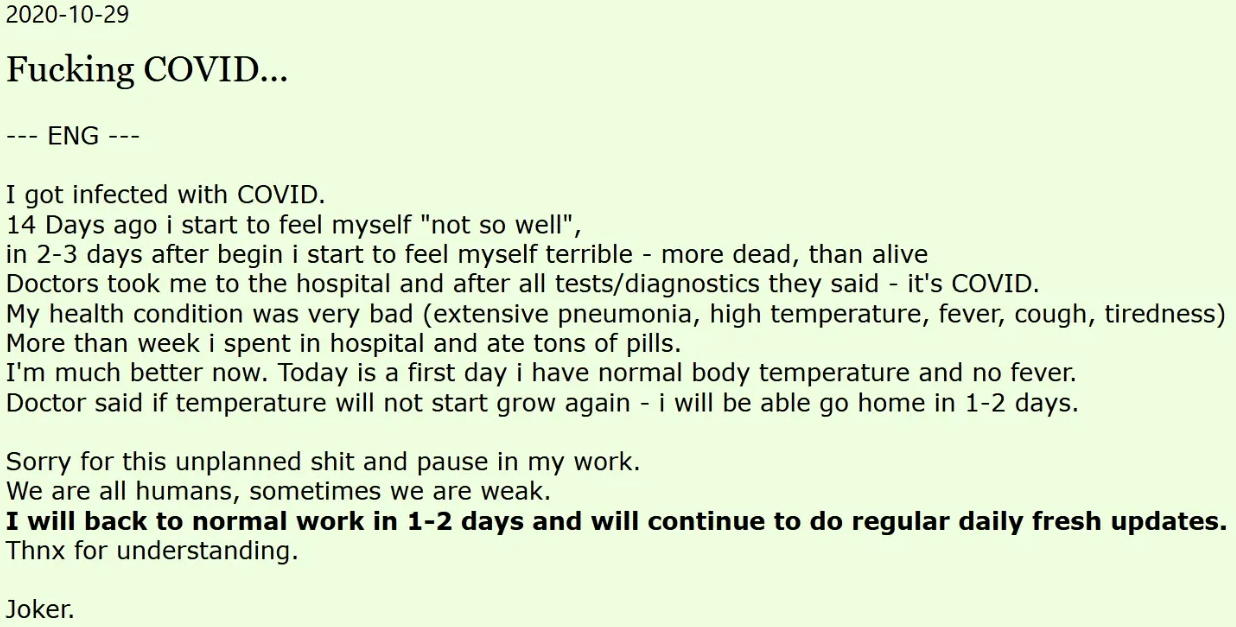
Image: Gemini Advisory

That COVID diagnosis may have affected the shop owner’s ability to maintain fresh and valid inventory on his site. Gemini Advisory, a New York City-based company that monitors underground carding shops, tracked a “severe decline” in the volume of compromised payment card accounts for sale on Joker’s Stash over the past six months.

“Joker’s Stash has received numerous user complaints alleging that card data validity is low, which even prompted the administrator to upload proof of validity through a card-testing service,” Gemini wrote in a blog post about the planned shutdown.
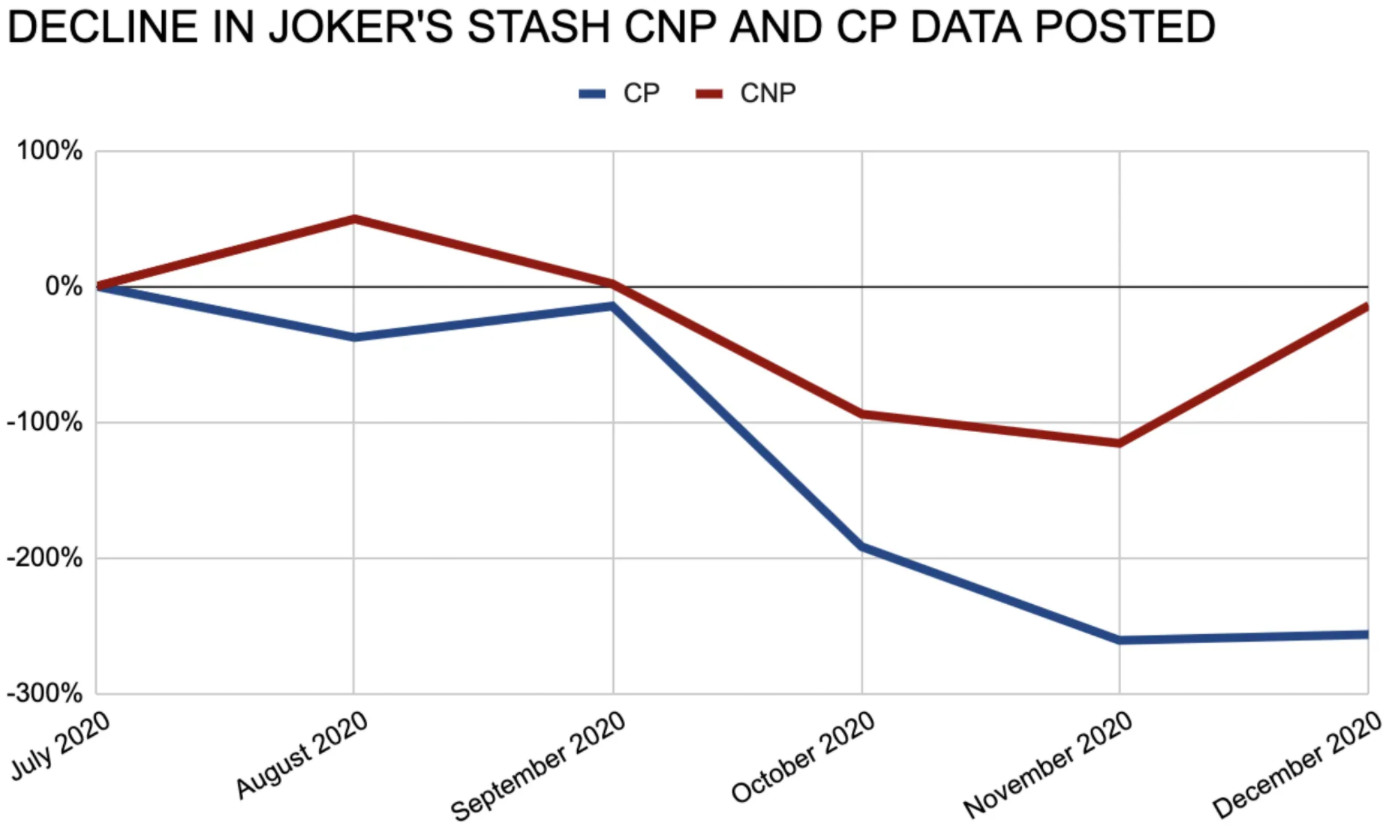
Image: Gemini Advisory

Then on Dec. 16, 2020, several of Joker’s long-held domains began displaying notices that the sites had been seized by the U.S. Department of Justice and Interpol. The crime shop quickly recovered, moving to new infrastructure and assuring the underground community that it would continue to operate normally.

Gemini estimates that Joker’s Stash generated more than a billion dollars in revenue over the past several years. Much of that revenue came from high-profile breaches, including tens of millions of payment card records stolen from major merchants including Saks Fifth Avenue, Lord and TaylorBebe StoresHilton HotelsJason’s DeliWhole FoodsChipotle, Wawa, Sonic Drive-In, the Hy-Vee supermarket chain, Buca Di Beppo, and Dickey’s BBQ.

Joker’s Stash routinely teased big breaches days or weeks in advance of selling payment card records stolen from those companies, and periodically linked to this site and other media outlets as proof of his shop’s prowess and authenticity.

Like many other top cybercrime bazaars, Joker’s Stash was a frequent target of phishers looking to rip off unwary or unsophisticated thieves. In 2018, KrebsOnSecurity detailed a vast network of fake Joker’s Stash sites set up to steal login credentials and bitcoin. The phony sites all traced back to the owners of a Pakistani web site design firm. Many of those fake sites are still active (e.g. jokersstash[.]su).

As noted here in 2016, Joker’s Stash attracted an impressive number of customers who kept five and six-digit balances at the shop, and who were granted early access to new breaches as well as steep discounts for bulk buys. Those “partner” customers will be given the opportunity to cash out their accounts. But the majority of Stash customers do not enjoy this status, and will have to spend their balances by Feb. 15 or forfeit those funds.
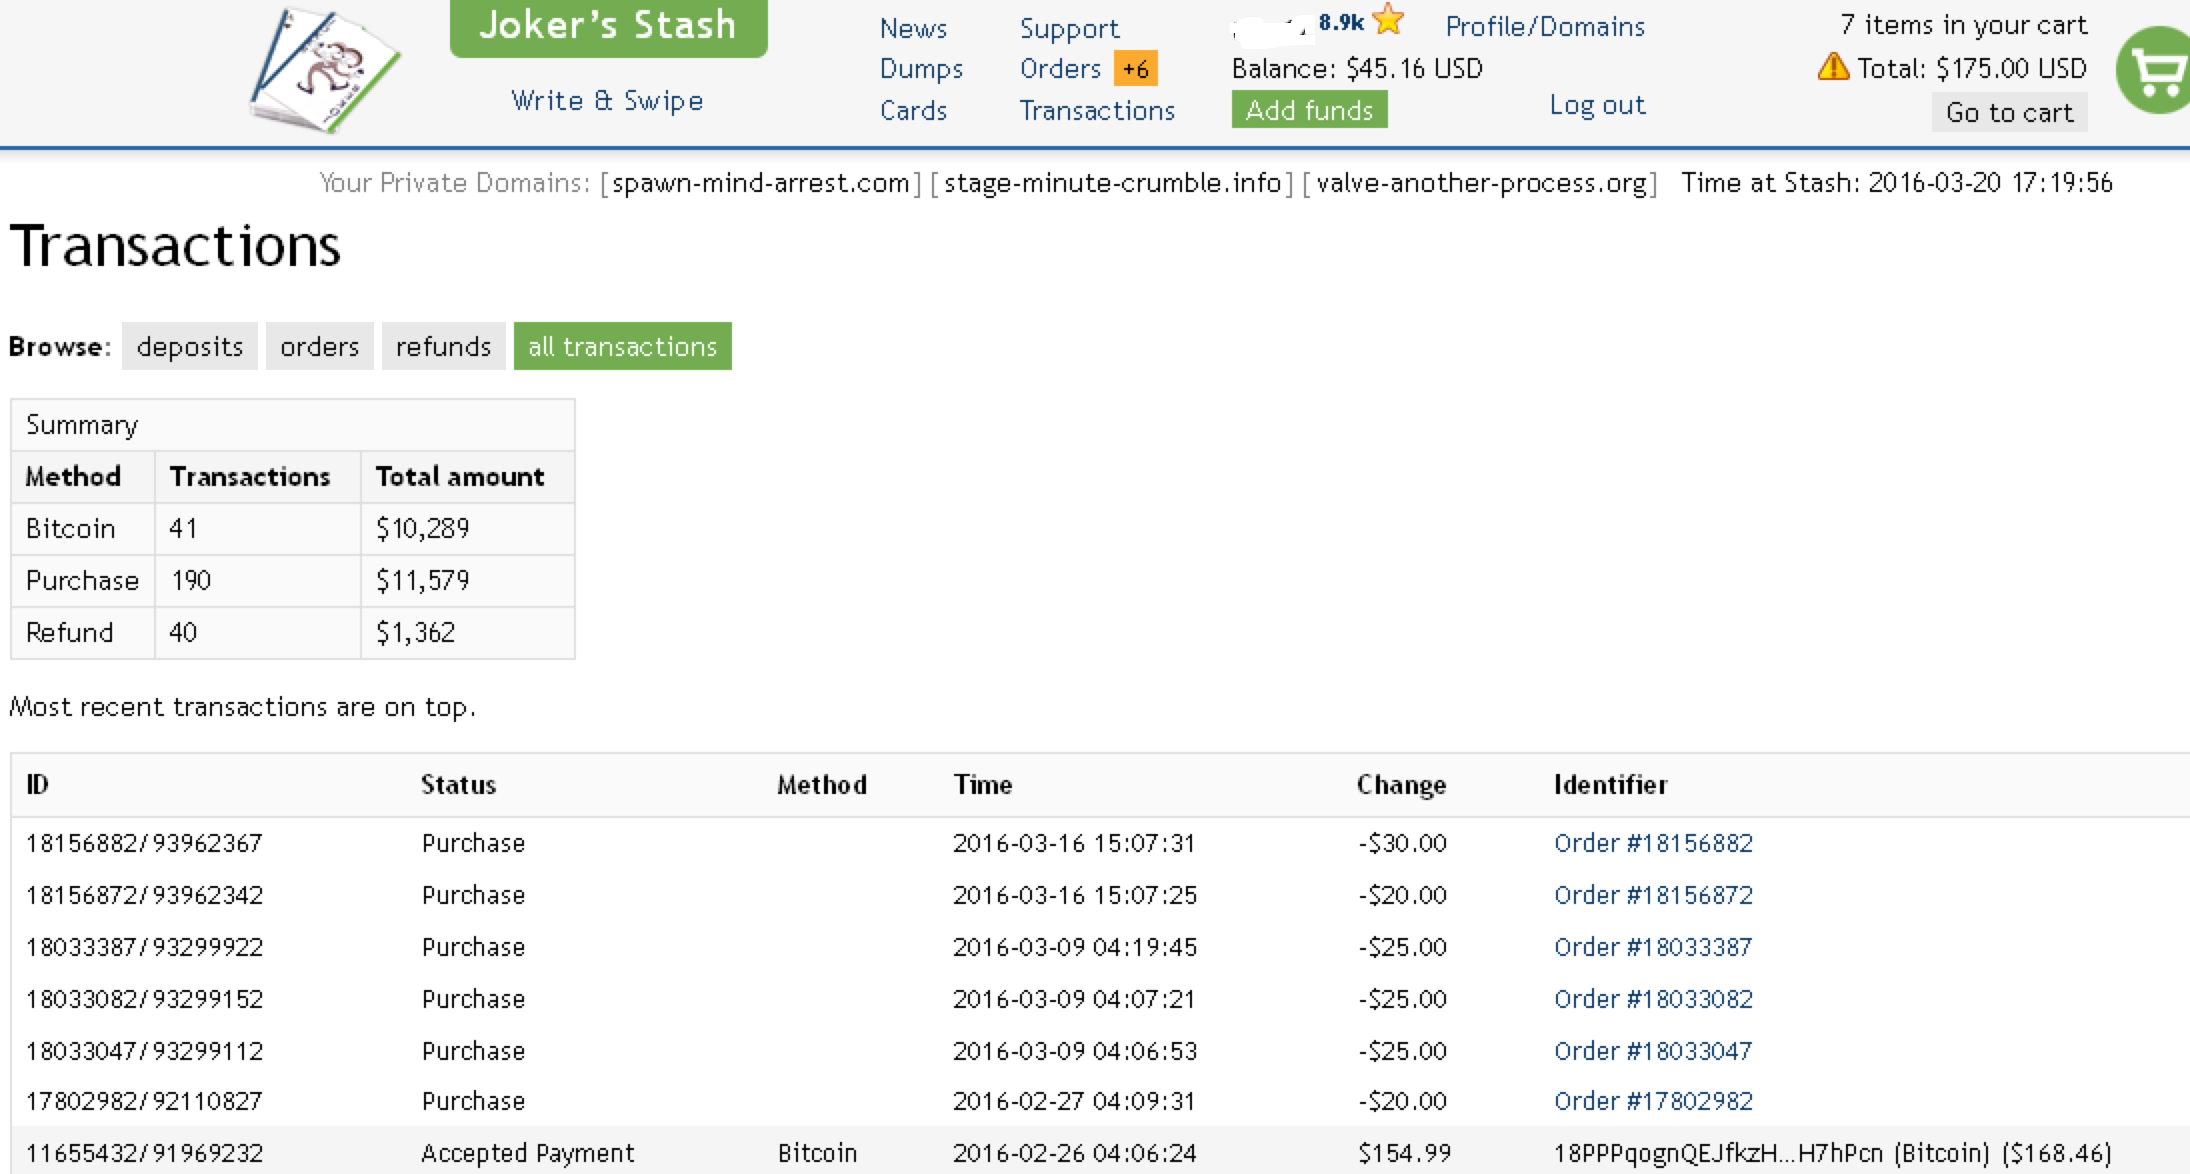
The dashboard for a Joker’s Stash customer who’s spent over $10,000 buying stolen credit cards from the site.

Gemini said another event that may have contributed to this threat actor shutting down their marketplace is the recent spike in the value of Bitcoin. A year ago, one bitcoin was worth about $9,000. Today a single bitcoin is valued at more than $35,000.

“JokerStash was an early advocate of Bitcoin and claims to keep all proceeds in this cryptocurrency,” Gemini observed in a blog post. “This actor was already likely to be among the wealthiest cybercriminals, and the spike may have multiplied their fortune, earning them enough money to retire. However, the true reason behind this shutdown remains unclear.”

If the bitcoin price theory holds, that would be fairly rich considering the parting lines in the closure notice posted to Joker’s Stash.

“We are also want to wish all young and mature ones cyber-gangsters not to lose themselves in the pursuit of easy money,” the site administrator(s) advised. “Remember, that even all the money in the world will never make you happy and that all the most truly valuable things in this life are free.”

Regardless, the impending shutdown is unlikely to have much of an impact on the overall underground carding industry, Gemini notes.

“Given Joker’s Stash’s high profile, it relied on a robust network of criminal vendors who offered their stolen records on this marketplace, among others,” the company wrote. “Gemini assesses with a high level of confidence that these vendors are very likely to fully transition to other large, top-tier dark web marketplaces.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Florida Man Cyberstalked Survivor of Murder Attempt

Florida Man Cyberstalked Survivor of Murder Attempt

A man from Florida has admitted cyberstalking a woman who survived a violent attack in her childhood that left another young girl dead. 

Alvin Willie George of Cross City pleaded guilty to two counts of cyberstalking related to the online harassment of the survivor and her sisters. 

According to court records, the victim was in a Texas bedroom with another girl in December 1999 when an assailant entered and attacked the two friends. Both girls had their throats slit. 

One girl died from the attack, while her friend survived. The perpetrator of this vicious assault was later caught and convicted. 

George, who has no connection to the surviving victim or her family, began harassing the victim and her family 17 years after the attack took place.  

In or around November 2016, George started researching the deadly crime on the internet. The 25-year-old then created various Facebook accounts that he used to send harassing messages to the victim and her sisters, all of whom live in Idaho. In the messages, George threatened to rape and kill the women. 

The case was investigated by the Federal Bureau of Investigation and the Boise Police Department.

A federal grand jury in Boise indicted George on December 11, 2019. On Thursday, the US Attorney’s Office in Boise, Idaho, announced George’s guilty plea.

Sentencing is scheduled to take place on April 8, 2021, before US District Judge B. Lynn Winmill at the federal courthouse in Boise.

In Idaho, the crime of cyberstalking is punishable by up to five years in prison, a maximum fine of $250,000, and a supervised release period of up to three years, per charge.

According to the Stalking Prevention, Awareness and Resource Center, an estimated 6 to 7.5 million people are stalked annually in the United States. 

The majority of stalking victims are stalked by someone they know; just one in five stalking victims are stalked by a stranger. 

A quarter of stalking victims report being stalked through the use of some form of technology such as e-mail or instant messaging. While 10% of victims report being monitored with global positioning systems, 8% report being monitored through video or digital cameras, or listening devices.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Women in Cybersecurity Mid-Atlantic Partners with CMMC COE

Women in Cybersecurity Mid-Atlantic Partners with CMMC COE

The Cybersecurity Maturity Model Certification Center of Excellence (CMMC COE) yesterday announced a Memorandum of Understanding with the Women in Cybersecurity (WiCyS) Mid-Atlantic affiliate.

The executed MOU creates a cooperative agreement between the two parties to partner in the furthering of their missions and objectives around the adoption, use, and expansion of CMMC-based cybersecurity practices for the US Department of Defense (DoD) global Defense Industrial Base (DIB) contractor community and the information and communication technology community.

Objectives of the new partnership include a desire to aid efforts to advance the goals for improving the cyber and supply-chain security and resilience of the DIB network of contractors, suppliers, and vendors.

Among the specific actions planned is the co-development of CMMC advisory services, cyber education and training programs to increase cyber adoption, accelerating CMMC certification, and improving cyber protection and resilience.

The partners also want to expand and drive diversity across the cybersecurity workforce, which in 2019 was 80% male

“The WiCyS Mid-Atlantic is excited to team with the CMMC COE in efforts to enhance the overall security of the defense industrial base supply chain,” said Diane Janosek, founder and senior advisor of Women in Cybersecurity Mid-Atlantic.

“This partnership clearly demonstrates the CMMC COE’s commitment to a diverse cybersecurity workforce, which is key to defending the nation’s cyber critical infrastructure. Creative and inclusive teaming is essential to the CMMC’s success.” 

Further actions planned by the partnership are the co-sponsorship of symposiums, training programs, and podcasts, leveraging their combined cyber and IT expertise, and the hosting of regular working groups, along with additional partners, to allow collaboration and communication. 

The establishment of an independent Industry Cyber Security Advisory Council is also planned, with peer organizations brought in to advise and educate leaders across government and industry on the effectiveness and continued evolution of CMMC.

“This is exciting opportunity for us,” said John Weiler, chairman of the board at CMMC Center of Excellence. “This new partnership will further help advance the goals and objectives for improving the supply chain security and resilience of the US Department of Defense.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

UK Accidentally Deletes 150k Arrest Records

UK Accidentally Deletes 150k Arrest Records

The UK government is investigating a technical issue that led to 150,000 arrest records’ being accidentally wiped from nationwide police databases. 

The unintentional erasure, reported initially by The Times, is believed to have been caused by human error and defective code that earmarked the wrong files for deletion.

Over 150,000 fingerprint records, DNA records, and arrest history records were lost as a result of the glitch. One source told The Times that the error could potentially allow offenders to escape justice as biometric evidence captured from crime scenes will no longer be flagged on the Police National Computer (PNC). 

The error also impacted Britain’s visa system, causing the processing of applications to be suspended for two days. 

Sources told The Times that the records were accidentally wiped during one of the weekly data expunging acts known as “weeding” sessions. 

The newspaper reported that “crucial intelligence about suspects” had vanished as a result of the incident. However, the Home Office said that no records of criminals or dangerous persons had been deleted and that the lost data related to individuals who had been arrested and then released without charge.

UK Minister for Policing Kit Malthouse said officials were “working at pace” to attempt the recovery of the lost records.

He said: “A fast time review has identified the problem and corrected the process so it cannot happen again. The Home Office, NPCC [National Police Chiefs’ Council] and other law enforcement partners are working at pace to recover the data.

“While the loss relates to individuals who were arrested and then released with no further action, I have asked officials and the police to confirm their initial assessment that there is no threat to public safety. I will provide further updates as we conclude our work.”

Shadow Home Secretary Nick Thomas-Symonds said: “This is an extraordinarily serious security breach that presents huge dangers for public safety. The incompetence of this shambolic government cannot be allowed to put people at risk, let criminals go free and deny victims justice.”

The loss of the data follows the removal of 40,000 alerts regarding European criminals from the PNC with the UK’s Brexit departure from the European Union.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk