Kaspersky and Alias Robotics Partner to Secure Robots in OT Infrastructure
Kaspersky and Alias Robotics Partner to Secure Robots in OT Infrastructure

Global security giant Kaspersky and robot cybersecurity firm Alias Robotics have announced a partnership that will seek to enhance protection for robots used in operational technology (OT) infrastructure.

Used in many industrial operations, robots – a key component of Industry 4.0 – represent yet another type of endpoint in OT settings that must be secured. However, as robots are separate, complex and connected systems with specific protocols and tools, protecting them requires a unique approach.

According to a case study from Kaspersky and Alias Robotics, the solutions offered by each company can effectively work together to prevent attacks on OT networks with robots, harden control stations and protect robot endpoints from being compromised.

“Robots have their own networks, technologies, safety requirements and business priorities, all of which must be uniquely addressed,” said Víctor Mayoral Vilches, CTO and founder at Alias Robotics. “These systems demand specialized cybersecurity measures that need to happen at the endpoint to guarantee no-human-harm. By integrating [our] robot immune system (RIS) into Kaspersky Industrial CyberSecurity, our clients can now protect their robots with RIS and manage the security of their ICS infrastructure seamlessly via Kaspersky’s solution.”

Anton Shipulin, solution business lead, Kaspersky Industrial CyberSecurity, Kaspersky, added that as OT infrastructure becomes more complex, it is important to add security for all of its various parts and layers.

“Protection measures and tools should also work smoothly with each other to cover the entire environment without any gaps. Considering the growing implementation of industrial robots, this partnership with Alias Robotics allows our customers with robots in their infrastructure to meet the demand for reliable protection.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
DoJ: SolarWinds Attackers Hit Thousands of O365 Inboxes

DoJ: SolarWinds Attackers Hit Thousands of O365 Inboxes

Thousands of Department of Justice (DoJ) email accounts were accessed by SolarWinds attackers last year, the department has confirmed.

The DoJ issued a brief statement yesterday to shed more light on the impact of the attacks, which the government has so far acknowledged and blamed on Russia, but done little else to clarify.

“On December 24 2020, the Department of Justice’s Office of the Chief Information Officer (OCIO) learned of previously unknown malicious activity linked to the global SolarWinds incident that has affected multiple federal agencies and technology contractors, among others. This activity involved access to the department’s Microsoft Office 365 email environment,” it explained.

“After learning of the malicious activity, the OCIO eliminated the identified method by which the actor was accessing the Office 365 email environment. At this point, the number of potentially accessed Office 365 mailboxes appears limited to around 3% and we have no indication that any classified systems were impacted.”

With around 113,000 employees thought to work in the DoJ, this means over 3300 mailboxes could have been accessed by the attackers.

Even if no “classified systems” were impacted, this represents a major security breach that could have given attackers access to strategically useful information and provided a staging post for convincing phishing attacks on other government users.

In fact, the DoJ admitted that the activity it detected constitutes a “major incident” under the Federal Information Security Modernization Act, and said it “is taking the steps consistent with that determination.”

In an update earlier this week, the authorities claimed that fewer than 10 government departments and agencies were affected by the campaign. Others thought to have been infiltrated by the state-backed Russian operatives are the Treasury, State, Homeland Security and Energy departments and the Cybersecurity and Infrastructure Security Agency (CISA).

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Social Media Neuters Trump’s Accounts After Fans Storm Capitol

Social Media Neuters Trump’s Accounts After Fans Storm Capitol

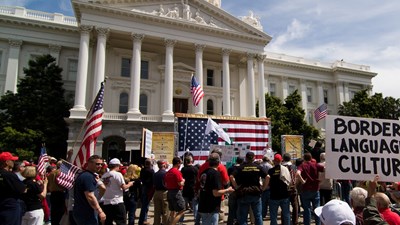
Social media companies have moved swiftly to block posts by Donald Trump in the wake of extraordinary scenes in the US capital that have left four people dead.

Twitter and Facebook both blocked the outgoing President’s accounts following policy violations, removing posts which repeated baseless allegations of election fraud and praised his followers – men and women who at the time were storming Capitol Hill.

Although Twitter has been flagging Trump’s repeated claims of fraud, which he says cost him victory last November, this marks an escalation in its actions.

“As a result of the unprecedented and ongoing violent situation in Washington, D.C., we have required the removal of three @realDonaldTrump Tweets that were posted earlier today for repeated and severe violations of our Civic Integrity policy,” it said in a statement on the platform.

“This means that the account of @realDonaldTrump will be locked for 12 hours following the removal of these Tweets. If the Tweets are not removed, the account will remain locked.”

More worrying for the former reality TV star is that Twitter said it will permanently suspend Trump’s account if he violates Twitter rules in the future.

He currently has 88.7 million followers on the social media platform, which has been a key tool over the past for years for a President that prefers one-way communication with his fanbase to difficult media interviews.

Elsewhere, Facebook and Instagram both locked Trump’s accounts for 24 hours and the former removed a video in which he praised the protesters as ‘patriots.’ YouTube also removed the video.

Facebook has said it is also looking to remove any other content on the platform that may have incited the violence and has banned the #StormtheCapitol hashtag, although some reports suggest that “Stop The Steal” Facebook events and groups remain live. 

As events have proven, social media companies still struggle to take down offensive and dangerous content in time, as they must balance the right to free speech with their other commitments to the rule of law and the safety of users.

In the meantime, lawmakers have since returned to Congress to confirm Joe Biden’s victory last November, with some calling for Trump’s impeachment over the incident.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Over a Third of TMT Firms Hit by Security Breach in 2020

Over a Third of TMT Firms Hit by Security Breach in 2020

Over a third of technology and media companies in the UK suffered a serious cyber-incident last year, according to new data from insurer Hiscox.

The firm claimed that 34% of firms in the technology, media and telecoms (TMT) sector were caught out by a cyber-incident or breach in 2020, leading to a median loss of nearly $40,000.

Phishing accounted for the majority (53%) of incidents, followed by web-based attacks (42%) such as those exploiting web app vulnerabilities.

Nearly a quarter (23%) suffered a ransomware attack where they were able to recover data from backup.

The Hiscox Cyber Readiness Report 2020 ranked the global TMT sector as one of the most frequently targeted by attackers, alongside financial services. It said 44% of firms in each vertical were hit by at least one incident or breach in the previous year.

TMT also ranked as one of the best prepared industries in terms of “cyber-readiness,” although the report clarified that “firms are often forced into becoming experts when they are heavily targeted industries.”

That chimes with the latest UK findings, which revealed that 67% of respondents in TMT are confident in their cyber-readiness, and 85% have a dedicated team or leader in cybersecurity.

“Research shows that the UK tech sector is far from exempt when it comes to major cybersecurity threats – proving that even for those sectors most equipped to deal with threats, vulnerabilities should never be overlooked,” said Stephen Ridley, Hiscox UK cyber-underwriting manager.

“The industry is, however, following best practice and building resilience through spending priorities and dedicated cyber-roles. The findings are a reminder that firms should always look to shift cyber-strategies and improve resilience capabilities.”

In fact, the UK’s TMT firms added £1m on average to their cybersecurity budgets in 2019 versus the previous year, the insurer claimed.

Security spending priorities over the coming year include endpoint malware detection, compliance, supply chain security, customer-facing services/applications and existing vulnerabilities.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Bug Bounty Program Launched to Discover US Army Vulnerabilities

Bug Bounty Program Launched to Discover US Army Vulnerabilities

The Defense Digital Service (DDS) and HackerOne have announced the launch of a new bug bounty program, in which participants will attempt to uncover vulnerabilities in the US Army’s digital systems.

This will be the 11th bug bounty program to take place between the DDS and HackerOne, and the third with the US Department of the Army, offering the chance for military and civilian participants to discover vulnerabilities in exchange for monetary rewards. It will run from January 6 to February 17 2021, and is named Hack the Army 3.0.

Participation is by invitation only to civilian hackers and members of the US military, with bug bounties offered only to civilian hackers when valid security vulnerabilities are found according to the program policy.

The purpose of the program is to highlight security vulnerabilities in the US Army’s digital assets before they can be exploited by nefarious actors. These can then be secured to prevent successful cyber-attacks taking place.

Brig. Gen. Adam C. Volant, US Army cyber-command director of operations commented: “Bug bounty programs are a unique and effective ‘force multiplier’ for safeguarding critical Army networks, systems and data, and build on the efforts of our Army and DoD security professionals.

 “By ‘crowdsourcing’ solutions with the help of the world’s best military and civilian ethical hackers, we complement our existing security measures and provide an additional means to identify and fix vulnerabilities. Hack the Army 3.0 builds upon the successes and lessons of our prior bug bounty programs.”

Marten Mickos, CEO of HackerOne, said: “We are living in a different world today than even just a year ago. Amid disinformation and a global health crisis, citizens are increasingly wary of how, when and where their information is used. For years, the US Department of Defense and respective military branches have successfully strengthened their cybersecurity posture and protected precious data by enlisting the help of ethical hackers on HackerOne. Years later, hacker-powered security is not only a best practice in the US military, but it is now a mandated requirement among civilian federal agencies. There is only one way to secure our connected society, together, and the US Army is leading the charge with this latest challenge.”

DDS has made extensive use of bug bounty challenges of this nature to improve security systems of US government departments. Since Hack the Pentagon was launched back in 2016, it has executed 14 public bounties on external-facing websites and applications in addition to 10 private bounties on sensitive internal systems in the US Department of Defense. These include Hack the Pentagon, Hack the Defense Travel System and Hack the Air Force.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk