Jason Kent, hacker-in-residence at Cequence, walks through online-retail card fraud and what to do about it.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Bellingcat has investigated the near-fatal poisoning of Alexey Navalny by the Russian FSB back in August. The details display some impressive traffic analysis. Navalny got a confession out of one of the poisoners, displaying some masterful social engineering.
Lots of interesting opsec details in all of this.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Scammers are impersonating New York State’s Department of Labor to steal personal information from state residents seeking to claim money from a COVID relief fund.
Targets are sent an email bearing the state logo that appears to come from “noreply@labor.ny.gov.” The email states that by activating their account, the recipient will receive $600 in pandemic aid.
It reads: “Dear Citizen, Due to Covid-19 related issues, NY.GOV will pay $600 for victims who are affected by this pandemic. Please complete the online form to join the aids program. Please click here to active your account. Please do not close out of the browser while completing the account activation. Thank you, New York State.”
A malicious link contained within the email directs the target to a webpage controlled by the attackers. The page has been set up to mimic a page on the New York State government site.
Targets are instructed to fill in a form that asks for their name, address, date of birth, Social Security number, and driver’s license number.
The new phishing attack was detected by researchers at Abnormal Security, who believe that it could have landed in as many as 100,000 mailboxes.
Researchers found that the email’s true sender was “naij30@naija9icevibes.com,” a Panamanian-registered domain that is not associated with the New York state government.
“The email contains an embedded link that should supposedly lead to a NY.GOV site, but actually points to ‘https://thesender[.]org/fjc4’,” wrote researchers. “After clicking on the hypertext, the link redirects to ‘bo2.cloudns.cl/NYU/cnf[.]php,’ a phishing page posing as a legitimate government website.”
“Although this landing page displays the official New York state government logo, the URL is not associated with the New York Department of Labor.”
Researchers noted that the attackers had used the lure of money coupled with an air of authority created by impersonating an official government entity to incentivize the target to act quickly. They also observed that the timing of the attack may have given it added legitimacy.
“Americans have already received pandemic stimulus checks from the government, so a recipient of this email may be more likely to believe that the government is offering additional relief as the pandemic continues,” wrote researchers.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
A computer programmer from Ohio who lied to federal agents about his involvement with an illegal online marketplace has been sentenced to prison.
Michael R. Weigand, also known by his online pseudonyms “Shabang” and “~Shabang~,” concealed his work for illicit black marketplace Silk Road when questioned by an IRS special agent and an FBI agent in January 2019.
Silk Road was used by several thousand criminals around the world to distribute hundreds of millions of dollars’ worth of narcotics and other contraband. The site, which was founded and administered by Ross Ulbricht, aka “Dread Pirate Roberts” and “DPR,” was shut down by law enforcement in October 2013.
Kirtland resident Weigand claimed that he had never opened an account on Silk Road, never transferred Bitcoin to the marketplace, and never performed any services for the Silk Road website.
In fact, the 56-year-old programmer and electrical engineer had been hired by Ulbricht’s senior adviser, Roger Thomas Clark, to work on various aspects of the Silk Road business and laundered $75k in Silk Road proceeds after the site was shut down.
Together, Weigand and Clark worked to identify security vulnerabilities in the Silk Road website. Weigand also supplied technological advice to Ulbricht and Clark, who used the online pseudonym “Variety Jones.”
Despite working directly with Ulbricht and Clark, Weigand told federal agents that he had never communicated with anyone who used the online pseudonyms “Dread Pirate Roberts,” “DPR,” or “Silk Road” and didn’t know the true identity of “Variety Jones.”
Weigand also lied about a trip he took to London in late 2013, after Silk Road had been seized and its founder arrested. The programmer claimed he visited the English capital to talk about a marijuana seed business with Clark’s associate. In reality, he made the journey in order to remove Silk Road evidence from Clark’s London residence after receiving $20,000 in Bitcoin from Clark.
On September 21, Weigand pleaded guilty to one count of making false statements. On December 18, he was sentenced to eight months in prison and three years of supervised release.
Ulbricht is currently serving a double life sentence without parole, plus 40 years. Clark pleaded guilty to conspiring to distribute narcotics, and his sentencing is currently pending.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
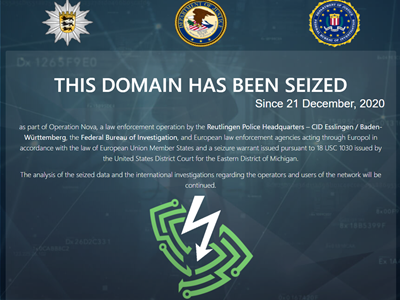
A virtual private network (VPN) used by some of the world’s leading cyber-criminals has been shut down in an international law enforcement action led by German police.
The Safe-Inet service was deactivated yesterday as part of Operation Nova, a coordinated effort that involved the Federal Bureau of Investigation and European law enforcement agencies acting through Europol.
Servers used by the service were taken down, and its infrastructure was seized in France, Germany, the Netherlands, Switzerland, and the United States. Visitors to the Safe-Inet webpage are now greeted by a domain seizure notice.
Safe-Inet was active for eleven years prior to yesterday’s action, describing itself as an international team of “experienced technical specialists who understand how important anonymity on the network is for our clients.”
According to Europol, the service was used by cyber-criminals to carry out serious crimes including e-skimming breaches and ransomware attacks.
“This VPN service was sold at a high price to the criminal underworld as one of the best tools available to avoid law enforcement interception, offering up to 5 layers of anonymous VPN connections,” said a spokesperson for Europol.
Law enforcement observed criminals using Safe-Inet to spy on 250 companies located around the world. Police warned the companies that they may be targeted by ransomware and advised them to beef up their cybersecurity.
Investigations are ongoing in multiple countries to identify and prosecute individuals who used the VPN service to commit crimes.
Operation Nova was led by German Reutlingen Police Headquarters and carried out in the framework of the European Multidisciplinary Platform Against Criminal Threats (EMPACT).
“The investigation carried out by our cybercrime specialists has resulted in such a success thanks to the excellent international cooperation with partners worldwide,” said police president of the Reutlingen Police Headquarters, Udo Vogel.
“The results show that law enforcement authorities are equally as well connected as criminals.”
Head of Europol’s European Cybercrime Centre, Edvardas Šileris, said that cybercriminals couldn’t hide from the law.
“The strong working relationship fostered by Europol between the investigators involved in this case on either side of the world was central in bringing down this service,” said Šileris.
“Criminals can run but they cannot hide from law enforcement, and we will continue working tirelessly together with our partners to outsmart them.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
The Ministry of Justice (MoJ) reported 17 serious data breaches during the last financial year, according to official figures analysed by the Parliament Street think tank.
The UK government department responsible for running the country’s justice system revealed in its annual report 2019-20 that it informed the Information Commissioner’s Office (ICO) of personal data loss incidents affecting a total of 121,355 people.
In the largest of the incidents reported to the ICO, a technical error in a sub-processor made various files on a staff training database briefly accessible to unauthenticated users, resulting in one full and one partial unauthorized download. This disclosed personal information of 120,000 people, including staff data such as names, work locations, staff numbers, national insurance numbers, email addresses and training records.
The second largest incident was caused by a set of prison records being dispatched to the wrong prisoner by mistake. Impacting a total of 143 people, this exposed data relating to the offender’s friends, family, solicitors and MoJ officials.
Other breaches included an applicant’s address and the names of five children being disclosed to the respondent in a domestic violence court case, a lost unencrypted USB stick containing around 33,000 documents from a fraud trial and the leaking of sensitive data about seven staff members following the theft of a laptop and mobile phone.
A further 6425 data incidents were recorded by the MoJ in the 12-month period, although these were not substantial enough to be reported to the ICO. Most (5445) were labelled as ‘unauthorized disclosure’, while 823 were as a result of ‘inadequately protected electronic equipment, devices or paper documents’.
Commenting on the figures, Tim Sadler, CEO at Tessian said: “Data security is, today, well and truly in the hands of the employees. But, sometimes, employees make mistakes – as we can see from the breaches reported by the MoJ to the ICO. It’s human nature; people misplace things, we send emails containing sensitive information to the wrong person, and we click the wrong buttons. And because people are in control of more data than ever before, the risk of that data being accidentally leaked or exposed is only growing.
“As organizations expect people to be responsible for more and more sensitive data, measures must be in place to prevent the mistakes that compromise security. Failure to do so could result in regulatory fines and ruined reputations.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Security firm Cybereason has announced a new partnership with Oracle to enhance protection for customers in the face of a growing cyber-threat landscape.
Firstly, it has adopted the Oracle Cloud Infrastructure to run its automated Cyber Defense Platform. Cybereason said this will improve security and risk posture as well as reduce operational costs for customers using its platform. It placed a particular emphasis on Oracle Cloud Infrastructure’s ability to accelerate artificially intelligent threat detection.
Additionally, the two companies have entered into an agreement to jointly market and sell solutions, helping organizations search for available applications and services that best fit their needs.
Cybereason hopes the partnership will help facilitate its global expansion.
Lior Div, Cybereason CEO and cofounder commented: “We’re excited to collaborate with Oracle to enhance our company’s cloud infrastructure for our award-winning unified protection platform. We chose Oracle Cloud Infrastructure because of its security-first approach and performance. Together, we will deliver unmatched visibility and risk reduction to our global customer base. Additionally, the Oracle Cloud global footprint will enable Cybereason to offer in-country hosting in more locations for meeting regulatory data sovereignty requirements.”
Clay Magouyrk, executive vice president, Oracle Cloud Infrastructure, said: “Cybereason joins a growing roster of companies adopting Oracle Cloud Infrastructure for its leading security and price performance advantages delivered across its global cloud footprint. Adopting Oracle Cloud Infrastructure will enhance Cybereason’s ability to deliver insights into threats across thousands of endpoints and enable customers to stay one step ahead of today’s most nefarious attacks.”
In September, it was announced that a department of the UK’s Ministry of Defence (MoD) added the Oracle Cloud Infrastructure within its MODCLOUD Multi-Hybrid suite of secure services.
Adoption of cloud services has grown substantially this year as organizations looked to function efficiently following the shift to remote working as a result of COVID-19. According to a recent study by Sumo Logic, multi-cloud adoption went up by 70% year-over-year in 2020.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Microsoft, Google, Cisco and a host of other tech giants have added their names to a legal filing supporting Facebook’s case against controversial spyware developer NSO Group.
The social network took the Israeli firm to court after alleging that the latter exploited a vulnerability in WhatsApp which helped its clients spy on over 1400 users globally. It’s believed that the bug or similar ones may also have been used to help Saudi Arabian officials spy on murdered journalist Jamal Khashoggi and his former boss, Jeff Bezos.
NSO Group has argued that its tools are only ever used for legitimate law enforcement purposes, and that, as it sells exclusively to governments, it should benefit from the “sovereign immunity” that means nation states can’t be taken to court.
The case is now at the Court of Appeals after Facebook won the argument in the Northern District of California in July.
That’s where the latest amicus brief filing comes in: it shows support for Facebook’s position from a wide range of tech firms, including rivals. As well as those listed above, the signatories also include lobby group the Internet Association, which counts among its members tech firms including Amazon, Twitter, PayPal, eBay, Uber and Reddit.
Microsoft’s VP of customer security and trust, Tom Burt, argued that NSO Group’s actions should not be granted legal immunity for three reasons.
He claimed that the firm’s tools could end up in the wrong hands, as per the Shadow Brokers hack that resulted in NotPetya and WannaCry, if sophisticated attackers decide to target NSO Group itself, or its government customers.
He also argued that, unlike governments which are bound by international laws and diplomatic norms, private companies like the Israeli firm are only motivated by profit.
Finally, Burt argued that these tools threaten human rights, despite NSO Group’s protestations to the contrary, by expanding the range of autocratic regimes that can access sophisticated spyware.
“Reporting shows foreign governments are using those surveillance tools, bought from PSOAs [private sector offensive actors], to spy on human rights defenders, journalists and others, including US citizens,” he added.
“These tools allow the user to track someone’s whereabouts, listen in on their conversations, read their texts and emails, look at their photographs, steal their contacts list, download their data, review their internet search history and more.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk