Finnish Data Theft and Extortion

The Finnish psychotherapy clinic Vastaamo was the victim of a data breach and theft. The criminals tried extorting money from the clinic. When that failed, they started extorting money from the patients:

Neither the company nor Finnish investigators have released many details about the nature of the breach, but reports say the attackers initially sought a payment of about 450,000 euros to protect about 40,000 patient records. The company reportedly did not pay up. Given the scale of the attack and the sensitive nature of the stolen data, the case has become a national story in Finland. Globally, attacks on health care organizations have escalated as cybercriminals look for higher-value targets.

[…]

Vastaamo said customers and employees had “personally been victims of extortion” in the case. Reports say that on Oct. 21 and Oct. 22, the cybercriminals began posting batches of about 100 patient records on the dark web and allowing people to pay about 500 euros to have their information taken down.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Payment Processing Giant TSYS: Ransomware Incident “Immaterial” to Company

Payment card processing giant TSYS suffered a ransomware attack earlier this month. Since then reams of data stolen from the company have been posted online, with the attackers promising to publish more in the coming days. But the company says the malware did not jeopardize card data, and that the incident was limited to administrative areas of its business.

Headquartered in Columbus, Ga., Total System Services Inc. (TSYS) is the third-largest third-party payment processor for financial institutions in North America, and a major processor in Europe.

TSYS provides payment processing services, merchant services and other payment solutions, including prepaid debit cards and payroll cards. In 2019, TSYS was acquired by financial services firm Global Payments Inc. [NYSE:GPN].

On December 8, the cybercriminal gang responsible for deploying the Conti ransomware strain (also known as “Ryuk“) published more than 10 gigabytes of data that it claimed to have removed from TSYS’s networks.

Conti is one of several cybercriminal groups that maintains a blog which publishes data stolen from victims in a bid to force the negotiation of ransom payments. The gang claims the data published so far represents just 15 percent of the information it offloaded from TSYS before detonating its ransomware inside the company.

In a written response to requests for comment, TSYS said the attack did not affect systems that handle payment card processing.

“We experienced a ransomware attack involving systems that support certain corporate back office functions of a legacy TSYS merchant business,” TSYS said. “We immediately contained the suspicious activity and the business is operating normally.”

According to Conti, the “legacy” TSYS business unit hit was Cayan, an entity acquired by TSYS in 2018 that enables payments in physical stores and mobile locations, as well as e-commerce.

Conti claims prepaid card data was compromised, but TSYS says this is not the case.

“Transaction processing is conducted on separate systems, has continued without interruption and no card data was impacted,” the statement continued. “We regret any inconvenience this issue may have caused. This matter is immaterial to the company.”

TSYS declined to say whether it paid any ransom. But according to Fabian Wosar, chief technology officer at computer security firm Emsisoft, Conti typically only publishes data from victims that refuse to negotiate a ransom payment.

Some ransomware groups have shifted to demanding two separate ransom payments; one to secure a digital key that unlocks access to servers and computers held hostage by the ransomware, and a second in return for a promise not to publish or sell any stolen data. However, Conti so far has not adopted the latter tactic, Wosar said.

“Conti almost always does steal data, but we haven’t seen them negotiating for leaks and keys separately,” he explained. “For the negotiations we have seen it has always been one price for everything (keys, deletion of data, no leaks etc.).”

According to a report released last month by the Financial Services Information Sharing and Analysis Center (FS-ISAC), an industry consortium aimed at fighting cyber threats, the banking industry remains a primary target of ransomware groups. FS-ISAC said at least eight financial institutions were hit with ransomware attacks in the previous four months. The report notes that by a wide margin, Ryuk continues to be the most prolific ransomware threat targeting financial services firms.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Alleged Cyber-Stalker Indicted for Murder

Alleged Cyber-Stalker Indicted for Murder

A man from Texas, charged in January with cyber-stalking realtors across the United States, has been indicted for capital murder in the deaths of two women.

Andy Castillo was arrested on January 6 for allegedly cyber-stalking as many as 100 realtors in up to 22 different states. 

The 57-year-old Lubbock resident was accused of sending sexually explicit messages and pornographic images to agents via text message. 

Realtors also received messages containing images of their own children that had been downloaded from social media along with descriptions of the ways in which the sender wanted to sexually assault the minors.

The McLennan County Sheriff’s Office began investigating Castillo in late December 2019 after receiving complaints from seven Waco-based realtors who received sexually explicit images and messages from unknown numbers.

Investigators said that the stalker used multiple phone numbers and an app to mask his identity but eventually made a mistake that allowed his digital trail to be followed. 

In January, Castillo was charged with one count of cyber-stalking and two counts of criminal solicitation-aggravated sexual assault of a child, relating to alleged crimes in Waco.

Now a grand jury has indicted Castillo for capital murder over the deaths of roommates Cynthia Palacio and Linda Carbajal, who resided in Lubbock. 

Palacio’s partially clothed body was discovered on a rural road in Slaton, Texas, in July 2003. Carbajal’s body was found nine months later on a dirt road in northern Lubbock County. Both women were aged 21 at the time of their demise.

Cold case investigators revealed in September that DNA evidence found at both murder scenes had been linked to Castillo. 

According to court documents, a match was found between Castillo’s DNA and DNA evidence that was originally taken from Palacio’s thigh, from underneath her fingernails, as well as from the necklace and blouse she had been wearing on the day she died from asphyxiation.  

After Castillo’s arrest relating to the Waco-area cases, authorities were able to obtain a DNA sample and match it to the DNA found with Palacio.

Castillo is currently being detained in Lubbock County Detention Center on a $500,000 bond. 

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Vulnerabilities Found in Multiple GE Imaging Systems

Vulnerabilities Found in Multiple GE Imaging Systems

Critical vulnerabilities have been found in over a hundred different GE Healthcare imaging and ultrasound products commonly used at hospitals throughout the USA.

If exploited, the vulnerabilities could allow an attacker to gain access to sensitive personal health information (PHI), alter data, and impact the availability of the medical device.

The flaws were discovered by a team of researchers at CyberMDX that launched an investigation after noticing similar patterns of unsecured communications between medical devices and the corresponding vendor’s servers. 

Researchers observed the issue occurring across several different health delivery organizations (HDOs). 

GE Healthcare has confirmed that the vulnerabilities impact 104 radiological devices, including CT scanners, PET machines, molecular imaging devices, MRI machines, mammography devices, x-ray machines, and ultrasound devices. Certain workstations and imaging devices used in surgery are also at risk.

The healthcare provider has identified mitigations for specific products and releases and has said that it will take proactive measures to ensure proper configuration of the product firewall protection and change default passwords on impacted devices where possible.

“Over the past few months we’ve seen a steady rise in the targeting of medical devices and networks, and the medical industry is unfortunately learning the hard way the consequences of previous oversights,” said Elad Luz, head of research at CyberMDX. 

“Protecting medical devices so that hospitals can ensure quality care is of utmost importance. We must continue to eliminate easy access points for hackers and ensure the highest level of patient safety is upheld across all medical facilities.”

The discovery of the vulnerabilities prompted the United States Cybersecurity and Infrastructure Agency (CISA) to issue an ICS Medical Advisory, ICSMA-20-343-01, yesterday.

CISA advised that the vulnerabilities were exploitable remotely and that attackers only required a low skill level to abuse them.

“If exploited, these vulnerabilities could allow an attacker to gain access to affected devices in a way that is comparable with GE (remote) service user privileges,” warned CISA.

“A successful exploitation could expose sensitive data such as a limited set of patient health information (PHI) or could allow the attacker to run arbitrary code, which might impact the availability of the system and allow manipulation of PHI.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

IT Workers Fear Becoming Obsolete in Cyber Roles

IT Workers Fear Becoming Obsolete in Cyber Roles

Some IT leaders in the UK expect to be replaced in their jobs by artificial intelligence within the next ten years, according to new research by cloud security provider Trend Micro

Researchers interviewed 500 IT directors and managers, CIOs, and CTOs about what kinds of threats they reckon will be most pervasive over the next few years.

Key findings to emerge were that more than two-fifths (41%) of IT leaders believe that AI will replace their role by 2030. Only 9% of respondents were confident that their job would not be performed by AI within a decade. 

Nearly a third (32%) said they thought the technology would one day lead to the total automation of all cybersecurity, with little need for human intervention.

Asked about data access in the future, around a quarter (24%) predicted that unauthorized access would be impossible by 2030 because access would be fully tied to an individual’s DNA or biometric information.

Trend Micro’s technical director, Bharat Mistry, said IT leaders shouldn’t lose sleep over the study’s revelations, because other roles will be created in the future, and AI relies upon a human touch.

“While AI is a useful tool in helping us to defend against threats, its value can only be harnessed in combination with human expertise,” said Mistry.

“We shouldn’t worry about jobs becoming obsolete,” he added, as “the profession will certainly adapt and evolve in new ways.”

Another prediction made by 22% of UK IT bosses is that by 2025, most organizations will have significantly reduced investment in property as remote working becomes de rigeur.

Another IT prophecy, and one that echoes a storyline in Charlie Brooker’s TV show Black Mirror, is that early adopters of “digital immortality” (AI facsimiles of a person created after their death) will start to appear online in the next five years.

UK IT bosses expect the rollout of nationwide 5G to have a huge impact on the British Isles, with 21% predicting that it will entirely transform network and security infrastructure. 

In the near future, 45% of leaders said, they plan to focus investment on staff training and education with a particular focus on working remotely. 

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Data Loss Reports to ICO Increase Once Again

Data Loss Reports to ICO Increase Once Again

The number of incidents reported to the Information Commissioner’s Office (ICO) in the second quarter of 2020 has increased by over a thousand in comparison to Q1.

In the previous report for Q1, there were 1446 reported incidents, including 412 cited as cybersecurity events. However, for Q2, there were 2594 reported incidents, which included 737 cybersecurity events, including 258 for phishing, 152 for ransomware and 190 for unauthorized access.

Among the non-cybersecurity incidents, there were 402 instances of data being emailed to the wrong person, 266 of data posted or faxed to the incorrect recipient and 141 of loss or theft of paperwork or data left in insecure locations.

With the “non cyber-incidents” still fairly prominent, Infosecurity asked speaker and author Raef Meeuwisse if he saw this ever reducing. “Whenever you get down to trusting human actions, you will always get a certain amount of human error,” he said. “Most enterprises now have various process and technology safeguards in place to reduce the possibility of human error – but there is only one way to totally get rid of human error – and that is to get rid of all the humans.

“The safeguards most enterprises have mean that although data emailed to incorrect recipient was high in terms of numbers of incidents, in most of the cases, it should not have been any significant number of records that were exposed.”

Meanwhile, Rick Goud, CEO and founder of Zivver, predicted that this type of “non cyber-incident” will become a bigger issue due to an increased digital workforce. “Digital transformation will most likely continue in 2021, but if transformation does not go hand-in-hand with providing employees with the right tools to make better decisions, many companies will see a significant increase in data leaks,” he said.

Also, considering that 141 incidents were due to loss or theft of paperwork or data left in insecure locations, how much of an issue has the move to remote working had? Goud said: “In Q2, people suddenly had to work from home, still were printing stuff, but had no place to securely dispose of the information. I expect this to drop in 2021 as people will adapt to the possibilities of digital and will print less or fax less, because both habits – and also company policies – will change.”

Meeuwisse agreed, saying that the downside to working from home is that if you need to print something out, you are no longer doing so in a secure work location.

He said: “For example, your home may not have a shredder, or lockable desk drawer and not everyone in your household may understand the significance or sensitivity of any document that is lying around. The trick is to keep printing to a minimum, keep any confidential or sensitive material locked away and always shred or burn confidential documents once they are no longer required.

“You may be in your own home – but that does not mean that everyone around you has the same understanding and regard for the materials you may need to use for your work. Most ‘loss or theft’ incidents involving confidential documents in home environments are accidental – but such incidents can be embarrassing and difficult for the employee and his, her or their company.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Winners of the 2020 Tech Trailblazers Awards Announced

Winners of the 2020 Tech Trailblazers Awards Announced

The winners of the 2020 Tech Trailblazers Awards have been announced, with a number of early-stage tech companies recognized for their outstanding innovations during what has been a turbulent year.

There was lots of competition this year, with a record number of entries despite the challenges posed by COVID-19, which is testament to the growing importance of the tech and cybersecurity sectors as a result of changing working and home practices emanating from the global crisis.

A total of 15 winners were selected by a combination of public vote and a panel of judges, which included Infosecurity’s editor Michael Hill.

The coveted Tech Trailblazer of the Year Award, which celebrates individual male and female executives who have delivered outstanding innovation or change, went to Stephanie Fohn of NeuVector and Dean Sysman of Axonius in the female and male categories, respectively. The runners-up in the female category were Grace Waters of Codastra and Melissa Wong of Retail Zipline, while runners-up in the male section were Patrick Harr of SlashNext and Tim Hinrichs of Styra, Inc.

The Firestarter award went to Codastra, with the runners-up prizes going to Eldir (Pty) Ltd, NexBotix Ltd and Vastmindz.

Across the 12 major enterprise categories, this year’s winners were as follows:

Rose Ross, founder of the Tech Trailblazers Awards, commented: “Despite the difficulties caused by the pandemic, we received a record number of entries this year – up by 50% from last year. We congratulate all the winners both on their innovation and on their efforts to bring their innovations to market – they are all outstanding in their fields.”

This has been the ninth edition of the Tech Trailblazers Awards since it first started back in 2012 to highlight the achievements of enterprise technology startups. Many previous winners and runners-up have gone on to receive substantial investment while others have been acquired. To qualify, businesses have to be under six years old, privately funded and at C-series funding or below.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Researchers Uncover New Cyber-Espionage Campaign Targeting Middle Eastern Politicians

Researchers Uncover New Cyber-Espionage Campaign Targeting Middle Eastern Politicians

A new cyber-espionage campaign using popular social media and cloud platforms to target high ranking political figures has been revealed following an investigation by Cybereason.

The campaign has been observed to operate primarily across the Middle East, and the researchers believe it is aimed at high ranking political figures and government officials in the region. Cybereason has attributed the campaign to the politically-motivated APT group Molerats, which has been active in the Middle East since 2012. The threat actors have previously used the Spark and Pierogi backdoors to execute targeted attacks against Palestinian officials.

The new campaign utilizes three previously unidentified malware variants: two backdoors named SharpStage and Dropbox and a downloader called MoleNet. These are designed to help leverage Facebook, Dropbox, Google Docs and Simplenote for command and control to exfiltrate sensitive data from victims’ computers.

Cybereason added that these new malware variants were used in conjunction with the Spark backdoor previously attributed to Molerats, as well as payloads including the open-source Quasar RAT known to have been employed by the group.

Email phishing is another aspect of the espionage operation, with themes focusing on sensitive political issues in the Middle East including Israel-Saudi relations, Hamas elections and even a secretive meeting between the US Secretary of State, the Israeli Prime Minister and the Crown Prince of Saudi Arabia.

Lior Div, co-founder and CEO at Cybereason, commented: “While it’s no surprise to see threat actors take advantage of politically charged events to fuel their phishing campaigns, it is concerning to see an increase in social media platforms being used for issuing command and control instructions and other legitimate cloud services being used for data exfiltration activities.

“This puts the onus even more on the defenders to be hyper-vigilant with regard to potentially malicious network traffic connecting to legitimate services, and it underscores the need to adopt an operation-centric approach to expose these more subtle indicators of behavior.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

#BHEU: Focus on Security Fundamentals, Not Adversarial Sophistication

#BHEU: Focus on Security Fundamentals, Not Adversarial Sophistication

Focus on the fundamentals of security to ensure you keep on top of incidents and have the best company culture.

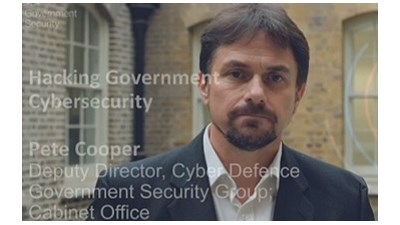
Speaking in the opening keynote of Black Hat Europe 2020, Pete Cooper, deputy director for cyber-defense at the Cabinet Office, said “hacking is a mindset” and it is about being resourceful and finding solutions.

Comparing his time in government to his time in the RAF, he said that it is cool to fly Tornados, but preparation needed to be done in “learning the basics, building the applications and learning key critical skills, as you can learn how to fly and do the fundamentals every single time without thinking about it and the fundamentals have to become second nature.” This is because, irrespective of what the adversary throws at you, you have to be able to do the basics right.

He said: “When it all starts to go wrong, it’s your fundamentals that will keep you moving forwards and doing the right thing.” He also said that, in cybersecurity, it is very easy to get excited about “the latest sharp, pointy thing” but being able to detect and protect against cybersecurity attacks, and minimizing those attacks, enables everything else.

Winning and losing is not defined by technology, he added, as adversaries do not have access to technology that defenders do, and “our thinking allows us to make the most of our technology.” Also, there needs to be assurance that technology is safe out of the box and with trust in the system to know how it will work. “There is a key element in getting it right as the user can get it wrong,” he said.

This is why a culture of safety is important, where an engaged culture begins with reporting “problems, errors and near misses” and where acceptable and unacceptable behavior is understood. “If your organization or team is raising these issues, then you need to have a flexible culture, as the adversary has evolved and therefore we need to do so too, as security is not a static task and we need the flexibility at both a technical and organizational layers to respond to our challenges,” he said.

When those challenges are understood, there needs to be a culture of learning so it is about more than fixing, and understanding why and how something happened “so we can change and adapt all the way through.” If users are empowered, it brings the power of the individual to the organization, and the culture will help you understand that unique risk to your data and company.

Cooper said there similarities between his time in the RAF and what he does now, but his former career helped shape his thinking “and it is basics such as staying absolutely focused on the fundamentals, and no matter what your adversaries throw at you, you keep going back to those fundamentals and manage to keep plugging through.” He explained that incidents are the tip of the iceberg, and there is a need to understand what the ideas and problems are and to bring together skills, knowledge and data.

Concluding, he said this will require collaboration which takes time and effort, but if it is done, we can form “shared perspectives” and make a difference across “joint horizons” in partnering with communities across the industry, and the better it will be for everyone in tackling key risks we will face going forwards.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

How 2020 Has Changed the Data Privacy Landscape

How 2020 Has Changed the Data Privacy Landscape

The most important data protection and privacy events from 2020 and their impact on the US over the long term were discussed during the webinar Data Protection and Privacy: Year in Review & 2021 Outlook.

The first area highlighted was the passing of the California Privacy Rights Act (CPRA) 2020 into law last month, amending the California Consumer Privacy Act (CCPA) of 2018. Scott Giordano, VP and senior counsel, privacy and compliance at Spirion noted: “This is essentially a national standard; it’s changed the California constitution,” bestowing “new rights for consumers and new responsibilities for businesses.” He explained that the law has been heavily influenced by the European General Data Protection Regulation (GDPR) legislation, with changes including allowing consumers to direct businesses not to use or disclose their SPI, and introducing the concept of non-personalized advertising, defined as advertising and marketing not based on a consumers’ past behavior.

It will also see the creation of a new government agency to enforce the law, which is a first for the US. “That says privacy and data protection are here to stay,” commented K Royal, associate general counsel at TrustArc.

Applying to data collected on or after January 2022, the new law will have a particularly major impact on giant tech firms such as Facebook and Google, according to Giordano. “It’s a big change and I don’t think anyone appreciates just how big it’s going to be until enforcement starts,” he added.

The other huge event this year was the Schrems II court decision in July concerning data transfers. This has invalidated the US-EU Privacy Shield, therefore causing a lot of issues for US businesses operating in Europe, especially as the ruling took effect immediately. While standard contractual clauses as a mechanism for transfers remain valid, this must be done on a case-by-case basis, with organizations assessing whether the laws of the country data is being transferred to will impact an individual’s right to privacy through government surveillance.

Royal explained that this is an ongoing situation, and the EU recently released recommendations for businesses including the criteria that a third country’s data privacy legislation needs to meet in order to justify surveillance; however, this is an area laws in the US do not currently reach according to these standards.

Giordano noted: “There’s a lot to be done to get on board with what the EU is asking for.”

In light of these two profound changes in 2020 as well as the growth of data privacy legislation worldwide, organizations will need to do plenty to prepare to meet the new global landscape over the next three to five years. Giordano set out six action areas to be implemented during this timeframe: implementing a comprehensive framework to build consistency, having data inventory, introducing training on standards for teams, understanding individual rights, vendor management and oversight, and notice/transparency.

Royal added: “The key to moving forward in the next three to five years is to make sure that you are prepared with the general privacy practices that are pretty consistent across all privacy laws.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk