Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Author: admin
Scalper-Bots Shake Down Desperate PS5, Xbox Series X Shoppers
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Colossal Intel Update Anchored by Critical Privilege-Escalation Bugs
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Apple to Deliver ‘Privacy Labels’ for Apps, Revealing Data-Sharing Details
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Microsoft Teams Users Under Attack in ‘FakeUpdates’ Malware Campaign
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Ghimob Android Banking Trojan Targets 153 Mobile Apps
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
2020 Was a Secure Election
Over at Lawfare: “2020 Is An Election Security Success Story (So Far).”
What’s more, the voting itself was remarkably smooth. It was only a few months ago that professionals and analysts who monitor election administration were alarmed at how badly unprepared the country was for voting during a pandemic. Some of the primaries were disasters. There were not clear rules in many states for voting by mail or sufficient opportunities for voting early. There was an acute shortage of poll workers. Yet the United States saw unprecedented turnout over the last few weeks. Many states handled voting by mail and early voting impressively and huge numbers of volunteers turned up to work the polls. Large amounts of litigation before the election clarified the rules in every state. And for all the president’s griping about the counting of votes, it has been orderly and apparently without significant incident. The result was that, in the midst of a pandemic that has killed 230,000 Americans, record numbers of Americans voted — and voted by mail — and those votes are almost all counted at this stage.
On the cybersecurity front, there is even more good news. Most significantly, there was no serious effort to target voting infrastructure. After voting concluded, the director of the Cybersecurity and Infrastructure Security Agency (CISA), Chris Krebs, released a statement, saying that “after millions of Americans voted, we have no evidence any foreign adversary was capable of preventing Americans from voting or changing vote tallies.” Krebs pledged to “remain vigilant for any attempts by foreign actors to target or disrupt the ongoing vote counting and final certification of results,” and no reports have emerged of threats to tabulation and certification processes.
A good summary.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Patch Tuesday, November 2020 Edition
Adobe and Microsoft each issued a bevy of updates today to plug critical security holes in their software. Microsoft’s release includes fixes for 112 separate flaws, including one zero-day vulnerability that is already being exploited to attack Windows users. Microsoft also is taking flak for changing its security advisories and limiting the amount of information disclosed about each bug.
Some 17 of the 112 issues fixed in today’s patch batch involve “critical” problems in Windows, or those that can be exploited by malware or malcontents to seize complete, remote control over a vulnerable Windows computer without any help from users.
Most of the rest were assigned the rating “important,” which in Redmond parlance refers to a vulnerability whose exploitation could “compromise the confidentiality, integrity, or availability of user data, or of the integrity or availability of processing resources.”
A chief concern among all these updates this month is CVE-2020-17087, which is an “important” bug in the Windows kernel that is already seeing active exploitation. CVE-2020-17087 is not listed as critical because it’s what’s known as a privilege escalation flaw that would allow an attacker who has already compromised a less powerful user account on a system to gain administrative control. In essence, it would have to be chained with another exploit.
Unfortunately, this is exactly what Google researchers described witnessing recently. On Oct. 20, Google released an update for its Chrome browser which fixed a bug (CVE-2020-15999) that was seen being used in conjunction with CVE-2020-17087 to compromise Windows users.
If you take a look at the advisory Microsoft released today for CVE-2020-17087 (or any others from today’s batch), you might notice they look a bit more sparse. That’s because Microsoft has opted to restructure those advisories around the Common Vulnerability Scoring System (CVSS) format to more closely align the format of the advisories with that of other major software vendors.
But in so doing, Microsoft has also removed some useful information, such as the description explaining in broad terms the scope of the vulnerability, how it can be exploited, and what the result of the exploitation might be. Microsoft explained its reasoning behind this shift in a blog post.
Not everyone is happy with the new format. Bob Huber, chief security officer at Tenable, praised Microsoft for adopting an industry standard, but said the company should consider that folks who review Patch Tuesday releases aren’t security practitioners but rather IT counterparts responsible for actually applying the updates who often aren’t able (and shouldn’t have to) decipher raw CVSS data.
“With this new format, end users are completely blind to how a particular CVE impacts them,” Huber said. “What’s more, this makes it nearly impossible to determine the urgency of a given patch. It’s difficult to understand the benefits to end-users. However, it’s not too difficult to see how this new format benefits bad actors. They’ll reverse engineer the patches and, by Microsoft not being explicit about vulnerability details, the advantage goes to attackers, not defenders. Without the proper context for these CVEs, it becomes increasingly difficult for defenders to prioritize their remediation efforts.”
Dustin Childs with Trend Micro‘s Zero Day Initiative also puzzled over the lack of details included in Microsoft advisories tied to two other flaws fixed today — including one in Microsoft Exchange Server (CVE-2020-16875) and CVE-2020-17051, which is a scary-looking weakness in the Windows Network File System (NFS).
The Exchange problem, Childs said, was reported by the winner of the Pwn2Own Miami bug finding contest.
“With no details provided by Microsoft, we can only assume this is the bypass of CVE-2020-16875 he had previously mentioned,” Childs said. “It is very likely he will publish the details of these bugs soon. Microsoft rates this as important, but I would treat it as critical, especially since people seem to find it hard to patch Exchange at all.”
Likewise, with CVE-2020-17051, there was a noticeable lack of detail for bug that earned a CVSS score of 9.8 (10 is the most dangerous).
“With no description to work from, we need to rely on the CVSS to provide clues about the real risk from the bug,” Childs said. “Consider this is listed as no user interaction with low attack complexity, and considering NFS is a network service, you should treat this as wormable until we learn otherwise.”
Separately, Adobe today released updates to plug at least 14 security holes in Adobe Acrobat and Reader. Details about those fixes are available here. There are no security updates for Adobe’s Flash Player, which Adobe has said will be retired at the end of the year. Microsoft, which has bundled versions of Flash with its Web browsers, says it plans to ship an update in December that will remove Flash from Windows PCs, and last month it made the removal tool available for download.
Windows 10 users should be aware that the operating system will download updates and install them on its own schedule, closing out active programs and rebooting the system. If you wish to ensure Windows has been set to pause updating so you can back up your files and/or system, see this guide.
But please do back up your system before applying any of these updates. Windows 10 even has some built-in tools to help you do that, either on a per-file/folder basis or by making a complete and bootable copy of your hard drive all at once.
As always, if you experience glitches or problems installing any of these patches this month, please consider leaving a comment about it below; there’s a better-than-even chance other readers have experienced the same and may chime in here with some helpful tips.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Ransomware Group Turns to Facebook Ads
It’s bad enough that many ransomware gangs now have blogs where they publish data stolen from companies that refuse to make an extortion payment. Now, one crime group has started using hacked Facebook accounts to run ads publicly pressuring their ransomware victims into paying up.
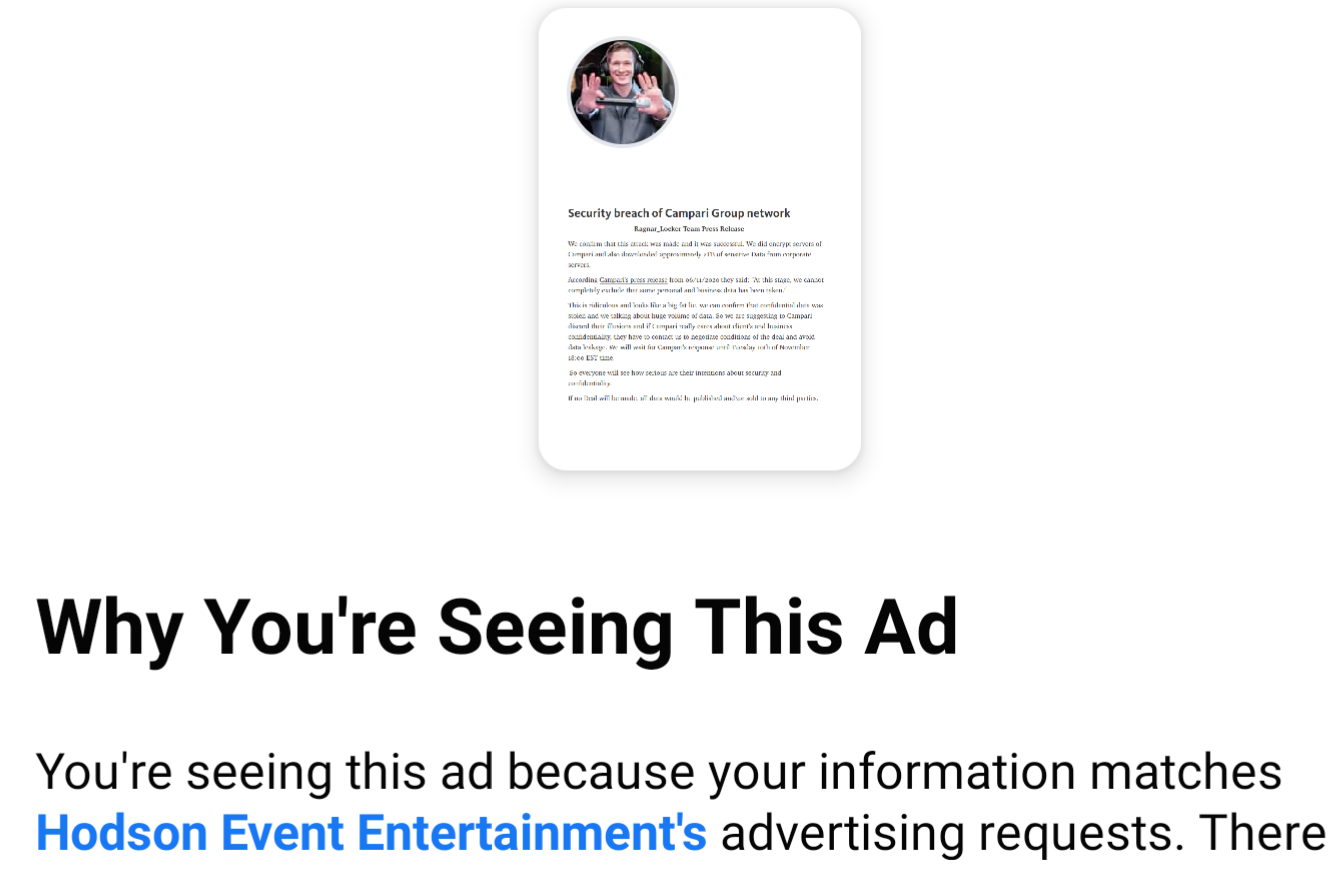
On the evening of Monday, Nov. 9, an ad campaign apparently taken out by the Ragnar Locker Team began appearing on Facebook. The ad was designed to turn the screws to the Italian beverage vendor Campari Group, which acknowledged on Nov. 3 that its computer systems had been sidelined by a malware attack.
On Nov. 6, Campari issued a follow-up statement saying “at this stage, we cannot completely exclude that some personal and business data has been taken.”
“This is ridiculous and looks like a big fat lie,” reads the Facebook ad campaign from the Ragnar crime group. “We can confirm that confidential data was stolen and we talking about huge volume of data.”
The ad went on to say Ragnar Locker Team had offloaded two terabytes of information and would give the Italian firm until 6 p.m. EST today (Nov. 10) to negotiate an extortion payment in exchange for a promise not to publish the stolen files.
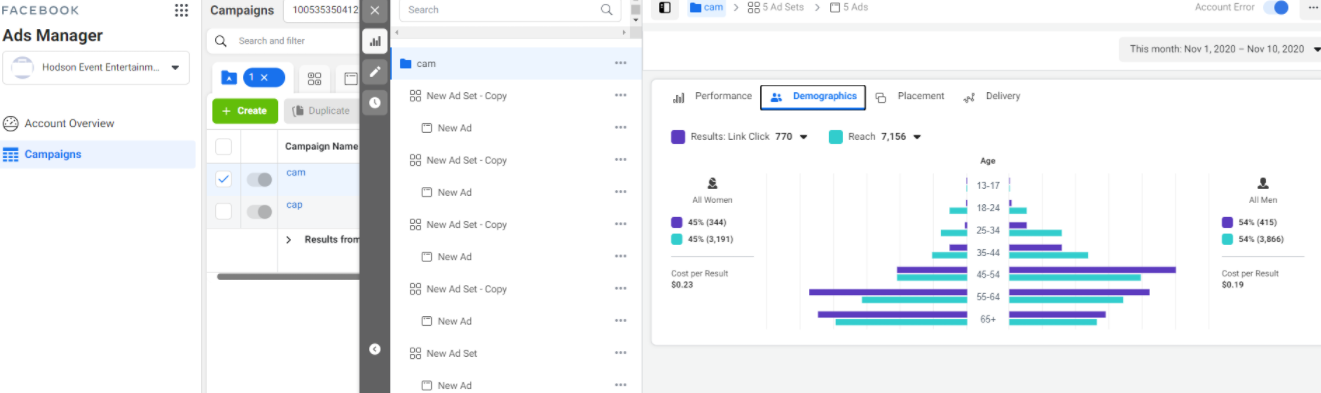
The Facebook ad blitz was paid for by Hodson Event Entertainment, an account tied to Chris Hodson, a deejay based in Chicago. Contacted by KrebsOnSecurity, Hodson said his Facebook account indeed was hacked, and that the attackers had budgeted $500 for the entire campaign.
“I thought I had two-step verification turned on for all my accounts, but now it looks like the only one I didn’t have it set for was Facebook,” Hodson said.
Hodson said a review of his account shows the unauthorized campaign reached approximately 7,150 Facebook users, and generated 770 clicks, with a cost-per-result of 21 cents. Of course, it didn’t cost the ransomware group anything. Hodson said Facebook billed him $35 for the first part of the campaign, but apparently detected the ads as fraudulent sometime this morning before his account could be billed another $159 for the campaign.
It’s not clear whether this was an isolated incident, or whether the fraudsters also ran ads using other hacked Facebook accounts. A spokesperson for Facebook said the company is still investigating the incident. A request for comment sent via email to Campari’s media relations team was returned as undeliverable.
But it seems likely we will continue to see more of this and other mainstream advertising efforts by ransomware groups going forward, even if victims really have no expectation that paying an extortion demand will result in criminals actually deleting or not otherwise using stolen data.
Fabian Wosar, chief technology officer at computer security firm Emsisoft, said some ransomware groups have become especially aggressive of late in pressuring their victims to pay up.
“They have also started to call victims,” Wosar said. “They’re outsourcing to Indian call centers, who call victims asking when they are going to pay or have their data leaked.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Paralegal Admits Role in Outing Iowa Witnesses

A former contractor with the United States Department of Justice has admitted her role in exposing the identities of cooperating witnesses in a federal drug-trafficking investigation.
Danielle Taff was employed as a contractor paralegal at the US Attorney’s Office for the Southern District of Iowa from approximately June 2017 to June 2018.
The 37-year-old resident of Ankeny, Iowa, was hired to work exclusively on matters related to civil forfeiture. However, she admitted using her DOJ computer to access criminal files stored on the district’s shared electronic data storage drive.
Among the files unlawfully accessed by Taff were reports of law enforcement interviews with at least two individuals who cooperated with the district in a drug-trafficking investigation.
Taff confessed to taking approximately 30 photographs of sensitive, non-public documents relating to that investigation with her cell phone on May 16, 2018, and sharing the images with a friend.
The friend, referred to in court documents as Person A, subsequently sent the photographs to several different individuals via the social media app Facebook.
“As a result, in October 2018, other individuals posted those photographs to a Facebook group dedicated to outing ‘snitches,’ or law enforcement cooperators, in the Des Moines, Iowa region,” said the DOJ in a statement released on November 6.
“Among other sensitive information, the photographs taken by Taff and subsequently posted on Facebook identified at least two cooperators in the drug-trafficking investigation by name and other personal identifiers.”
According to the Daily Beast, Taff passed the sensitive documents on to a friend during a coffee date. The documents, which contained the informants’ names, addresses, and phone numbers, then ended up on a “stop snitching” Facebook page with nearly 10,000 members.
Taff admitted unlawfully using her government computer to access government records and providing sensitive, non-public information to another individual. On November 6, Taff pleaded guilty to one count of fraud and related activity in connection with computers before US District Judge Stephanie Rose of the Southern District of Iowa.
An investigation into the case is being undertaken by the Department of Justice Office of the Inspector General, Chicago Field Division.
A sentencing date has not been scheduled.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk