Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Author: admin
Barnes & Noble Hack: A Reading List for Phishers and Crooks
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
US Cyber Command and Microsoft Are Both Disrupting TrickBot
Earlier this month, we learned that someone is disrupting the TrickBot botnet network.
Over the past 10 days, someone has been launching a series of coordinated attacks designed to disrupt Trickbot, an enormous collection of more than two million malware-infected Windows PCs that are constantly being harvested for financial data and are often used as the entry point for deploying ransomware within compromised organizations.
On Sept. 22, someone pushed out a new configuration file to Windows computers currently infected with Trickbot. The crooks running the Trickbot botnet typically use these config files to pass new instructions to their fleet of infected PCs, such as the Internet address where hacked systems should download new updates to the malware.
But the new configuration file pushed on Sept. 22 told all systems infected with Trickbot that their new malware control server had the address 127.0.0.1, which is a “localhost” address that is not reachable over the public Internet, according to an analysis by cyber intelligence firm Intel 471.
A few days ago, the Washington Post reported that it’s the work of US Cyber Command:
U.S. Cyber Command’s campaign against the Trickbot botnet, an army of at least 1 million hijacked computers run by Russian-speaking criminals, is not expected to permanently dismantle the network, said four U.S. officials, who spoke on the condition of anonymity because of the matter’s sensitivity. But it is one way to distract them at least for a while as they seek to restore operations.
The network is controlled by “Russian speaking criminals,” and the fear is that it will be used to disrupt the US election next month.
The effort is part of what Gen. Paul Nakasone, the head of Cyber Command, calls “persistent engagement,” or the imposition of cumulative costs on an adversary by keeping them constantly engaged. And that is a key feature of CyberCom’s activities to help protect the election against foreign threats, officials said.
Here’s General Nakasone talking about persistent engagement.
Microsoft is also disrupting Trickbot:
We disrupted Trickbot through a court order we obtained as well as technical action we executed in partnership with telecommunications providers around the world. We have now cut off key infrastructure so those operating Trickbot will no longer be able to initiate new infections or activate ransomware already dropped into computer systems.
[…]
We took today’s action after the United States District Court for the Eastern District of Virginia granted our request for a court order to halt Trickbot’s operations.
During the investigation that underpinned our case, we were able to identify operational details including the infrastructure Trickbot used to communicate with and control victim computers, the way infected computers talk with each other, and Trickbot’s mechanisms to evade detection and attempts to disrupt its operation. As we observed the infected computers connect to and receive instructions from command and control servers, we were able to identify the precise IP addresses of those servers. With this evidence, the court granted approval for Microsoft and our partners to disable the IP addresses, render the content stored on the command and control servers inaccessible, suspend all services to the botnet operators, and block any effort by the Trickbot operators to purchase or lease additional servers.
To execute this action, Microsoft formed an international group of industry and telecommunications providers. Our Digital Crimes Unit (DCU) led investigation efforts including detection, analysis, telemetry, and reverse engineering, with additional data and insights to strengthen our legal case from a global network of partners including FS-ISAC, ESET, Lumen’s Black Lotus Labs, NTT and Symantec, a division of Broadcom, in addition to our Microsoft Defender team. Further action to remediate victims will be supported by internet service providers (ISPs) and computer emergency readiness teams (CERTs) around the world.
This action also represents a new legal approach that our DCU is using for the first time. Our case includes copyright claims against Trickbot’s malicious use of our software code. This approach is an important development in our efforts to stop the spread of malware, allowing us to take civil action to protect customers in the large number of countries around the world that have these laws in place.
Brian Krebs comments:
In legal filings, Microsoft argued that Trickbot irreparably harms the company “by damaging its reputation, brands, and customer goodwill. Defendants physically alter and corrupt Microsoft products such as the Microsoft Windows products. Once infected, altered and controlled by Trickbot, the Windows operating system ceases to operate normally and becomes tools for Defendants to conduct their theft.”
This is a novel use of trademark law.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Breach at Dickey’s BBQ Smokes 3M Cards
One of the digital underground’s most popular stores for peddling stolen credit card information began selling a batch of more than three million new card records this week. KrebsOnSecurity has learned the data was stolen in a lengthy data breach at more than 100 Dickey’s Barbeque Restaurant locations around the country.
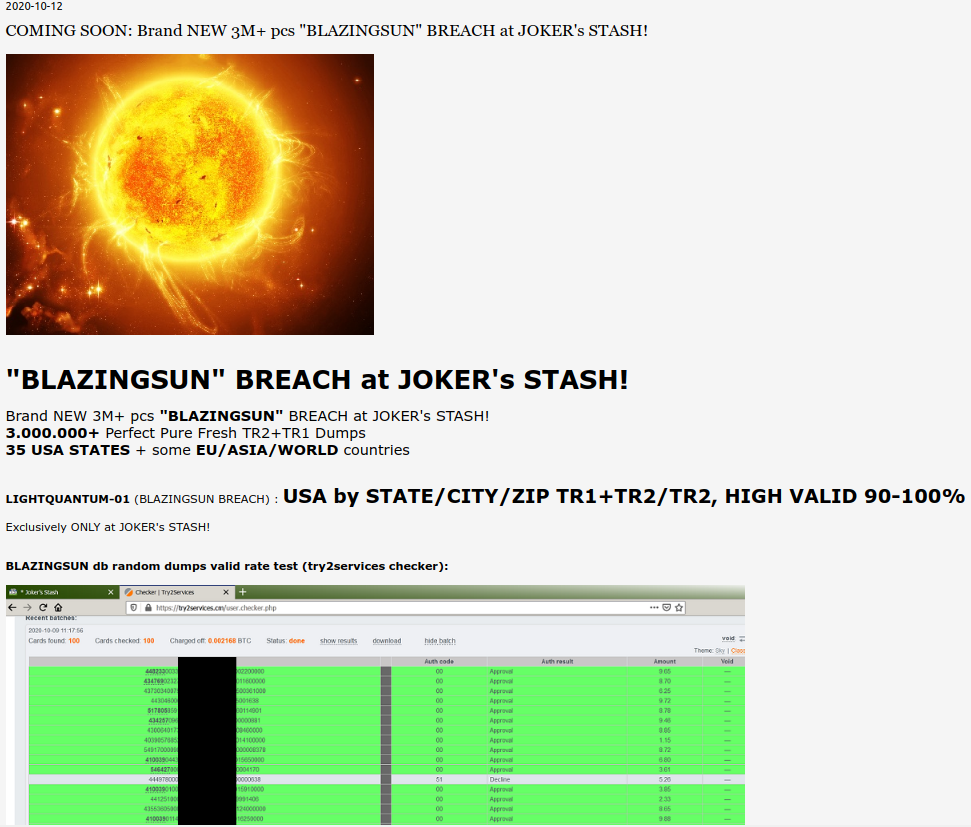
An ad on the popular carding site Joker’s Stash for “BlazingSun,” which fraud experts have traced back to a card breach at Dickey’s BBQ.
On Monday, the carding bazaar Joker’s Stash debuted “BlazingSun,” a new batch of more than three million stolen card records, advertising “valid rates” of between 90-100 percent. This is typically an indicator that the breached merchant is either unaware of the compromise or has only just begun responding to it.
Multiple companies that track the sale in stolen payment card data say they have confirmed with card-issuing financial institutions that the accounts for sale in the BlazingSun batch have one common theme: All were used at various Dickey’s BBQ locations over the past 13-15 months.
KrebsOnSecurity first contacted Dallas-based Dickey’s on Oct. 13. Today, the company shared a statement saying it was aware of a possible payment card security incident at some of its eateries:
“We received a report indicating that a payment card security incident may have occurred. We are taking this incident very seriously and immediately initiated our response protocol and an investigation is underway. We are currently focused on determining the locations affected and time frames involved. We are utilizing the experience of third parties who have helped other restaurants address similar issues and also working with the FBI and payment card networks. We understand that payment card network rules generally provide that individuals who timely report unauthorized charges to the bank that issued their card are not responsible for those charges.”
The confirmations came from Miami-based Q6 Cyber and Gemini Advisory in New York City.
Q6Cyber CEO Eli Dominitz said the breach appears to extend from May 2019 through September 2020.
“The financial institutions we’ve been working with have already seen a significant amount of fraud related to these cards,” Dominitz said.
Gemini says its data indicated some 156 Dickey’s locations across 30 states likely had payment systems compromised by card-stealing malware, with the highest exposure in California and Arizona. Gemini puts the exposure window between July 2019 and August 2020.
“Low-and-slow” aptly describes the card breach at Dickie’s, which persisted for at least 13 months.
With the threat from ransomware attacks grabbing all the headlines, it may be tempting to assume plain old credit card thieves have moved on to more lucrative endeavors. Alas, cybercrime bazaars like Joker’s Stash have continued plying their trade, undeterred by a push from the credit card associations to encourage more merchants to install credit card readers that require more secure chip-based payment cards.
That’s because there are countless restaurant locations — usually franchise locations of an established eatery chain — that are left to decide for themselves whether and how quickly they should make the upgrades necessary to dip the chip versus swipe the stripe.
“Dickey’s operates on a franchise model, which often allows each location to dictate the type of point-of-sale (POS) device and processors that they utilize,” Gemini wrote in a blog post about the incident. “However, given the widespread nature of the breach, the exposure may be linked to a breach of the single central processor, which was leveraged by over a quarter of all Dickey’s locations.”
While there have been sporadic reports about criminals compromising chip-based payment systems used by merchants in the U.S., the vast majority of the payment card data for sale in the cybercrime underground is stolen from merchants who are still swiping chip-based cards.
This isn’t conjecture; relatively recent data from the stolen card shops themselves bear this out. In July, KrebsOnSecurity wrote about an analysis by researchers at New York University, which looked at patterns surrounding more than 19 million stolen payment cards that were exposed after the hacking of BriansClub, a top competitor to the Joker’s Stash carding shop.
The NYU researchers found BriansClub earned close to $104 million in gross revenue from 2015 to early 2019, and listed over 19 million unique card numbers for sale. Around 97% of the inventory was stolen magnetic stripe data, commonly used to produce counterfeit cards for in-person payments.
Visa and MasterCard instituted new rules in October 2015 that put retailers on the hook for all of the losses associated with counterfeit card fraud tied to breaches if they haven’t implemented chip-based card readers and enforced the dipping of the chip when a customer presents a chip-based card.
Dominitz said he never imagined back in 2015 when he founded Q6Cyber that we would still be seeing so many merchants dealing with magstripe-based data breaches.
“Five years ago I did not expect we would be in this position today with card fraud,” he said. “You’d think the industry in general would have made a bigger dent in this underground economy a while ago.”
Tired of having your credit card re-issued and updating your payment records at countless e-commerce sites every time some restaurant you frequent has a breach? Here’s a radical idea: Next time you visit an eatery (okay, if that ever happens again post-COVID, etc), ask them if they use chip-based card readers. If not, consider taking your business elsewhere.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Carnival Confirms Passenger Data Compromised

Carnival Corporation has disclosed that passenger and employee data from three different cruise lines was accessed in a ransomware attack that took place in August.
On August 15, the British-American cruise operator discovered that an unauthorized third party had compromised its computer system and downloaded data files.
An update issued by the corporation yesterday states that personal data from passengers of Carnival Cruise Line, Holland America Line, and Seabourn was impacted in the August attack.
“While the investigation is ongoing, early indications are that in early August the unauthorized third party gained access to certain personal information relating to some guests, employees and crew for three of the corporation’s brands—Carnival Cruise Line, Holland America Line and Seabourn, as well as casino operations,” said Carnival.
Information accessed by the threat actor may include names, addresses, phone numbers, passport numbers, and dates of birth.
Carnival said: “The investigation into the specific data impacted is ongoing, but in some limited instances, we anticipate additional information impacted may include data such as Social Security numbers, health information, or other personal information.”
Carnival, with over 150,000 employees, is the largest cruise operator in the world, serving over 13 million passengers annually before the outbreak of COVID-19.
In the disclosure, Carnival stated that it is working “as quickly as possible” to identify and notify the passengers, employees, crew, and other individuals whose personal data may have been accessed. Working out precisely whose data was impacted could take up to 60 days to complete.
Following the attack, Carnival said it took steps to recover the files being held ransom by the threat actors. The corporation’s investigation into the incident is ongoing, but Carnival said early indicators suggest that the likelihood that the data accessed without authorization has since been misused was “low.”
“While how the third party gained unauthorized access has not been disclosed, this is yet another example of the importance of proper investment in cyber security programs to protect company and customer data,” commented Terence Jackson, CISO at Thycotic.
“Attackers are not taking it easy during the pandemic. They are stepping the attacks up and we have to be ready.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Suspended Sentence for Brit Caught in FBI Creepware Sting

A British man who hacked into webcams and CCTV so he could spy on people in their own homes and while on holiday has received a suspended prison sentence.
John Wood’s voyeuristic crimes were uncovered in 2018 as part of a joint investigation by British police and the Federal Bureau of Investigation (FBI) in the United States into the creator of LuminosityLink malware, Colton Grubbs.
The off-the-shelf malware could be secretly deployed on a computer with a Windows OS to hack into the device’s webcam and broadcast footage back to the attacker. Threat actors could also use LuminosityLink to record keystrokes and entrap an infected computer into a botnet.
In 2018, Kentucky resident Grubbs admitted designing and selling LuminosityLink software to over 6,000 customers at $39.99 apiece, despite knowing that many of his customers were using it to spy on victims without their consent.
Wood, of Minety near Swindon, pleaded guilty to two Computer Misuse Act charges and six counts of voyeurism at Swindon Crown Court. The 42-year-old was handed a two-year-suspended prison sentence. His barrister told the court Wood had been diagnosed with mental health difficulties.
According to the Swindon Advertiser, Wood purchased LuminosityLink software in 2015, but the court heard no evidence that he had used it. However, Wood did use a CCTV management product called Blue Iris to hack into webcams and spy on people.
Between 2011 and 2016, Wood made over 1,400 illicit video recordings, “the majority of which showed people having sex at home,” according to the newspaper. He also set up secret cameras inside and outside his own home in order to covertly film women.
Wood didn’t ditch his illegal activities when he went on vacation. The court heard that this committed voyeur set up hidden cameras at a holiday cottage and at the Bognor Regis Butlins holiday resort, capturing video of over 167 victims.
Judge Peter Crabtree, while passing sentence, described Wood as having engaged in a “systematic campaign of voyeurism over a period of six years.”
While LuminosityLink’s creator was sentenced to 30 months in prison in the United States and ordered to forfeit 114 Bitcoins worth $725K, Wood was ordered to register as a sex offender, complete 100 hours of community service, and attend a 30-day sex offender rehabilitation program.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
DFS Calls for Regulation of Social Media Giants

The New York State Department of Financial Services (DFS) has called for the regulation of social media giants after finding the cybersecurity protections at Twitter woefully inadequate.
Governor of New York, Andrew Cuomo, asked the DFS to investigate Twitter following the July 15, 2020, hack into the Twitter accounts of several cryptocurrency firms and well-known public figures.
A report on that investigation, released today, found that the global social media platform lacked adequate cybersecurity protections and, at the time of the attack, did not have a chief information security officer in place.
The department found that threat actors gained access to Twitter’s systems simply “by calling Twitter employees and claiming to be from Twitter’s IT department,” then asking for victims’ login credentials.
Using this unsophisticated attack strategy, the cyber-criminals hijacked the Twitter accounts of politicians, celebrities, and entrepreneurs, including Barack Obama, Kim Kardashian West, Jeff Bezos, Elon Musk, and several cryptocurrency companies regulated by the DFS.
“The Twitter Hack demonstrates the need for strong cybersecurity to curb the potential weaponization of major social media companies,” noted the DFS.
The report recommended that a new cybersecurity regulatory framework be created for giant social media companies. Currently, the cybersecurity policies and programs of such companies are not overseen by a dedicated federal or state regulator that would ensure that their cybersecurity policies and programs adequately address the risks of their digital operating models.
Superintendent of Financial Services Linda Lacewell said that companies like Facebook, Twitter, and Instagram had been allowed to regulate themselves for long enough.
“Social media platforms have quickly become the leading source of news and information, yet no regulator has adequate oversight of their cybersecurity,” she said.
“The fact that Twitter was vulnerable to an unsophisticated attack shows that self-regulation is not the answer.”
Lacewell said that poor cybersecurity at immensely influential social media platforms that increasingly dictate what content is newsworthy could potentially allow hackers to interfere with the US presidential election.
Lacewell said: “As we approach an election in fewer than 30 days, we must commit to greater regulatory oversight of large social media companies. The integrity of our elections and markets depends on it.”
The report recommends that, given their millions of users and tremendous power over news media, social media companies should be “designated as systemically important institutions with prudent regulation to manage heightened cybersecurity risk.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Ransomware Victims Struggle to Recover, Hire and Spend on Threat Prevention

IT managers at organizations hit by ransomware are nearly three-times as likely to feel “significantly behind” when it comes to understanding cyber-threats.
According to new research from Sophos, organizations “are never the same after being hit by ransomware” and a third (35%) of victims reported that recruiting and retaining skilled IT security professionals was their single biggest challenge when it comes to cybersecurity.
In an email to Infosecurity, Chester Wisniewski, principal research scientist at Sophos, said that falling victim to a cyber-attack has a major impact on attitudes to cybersecurity staffing. “It is likely that there are several factors behind these varying attitudes. Firstly, the consequences of limited security skills are still fresh in the minds of those who have recently suffered the financial, operational and reputational cost of being held to ransom,” he explained.
“In addition, ransomware victims will invariably have investigated the source of the attack. In doing so, they will have identified the gaps in their defenses that enabled the attackers to penetrate their organizations and access their data. Many will likely have identified a shortage of human expertise as a contributing factor to falling victim to attack.”
The survey of 5000 IT decision makers also found that ransomware victims spend proportionally less time on threat prevention (42.6%) and more time on response (27%) compared to those who haven’t been hit (49% and 22% respectively), diverting resources towards dealing with incidents rather than stopping them in the first place.
Asked if this shows there is a requirement for a more proactive stance on security, Wisniewski said: “The difference in resource priorities could indicate that ransomware victims have more incidents to deal with overall. However, it could equally indicate that they are more alert to the complex, multi-stage nature of advanced attacks and therefore put greater resource into detecting and responding to the tell-tale signs that an attack is imminent.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Ivanti Appoints Melissa Puls as New SVP and CMO

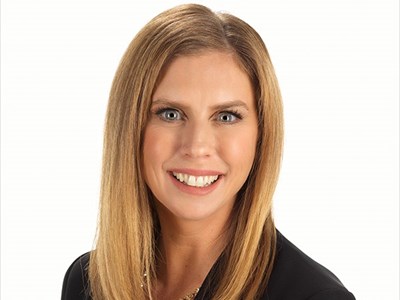
IT management and security company Ivanti has announced the appointment of Melissa Puls as its new senior vice-president (SVP) and chief marketing officer (CMO).
Puls joins Ivanti after recently serving as SVP and CMO at Avid, and brings decades of experience to the company with a strong track record of fuelling growth through a customer-centric approach and integrating marketing strategies for acquired companies.
Puls will lead Ivanti’s global marketing function to drive expansion and adoption of the company’s enterprise software solutions globally.
“Ivanti is at an exciting and pivotal time in its growth and transformation,” said Puls. “With an impressive portfolio of solutions that improve the security, manageability and serviceability of today’s remote and digital workplace, Ivanti is poised for unprecedented growth. I’m thrilled to be playing such a strategic role in helping Ivanti capitalize on this extraordinary market opportunity.”
Jeff Abbott, president of Ivanti, said that Puls is perfectly-suited to enriching and expanding Ivanti’s marketing footprint as the firm continues to grow.
“Her market insights, go-to-market expertise and deep understanding of the customer engagement journey will play a valued role on the Ivanti executive team as we continue building our market position as both a leader and innovator for the digital enterprise,” he added.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
DVLA Submits Nearly 200 Breach Notifications to ICO

The DVLA reported nearly 200 breach notifications to the data protection regulator over the past year, according to new Freedom of Information (FOI) data.
FOI requests were sent to 17 government departments by secure storage vendor Apricorn, to assess the effectiveness of data security measures in the public sector. Some 14 departments provided responses for the period April 2019 to July 2020.
The DVLA said it submitted 181 breach notifications to the Information Commissioner’s Office (ICO) across 2019-20. By contrast, the Home Office submitted just 25 during the period, while NHS Digital notified the ICO only four times.
“The large number of data incidents being reported may be in part due to the increased awareness and changes in processes when identifying and managing data breaches. The change in requirements in line with the GDPR will of course see a rise in the numbers now being reported to the ICO,” argued Apricorn EMEA managing director, Jon Fielding.
“Needless to say, if the data is secure in the first instance, the number of breaches, and the need to report them, would obviously decline. Public sector bodies should follow the same process as any business would when it comes to mitigating risk. At the very least, data should be encrypted in transit and at rest so that, in the event defenses are compromised, the data remains inaccessible.”
He added that the surge in remote working thanks to the pandemic will also potentially introduce data security concerns if information is not properly protected when flowing out to home endpoints and cloud servers.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk