Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Author: admin
Hacking Apple for Profit
Five researchers hacked Apple Computer’s networks — not their products — and found fifty-five vulnerabilities. So far, they have received $289K.
One of the worst of all the bugs they found would have allowed criminals to create a worm that would automatically steal all the photos, videos, and documents from someone’s iCloud account and then do the same to the victim’s contacts.
Lots of details in this blog post by one of the hackers.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Microsoft Uses Trademark Law to Disrupt Trickbot Botnet
Microsoft Corp. has executed a coordinated legal sneak attack in a bid to disrupt the malware-as-a-service botnet Trickbot, a global menace that has infected millions of computers and is used to spread ransomware. A court in Virginia granted Microsoft control over many Internet servers Trickbot uses to plunder infected systems, based on novel claims that the crime machine abused the software giant’s trademarks. However, it appears the operation has not completely disabled the botnet.
A spam email containing a Trickbot-infected attachment that was sent earlier this year. Image: Microsoft.
“We disrupted Trickbot through a court order we obtained as well as technical action we executed in partnership with telecommunications providers around the world,” wrote Tom Burt, corporate vice president of customer security and trust at Microsoft, in a blog post this morning about the legal maneuver. “We have now cut off key infrastructure so those operating Trickbot will no longer be able to initiate new infections or activate ransomware already dropped into computer systems.”
Microsoft’s action comes just days after the U.S. military’s Cyber Command carried out its own attack that sent all infected Trickbot systems a command telling them to disconnect themselves from the Internet servers the Trickbot overlords used to control them. The roughly 10-day operation by Cyber Command also stuffed millions of bogus records about new victims into the Trickbot database in a bid to confuse the botnet’s operators.
In legal filings, Microsoft argued that Trickbot irreparably harms the company “by damaging its reputation, brands, and customer goodwill. Defendants physically alter and corrupt Microsoft products such as the Microsoft Windows products. Once infected, altered and controlled by Trickbot, the Windows operating system ceases to operate normally and becomes tools for Defendants to conduct their theft.”
From the civil complaint Microsoft filed on October 6 with the U.S. District Court for the Eastern District of Virginia:
“However, they still bear the Microsoft and Windows trademarks. This is obviously meant to and does mislead Microsoft’s customers, and it causes extreme damage to Microsoft’s brands and trademarks.”
“Users subject to the negative effects of these malicious applications incorrectly believe that Microsoft and Windows are the source of their computing device problems. There is great risk that users may attribute this problem to Microsoft and associate these problems with Microsoft’s Windows products, thereby diluting and tarnishing the value of the Microsoft and Windows trademarks and brands.”
Microsoft said it will leverage the seized Trickbot servers to identify and assist Windows users impacted by the Trickbot malware in cleaning the malware off of their systems.
Trickbot has been used to steal passwords from millions of infected computers, and reportedly to hijack access to well more than 250 million email accounts from which new copies of the malware are sent to the victim’s contacts.
Trickbot’s malware-as-a-service feature has made it a reliable vehicle for deploying various strains of ransomware, locking up infected systems on a corporate network unless and until the company agrees to make an extortion payment.
A particularly destructive ransomware strain that is closely associated with Trickbot — known as “Ryuk” or “Conti” — has been responsible for costly attacks on countless organizations over the past year, including healthcare providers, medical research centers and hospitals.
One recent Ryuk victim is Universal Health Services (UHS), a Fortune 500 hospital and healthcare services provider that operates more than 400 facilities in the U.S. and U.K.
On Sunday, Sept. 27, UHS shut down its computer systems at healthcare facilities across the United States in a bid to stop the spread of the malware. The disruption caused some of the affected hospitals to redirect ambulances and relocate patients in need of surgery to other nearby hospitals.
Microsoft said it did not expect its action to permanently disrupt Trickbot, noting that the crooks behind the botnet will likely make efforts to revive their operations. But so far it’s not clear whether Microsoft succeeded in commandeering all of Trickbot’s control servers, or when exactly the coordinated seizure of those servers occurred.
As the company noted in its legal filings, the set of Internet address used as Trickbot controllers is dynamic, making attempts to disable the botnet more challenging.
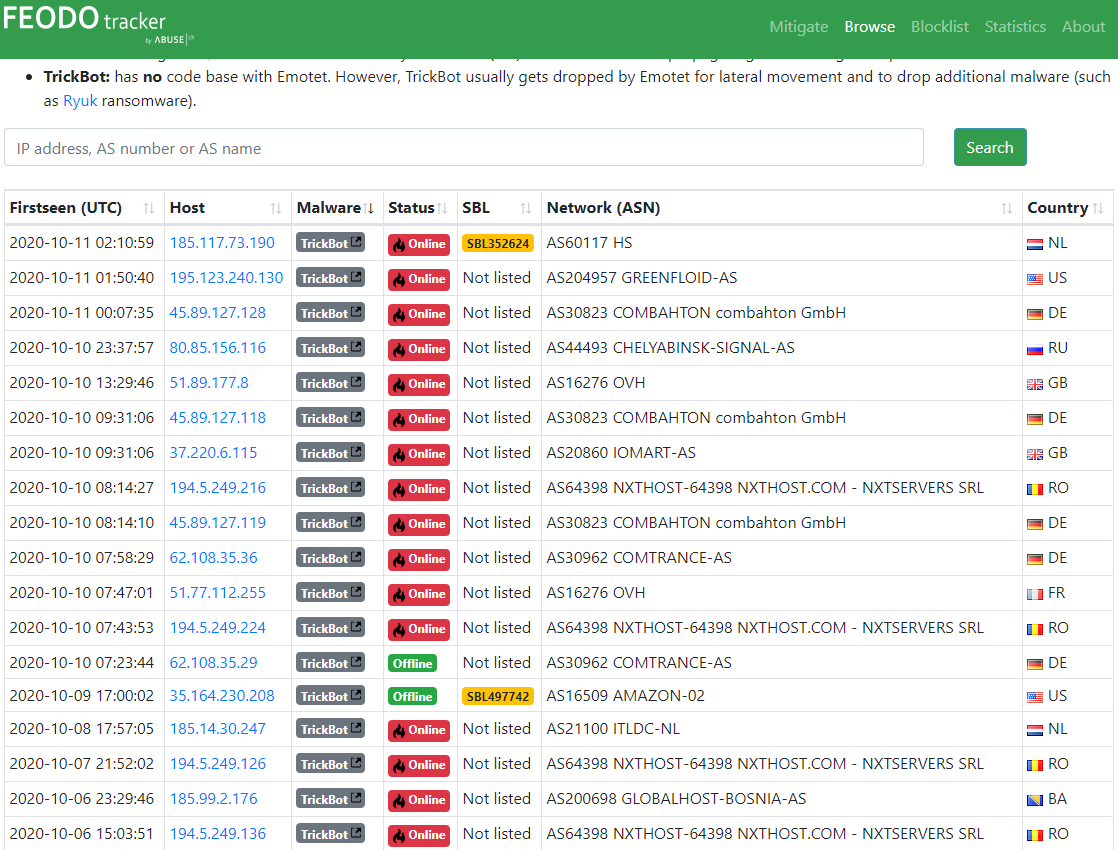
Indeed, according to real-time information posted by Feodo Tracker, a Swiss security site that tracks Internet servers used as controllers for Trickbot and other botnets, nearly two dozen Trickbot control servers — some of which first went active at beginning of this month — are still live and responding to requests at the time of this publication.
Cyber intelligence firm Intel 471 says fully taking down Trickbot would require an unprecedented level of collaboration among parties and countries that most likely would not cooperate anyway. That’s partly because Trickbot’s primary command and control mechanism supports communication over The Onion Router (TOR) — a distributed anonymity service that is wholly separate from the regular Internet.
“As a result, it is highly likely a takedown of the Trickbot infrastructure would have little medium- to long-term impact on the operation of Trickbot,” Intel 471 wrote in an analysis of Microsoft’s action.
What’s more, Trickbot has a fallback communications method that uses a decentralized domain name system called EmerDNS, which allows people to create and use domains that cannot be altered, revoked or suspended by any authority. The highly popular cybercrime store Joker’s Stash — which sells millions of stolen credit cards — also uses this setup.
From the Intel 471 report [malicious links and IP address defanged with brackets]:
“In the event all Trickbot infrastructure is taken down, the cybercriminals behind Trickbot will need to rebuild their servers and change their EmerDNS domain to point at their new servers. Compromised systems then should be able to connect to the new Trickbot infrastructure. Trickbot’s EmerDNS fall-back domain safetrust[.]bazar recently resolved to the IP address 195.123.237[.]156. Not coincidentally, this network neighborhood also hosts Bazar malware control servers.”
“Researchers previously attributed the development of the Bazar malware family to the same group behind Trickbot, due to code similarities with the Anchor malware family and its methods of operation, such as shared infrastructure between Anchor and Bazar. On Oct. 12, 2020 the fall-back domain resolved to the IP address 23.92.93[.]233, which was confirmed by Intel 471 Malware Intelligence systems to be a Trickbot controller URL in May 2019. This suggests the fall-back domain is still controlled by the Trickbot operators at the time of this report.”
Intel 471 concluded that the Microsoft action has so far has done little to disrupt the botnet’s activity.
“At the time of this report, Intel 471 has not seen any significant impact on Trickbot’s infrastructure and ability to communicate with Trickbot-infected systems,” the company wrote.
The legal filings from Microsoft are available here.
Update, 9:51 a.m. ET: Feodo Tracker now lists just six Trickbot controllers as responding. All six were first seen online in the past 48 hours. Also added perspective from Intel 471.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Report: U.S. Cyber Command Behind Trickbot Tricks
A week ago, KrebsOnSecurity broke the news that someone was attempting to disrupt the Trickbot botnet, a malware crime machine that has infected millions of computers and is often used to spread ransomware. A new report Friday says the coordinated attack was part of an operation carried out by the U.S. military’s Cyber Command.
Image: Shutterstock.
On October 2, KrebsOnSecurity reported that twice in the preceding ten days, an unknown entity that had inside access to the Trickbot botnet sent all infected systems a command telling them to disconnect themselves from the Internet servers the Trickbot overlords used to control compromised Microsoft Windows computers.
On top of that, someone had stuffed millions of bogus records about new victims into the Trickbot database — apparently to confuse or stymie the botnet’s operators.
In a story published Oct. 9, The Washington Post reported that four U.S. officials who spoke on condition of anonymity said the Trickbot disruption was the work of U.S. Cyber Command, a branch of the Department of Defense headed by the director of the National Security Agency (NSA).
The Post report suggested the action was a bid to prevent Trickbot from being used to somehow interfere with the upcoming presidential election, noting that Cyber Command was instrumental in disrupting the Internet access of Russian online troll farms during the 2018 midterm elections.
The Post said U.S. officials recognized their operation would not permanently dismantle Trickbot, describing it rather as “one way to distract them for at least a while as they seek to restore their operations.”
Alex Holden, chief information security officer and president of Milwaukee-based Hold Security, has been monitoring Trickbot activity before and after the 10-day operation. Holden said while the attack on Trickbot appears to have cut its operators off from a large number of victim computers, the bad guys still have passwords, financial data and reams of other sensitive information stolen from more than 2.7 million systems around the world.
Holden said the Trickbot operators have begun rebuilding their botnet, and continue to engage in deploying ransomware at new targets.
“They are running normally and their ransomware operations are pretty much back in full swing,” Holden said. “They are not slowing down because they still have a great deal of stolen data.”
Holden added that since news of the disruption first broke a week ago, the Russian-speaking cybercriminals behind Trickbot have been discussing how to recoup their losses, and have been toying with the idea of massively increasing the amount of money demanded from future ransomware victims.
“There is a conversation happening in the back channels,” Holden said. “Normally, they will ask for [a ransom amount] that is something like 10 percent of the victim company’s annual revenues. Now, some of the guys involved are talking about increasing that to 100 percent or 150 percent.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Cyber-attacks on Angolan Journalists Who Reported Government Corruption

Cyber-attacks have been levied against journalists in Angola after they reported that the Angolan president’s chief of staff had embezzled public funds.
Independent online news provider Correio Angolense published an article online covering the claims against Edeltrudes Costa that were first made by the Portuguese TV channel Televisão Independente (TVI).
The broadcaster launched an investigation after companies owned by Costa were awarded several major contracts by the government, including a multi-million-dollar contract to renovate Angola’s airports. TVI alleged that Costa transferred public money paid to his businesses to offshore accounts in Panama and Portugal, then used it to acquire luxury properties.
Shortly after Correio Angolense covered the allegations, the website of the news provider was hit by a denial-of-service (DDoS) attack. As a result, the website has been inaccessible since September 25.
Its editor, Graça Campos, told Reporters Without Borders (RSF) that the site was crashed by thousands of simultaneous connection attempts in what appeared to be a deliberate cyber-attack.
RSF’s former Angola correspondent, freelance journalist Siona Casimiro, was also the target of a cyber-attack after he worked on the Costa embezzlement story.
Casimiro told RSF: “There can be no doubt about the desire to silence journalists with regard to the Edeltrudes Costa affair.”
Combatting corruption has been one of President João Lourenço’s key pledges since his election in 2017. When news of Costa’s alleged crime broke, around 200 people took to the streets of the nation’s capital Luanda to protest and call for the chief of staff’s resignation.
Lourenço’s campaign against corruption led to the imprisonment in August of José Filomeno dos Santos, son of Angola’s former president José Eduardo dos Santos, who served as the country’s head of state from 1979 to 2017. José Filomeno was sentenced to five years in prison after diverting oil revenues from Angola’s sovereign wealth fund, which he oversaw from 2013 to 2018.
An investigation is ongoing into the activities of his half-sister Isabel dos Santos, who, according to Africa News, is suspected of “a long list of crimes including mismanagement, embezzlement and money laundering during her stewardship of state oil giant Sonangol.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Tennessee Health Data Management Firm Agrees to $2m Data Breach Settlement

A Tennessee firm that provides health data management services has agreed to pay the United States Office for Civil Rights (OCR) $2.3m to settle charges related to a data breach.
Charges were brought against Tennessee-based Community Health Systems (CHSPSC LLC) by 28 states after the personal health information (PHI) of millions of people ended up in the hands of cyber-criminals.
In April 2014, CHSPSC was notified by the Federal Bureau of Investigation that Chinese advanced persistent threat group APT18 had gained access to the company’s information system and was exfiltrating PHI. The hackers continued to access and exfiltrate the PHI until August 2014, despite the notice’s being sent.
CHSPSC provides a variety of business associate services, including IT and health information management, to hospitals and clinics indirectly owned by Community Health Systems, Inc., in Franklin, Tennessee. Community Health Systems owned, leased, or operated 206 affiliated hospitals at the time of the data breach.
A total of 6,121,158 individuals were impacted by the cyber-attack on CHSPSC. Data accessed by the threat group included names, birthdates, Social Security numbers, phone numbers, and addresses of patients.
The threat group accessed CHSPSC’s information system remotely, using compromised administrative credentials to get into the company’s virtual private network.
An investigation into the incident by OCR found long-standing, systemic noncompliance with the HIPAA Security Rule that included failures to implement information system activity review, security incident procedures, and access controls and a failure to conduct a risk analysis.
“The health care industry is a known target for hackers and cyberthieves. The failure to implement the security protections required by the HIPAA Rules, especially after being notified by the FBI of a potential breach, is inexcusable,” said OCR director Roger Severino.
Yesterday, Tennessee attorney general Herbert Slatery III, along with the attorneys general of 27 other states, announced a settlement with Community Health Systems and its subsidiary, CHSPSC LLC. As part of the judgement, CHS has agreed to pay $5m to the states.
In addition to the monetary settlement, CHSPSC has agreed to protect patient data by implementing and maintaining a robust security program.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
US to Grow Space Force Cybersecurity Team

The Pentagon is to significantly increase the size of the United States Space Force’s cybersecurity team.
Plans to add over a thousand new personnel were revealed by the force’s chief technology and innovation officer, US Space Force Major General Kimberly Crider.
Speaking at the CyberSatGov virtual event held yesterday, Crider said that 130 cybersecurity officers would be transferred into the Space Force along with 1,000 enlisted personnel, who would be assigned cybersecurity work in the fiscal year 2021.
The staff who are to be transferred have been supporting the Space Force from their positions within the US Air Force. Once the transfer has been complete, the staff’s main focus will be on the Space Force’s defensive operations.
Crider said that part of the Space Force’s cyber future response would include technologies like GPS anti-jamming solutions and Protected Anti-Jam Tactical Satcom (PATS). The force is also introducing military procurement events and programs that will allow its personnel to acquire state-of-the-art capabilities from non-traditional vendors.
One such event is Space Force Pitch Day, which is currently scheduled to take place in Los Angeles in the spring of 2021, hosted by the Space Force’s Space and Missile Systems Center (SMC).
Crider praised the commercial defense industry for its work building security into military systems and networks and said that the Space Force may collaborate with the industry in the future.
“The advancement of DevSecOps as a critical methodology for how we develop software, and how we integrate software testing as a continuous process throughout development of code as it’s deployed into production, is another key and important feature to how we can protect the capabilities that could be subject to cyberspace attacks,” Crider said. “Our industry partners, as key members of our software development teams and providers of critical software capabilities, embrace DevSecOps methods, and we very much rely upon that as another realm of protecting ourselves from malicious attacks.”
Crider said that diversity will be vital to the force’s future cyber-defense.
“Space systems will become the next front of the cyber conflict,” she said. “Diversity is key to our resiliency. If one space system is jammed, we need to have other systems that we can fall back on.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Parents Using School Payment Service Have Card Details Compromised

UK school payment service Wisepay has revealed that the card details of parents who made transactions on its site between October 2 and 5 have been compromised.
This was after Wisepay’s website was hacked, resulting in an attacker harvesting payment details via a spoof page. The attack begun on the evening of Friday October 2 and was not noticed until the following Monday morning at 10.00am.
The company, which is “a secure online school payments service, allowing parents and guardians to make cashless payments to their school or college” ranging from exam fees to school meals, temporarily took its site offline in response.
Quoted by the BBC, Wisepay’s managing director Richard Grazier said the site has since come back online and is safe to use. While attempted payments to around 300 schools are believed to have been affected by the attack, Grazier added that “it’s quite a small subset of users of the platform” because the kinds of cashless payments made are not conducted on a daily basis.
Those affected will be identified and contacted by Wisepay.
Commenting on the story, Miles Tappin, VP of EMEA at ThreatConnect said: “The threat landscape for any organization is massive and finding gaps in security is simply a cat and mouse game for hackers. When it comes to financial organizations, they are seen as a lucrative target as they hold highly sensitive information and have a mandate to protect the personal information of their customers. With WisePay being a financial organization aimed at the education sector, this proved to be a gold mine for hackers.
“No company is immune from the dangers of being compromised. It’s essential that any potential target understands as much as they can about the threats they face and the tools needed to ensure they remain secure. Organizations must prioritise knowing where adversaries are, the tools and techniques they use, and what information adversaries think are most valuable.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Global Privacy Control Launched to Offer Users Greater Internet Trust

A number of technology companies have come together to create the Global Privacy Control (GPC), a new standard to help ensure consumers can feel safe about how their personal data is used on participating websites.
The GPC is a standard for web browsers and websites to simplify making and handling online privacy requests, in particular requests like “Do Not Sell” (do not sell my data to third parties without my consent). This claims that users have lacked tools and standards to invoke privacy rights offered as part of GDPR and CCPA, so rather than having to click on individual links across many websites, users can communicate their privacy preferences in one step via the GPC.
Rob Shavell, CEO of Abine, said the launch of GPC and associated technology aims to change the issue of consumer rights outlined being complicated to enforce. “The industry has relied upon this ‘nothing will happen in practice’ understanding to avoid both real investment and real change. The launch of GPC and associated technology aims to change this status quo.”
The GPR will enable browsers and extensions to send a signal to participating websites to communicate a ‘Do Not Sell’ request to limit the sale or sharing of the user’s personal data.
In this phase of the rollout, individuals can enable GPC by installing a supported browser or extension such as Blur by Abine or by going to the official Global Privacy Control website to download one of the other participating browsers and extensions from the EFF, DuckDuckGo, Brave, Mozilla, and Disconnect.
In an email to Infosecurity, Tom Pendergast, chief learning officer at MediaPro, said: “Anything that makes complicated privacy controls easy and transparent increases the feeling that people can control their internet experience—and that’s a good thing.
“I hope this is the first in a new wave of consumer privacy enabling technology. This looks like a great leap forward in the amount of control offered to individuals. Measures, such as the CCPA and the GDPR, lay the groundwork that gives individuals power, but it’s been too difficult to exercise. This makes it easy.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Marketing Firm Spills Nearly Three Million Records

A US digital marketing provider has exposed almost three million records containing personally identifiable information (PII) after another cloud configuration mistake.
The privacy snafu at Friendemic, whose main clients are reportedly US car dealerships, was discovered by Aaron Phillips at Comparitech. As is usual in these cases, the unencrypted data was left exposed to the public internet with no password or authentication required to access it.
In this particular instance it was an unsecured Amazon S3 bucket which Phillips claimed to be an SQL dump or database backup, potentially created for migrating data between servers.
All told there were over 2.7 million records including full names, phone numbers and email addresses, alongside 16 OAuth tokens stored in plaintext.
However, exactly who these records belong to remains a mystery: Friendemic told Comparitech that they were not related to customers of its car dealership clients. It also claimed that the OAuth tokens were for internal systems only and were no longer in use when the data was exposed.
To its credit, the firm appeared to act quickly on being informed of the incident, remediating the risk within a day.
“While no company ever wants something like this to happen, we are glad to have the vulnerability fixed,” it noted in a statement. “Thank you for notifying us and acting professionally. We have also notified our clients of the situation and have been doing a thorough review and enhancement of our data security.”
However, incidents like these are increasingly commonplace and could put customers at risk of follow-on phishing and identity fraud attacks.
There’s also the risk that attackers could steal the database completely and ransom the contents, or even destroy what they found, as per the recent spate of “Meow” attacks.
Research earlier this year found that misconfiguration accounts for 82% of all security vulnerabilities today.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk