Friday Squid Blogging: COVID-19 Found on Chinese Squid Packaging

I thought the virus doesn’t survive well on food packaging:

Authorities in China’s northeastern Jilin province have found the novel coronavirus on the packaging of imported squid, health authorities in the city of Fuyu said on Sunday, urging anyone who may have bought it to get themselves tested.

As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.

Read my blog posting guidelines here.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Who is Tech Investor John Bernard?

John Bernard, the subject of a story here last week about a self-proclaimed millionaire investor who has bilked countless tech startups, appears to be a pseudonym for John Clifton Davies, a U.K. man who absconded from justice before being convicted on multiple counts of fraud in 2015. Prior to his conviction, Davies served 16 months in jail before being cleared of murdering his wife on their honeymoon in India.

The Private Office of John Bernard, which advertises itself as a capital investment firm based in Switzerland, has for years been listed on multiple investment sites as the home of a millionaire who made his fortunes in the dot-com boom 20 years ago and who has oodles of cash to invest in tech startups.
But as last week’s story noted, Bernard’s investment company is a bit like a bad slot machine that never pays out. KrebsOnSecurity interviewed multiple investment brokers who all told the same story: After promising to invest millions after one or two phone calls and with little or no pushback, Bernard would insist that companies pay tens of thousands of dollars worth of due diligence fees up front.

However, the due diligence company he insisted on using — another Swiss firm called Inside Knowledge — also was secretly owned by Bernard, who would invariably pull out of the deal after receiving the due diligence money.

Neither Mr. Bernard nor anyone from his various companies responded to multiple requests for comment over the past few weeks. What’s more, virtually all of the employee profiles tied to Bernard’s office have since last week removed those firms from their work experience as listed on their LinkedIn resumes — or else deleted their profiles altogether.

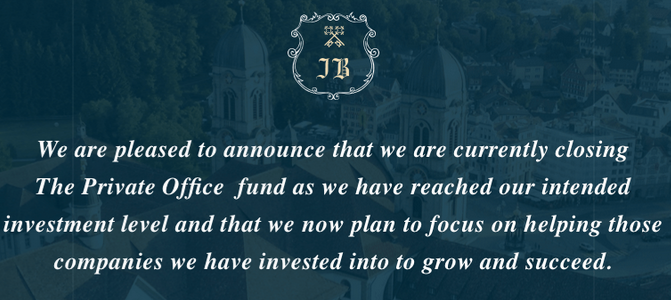
Sometime on Thursday John Bernard’s main website — the-private-office.ch — replaced the content on its homepage with a note saying it was closing up shop.

“We are pleased to announce that we are currently closing The Private Office fund as we have reached our intended investment level and that we now plan to focus on helping those companies we have invested into to grow and succeed,” the message reads.
As noted in last week’s story, the beauty of a scam like the one multiple investment brokers said was being run by Mr. Bernard is that companies bilked by small-time investment schemes rarely pursue legal action, mainly because the legal fees involved can quickly surpass the losses. What’s more, most victims will likely be too ashamed to come forward.

Also, John Bernard’s office typically did not reach out to investment brokers directly. Rather, he had his firm included on a list of angel investors focused on technology companies, so those seeking investments usually came to him.

Finally, multiple sources interviewed for this story said Bernard’s office offered a finders fee for any investment leads that brokers brought his way. While such commissions are not unusual, the amount promised — five percent of the total investment in a given firm that signed an agreement — is extremely generous. However, none of the investment brokers who spoke to KrebsOnSecurity were able to collect those fees, because Bernard’s office never actually consummated any of the deals they referred to him.

PAY NO ATTENTION TO THE EMPTY BOOKSHELVES

After last week’s story ran, KrebsOnSecurity heard from a number of other investment brokers who had near identical experiences with Bernard. Several said they at one point spoke with him via phone or Zoom conference calls, and that he had a distinctive British accent.

When questioned about why his staff was virtually all based in Ukraine when his companies were supposedly in Switzerland, Bernard replied that his wife was Ukrainian and that they were living there to be closer to her family.

One investment broker who recently got into a deal with Bernard shared a screen shot from a recent Zoom call with him. That screen shot shows Bernard bears a striking resemblance to one John Clifton Davies, a 59-year-old from Milton Keynes, a large town in Buckinghamshire, England about 50 miles (80 km) northwest of London.
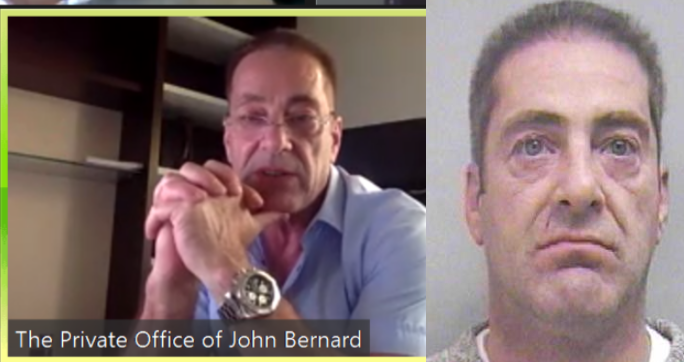
John Bernard (left) in a recent Zoom call, and a photo of John Clifton Davies from 2015.

In 2015, Mr. Davies was convicted of stealing more than GBP 750,000 from struggling companies looking to restructure their debt. For at least seven years, Davies ran multiple scam businesses that claimed to provide insolvency consulting to distressed companies, even though he was not licensed to do so.

“After gaining the firm’s trust, he took control of their assets and would later pocket the cash intended for creditors,” according to a U.K. news report from 2015. “After snatching the cash, Davies proceeded to spend the stolen money on a life of luxury, purchasing a new upmarket home fitted with a high-tech cinema system and new kitchen.”

Davies disappeared before he was convicted of fraud in 2015. Two years before that, Davies was released from prison after being held in custody for 16 months on suspicion of murdering his new bride in 2004 on their honeymoon in India.

Davies’ former wife Colette Davies, 39, died after falling 80 feet from a viewing point at a steep gorge in the Himachal Pradesh region of India. Mr. Davies was charged with murder and fraud after he attempted to collect GBP 132,000 in her life insurance payout, but British prosecutors ultimately conceded they did not have enough evidence to convict him.

THE SWISS AND UKRAINE CONNECTIONS

While the photos above are similar, there are other clues that suggest the two identities may be the same person. A review of business records tied to Davies’ phony insolvency consulting businesses between 2007 and 2013 provides some additional pointers.

John Clifton Davies’ former listing at the official U.K. business registrar Companies House show his company was registered at the address 26 Dean Forest Way, Broughton, Milton Keynes.

A search on that street address at 4iq.com turns up several interesting results, including a listing for senecaequities.com registered to a John Davies at the email address john888@myswissmail.ch.

A Companies House official record for Seneca Equities puts it at John Davies’ old U.K. address at 26 Dean Forest Way and lists 46-year-old Iryna Davies as a director. “Iryna” is a uniquely Ukrainian spelling of the name Irene (the Russian equivalent is typically “Irina”).

A search on John Clifton Davies and Iryna turned up this 2013 story from The Daily Mirror which says Iryna is John C. Davies’ fourth wife, and that the two were married in 2010.

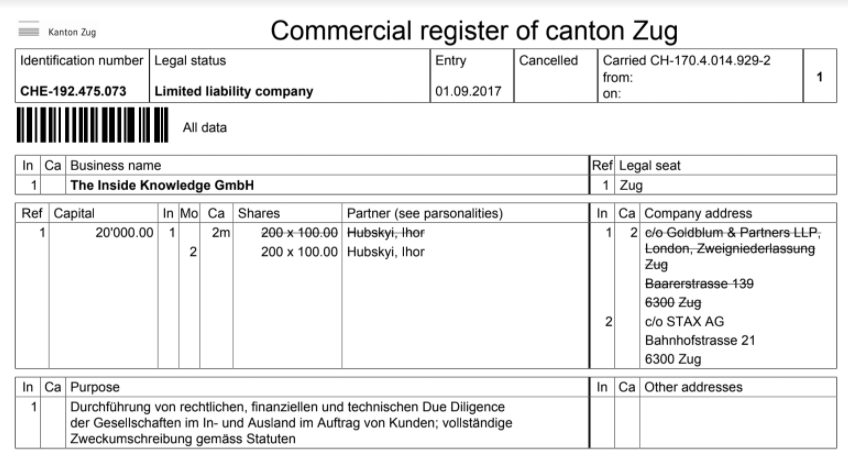
A review of the Swiss company registrar for The Inside Knowledge GmbH shows an Ihor Hubskyi was named as president of the company. This name is phonetically the same as Igor Gubskyi, a Ukrainian man who was listed in the U.K.’s Companies House records as one of five officers for Seneca Equities along with Iryna Davies.
KrebsOnSecurity sought comment from both the U.K. police district that prosecuted Davies’ case and the U.K.’s National Crime Agency (NCA). Neither wished to comment on the findings. “We can neither confirm nor deny the existence of an investigation or subjects of interest,” a spokesperson for the NCA said.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Attacks Against Oil and Gas Industry on the Rise

Attacks Against Oil and Gas Industry on the Rise

New research published today by Kaspersky examines a rise in the number of cyber-attacks on industrial control system (ICS) computers used by the oil and gas industry.

Over the first six months of 2020, the percentage of systems attacked in the oil and gas industry increased when compared to the same time period last year. The same trend was discovered at play in the building automation industry.

Researchers noted: “The percentage of ICS computers on which malicious objects were blocked grew from 38% in H2, 2019 to 39.9% in H1, 2020 in the building automation industry and from 36.3% to 37.8% in the oil and gas industry.”

Growth in the number of attacks on these sectors occurred as the percentage of industrial control system computers attacked in other industries declined. 

The research appears to indicate that cyber-criminals are moving their focus away from the energy, automotive manufacturing and engineering, and ICS integration industries. 

Kaspersky noted that building automation systems are especially vulnerable to cyber-attacks. 

“They often have a larger attack surface than traditional ICS computers because they are frequently connected to corporate networks and the Internet,” wrote researchers. “At the same time, because they traditionally belong to contractor organizations, these systems are not always managed by the organization’s corporate information security team, making them an easier target.”

Changes in working practices brought about by COVID-19 have left systems more exposed to attack. 

“With many enterprises forced to work remotely and sign-in to corporate systems from home, ICS have naturally become more exposed to cyberthreats,” said Evgeny Goncharov, security expert at Kaspersky.

“With fewer on-site personnel, there are fewer people available to respond and mitigate an attack, meaning the consequences may be far more devastating.”

Further findings were that the percentage of ICS computers affected by ransomware grew slightly in H1 2020 when compared to H2 2019 across all industries, with a series of attacks witnessed against medical facilities and industrial companies.

Kaspersky recommended that companies in the oil and gas and building automation industries that use ICS computers regularly update operating systems and application software that are part of the enterprise’s industrial network.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

US Customs and Border Protection Failed to Safeguard Data

US Customs and Border Protection Failed to Safeguard Data

A review of a facial recognition technology pilot scheme conducted by US Customs and Border Protection (CBP) has found that sensitive biometric data was not adequately protected. 

The Vehicle Face System was trialed last year by CBP. A major cybersecurity incident occurred when subcontractor Perceptics, hired to work on the pilot, transferred copies of CBP’s biometric data to its own company network.

The subcontractor obtained access to this data between August 2018 and January 2019 without CBP’s authorization or knowledge. Later in 2019, the Department of Homeland Security experienced a major privacy incident, as the subcontractor’s network was subjected to a malicious cyber-attack.

Subsequently, CBP data, including traveler images from CBP’s facial recognition pilot, appeared on the dark web, triggering a review by the Office of the Inspector General (OIG).

The data breach compromised approximately 184,000 traveler images from CBP’s facial recognition pilot. At least 19 of the images were later posted to the dark web.

In the review, published on September 21, the OIG found “CBP did not adequately safeguard sensitive data on an unencrypted device used during its facial recognition technology pilot.”

The OIG also found that Perceptics staff “directly violated DHS security and privacy protocols when they downloaded CBP’s sensitive PII from an unencrypted device and stored it on their own network.” 

Perceptics’ actions went against a Department of Homeland Security stipulation that requires subcontractors to protect personally identifiable information (PII) from identity theft or misuse.

The OIG made a series of recommendations to the CBP that included implementing USB device restrictions, applying enhanced encryption methods, and routinely assessing third-party equipment supporting biometric data collection to ensure partners’ compliance with Department security and privacy standards.

Congress used the FY 2016 Consolidated Appropriations Act to provide CBP with up to $1bn in funding over a 10-year period to develop a biometric entry-exit solution that will monitor travelers to and from the United States. 

To date, CBP’s Biometric Entry-Exit Program Office has focused primarily on air departures, starting with a pilot program at nine airports across the country in 2017.

As of April 2019, CBP had processed 19,829 flights and 2.8 million travelers across 19 airports through its biometric program.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

America Moves to Protect Free Speech Online

America Moves to Protect Free Speech Online

The United States Justice Department is calling for legal reform that would make online platforms accountable when they unlawfully censor speech or knowingly facilitate online criminal activity. 

The DOJ, on behalf of the Trump administration, sent draft legislation to Congress yesterday to reform Section 230 of the Communications Decency Act. The draft legislative text implements reforms deemed necessary by the Department in its June Recommendations and follows a year-long review of the statute. 

Current interpretations of the deliberately vaguely worded Section 230 enable online platforms to censor whatever lawful speech they don’t agree with, with impunity, feeding the growth of a ‘cancel culture’ in which only one opinion is permitted and the opportunity for free and open debate is quashed. 

To promote transparency and open discourse, the draft legislation proposes removing the shield of immunity from the hands of online platforms that willfully distribute illegal material or that moderate content in a way that isn’t deemed fair to the public. 

“The department’s legislative proposal revises and clarifies the existing language of Section 230 and replaces vague terms that may be used to shield arbitrary content moderation decisions with more concrete language that gives greater guidance to platforms, users, and courts,” stated the DOJ yesterday.

The legislative proposal also adds language to the definition of “information content provider” in an attempt to clarify when platforms should be responsible for speech that they “affirmatively and substantively contribute to or modify.”

Further amendments proposed by the DOJ are aimed at incentivizing platforms to address the growing amount of illicit content online, while preserving the core of Section 230’s immunity for defamation claims.

Deputy Attorney General Jeffrey Rosen said: “The Department’s proposal is an important step in reforming Section 230 to further its original goal: providing liability protection to encourage good behavior online.”

Legislative carve-outs were suggested that would block online immunity in cases of child abuse, terrorism, cyber-stalking, and for “truly bad actors,” allowing victims to seek redress via civil claims. 

“For too long Section 230 has provided a shield for online platforms to operate with impunity,” said US Attorney General William Barr. “Ensuring that the internet is a safe, but also vibrant, open and competitive environment is vitally important to America.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Evasive Malware Threats on the Rise Despite Decline in Overall Attacks

Evasive Malware Threats on the Rise Despite Decline in Overall Attacks

Over two-thirds (70%) of all malware attacks involved evasive zero-day malware in Q2 of 2020, which is a 12% rise on the previous quarter, according to WatchGuard Technologies latest Internet Security Report.

Interestingly, the increase in this form of malware, which circumvents anti-virus signatures, has come as overall malware detections fell by 8% compared to Q1. WatchGuard attributes this reduction to the rise in remote working brought about by COVID-19, as less employees are operating behind corporate network perimeters.

Around 34% of attacks were sent over encrypted HTTPS connections, meaning that organizations unable to inspect encrypted traffic will miss over one-third of incoming threats.

The report also showed an increase in JavaScript-based attacks. For instance, the scam script Trojan.Gnaeus, which enables threat actors to hijack control of the victim’s browser with a sophisticated code and forcibly redirects them to domains under the attackers control, comprised nearly one in five of all malware detections.

Threat actors increasingly used encrypted Excel files to hide malware in Q2, according to the report. This included the malware variant Abracadabra, which is delivered as an encrypted Excel file with the password VelvetSweatShop, the default password for Excel documents that allows it to bypass many basic anti-virus solutions.

Additionally, a six-year-old denial of service (DoS) vulnerability affecting WordPress and Drupal made a comeback in this period, and was included in the top 10 of WatchGuard’s list of network attacks by volume.

Commenting on the findings, Corey Nachreiner, CTO of WatchGuard, said: “Businesses aren’t the only ones that have adjusted operations due to the global COVID-19 pandemic – cyber-criminals have too.

“The rise in sophisticated attacks, despite the fact that overall malware detections declined in Q2, likely due to the shift to remote work, shows that attackers are turning to more evasive tactics that traditional signature-based anti-malware defenses simply can’t catch. Every organization should be prioritizing behavior-based threat detection, cloud-based sandboxing, and a layered set of security services to protect both the core network, as well as remote workforces.”   

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Bug Fixes Take Twice as Long for Manufacturing Firms

Bug Fixes Take Twice as Long for Manufacturing Firms

Manufacturing firms take twice as long to fix vulnerabilities as their peers in other verticals, although healthcare organizations have over three-times as many flaws per asset, according to new research from Kenna Security.

The security vendor teamed up with the Cyentia Institute to lift the lid on vulnerability management in 14 key sectors, with a particular focus on four: tech, manufacturing, healthcare and finance.

Although remediation capacity remained fairly consistent across the verticals, with a typical organization fixing one in every 10 vulnerabilities on their system, the research revealed specific challenges in each.

The median number of flaws per asset affecting manufacturing firms is 10, slightly higher than in other industries (7). However, they are lagging behind the average when it comes to “remediation velocity.”

The half-life of vulnerabilities for manufacturing firms is typically 69 days, versus 36 days elsewhere, while fixing 75% of bugs takes 280 days versus 201, Kenna Security revealed.

“Manufacturing companies are able to patch eight out of every 10 high risk vulnerabilities, placing them in the top sectors,” explained Kenna Security CTO, Ed Bellis. “Individual companies lag however. About four in 10 firms end each month with more high-risk vulnerabilities than they started with. The other six either break even or gain ground.”

In healthcare, there’s an average of 34 bugs per asset, nearly five-times the industry average. Although these organizations seem to be doing a good job of keeping on top of flaws, there’s still room for improvement.

“Healthcare organizations are highly efficient at finding and patching high risk vulnerabilities. On average, they tend to close about 75% of them,” explained Bellis. “That’s an admirable result, but in terms of comparisons to other sectors, it seems that healthcare lags. Of the 14 sectors we tracked in all, more than half do better.”

The finance vertical had the second highest number of flaws per asset, at 18, which could be explained by the relatively large digital footprint of many of its firms. Although they remediate half of these vulnerabilities slightly slower than most firms (44 days versus 34) they’re good at tackling high-risk bugs.

“They close 85% of the most dangerous vulnerabilities,” said Bellis. “About seven in 10 finance firms either hold ground or close more vulnerabilities than hit their books every month.”

The tech industry stood out as having the fewest number of vulnerabilities per asset, just two, and in terms of coverage, with tech firms closing around 90% of them.

“A typical company – across all sectors – closes about 25% of its vulnerabilities in 19 days, and 75% of its vulnerabilities in 202 days. Tech companies, however, close half of all vulnerabilities in 17 days and they close 75% of vulnerabilities in 67 days,” said Bellis.

Agriculture was the worst performing sector in terms of coverage, fixing just 28% of vulnerabilities.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Millions Exposed in #COVID19 Surveillance Platform Snafu

Millions Exposed in #COVID19 Surveillance Platform Snafu

Over eight million patients in India had their personal and medical details exposed after security researchers discovered multiple vulnerabilities in a government-run COVID-19 surveillance system.

The “Surveillance Platform Uttar Pradesh Covid-19” software was first discovered by vpnMentor researchers via a web scan on August 1 2020. After contacting CERT-In and the cybercrime department of the Uttar Pradesh government, the issues were finally remediated on September 10.

The research team found two main problems: an unsecured git repository containing code for the platform as well as plain text admin credentials and a separate index of CSV files containing daily COVID-19 patient reports, which was accessible without a password.

Personal data exposed included full names, addresses, phone numbers, diagnoses, symptoms and medical records.

Even worse, the passwords in the git repository were listed twice, once in easy-to-crack, unsalted MD5 hashes. Most were simply four-digit numbers, often linked to the same code as that of the platform’s administrators, the report noted.

“It appears that no security audits were undertaken on the git repository to review who had access to the data, and to implement robust security protocols, despite numerous parties spread throughout Uttar Pradesh using the surveillance platform to upload data,” said vpnMentor.

“As a result, anyone with knowledge of the platform’s URL and access to the git repository could gain complete access to its admin dashboard. Not only did this expose any data stored therein to possible theft, but, based on additional information stored on the git repository, we believe that once a hacker had access to the admin dashboard of the surveillance platform, they would have complete control.”

The security snafu therefore could have had several unintended consequences: offering hostile nations an opportunity to disrupt state efforts to tackle the pandemic, as well as providing a trove of sensitive data for cyber-criminals to craft follow-on phishing and identity fraud attacks.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk