Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Author: admin
OldGremlin Ransomware Group Bedevils Russian Orgs
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
CISA: LokiBot Stealer Storms Into a Resurgence
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Documented Death from a Ransomware Attack
A Dusseldorf woman died when a ransomware attack against a hospital forced her to be taken to a different hospital in another city.
I think this is the first documented case of a cyberattack causing a fatality. UK hospitals had to redirect patients during the 2017 WannaCry ransomware attack, but there were no documented fatalities from that event.
The police are treating this as a homicide.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Govt. Services Firm Tyler Technologies Hit in Apparent Ransomware Attack
Tyler Technologies, a Texas-based company that bills itself as the largest provider of software and technology services to the United States public sector, is battling a network intrusion that has disrupted its operations. The company declined to discuss the exact cause of the disruption, but their response so far is straight out of the playbook for responding to ransomware incidents.

Plano, Texas-based Tyler Technologies [NYSE:TYL] has some 5,300 employees and brought in revenues of more than $1 billion in 2019. It sells a broad range of services to state and local governments, including appraisal and tax software, integrated software for courts and justice agencies, enterprise financial software systems, public safety software, records/document management software solutions and transportation software solutions for schools.
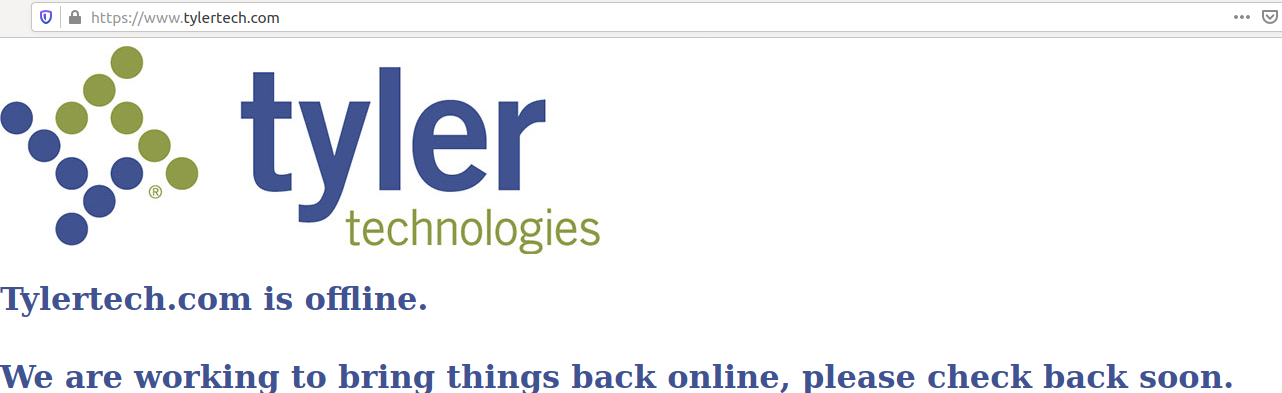
Earlier today, the normal content on tylertech.com was replaced with a notice saying the site was offline. In a statement provided to KrebsOnSecurity after the markets closed central time, Tyler Tech said early this morning the company became aware that an unauthorized intruder had gained access to its phone and information technology systems.
“Upon discovery and out of an abundance of caution, we shut down points of access to external systems and immediately began investigating and remediating the problem,” Tyler’s Chief Information Officer Matt Bieri said. “We have since engaged outside IT security and forensics experts to conduct a detailed review and help us securely restore affected equipment. We are implementing enhanced monitoring systems, and we have notified law enforcement.”
“At this time and based on the evidence available to us to-date, all indications are that the impact of this incident is limited to our internal network and phone systems,” their statement continues. “We currently have no reason to believe that any client data, client servers, or hosted systems were affected.”
While it may be comforting to hear that last bit, the reality is that it is still early in the company’s investigation. Also, ransomware has moved well past just holding a victim firm’s IT systems hostage in exchange for an extortion payment: These days, ransomware purveyors will offload as much personal and financial data that they can before unleashing their malware, and then often demand a second ransom payment in exchange for a promise to delete the stolen information or to refrain from publishing it online.
Tyler Technologies declined to say how the intrusion is affecting its customers. But several readers who work in IT roles at local government systems that rely on Tyler Tech said the outage had disrupted the ability of people to pay their water bills or court payments.
“Tyler has access to a lot of these servers in cities and counties for remote support, so it was very thoughtful of them to keep everyone in the dark and possibly exposed if the attackers made off with remote support credentials while waiting for the stock market to close,” said one reader who asked to remain anonymous.
Depending on how long it takes for Tyler to recover from this incident, it could have a broad impact on the ability of many states and localities to process payments for services or provide various government resources online.
Tyler Tech has pivoted on the threat of ransomware as a selling point for many of its services, using its presence on social media to promote ransomware survival guides and incident response checklists. With any luck, the company was following some of its own advice and will weather this storm quickly.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
179 Arrested for Darknet Drug Trafficking

A global sting operation targeting drug trafficking on the darknet has led to 179 arrests and the seizure of weapons, drugs, and millions of dollars in cash and virtual currencies.
Operation DisrupTor was conducted across the United States and Europe and was a collaborative effort between the law enforcement and judicial authorities of Austria, Cyprus, Germany, the Netherlands, Sweden, Australia, Canada, the United Kingdom, and the United States.
According to a statement released today by Europol, the 179 individuals arrested as part of the operation were vendors who had allegedly engaged in tens of thousands of sales of illicit goods.
The arrests were carried out in the United States (121), Germany (42), the Netherlands (8), United Kingdom (4), Austria (3), and Sweden (1).
Hinting at more arrests to come, Europol said: “A number of investigations are still ongoing to identify the individuals behind dark web accounts.”
Law enforcement seized $6.5m, 64 firearms, and 500 kilograms of drugs, including fentanyl, oxycodone, hydrocodone, methamphetamine, heroin, cocaine, ecstasy, MDMA, and medicine containing addictive substances.
“The golden age of [the] dark web marketplace is over,” said Europol. “Operations such as these highlight the capability of law enforcement to counter encryption and the anonymity of dark web marketplaces.”
The head of Europol’s European Cybercrime Centre (EC3), Edvardas Šileris, said: “Today’s announcement sends a strong message to criminals selling or buying illicit goods on the dark web: the hidden internet is no longer hidden, and your anonymous activity is not anonymous.”
Operation DisrupTor builds on the success of last year’s Operation SaboTor and the coordinated law enforcement takedown of the Wall Street Market, one of the largest illegal online markets on the dark web.
“Following the Wall Street Market takedown in May 2019, US and international law enforcement agencies obtained intelligence to identify Darknet drug traffickers,” stated the United States Department of Justice. “Darknet vendor accounts were identified and attributed to real individuals selling illicit goods on Darknet market sites such as AlphaBay, Dream, WallStreet, Nightmare, Empire, White House, DeepSea, Dark Market and others.”
As a result of operation DisrupTor, federal prosecutions are being conducted in more than 20 federal districts.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Data Breach at Long Island Hospital

Long Island’s only tertiary care center and Regional Trauma Center has issued a warning to patients that their personal data may have been exposed as a result of a ransomware attack.
Stony Brook University Hospital has contacted patients by letter to notify them of a possible data breach following an attack on the hospital’s third-party vendor Blackbaud in May 2020.
Blackbaud is a communications and fundraising software provider for nonprofits, universities, healthcare organizations, foundations, and other entities worldwide.
Stony Brook was notified by Blackbaud on July 17 that “patient information may have been involved in a security incident on Blackbaud’s systems.”
Hospital patients have been warned that data that was on the Blackbaud systems affected by the cyber-attack may have included their name, date of birth, address, contact information, attending doctor, insurance provider, and medical service department.
“Stony Brook did not provide your Social Security number, bank account information or credit card number to Blackbaud, and so these types of information were not in Stony Brook’s files on the potentially affected systems,” the hospital told patients in a notification uploaded to its website.
Blackbaud assured the hospital that data stolen in the attack was destroyed and not used, sold, or distributed.
The healthcare provider said: “Based on statements from Blackbaud, we have no reason to believe that the information involved in this incident has been misused.”
The 624-bed hospital emphasized that the attack on Blackbaud did not involve access to any Stony Brook systems, including medical systems or electronic health records.
Stony Brook said that it will individually notify “potentially impacted patients for whom it has a valid mailing address.” It did not say how it intended to contact patients who did not have a valid mailing address.
Patients have been advised to regularly monitor any statements that they receive from their health plans or healthcare providers and check for any unfamiliar healthcare services.
Stony Brook said: “We are evaluating additional security measures and continue to conduct appropriate oversight of our vendors to help ensure this does not happen in the future.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Fatal Hospital Hack Linked to Russia

A cyber-attack that caused a German hospital to refuse treatment to a woman who subsequently died has been linked to a Russian ransomware gang.
Attackers struck Düsseldorf University Clinic (DUC) on the night of Thursday, September 10, gaining access by exploiting a vulnerability in some commercially available Citrix software.
The hospital’s IT systems crashed as a result, and patients seeking urgent care were diverted to another hospital 20 miles away in Wuppertal. A woman who had to seek urgent care elsewhere because the digitally besieged DUC was unable to treat her later died.
A spokesman for the responsible public prosecutor’s office at the Cybercrime Central and Contact Point (ZAC) said the investigation into the suspected negligent homicide of a patient is ongoing.
According to a report published today in German newspaper Aachener Zeitung, the cyber-attack on the DUC was carried out using crypto-locking DoppelPaymer malware.
First observed in April 2019, DoppelPaymer is a form of ransomware that is believed to have originated from Russia.
“DoppelPaymer is a fork of BitPaymer, and BitPaymer was attributed to Evil Corp, which has been sanctioned by the US and has ties to the Russian Government,” said Emsisoft‘s Brett Callow. “The nature of the relationship between DoppelPaymer and Evil Corp is not clear, but some cooperation has been observed.”
DoppelPaymer uses virus-themed email subject lines to attract victims. Like ransomware thugs MAZE, its operators extort money from victims by encrypting and exfiltrating their data and threatening to sell and/or publish sensitive information on the darknet.
News that DoppelPaymer was deployed in this tragic attack was included in a report to the German state parliament’s legal committee and announced earlier today by the Ministry of North Rhine-Westphalia.
An investigation into the cyber-incident by German authorities found that hackers smuggled a “loader” into the server at the DUC, possibly months before the next phase of the attack was carried out.
On the night of September 10, the criminals caused encryption software to be downloaded, infecting 30 servers at the DUC.
The hospital’s IT systems remain disrupted in the wake of the attack, threatening the safety of other people seeking urgent treatment. Emergency room services are expected to be restored this week.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Cisco: Ensure Collaboration to Better Survive Remote Working

Collaboration in an enterprise can better enable security going forward, after a challenging six months.
Speaking on a Cisco webinar, Wendy Nather, head of advisory CISOs, said there is need for collaboration over control, as “control presents greater cost for the enterprise.” Asking what you can ask users to take care of on the security side, and what can you no longer enforce, Richard Archdeacon, advisory CISO for Cisco EMEA said there is a chance CISOs are “losing control anyway and will need to become collaborative in order to secure their organizations.”
Fellow advisory CISO J. Wolfgang Goerlich said we have seen the workforce has become more savvy, and this has led to “creative things” in terms of the way the business works with the employees.
Goerlich said the idea of collaboration is sound, and asked how can we introduce constraints, yet still have good relations with the workforce? “Also, how can we leverage this savviness of the workforce that it is developing, and how can we embrace our shadow so to speak?”
Nather said the difference between collaboration and control could have a significant effect on how we build our security products, “not with the assumption that there is a centralized control point that is setting all of the policies and doing all the monitoring and the enforcement, but rather that there are multiple controls, some within the enterprise and some without.”
This has led to the concept of secure remote work, which Nather said when everyone needed to work from home, we saw some big problems in the supply chain and enterprises couldn’t get the laptops they needed for employees to take home and use what they have at home.
“That forced enterprises into BYOD, where they may not have necessarily embraced it before, but now they have no choice,” she said. “As a result of that, the users – especially in Europe – pushed back and are saying ‘this is not a corporate device and I do not want you monitoring it, I do not want any possibility you will erase my data’ and especially when users are at home. Those enterprises that are used to scanning endpoints for vulnerabilities cannot do it any more as the ISPs sitting between user at home and enterprise may see this as an attack.”
Nather said this has resulted into businesses saying to users that they can do what they wish on their own devices, but they need to meet security requirements to access corporate applications. “That is the balance, the collaboration that we are starting to see pushed more and more with remote work,” she said.
Goerlich said in times of stress and when everyone is trying to work remotely, when they go back to “tried and true security” like good MFA, DNS security and a good VPN connection. “One of the trends we’re seeing is in response to the stress, is a doubling down on bread and butter fundamental security controls,” he said.
Archdeacon said there is a trend to get the core fundamentals and controls correct, and now are looking back to ask how this will affect the business in the future. “This comes back to the point of collaboration and control, where we are going to shift the security control to endpoint and user and we’ve got to collaborate with them to be part of our frontline security team when they start to access our resources,” he said.
Nather concluded by saying that the remote work model had to be re-thought quickly, so many organizations had to put in whatever they could at the last minute, and this will impact on users, and ultimately CISOs too. “If they didn’t put in something sustainable at the beginning, they are going to have to now.”
It was also revealed Duo’s user authentications per month jumped from 600 million to 800 million per month due to the rush to enable remote work, while over 500 million meeting participants generated 25 billion meeting minutes in April, more than triple the volume in February.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
71% of CISOs Believe Cyber-warfare is a Threat to Their Organization

Over seven in 10 (71%) CISOs consider cyber-warfare to be a threat to their organization, according to Bitdefender’s global 10 in 10 study published today.
In addition, the report found that 50% of infosecurity professionals believe cyber-warfare will be detrimental to the overall economy during the next 12 months.
Despite this, over a fifth (22%) of CISOs admitted that they do not currently have a strategy in place to defend against this threat. More encouragingly, 51% of CISOs and 48% of infosec professionals acknowledged that they need a strategy to protect against cyber-warfare during the next 12-18 months.
The survey of 6,724 infosecurity professionals also showed that ransomware has risen substantially amid the COVID-19 pandemic in 2020, with 43% reporting seeing an increase in this type of attack. Close to three-quarters (70%) of CISOs/CIOs and 63% of infosec professionals said they expect to see ransomware attacks grow further in the next 12-18 months, while 59% of CISOs/CIOs and 50% of infosec professionals expressed fears that a ransomware attack could potentially wipe out their business in the next 12-18 months if there is no increased investment in security.
In order to gain internal investment to improve defences against these cyber-warfare and ransomware threats, there was agreement amongst 51% of infosec professionals that the way they communicate about security has to change dramatically. In regard to the type of changes needed, 41% of infosec professionals believe more communication with the wider public are required, both within and organization and outside. Additionally, 38% feel there should be better communication with C-suite executives, particularly in helping them appreciate the wider business risks posed by these cyber-attacks.
Liviu Arsene, global cybersecurity researcher at Bitdefender commented: “2020 has been a year of change — not only for the world at large — but for the security industry. The security landscape is rapidly evolving as it tries to adapt to the new normal, from distributed workforces to new threats. Amongst the new threats is cyberwarfare. It’s of great concern to businesses and the economy — and yet not everyone is prepared for it. At the same time, infosec professionals have had to keep up with new threats from an old source, ransomware, that can affect companies’ bottom lines if not handled carefully.
“The one thing we know is that the security landscape will continue to evolve. Changes will happen, but we can now make sure they happen for better and not for worse. To succeed in the new security landscape the way we as an industry talk about security has to become more accessible to a wider audience to gain support and investment from within the business. In addition, we have to start thinking about plugging the skills gap in a different way — we have to focus on diversity, and specifically neurodiversity, if we are to stand our ground and ultimately defeat bad actors.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk