New Bluetooth Vulnerability

There’s a new unpatched Bluetooth vulnerability:

The issue is with a protocol called Cross-Transport Key Derivation (or CTKD, for short). When, say, an iPhone is getting ready to pair up with Bluetooth-powered device, CTKD’s role is to set up two separate authentication keys for that phone: one for a “Bluetooth Low Energy” device, and one for a device using what’s known as the “Basic Rate/Enhanced Data Rate” standard. Different devices require different amounts of data — and battery power — from a phone. Being able to toggle between the standards needed for Bluetooth devices that take a ton of data (like a Chromecast), and those that require a bit less (like a smartwatch) is more efficient. Incidentally, it might also be less secure.

According to the researchers, if a phone supports both of those standards but doesn’t require some sort of authentication or permission on the user’s end, a hackery sort who’s within Bluetooth range can use its CTKD connection to derive its own competing key. With that connection, according to the researchers, this sort of erzatz authentication can also allow bad actors to weaken the encryption that these keys use in the first place — which can open its owner up to more attacks further down the road, or perform “man in the middle” style attacks that snoop on unprotected data being sent by the phone’s apps and services.

Another article:

Patches are not immediately available at the time of writing. The only way to protect against BLURtooth attacks is to control the environment in which Bluetooth devices are paired, in order to prevent man-in-the-middle attacks, or pairings with rogue devices carried out via social engineering (tricking the human operator).

However, patches are expected to be available at one point. When they’ll be, they’ll most likely be integrated as firmware or operating system updates for Bluetooth capable devices.

The timeline for these updates is, for the moment, unclear, as device vendors and OS makers usually work on different timelines, and some may not prioritize security patches as others. The number of vulnerable devices is also unclear and hard to quantify.

Many Bluetooth devices can’t be patched.

Final note: this seems to be another example of simultaneous discovery:

According to the Bluetooth SIG, the BLURtooth attack was discovered independently by two groups of academics from the École Polytechnique Fédérale de Lausanne (EPFL) and Purdue University.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Chinese Antivirus Firm Was Part of APT41 ‘Supply Chain’ Attack

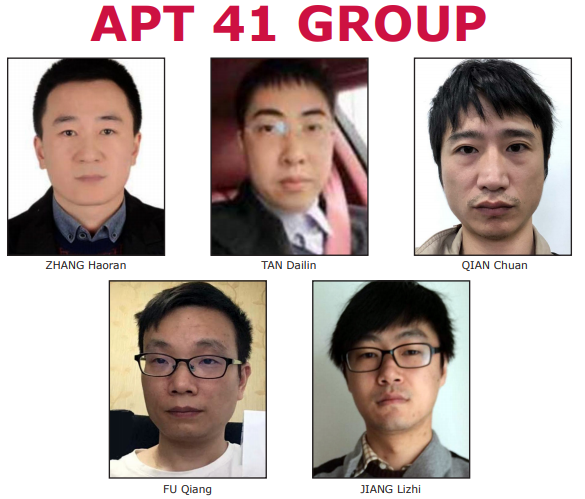
The U.S. Justice Department this week indicted seven Chinese nationals for a decade-long hacking spree that targeted more than 100 high-tech and online gaming companies. The government alleges the men used malware-laced phishing emails and “supply chain” attacks to steal data from companies and their customers. One of the alleged hackers was first profiled here in 2012 as the owner of a Chinese antivirus firm.

Image: FBI

Charging documents say the seven men are part of a hacking group known variously as “APT41,” “Barium,” “Winnti,” “Wicked Panda,” and “Wicked Spider.” Once inside of a target organization, the hackers stole source code, software code signing certificates, customer account data and other information they could use or resell.

APT41’s activities span from the mid-2000s to the present day. Earlier this year, for example, the group was tied to a particularly aggressive malware campaign that exploited recent vulnerabilities in widely-used networking products, including flaws in Cisco and D-Link routers, as well as Citrix and Pulse VPN appliances. Security firm FireEye dubbed that hacking blitz “one of the broadest campaigns by a Chinese cyber espionage actor we have observed in recent years.”

The government alleges the group monetized its illicit access by deploying ransomware and “cryptojacking” tools (using compromised systems to mine cryptocurrencies like Bitcoin). In addition, the gang targeted video game companies and their customers in a bid to steal digital items of value that could be resold, such as points, powers and other items that could be used to enhance the game-playing experience.

APT41 was known to hide its malware inside fake resumes that were sent to targets. It also deployed more complex supply chain attacks, in which they would hack a software company and modify the code with malware.

“The victim software firm — unaware of the changes to its product, would subsequently distribute the modified software to its third-party customers, who were thereby defrauded into installing malicious software code on their own computers,” the indictments explain.

While the various charging documents released in this case do not mention it per se, it is clear that members of this group also favored another form of supply chain attacks — hiding their malware inside commercial tools they created and advertised as legitimate security software and PC utilities.

One of the men indicted as part of APT41 — now 35-year-old Tan DaiLin — was the subject of a 2012 KrebsOnSecurity story that sought to shed light on a Chinese antivirus product marketed as Anvisoft. At the time, the product had been “whitelisted” or marked as safe by competing, more established antivirus vendors, although the company seemed unresponsive to user complaints and to questions about its leadership and origins.

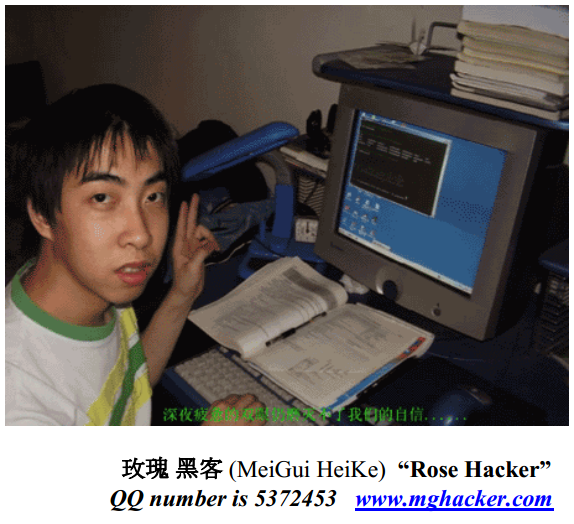
Tan DaiLin, a.k.a. “Wicked Rose,” in his younger years. Image: iDefense

Anvisoft claimed to be based in California and Canada, but a search on the company’s brand name turned up trademark registration records that put Anvisoft in the high-tech zone of Chengdu in the Sichuan Province of China.

A review of Anvisoft’s website registration records showed the company’s domain originally was created by Tan DaiLin, an infamous Chinese hacker who went by the aliases “Wicked Rose” and “Withered Rose.” At the time of story, DaiLin was 28 years old.

That story cited a 2007 report (PDF) from iDefense, which detailed DaiLin’s role as the leader of a state-sponsored, four-man hacking team called NCPH (short for Network Crack Program Hacker). According to iDefense, in 2006 the group was responsible for crafting a rootkit that took advantage of a zero-day vulnerability in Microsoft Word, and was used in attacks on “a large DoD entity” within the USA.

“Wicked Rose and the NCPH hacking group are implicated in multiple Office based attacks over a two year period,” the iDefense report stated.

When I first scanned Anvisoft at Virustotal.com back in 2012, none of the antivirus products detected it as suspicious or malicious. But in the days that followed, several antivirus products began flagging it for bundling at least two trojan horse programs designed to steal passwords from various online gaming platforms.

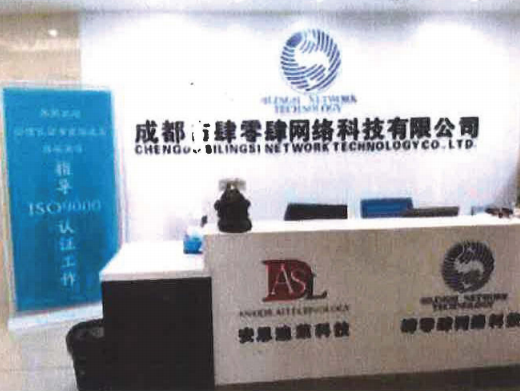
Security analysts and U.S. prosecutors say APT41 operated out of a Chinese enterprise called Chengdu 404 that purported to be a network technology company but which served a legal front for the hacking group’s illegal activities, and that Chengdu 404 used its global network of compromised systems as a kind of dragnet for information that might be useful to the Chinese Communist Party.

Chengdu404’s offices in China. Image: DOJ.

“CHENGDU 404 developed a ‘big data’ product named ‘SonarX,’ which was described…as an ‘Information Risk Assessment System,’” the government’s indictment reads. “SonarX served as an easily searchable repository for social media data that previously had been obtained by CHENGDU 404.”

The group allegedly used SonarX to search for individuals linked to various Hong Kong democracy and independence movements, and snoop on a U.S.-backed media outlet that ran stories examining the Chinese government’s treatment of Uyghur people living in its Xinjian region.

As noted by TechCrunch, after the indictments were filed prosecutors said they obtained warrants to seize websites, domains and servers associated with the group’s operations, effectively shutting them down and hindering their operations.

“The alleged hackers are still believed to be in China, but the allegations serve as a ‘name and shame’ effort employed by the Justice Department in recent years against state-backed cyber attackers,” wrote TechCrunch’s Zack Whittaker.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Lawsuit Filed Against Warner Music Group Over Data Breach

Lawsuit Filed Against Warner Music Group Over Data Breach

A lawsuit has been filed against Warner Music Group following the disclosure of a data breach that compromised customers’ sensitive personal information.

Warner notified customers of a breach earlier this month after discovering a number of its e-commerce websites had fallen victim to a prolonged skimming attack. 

Attackers were able to access personal data entered by customers into the impacted sites between April 25, 2020, and August 5, 2020. Information compromised in the attack included names, email addresses, telephone numbers, billing addresses, shipping addresses, credit card numbers, card expiration dates, and CVC and CVV codes. 

Following the cyber-incident, Morgan & Morgan has filed a class-action lawsuit against the music recording company on behalf of two plaintiffs.

Levi Combs of Marysville, Ohio, and Esteban Trujillo of Orlando, Florida, purchased items from websites operated by Warner in July 2020 and May 2020, respectively. 

Both men subsequently received Warner’s Notice of a Data Breach document at the beginning of September.

Combs and Trujillo allege that Warner failed to “properly secure and safeguard personal identifiable information, including without limitation, unencrypted names, email addresses, telephone numbers, billing addresses, shipping addresses, payment card numbers, payment card CVV security codes, and payment card expiration dates.”

The plaintiffs further claim that the company “failed to provide timely, accurate, and adequate notice to plaintiffs and similarly situated WMG customers (‘Class Members’) that their PII had been stolen by hackers, and precisely what types of information was unencrypted and in the possession of unknown, unauthorized third parties.”

In August, the same payment cards that Combs and Trujillo had used to make purchases from Warner’s hacked websites were used by an unknown third party or parties to make two unauthorized purchases, one of which was declined by the bank after appearing suspicious. 

“These large companies know the risk posed by cyber-criminals and continue to be cavalier with their customers’ personal information,” said Morgan & Morgan attorneys John Morgan and Jean Martin in a statement. 

“The fact that this breach allegedly went on undetected for more than three months demonstrates the alleged lack of care taken by Warner Media Group to secure its customers’ information.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

US Staffing Firm Hit by Ransomware Again

US Staffing Firm Hit by Ransomware Again

One of the largest IT staffing companies in America has been hit by a second ransomware attack in nine months. 

At the start of September, Artech Information Systems disclosed a data breach caused by a ransomware attack perpetrated between January 5 and 8, 2020.

Attackers deployed the ransomware three days after gaining unauthorized access to some of the company’s systems. The incident was picked up by the company following reports of suspicious activity on the user account of an Artech employee.

Ransomware gang REvil (Sodinokobi) presented themselves as responsible for the attack on Artech. After apparently failing to blackmail a ransom payment out of the company, on January 11 the gang leaked what they claimed was 337 MB of data stolen from Artech’s servers. 

Now it appears that the company has been hit with ransomware for a second time, but from a different source.

The profitable business, which brought in around $810m in annual revenue last year, is among the victims listed on the website of the threat group MAZE.

Along with the announcement of the alleged hack, MAZE has uploaded a zip file of data it claims to have stolen from Artech. 

Commenting on the alleged second ransomware attack, Emsisoft threat analyst Brett Callow told Infosecurity Magazine: “It’s not uncommon to see companies hit for a second time, and sometimes by a different ransomware group. In some cases, this will simply be coincidence. In other cases, it’s likely that the network was backdoored during the initial attack and the backdoor was subsequently sold or traded to whichever group carried out the second attack.”

Callow added that it was absolutely critical for any company hit by ransomware to take appropriate action to remediate the incident. 

“Failing to do so can result in a second attacker’s maintaining a foothold in the network, monitoring communications, continuing to exfiltrate data, and encrypting it for a second time,” said Callow.

Artech is a privately-held firm that provides government services, workforce and staffing solutions, and program management. It employs over 10,500 staff and consultants across the United States, Canada, China, and India.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Attacks on Mid-Market Organizations Soar

Attacks on Mid-Market Organizations Soar

Cyber-attacks on middle-market organizations have risen significantly since the outbreak of COVID-19 reached pandemic proportions.

According to global data gathered by specialist insurer Beazley Group, middle-market organizations have been especially hard hit by online social engineering attacks. 

In the report “Beazley Breach Insights – Q2 2020,” published today, the insurer said: “The arrival of the global pandemic provided cybercriminals with the perfect cover for ramping up email attacks. 

“Coinciding with the increase in remote working during the second quarter, our global data has shown employees have been more likely to fall for social engineering scams, with organizations in the middle market most likely to be victimized.”

Of all the social engineering attacks reported to Beazley Breach Response (BBR) Services globally in Q2 2020, 60% of organizations targeted were in the middle market (defined as over $35m in annual revenue), up from 46% in Q1.

In more than 80% of the incidents reported, the attack was stymied before a direct financial loss occurred.

Fraudulent instruction attacks also primarily hit middle-market organizations, which were the target in 55% of incidents, compared to 24% in Q1.

“Middle market organizations have been resilient in maintaining their day-to-day operations during the pandemic and, in turn, their employees are more available to be targeted. Additionally, cybercriminals are executing more sophisticated attacks and middle market organizations provide richer targets,” said Kimberly Horn, Beazley’s global claims team lead for cyber and tech.

“As our global breach data has demonstrated, if an incident is responded to early enough, an organization can often avoid a direct financial loss such as stolen funds. Modest investments in training and process changes could reduce the likelihood of falling victim,” she added.

In their report, the insurer suggests that employees who took up remote working because of the pandemic may be more susceptible to suspicious emails.

“While the increase in distractions that come with caring for family members while working have been widely discussed, physical separation from the workplace is also a factor,” states the report.

“Without a coworker to converse with at the next desk, employees are less likely to do a ‘sense check’ of a suspicious email.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

#GartnerSEC: Understanding a Changing Threat Landscape in Light of #COVID19

#GartnerSEC: Understanding a Changing Threat Landscape in Light of #COVID19

Organizations must become agile to respond effectively to the changing threat landscape, particularly in light of the turbulent events of 2020, according to Jonathan Care, senior director analyst at Gartner, speaking during the Gartner Security and Risk Virtual Summit. He noted: “We’ve seen drastic changes in how we as a society work and play as a result of the COVID-19 pandemic, and bad actors have taken notice.”

In doing so however, organizations must be careful not to be overly swayed by certain threats that may gain a lot of news coverage, but do not necessarily pose the greatest danger. Instead, a “risk-based approach” should be employed that focuses on the fluidity of threats.

Care said: “As threats and organizational risk-pots change over time, we must evolve how we address the threat landscape.” This notion has never been more applicable amid new behaviors brought about by COVID-19. He added: “Threats continue to change and diversify. New business opportunities drive new security requirements that we must address.”

Ransomware is currently the number one threat to organizations, according to Gartner. Care outlined that these attacks have become increasingly sophisticated, including the use of fileless malware that can bypass some preventive controls and attackers adding persistence to keep malware dormant for long periods. Therefore, adequate planning to react quickly to this type of threat is needed, such as being able to detect the type of malware being used and having capabilities to isolate infected systems quickly.

Care also said that due to changing working practices, many organizations are moving away from email as the primary communication method to other collaborative tools. This change is being exploited by attackers. “The low hanging fruit now are cloud services, which are often exposed to the internet and suffer from misconfigurations and can be susceptible to credential stuffing attacks,” he commented.

In regard to phishing, more targeted tactics like spear-phishing and whaling are becoming more prominent; in one example given, deepfake technology was used to successfully impersonate an executive and convince someone to wire money to a hacker’s bank account. Care said that as well as new tools, “attention to the people and processes in use” is crucial to protect against these methods.

Account takeover is another type of threat that has grown this year. One particularly dangerous example is the expanding practice of SIM swapping, enabling criminals to take over a phone number and reset passwords as a result. While multi-factorial authentication (MFA) remains the best way of defending against this, Care added that organizations must be aware that “attackers are shifting their tactics to bypass the MFA controls you have in place.”

Care also highlighted the increasing risk of attacks emanating from organizations’ supplier and partner relationships. He gave an example of organizations which enable employees to download and use consumer grade utilities, which if compromised, can be used to launch attacks on their systems. “If supply chain is currently not part of your threat environment, then it needs to be on the list of threats that need consideration as you examine those connections and relationships that you have,” he outlined.

Constant monitoring of the threat landscape is therefore critical for organizations to adequately protect themselves. Care concluded: “Understanding the trends and risks allows us to invest in the right equipment to navigate the rough waters ahead.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

#GartnerSEC: Top Trends for Risk and Security Include Cloud, Automation and Privacy

#GartnerSEC: Top Trends for Risk and Security Include Cloud, Automation and Privacy

The current top trends in security and risk management for threat-facing, disruption and the organization have been detailed at the Gartner Security and Risk Virtual Summit.

Speaking at the event, research VP Peter Firstbrook pointed at “mega trends that are beyond your control,” which include: the skills gap, regulation and privacy, application scale and complexity, endpoint diversity, attackers and the impact of COVID-19. He said that COVID-19 has accelerated a lot of the trends Gartner has been seeing in the last 10 years, and if your organization is mature “you’re probably in a good space to handle COVID.”

The top eight trends he cited were as follows:

Extended Detection and Response (XDR) – Firstbrook said this tool is replacing SIEM and SOAR tools and providing organizations to be “more operationally secure in their operations than by investing and trying to integrate a best of breed set of products.”

He said that XDR unites security tools into a common data format and make correlations between events, and gives the user an integrated incident response experience where products are combined into one. “Start prioritizing the product that you need to focus in on, so start focusing on where you think it is important to have integrated information and to do incident response,” he said.

Security Process Automation – This is a trend across products, as vendors invest in this to address the skills gap, and to make it “easier to get repetitive tasks done.” Firstbrook recommended looking at long manual processes and ways to automate that, and to develop a playbook to know what steps to go though. Also, look for products with API and automation technology built in.

Securing Artificial Intelligence – Firstbrook said this is becoming a security and risk manager’s responsibility. “A lot of organizations have invested in AI and machine learning, but very few have looked at how that AI might be gained by a malicious attacker,” he said. He recommended looking at machine learning algorithms, and what attacks can be made against them.

Impact of Cyber on the Physical World – This includes IoT and machinery, as Firstbrook said the duties of security and risk managers become about more than traditional information security to include safety too. This includes factory machinery that is not as well protected, as well as building security where “siegeware” attackers lock you out of a building or mess with the HVAC system. “These are issues that information security doesn’t address, so we see organizations reorganize and put someone from infosec or cybersecurity to work across disciplines – operational security, supply chain security and product management security,” he said. “These are all areas that need to be addressed that not necessarily are.”

Form Trust and Safety Teams – These teams form a “digital perimeter” which includes points where the customer interacts with your environment: your call center, website, social media, some physical presences. Firstbrook recommended forming at least a part time trust and safety team to include marketing, a brand manager, legal, privacy “and look at the environment holistically” and inventory controls to organize around that

Privacy – Firstbrook said this is becoming an influential discipline of its own, as it has been a part time job of the organization in the past, but now it is becoming a full time role. “The reason they are doing this is because organizations are concerned about financial loss, concerned about losing customers and worried about suffering from reputational damage.”

To do this efficiently, businesses should focus on assessing the data and business risk that a business has in its environment. The three areas to focus on are: consent and making sure customers opt in to share data with you, transparency so they know what you’re storing and why you’re storing it, and self-management to be able to manage and delete data.

Secure Access Service Edge (SASE) – Firstbrook said this is enabling your WAN architecture to look more like local area network (LAN) architecture. “So how do you regain visibility and control into these applications and services that exist outside of your environment, with the users that are also outside the environment?” He recommended SASE as the way to do it, as it is the integration of network security controls with new tech like remote access technology and CASB, which merge into a single platform “to provide all of this connectivity across all of the internet, and make the internet feel like your WAN.”

Cloud Workload Protection – This is seeing a number of disruptive vendors come in, where cloud applications are protected from development to production, as we see applications built bespoke, in containers and across SaaS services. “So you need an inventory of what they are using, where they are and what protocols are they using, and where the credentials being are stored – managing all of that has become very complex,” he said.

In conclusion, Firstbrook recommended taking a step back to “look at the broader picture and not just at individual problems.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Outbound Email Errors Cause 93% Increase in Breaches

Outbound Email Errors Cause 93% Increase in Breaches

IT leaders have suffered significantly higher numbers of data breaches as a result of outbound email in the last 12 months.

According to research by Egress, 93% of 538 IT leaders surveyed reported a breach in the past year due to an email error, with 70% of those believing remote working increases the risk of sensitive data being put at risk from outbound email data breaches.

Egress CEO Tony Pepper said the problem is only going to get worse with increased remote working and higher email volumes, which create prime conditions for outbound email data breaches of a type that traditional DLP tools simply cannot handle.

“Instead, organizations need intelligent technologies, like machine learning, to create a contextual understanding of individual users that spots errors such as wrong recipients, incorrect file attachments or responses to phishing emails, and alerts the user before they make a mistake,” he said.

The most common breach types were replying to spear-phishing emails (80%), emails sent to the wrong recipients (80%) and sending the incorrect file attachment (80%).

Speaking to Infosecurity, Egress VP of corporate marketing Dan Hoy, said businesses reported an increase in outbound emails since lockdown, “and more emails mean more risk.” He called this a numbers game which has increased risk as remote workers are more susceptible and likely to make mistakes the more they are removed from security and IT teams.

According to the research, 76% of breaches were caused by “intentional exfiltration.” Hoy confirmed this is a combination of employees innocently trying to do their job and not cause harm by sending files to webmail accounts, but this does increase risk “and you cannot ignore the malicious intent.”

This is where better technology could better resolve the problem, he said, as current technology (such as static rule-based data loss prevention) does not catch these issues and problems increase. “Technology needs to shoulder more of the burden,” Hoy added.

Furthermore, almost two-thirds (62%) of businesses rely on people to identify outbound email data breaches, whilst 24% of IT leaders said the employee who sent the email would disclose their error. In terms of action taken, 46% of respondents said the employee who caused a breach was given a formal warning, while legal action was taken in 28% of cases. In 27% of serious breach cases, respondents said the employee responsible was fired.

Hoy pointed to the 62% statistic and the fact that we are “still reliant on people to self report incidents” and called outbound email errors combined with remote workers as a “perfect storm.” Regarding employees being reprimanded, he said it is an interesting debate as to where responsibility lies.

Pepper said: “Relying on tired, stressed employees to notice a mistake and then report themselves or a colleague when a breach happens is unrealistic, especially given the repercussions they will face. With all the factors at play in people-led data breach reporting, we often find organizations are experiencing 10-times the number of incidents than they are aware of.

“It’s imperative that we build a culture where workers are supported and protected against outbound email breach risk with technology that adapts to the pressures they face and stops them from making simple mistakes in the first place. As workers get used to more regular remote working and reliance on email continues to grow, organizations need to step up to safeguard both employees and data from rising breach risks.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

#GartnerSEC: Rewrite Recruitment Strategies to Fit New Roles and Career Paths

#GartnerSEC: Rewrite Recruitment Strategies to Fit New Roles and Career Paths

Speaking during the Gartner Security and Risk Virtual Summit, research director David Gregory said the COVID-19 pandemic could be “considerable, in terms of the number of people who might be available” to fill security job roles. Despite this, he said it is unlikely this will lead to the right skills being available.

Globally, Gregory said that it was predicted that the skills gap would remain, and he suspected the impact of COVID-19 would not affect that.

He said a “fundamental issue is business are often guilty of looking in the wrong place for the wrong people with the wrong skills,” and it is the view of Gartner that there are underlying problems holding organizations back in this area. This includes businesses trying to find the “right candidate, even though this is never guaranteed.”

He also said a demand for “instant results” has led to a demand for instant talent rather than forming a long-term strategy, and organizations “develop their resilience strategy in silos, so working in this way we’re not able to see the bigger picture.”

Citing Gartner statistics which showed 61% of survey respondents said they are struggling to find and hire security professionals, Gregory said this requires an organizational response, as if a business operates in silos, “they will never understand full business concerns.” He also said that whilst IT and technical knowledge is important, business should be able to “engage with people at all levels of the organization, coupled with business acumen, which will be every bit as valuable in the future.”

He said the following skills are in demand, and can be developed and trained, and may also be suitable for outsourcing:

  • Information security/cybersecurity analyst
  • Security engineer/architect
  • Vulnerability analyst/penetration tester
  • Cyber-threat analyst
  • Risk assurance analyst
  • Information security/cybersecurity manager

“Now, more than ever, there is a need to ensure we have the right skills and competencies within our organizations,” he said. “The impact of COVID-19 will provide significant business challenges and lead almost certainly to organizations having to do more with less. There will be a need to focus on ensuring that the right skills are available to drive your organization through and beyond these difficult times.”

Gregory also said the COVID-19 pandemic will allow organizations to remove a “need to be in the office” mentality to hiring, “and the recruitment net can be cast over a wider geographic area for roles that can now be fulfilled remotely.”

For a strategic workforce planning process, Gregory recommended these steps:

  1. Understand business strategy, define value drivers/capabilities
  2. Segment roles by impact on capability delivery
  3. Scan the environment to identify key factors driving future-state scenarios
  4. Construct scenarios for the future state of the workforce
  5. Assess the current state of the workforce, define gaps against the future states
  6. Develop action plans to close gaps, monitor process and adjust for change

“There will be a need to bridge the skills gap inside the organization,” he said. “Taking a market-driven predictive approach connects those employees and learners to those in-demand skills. So to stay ahead of the curve, there is a need to consider reviewing the skills and recruitment strategy within your organization.”

A way to do this is to create job ladders so employees can see a career path, rather than just a job, which can better ensure employees remain with a company and make an organization “a destination of choice.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk