Companies that Scrape Your Email

Motherboard has a long article on apps — Edison, Slice, and Cleanfox — that spy on your email by scraping your screen, and then sell that information to others:

Some of the companies listed in the J.P. Morgan document sell data sourced from “personal inboxes,” the document adds. A spokesperson for J.P. Morgan Research, the part of the company that created the document, told Motherboard that the research “is intended for institutional clients.”

That document describes Edison as providing “consumer purchase metrics including brand loyalty, wallet share, purchase preferences, etc.” The document adds that the “source” of the data is the “Edison Email App.”

[…]

A dataset obtained by Motherboard shows what some of the information pulled from free email app users’ inboxes looks like. A spreadsheet containing data from Rakuten’s Slice, an app that scrapes a user’s inbox so they can better track packages or get their money back once a product goes down in price, contains the item that an app user bought from a specific brand, what they paid, and an unique identification code for each buyer.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Aflac to Open Global Cybersecurity Center in Belfast

Aflac to Open Global Cybersecurity Center in Belfast

A subsidiary of American insurance giant Aflac is to open a global IT and cybersecurity center in the Northern Irish capital city of Belfast. 

Aflac Northern Ireland signed a 10-year lease with Belfast Harbor on 11,000 sq ft of office space within the ongoing multi-million-dollar waterfront development City Quays. With the opening of the new center on regenerated dockland, Aflac Northern Ireland will create 130 jobs by 2023.

City Quays is currently being constructed on a 20-acre stretch of ex-shipping land in Belfast City Centre. Upon completion, the development will boast office spaces, leisure facilities, a four-star AC Hotel by Marriott Belfast, retail spaces, and multi-story parking. 

Aflac Northern Ireland is a subsidiary of Georgia-headquartered Aflac Incorporated, which provides supplemental health insurance to customers in the US and Japan. The company, which is ranked at 143 on the Fortune 500 list, announced plans to invest in Northern Ireland in October 2019.

Joe O’Neill, CEO of Belfast Harbor, welcomed Aflac’s decision to site the new center at City Quays, which has already secured leading global law firm Baker McKenzie and the broadcasting organization ITV as tenants.

Baker McKenzie was the first tent to move into the office space within City Quays in June 2015. In 2018, the company leased an additional floor of space to accommodate its growing business. 

O’Neill said: “There are currently over 5,500 workers based in City Quays and Clarendon Dock, and our ambition is that City Quays on completion will accommodate 13,000 people living and working on Belfast’s waterfront.”

Keith Farley, managing director and vice president of Aflac Northern Ireland, said: “City Quays offers an ideal location for technology innovation with its modern facilities and amenities.”

Aflac’s news comes just two weeks after Microsoft announced plans to establish a new cybersecurity center in Belfast. The IT giant’s proposed facility is expected to create 85 new jobs.

Economy Minister Diane Dodd described Microsoft’s decision to site the center in Belfast as “exciting and welcome news.”

Dodd said: “Not only is it a direct result of the skills and talent available here, but it is also an indicator of the strength and vibrancy of the local IT sector, particularly in the field of cyber security.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

White House Asks Congress for Largest IT Budget in History

White House Asks Congress for Largest IT Budget in History

President Donald Trump’s fiscal 2021 budget includes the largest ever information technology funding request in United States history. 

The White House is asking Congress to approve IT funding of $92.1 billion, up from the $91.9 billion sought in 2020 and the $88.7 billion requested in 2019. By contrast, the amount of cash the president is seeking to spend on cybersecurity in 2021 dropped from the $18.79 billion he asked for in 2020 to $18.18 billion. 

According to the budget, funds secured for IT “will be used to deliver critical citizen services, keep sensitive data and systems secure, and to further the vision of modern Government.”

Modernization is a key focus of the budget, with the administration revealing plans to replace highly customized, internally developed, and often single task–oriented systems that are costly to maintain and secure with “commercial off the shelf technologies that largely enable more efficient use of Federal technical resources.”

The budget states: “The Administration continues to pursue its IT Modernization CAP Goal, with its three-pronged approach focusing on enhancing Federal IT and digital services, reducing cybersecurity risks to the Federal mission, and building a modern IT and cybersecurity workforce.”

Federal chief information officer Suzette Kent said on Monday the IT budget was about “not only improving service, but saving money as well.” 

Kent said: “You see investments in shared services continue that helps us save money across agencies on the modernization side. We will continue the savings as we consolidate data centers.”

Another key policy identified in the budget is advancing automation, artificial intelligence (AI), and robotic process automation (RPA).

The budget states: “To maintain America’s AI advantage, federal agencies are to focus on two distinct areas. The first area of focus is internal—Federal use of AI to better achieve agency missions and serve citizens.

“The second focus area is external—including provision of data and related resources to support the private sector and academia in their efforts to harness AI. In both of these areas, the administration’s policies and strategies aim to accelerate AI innovation to increase our prosperity, enhance our national/economic security, and improve our quality of life.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

China Denies Involvement in Equifax Hack

China Denies Involvement in Equifax Hack

The People’s Republic of China (PRC) has denied any involvement in the Equifax hack that saw the personal data of nearly half of America’s population exposed. 

Yesterday the United States’ Department of Justice issued a nine-count indictment against four Chinese military personnel in connection with the cyber-attack, which took place from May to July 2017.

The US alleges that Wu Zhiyong (吴志勇), Wang Qian (王乾), Xu Ke (许可), and Liu Lei (刘磊), who are all members of the Chinese People’s Liberation Army (PLA), conspired to access Equifax’s computer systems. The defendants are accused of stealing trade secrets and the personal data of 145 million American citizens from the credit reporting agency. 

In a statement issued today from Beijing, PRC foreign ministry spokesperson Geng Shuang strongly denied that the Chinese military or government were responsible for this or any other cyber-attack. 

During a briefing, which was held over social media app WeChat to minimize the risks associated with the current outbreak of coronavirus in the PRC, Shuang wrote: “We firmly oppose and combat cyberattacks of any kind. China is a staunch defender of cybersecurity.”

Shuang further denied that the theft of data from Equifax had been a state-sponsored initiative conducted with the backing of the PRC.

“The Chinese government, military and relevant personnel never engage in cyber-theft of trade secrets,” wrote Shuang. 

According to Shuang, the same cannot be said of the United States, whom he accused of carrying out cyber-espionage activities on a grand scale. 

In the international diplomacy equivalent of the time-honored playground retort, “whoever smelt it, dealt it,” Shuang portrayed America rather than China as the cyber-aggressor.

Shuang wrote: “It has long been an open secret that relevant departments in the US, in violation of international law and basic norms governing international relations, have been engaging in large-scale, organized and indiscriminate cyber stealing, spying and surveillance activities on foreign governments, enterprises and individuals.”

Shuang went on to cite the cases of WikiLeaks and whistleblower Edward Snowden as examples of the “hypocrisy and double standards” being exercised by America when it came to cybersecurity. 

He added: “According to plenty of information that has been made public, US agencies have been engaging in cyber intrusion, surveillance and monitoring activities on foreign governments, institutions, enterprises, universities and individuals, including on its allies.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Year of the Catfish: 27% of Dating Site Users Scammed

Year of the Catfish: 27% of Dating Site Users Scammed

The UK banking industry is warning consumers not to fall victim to romance fraud, after revealing that over a quarter (27%) of dating website users have been scammed by fake personas over the past year.

Known as “catfishing,” these usually involve a fraudster posing as someone they’re not in order to gain the trust of those looking for love on a dating site.

Once they’ve ingratiated themselves, they typically will try to trick the victim into wiring them funds to deal with an ‘emergency,’ or even to become unwitting money mules.

Over a fifth (21%) of dating website users told UK Finance they have either been asked for money or have given money to someone that they met online. The average amount was £321, although in total £7.9m was lost to romance scams in the first half of 2019, an increase of 50% on the previous year.

The banking lobby group warned that over half (55%) of dating site users are inviting trouble by claiming to trust the people they meet online before they’ve seen them in person.

Men (33%) were more likely to say they had been catfished than women (20%), and also more likely to be asked for money than women (26% versus 15%).

Katy Worobec, managing director of economic crime at UK Finance, urged netizens to be cautious ahead of Valentine’s Day on Friday.

“Romance scams are both emotionally and financially damaging for victims,” she added.

“Although banks are always looking out for suspicious activity, customers must be on their guard and protect themselves too. Always be wary of requests for money from someone you’ve never met in person. If you think you’ve been the victim of a romance scam, contact your bank immediately.”

The research comes a week after the FBI released a similar warning to lonely hearts. According to the Bureau’s Internet Crime Complaint Center (IC3), 18,000 victims reported losses of over $362m in 2018.

Stay up-to-date with the latest information security trends and topics by registering for Infosecurity Magazine’s next Online Summit. Find out more here.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

LORCA and Kx Partner to Boost Cyber-Scaleups with Advanced Analytics

LORCA and Kx Partner to Boost Cyber-Scaleups with Advanced Analytics

The London Office for Rapid Cybersecurity Advancement (LORCA) has announced a new partnership with Kx to enhance cyber-scaleups through access to advanced data processing capabilities.

LORCA is a government-backed program that supports the UK’s most innovative cyber-companies with the aim of growing the UK’s cybersecurity sector and making the internet a safer place.

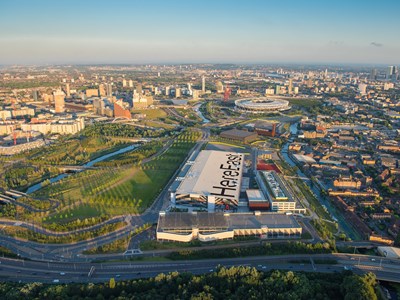
Based in East London and run by Plexal, LORCA offers members a range of forums, programs and events aimed at helping them develop, convening academia, innovators, government, investors and industry into a cross-sector, non-competitive and collaborative ecosystem.

Through the partnership with Kx, which will be spearheaded by Kx Ventures – an arm of the Kx company – LORCA members will receive 12 months of dedicated support designed to help them scale, and will have access to the Kx platform, allowing them to improve their product research and development by processing and analyzing data more efficiently.

Saj Huq, program director, LORCA, said: “Every successful cyber-company starts with a validated, market-ready product. Working with Kx will provide a valuable opportunity for LORCA members to glean advanced, data-led insights and improve their market readiness, as well as access commercial expertise from Kx.”

Paul Hollway, head of Kx Ventures, added: “We have been impressed by the caliber of innovators LORCA has sourced from around the world and the cluster’s ability to drive such companies to success. We look forward to supporting them as a technology partner.”

Stay up-to-date with the latest information security trends and topics by registering for Infosecurity Magazine’s next Online Summit. Find out more here.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Danes Blame Bug for ID Leak Affecting 1.3 Million

Danes Blame Bug for ID Leak Affecting 1.3 Million

The Danish government is under fire after an audit revealed that the personal identity numbers of over a fifth of the country’s population were leaked to US tech providers for five years.

The issue was discovered by the Agency for Development and Simplification (Udviklings-og Forenklingsstyrelsen) which maintains the country’s tax office IT systems.

It is linked to a software bug in the TastSelv Citizen portal used by taxpayers, which meant that ID (CPR) numbers appeared in the web address after a user updated their details.

This in turn meant that the numbers, as part of these URLs, were sent to analytics providers Google and Adobe. According to tech supplier DXC Technology, 1.26 million citizens were affected by this leak between 2015 and 2020, while a further 1330 were caught up in a smaller incident from January 29 to February 1 2020.

The government agency was quick to play down the seriousness of the incident, confirming that no other payroll, tax or personal data was included in the privacy snafu, and that the leaked CPR numbers were sent via an encrypted connection.

“This is an older software bug that has been fixed today. It is important to note that in both cases there is no risk that the information sent has been misused. In one case, the information has been deleted as an integral part of the recipient process, meaning it is neither logged in nor stored with Google,” said Andreas Berggreen, director of the Danish Development and Simplification Board.

“We take these kinds of cases very seriously, and of course we need to be able to make sure that our suppliers handle all data according to applicable law and within the framework agreed upon with them. We must note that this has not been the case here, and that is why we have asked the attorney general to assess what legal steps the case is giving to the supplier.”

The incident is nowhere near the scale of Scandinavian neighbor Sweden, which imperiled the top secret details of government officials after failing to mandate security clearance for outsourced transport agency staff in Serbia and the Czech Republic.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

DevOps Alert: 12,000 Jenkins Servers Exposed to DoS Attacks

DevOps Alert: 12,000 Jenkins Servers Exposed to DoS Attacks

Security researchers are warning that 12,000 cloud automation servers around the world could be hijacked to launch denial of service (DoS) attacks.

Radware issued an emergency response team threat alert yesterday after discovering 12,802 Jenkins servers that are still vulnerable to a flaw patched at the end of January.

Discovered by Adam Thorn of the University of Cambridge, CVE-2020-2100 affects Jenkins 2.218 and earlier as well as LTS 2.204.1 and earlier.

“Jenkins’ vulnerability is caused by an auto-discovery protocol that is enabled by default and exposed in publicly facing servers,” explained Radware security evangelist, Pascal Geenens. “Disabling the discovery protocol is only a single edit in the configuration file of Jenkins and it got fixed in last week’s patch from a default enabled to disabled.”

The bug could enable attackers to compromise exposed servers to launch two different types of DoS: an amplification attack and an infinite loop attack.

The latter was described by Geenens as “particularly nasty,” because “with a single spoofed packet, a threat actor can make two servers go into an infinite loop of replies, and they cannot be stopped unless one of the servers is rebooted or has its Jenkins service restarted.

“The same exposed service can also be abused by malicious actors to perform DDoS amplification attacks against random victims on the internet – victims do not have to run or expose Jenkins for the amplification attack to impact them,” he continued.

“If your DevOps teams are using Jenkins servers in their cloud or on-prem environments, there is a simple solution: either disable auto-discovery protocol if you do not use it or add a firewall policy to block access to port udp/33848.”

Open source Jenkins servers are popular among DevOps teams, which use them to build, test and deploy apps running in the cloud in environments such as Amazon Web Services, OVH, Hetzner, Host Europe, DigitalOcean and Linode.

Stay up-to-date with the latest information security trends and topics by registering for Infosecurity Magazine’s next Online Summit. Find out more here.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk