State-sponsored actors may have been behind the social media abuse, said Twitter.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
The Norwegian Consumer Council has published an extensive report about how the adtech industry violates consumer privacy. At the same time, it is filing three legal complaints against six companies in this space. From a Twitter summary:
1. [thread] We are filing legal complaints against six companies based on our research, revealing systematic breaches to privacy, by shadowy #OutOfControl #adtech companies gathering & sharing heaps of personal data. https://forbrukerradet.no/out-of-control/#GDPR… #privacy
2. We observed how ten apps transmitted user data to at least 135 different third parties involved in advertising and/or behavioural profiling, exposing (yet again) a vast network of companies monetizing user data and using it for their own purposes.
3. Dating app @Grindr shared detailed user data with a large number of third parties. Data included the fact that you are using the app (clear indication of sexual orientation), IP address (personal data), Advertising ID, GPS location (very revealing), age, and gender.
From a news article:
The researchers also reported that the OkCupid app sent a user’s ethnicity and answers to personal profile questions — like “Have you used psychedelic drugs?” — to a firm that helps companies tailor marketing messages to users. The Times found that the OkCupid site had recently posted a list of more than 300 advertising and analytics “partners” with which it may share users’ information.
This is really good research exposing the inner workings of a very secretive industry.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
A Pennsylvania man who operated one of the Internet’s longest-running online attack-for-hire or “booter” services was sentenced to five years probation today. While the young man’s punishment was heavily tempered by his current poor health, the defendant’s dietary choices may have contributed to both his capture and the lenient sentencing: Investigators say the onetime booter boss’s identity became clear after he ordered a bacon and chicken pizza delivered to his home using the same email address he originally used to register his criminal attack service.
David Bukoski, 24, of Hanover Township, Pa., pleaded guilty to running Quantum Stresser, an attack-for-hire business — also known as a “booter” or “stresser” service — that helped paying customers launch tens of thousands of digital sieges capable of knocking Web sites and entire network providers offline.
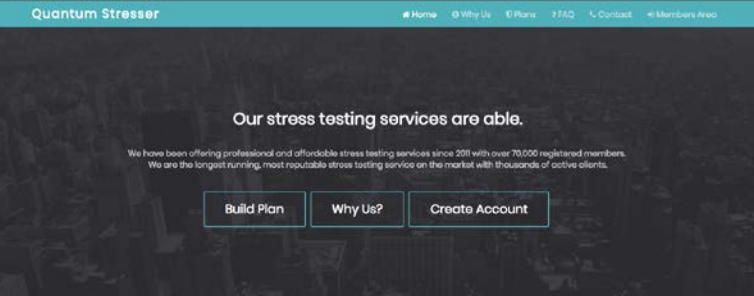
The landing page for the Quantum Stresser attack-for-hire service.
Investigators say Bukoski’s booter service was among the longest running services targeted by the FBI, operating since at least 2012. The government says Quantum Stresser had more than 80,000 customer subscriptions, and that during 2018 the service was used to conduct approximately 50,000 actual or attempted attacks targeting people and networks worldwide.
The Quantum Stresser Web site — quantumstress[.]net — was among 15 booter services that were seized by U.S. and international authorities in December 2018 as part of a coordinated takedown targeting attack-for-hire services.
Federal prosecutors in Alaska said search warrants served on the email accounts Bukoski used in conjunction with Quantum Stresser revealed that he was banned from several companies he used to advertise and accept payments for the booter service.
The government’s sentencing memorandum says Bukoski’s replies demanding to know the reasons for the suspensions were instrumental in discovering his real name. FBI agents were able to zero in on Bukoski’s real-life location after a review of his email account showed a receipt from May 2018 in which he’d gone online and ordered a handmade pan pizza to be delivered to his home address.
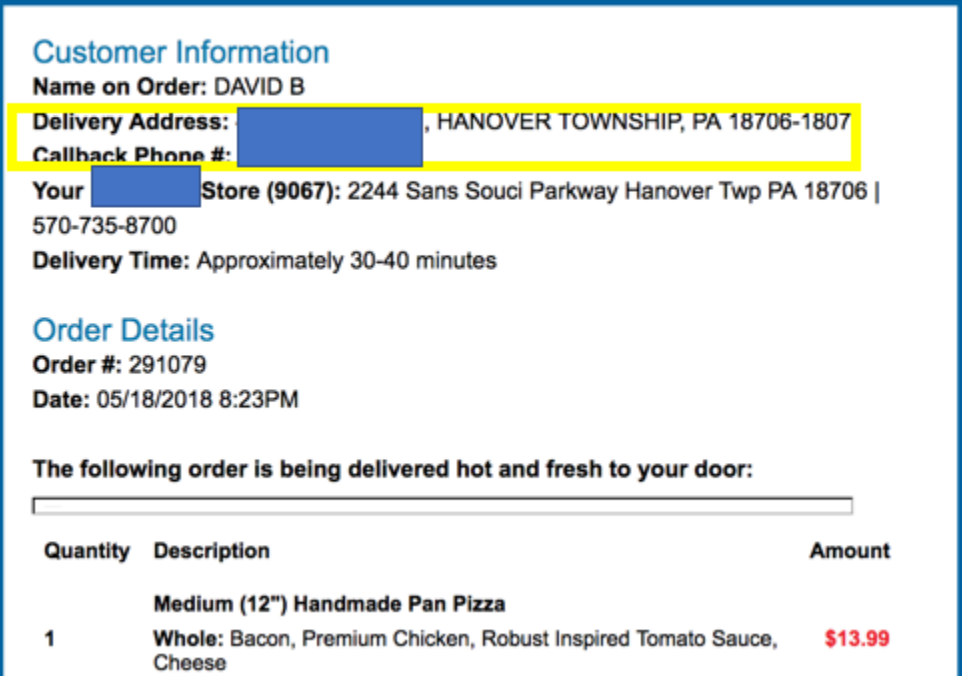
When an online pizza delivery order brings FBI agents to raid your home.
While getting busted on account of ordering a pizza online might sound like a bone-headed or rookie mistake for a cybercriminal, it is hardly unprecedented. In 2012 KrebsOnSecurity wrote about the plight of Yuriy “Jtk” Konovalenko, a then 30-year-old Ukrainian man who was rounded up as part of an international crackdown on an organized crime gang that used the ZeuS malware to steal tens of millions of dollars from companies and consumers. In that case, Konovalenko ultimately unmasked himself because he used his Internet connection to order the delivery of a “Veggie Roma” pizza to his apartment in the United Kingdom.
Interestingly, the feds say their examination of Bukoski’s Internet browsing records showed he knew full well that running a booter service was punishable under federal law (despite disclaimers published on Quantum Stresser stating that the site’s owners weren’t responsible for how clients used the service).
“The defendant’s web browsing history was significant to investigators for a number of reasons, including the fact that it shows that the defendant browsed an article written by a prominent security researcher referencing both the defendant’s enterprise along with a competing service, including a link provided by the researcher in the article to an advisory posted by the FBI warning that the operation of booter services was potentially punishable under federal law,” reads the sentencing memo from Assistant U.S. Attorney Adam Alexander.
That’s interesting because the article in question was actually a 2017 KrebsOnSecurity story about a mobile app tied to a competing booter service that happened to share some of the same content as Quantum Stresser.
That 2017 story referenced an FBI advisory that had just been issued warning the use of booter services is punishable under the Computer Fraud and Abuse Act, and may result in arrest and criminal prosecution.
Bukoski was sentenced to five years of probation and six months of “community confinement.” The government suggested a lenient sentence considering the defendant’s ongoing health complications, which include liver failure.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
A California man could face up to 25 years in prison after pleading guilty to downloading child pornography and habitually hacking into the computer system of Japanese gaming giant Nintendo.
Ryan Hernandez was still a minor when, together with an associate, he used a phishing technique to steal the credentials of a Nintendo employee in 2016. The data stolen by the Palmdale resident, who is now 21, was used to gain access to and download confidential Nintendo files related to the company’s consoles and games.
That stolen data, which included pre-release information about the anticipated Nintendo Switch console, was leaked to the public, sparking an investigation by the Federal Bureau of Investigation.
The FBI tracked Hernandez down to his parents’ house in October 2017 and let him off with a warning, but it wasn’t too long before the youngster threw away the second chance he was generously offered. Within nine months Hernandez was back to his old tricks, illegally accessing Nintendo servers and stealing confidential information.
Hernandez leaked the stolen information to others online via a chat forum he had christened “Ryan’s Underground Hangout.” There, the egotistical hacker discussed Nintendo products, shared confidential information he had stolen from people with actual talent, and highlighted possible Nintendo network vulnerabilities.
Far from displaying any guilt over his illicit activities, Hernandez brazenly boasted about his cyber-exploits on social media platforms, including Twitter and Discord.
Hernandez’s malicious hacking spree was curtailed in June 2019 when FBI agents seized from his home the computers, hard drives, and circumvention devices he used to access pirated video games and software.
A search of the devices revealed thousands of confidential Nintendo files and a sickening insight into Hernandez’s disturbing sexual predilections.
The US Department of Justice stated: “Forensic analysis of his devices also revealed that Hernandez had used the internet to collect more than one thousand videos and images of minors engaged in sexually explicit conduct, stored and sorted in a folder directory he labeled ‘Bad Stuff.'”
In a US District Court in Seattle, Washington, on Friday, Hernandez pleaded guilty to computer fraud and abuse and to possession of child pornography. Hernandez, who will now be required to register as a sex offender, agreed to pay $259,323 in restitution to Nintendo.
Hernandez will be sentenced on April 21.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
A major Australian freight company is experiencing operational difficulties after a cybersecurity incident caused an IT system shutdown.
Toll Group announced that it had experienced a “cybersecurity incident” on Friday. The company shut down a number of IT systems at multiple sites across the country in a bid to resolve the issue.
“As a precautionary measure, in response to a cyber security incident on Friday, Toll deliberately shut down a number of systems across multiple sites and business units,” said Toll Group in a statement.
“Toll IT teams are working closely with global cyber security experts to resolve the issue.”
Customers have reported issues with tracking shipments, reporting that IT systems were down at Toll depots. Until the incident is resolved, Toll Group is recording receipts manually.
The MyToll website, where customers can usually track deliveries and book package collections, has been taken offline and is currently displaying a cybersecurity warning message.
The company said its first priority was to bring its customer-facing applications back online.
“Toll is making progress with our recovery activities to restore our systems and Toll customer-facing applications,” stated the company.
“Our immediate focus is on bringing our systems back online in a controlled and secure manner. Business continuity plans have been activated to maintain customer service and operations.”
No information has been released by Toll Group so far regarding the nature or severity of the cyber-incident. The details of how it occurred are currently also being kept under wraps.
Toll Group is often contracted to handle Australia’s eBay deliveries. The freight company is also the carrier of choice for many of the country’s cell phone companies when sending out new handsets and SIM cards.
Business Insider reported that Toll operations in Australia, India, and the Philippines had been affected by the incident.
No timeline has been given for when Toll Group’s IT systems will be back up and running.
Toll Group operates a global express, freight forwarding, and logistics service from its base in Melbourne. The company, which was founded in 1888, was acquired by Japan Post in 2015.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
A British community housing charity was conned out of more than $1m in a domain spoofing and contractor impersonation scam.
Red Kite Community Housing announced on Tuesday that it had fallen victim to a cyber-scam in which criminals posed as genuine service providers to steal a staggering £932,000.
In a statement issued on January 28, Red Kite described the heavy financial loss as “absolutely galling.”
The charity described how criminals not only spoofed the domain of a genuine contractor but also sent emails to Red Kite that appeared to be from contacts who had already won the charity’s trust.
Detailing how the criminals got the better of the charity, Red Kite wrote: “What they managed to do was to expose a weakness using sophistication and human nature to carry out the theft of this money.
“In essence, they mimicked the domain and email details of known contacts that were providing services to Red Kite. Through this they managed to recreate an email thread that misled those who were copied into the email that it was a genuine follow up to an existing conversation.”
Unfortunately, a payment verification process put in place to prevent fraudulent transactions proved ineffective when the error it flagged was not actioned.
Red Kite wrote: “We still had an additional safety net in place; a two-stage process to verify changes to payments and accounts which ordinarily would have caught this attempt.
“This, however, proved to be our weak point, with an error being made by the clear process not been actioned, resulting in a missed opportunity to shut the door before the money was taken. This is the part that upsets everyone involved.”
The con was carried out in late August 2019 and is still under investigation by the police. As a result of the incident, Red Kite’s governance rating has been downgraded by the Regulator of Social Housing (RSH).
In a regulatory judgement made public last week, the RSH wrote that Red Kite experienced “a significant financial loss as a result of a fraud due to a basic failure in its system of internal controls”—and urged them to make improvements.
Red Kite, which is based in the southeastern county of Buckinghamshire, owns and manages around 6,500 homes across the town of High Wycombe.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
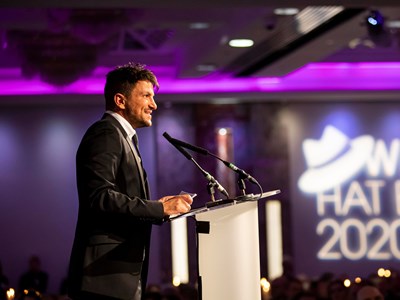
An incredible £187,000 was raised for the NSPCC counselling service Childline at the White Hat Ball on Friday January 31 2020.
Over 650 guests attended the event, which was hosted by singer and TV personality Peter Andre, at the Royal Lancaster Hotel in London.
Guests, including members of the Infosecurity Magazine team, enjoyed a champagne reception and a three-course dinner, followed by entertainment including silent and live auctions where fantastic prizes were won such as an exclusive VIP Manchester United experience and painting ‘Bowie’ by Daniel Mernaugh.
Organized by a committee of dedicated volunteers from the information risk and security sector, the event is now in its 15th year.
Speaking at the event, Peter Andre said: “I’ve been supporting Childline for many, many years so I was honored to be asked to host the White Hat Ball and raise lots of money for a cause close to my heart. I love everything Dame Esther Rantzen stands for. Every child is worth fighting for, and I’m proud to have been a part of this evening to support that.”
The money raised from the Ball will help Childline continue to be there 24/7 for young people in need of support for a range of issues, including mental health and concerns about abuse and neglect. On average, a child contacts Childline every 25 seconds, with almost three-quarters of counselling sessions now taking place online.
Sarah Jeffery, NSPCC special events manager, said: “It was fantastic to see so many people gather at the White Hat Ball, raising vital funds for Childline.
“We know that Childline provides a vital lifeline for young people across the country and events like the White Hat Ball enable us to continue to provide this life-changing service.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
The FBI has arrested a US defense contractor employee for allegedly taking classified information with him on a secret China trip.
Tucson-resident Wei Sun, 48, worked for Raytheon for over 10 years as an electrical engineer on the firm’s missile systems program. As such, the China-born US resident had access to technical data on highly regulated military technology which requires an export license to take out of the country.
However, he allegedly transported some of this data “knowingly and wilfully” on his work laptop on a December 2018 trip, despite being told by a manager that this would contravene company policy and federal law.
Whilst out of the country, he emailed Raytheon from his laptop and work account to resign, claiming he wanted to study and work overseas.
On returning, he admitted to security staff at the firm that he had taken information on Raytheon’s ballistic missile defense system abroad on his work laptop, but only to Singapore and the Philippines.
However, Sun’s story subsequently changed, as he admitted to travelling to China, Cambodia and Hong Kong — again with no attempt made to obtain an export license under the International Traffic in Arms Regulations (ITAR).
Sun was kicked out of the company after these interviews in January 2019 and arrested a year later for breaking the ITAR.
Reports suggest he was familiar with cutting-edge weapons systems of high strategic value to China, such as defense technology used to shoot down incoming missiles.
The US is clamping down on intelligence leaks of all types. Last week it emerged that a prominent Harvard academic had been arrested and charged with lying about his ties to China.
His case was published alongside news that a PLA officer and a second Chinese national were arrested after posing as students to steal sensitive research information.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Cyber-criminals behind the Maze ransomware attacks have claimed several more scalps over the past few days, including five law firms and a French industrial giant, all of which are thought to have had sensitive internal data stolen.
Brett Callow, a threat analyst with security vendor Emisoft, alerted Infosecurity to the developments over the weekend. The Maze group has a dedicated website where it first names victim organizations and then releases stolen data if they refuse to pay the ransom.
“This makes sense. The more data they publish and the more sensitive that data is, the less incentive an organization has to pay to prevent the remaining data being published,” said Callow.
“It’s the equivalent of a kidnapper sending a pinky finger. If the organization still doesn’t pay, the remaining data is published, sometimes on a staggered basis.”
That’s potentially bad news for the latest firms to fall victim to Maze ransomware. At present, only two of the law firms have had sensitive customer data published but, ominously for the other victims, the group promises that the “proofs” are coming soon.
The French firm struck by Maze, Bouygues Construction, published a brief statement on Friday admitting a “ransomware-type virus” had been detected on its network the day before.
However, there’s no word from the firm so far on whether key data has also been lifted, as alleged by the Maze hackers.
“As a precautionary measure, information systems have been shut down to prevent any propagation,” the statement read.
“Our teams are currently fully focused on returning to normal as quickly as possible, with the support of experts. Installations are progressively being put back into service after being tested. Operational activity on our construction sites has not been disrupted to date.”
Maze has hit a wide range of firms in the past, including the US City of Pensacola, cabling giant Southwire and security company Allied Universal.
It’s not unusual for the group to charge its victims twice, $1m for the decryption key and a further $1m for ‘deletion’ of the stolen data. There’s the added jeopardy that, if they’re not paid, stolen data will be leaked onto Russian hacker forums, as has happened in the past.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
UK law enforcers have tightened the net around the hackers that stole €13m ($14.4m) from one of Malta’s biggest banks, with the arrest of four men last week.
Malware planted on the Bank of Valletta’s servers back in February 2019 enabled hackers to transfer the money to accounts in the UK, US, Hong Kong and Czech Republic. The lender was forced to shut down all its operations after spotting the illegal activity and attempting to prevent the fund transfers.
However, £800,000 ($1m) was funnelled to an account in Belfast, with payments totalling £340,000 ($446,000) then disappearing from the account before it could be blocked.
According to the UK’s National Crime Agency (NCA), some of the money was spent at luxury stores including Harrods and Selfridges, to buy Rolex watches, and to purchase a Jaguar and an Audi A5.
Following the trail of money, NCA officers arrested three men on Friday on suspicion of money laundering, fraud and theft. These included a 33-year-old detained at Heathrow Airport as he returned to the UK from China, and two men aged 23 and 24 who handed themselves into a police station in Belfast.
These were preceded by the arrest of another Belfast man, aged 39, a day earlier, on suspicion on the same crimes, and the apprehension of two men aged 22 and 17 in London on January 22 after raids on properties in West Hampstead and Ladbroke Grove.
The arrests represent the latest stage in a 12-month investigation by the NCA and Malta Police Force Economic Crime Unit.
“The focus of our investigation is those suspected of having helped launder the proceeds of this cyber-attack, a large amount of which were funnelled through a bank account here in Belfast,” said NCA Belfast branch commander David Cunningham.
“It demonstrates how this type of criminality is often international in nature, and how tackling it is a priority for the National Crime Agency and partners, both within the UK and around the world.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk