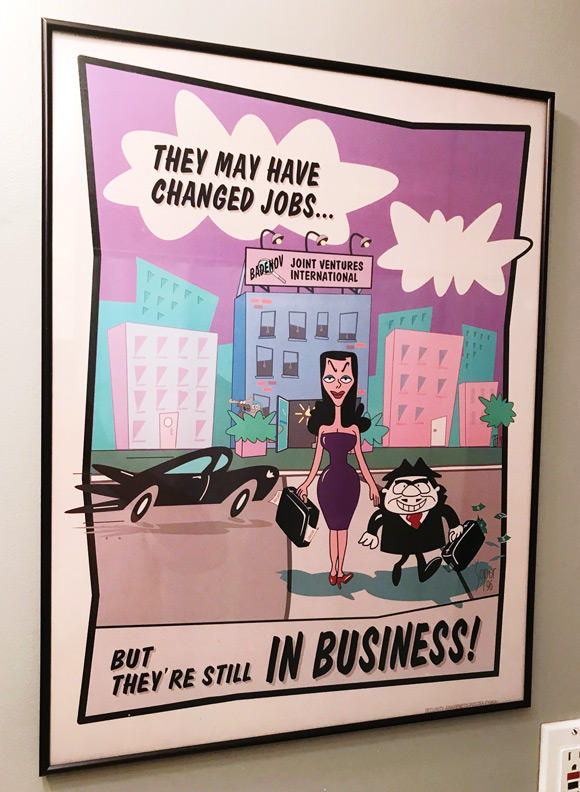
I have a related personal story. Back in 1993, during the first Crypto Wars, I and a handful of other academic cryptographers visited the NSA for some meeting or another. These sorts of security awareness posters were everywhere, but there was one I especially liked — and I asked for a copy. I have no idea who, but someone at the NSA mailed it to me. It’s currently framed and on my wall.
I’ll bet that the NSA didn’t get permission from Jay Ward Productions.
The Department of Interior is grounding all non-emergency drones due to security concerns:
The order comes amid a spate of warnings and bans at multiple government agencies, including the Department of Defense, about possible vulnerabilities in Chinese-made drone systems that could be allowing Beijing to conduct espionage. The Army banned the use of Chinese-made DJI drones three years ago following warnings from the Navy about “highly vulnerable” drone systems.
One memo drafted by the Navy & Marine Corps Small Tactical Unmanned Aircraft Systems Program Manager has warned “images, video and flight records could be uploaded to unsecured servers in other countries via live streaming.” The Navy has also warned adversaries may view video and metadata from drone systems even though the air vehicle is encrypted. The Department of Homeland Security previously warned the private sector their data may be pilfered off if they use commercial drone systems made in China.
I’m actually not that worried about this risk. Data moving across the Internet is obvious — it’s too easy for a country that tries this to get caught. I am much more worried about remote kill switches in the equipment.
On Sept. 11, 2019, two security experts at a company that had been hired by the state of Iowa to test the physical and network security of its judicial system were arrested while probing the security of an Iowa county courthouse, jailed in orange jumpsuits, charged with burglary, and held on $100,000 bail. On Thursday Jan. 30, prosecutors in Iowa announced they had dropped the criminal charges. The news came while KrebsOnSecurity was conducting a video interview with the two accused (featured below).
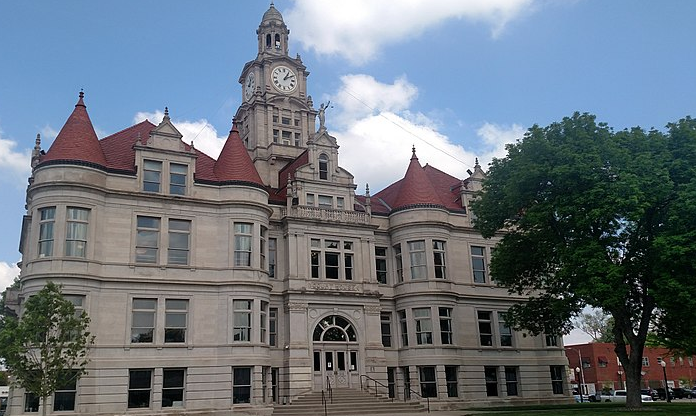
The courthouse in Dallas County, Iowa. Image: Wikipedia.
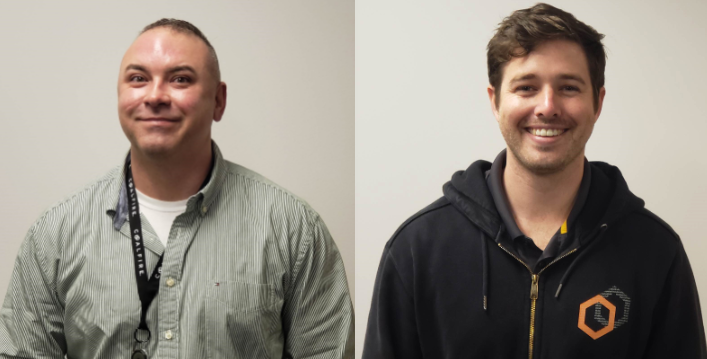
Gary DeMercurio, 43 of Seattle, and Justin Wynn, 29 of Naples, Fla., are both professional penetration testers employed by Coalfire Labs, a security firm based in Westminster, Colo. Iowa’s State Court Administration had hired the company to test the security of its judicial buildings.
Under the terms of their contract (PDF), DeMercurio and Wynn were permitted to impersonate staff and contractors, provide false pretenses to gain physical access to facilities, “tailgate” employees into buildings, and access restricted areas of those facilities. The contract said the men could not attempt to subvert alarm systems, force-open doors, or access areas that require protective equipment.
When the duo’s early-morning Sept. 11 test of the security at the courthouse in Dallas County, Iowa set off an audible security alarm, they followed procedure and waited on-site for the police. DeMercurio and Wynn said when the county’s sheriff deputies arrived on the scene just a few minutes later, they told the officers who they were and why they were there, and that they’d obtained entry to the premises via an unlocked door.
“They said they found a courthouse door unlocked, so they closed it from the outside and let it lock,” Dan Goodin of Ars Technica wrote of the ordeal in November. “Then they slipped a plastic cutting board through a crack in the door and manipulated its locking mechanism. (Pentesters frequently use makeshift or self-created tools in their craft to flip latches, trigger motion-detected mechanisms, and test other security systems.) The deputies seemed impressed.”
To assuage concerns they might be burglars, DeMercurio and Wynn produced an authorization letter detailing the job they’d been hired to do and listing the names and mobile phone numbers of Iowa state employees who could verify their story.
After contacting some of the court officials listed in the letter, the deputies seemed satisfied that the men weren’t thieves. That is, until Dallas County Sheriff Chad Leonard showed up.
“The pentesters had already said they used a tool to open the front door,” Goodin recounted. “Leonard took that to mean the men had violated the restriction against forcing doors open. Leonard also said the men attempted to turn off the alarm—something Coalfire officials vehemently deny. In Leonard’s mind that was a second violation. Another reason for doubt: one of the people listed as a contact on the get-out-of-jail-free letter didn’t answer the deputies’ calls, while another said he didn’t believe the men had permission to conduct physical intrusions.”
DeMercurio and Wynn were arrested, jailed, and held for nearly 24 hours before being released on a $100,000 bail. Initially they were charged with felony third-degree burglary and possessing burglary tools, although those charges were later downgraded to misdemeanor trespass.
What initially seemed to Coalfire as a momentary lapse of judgment by Iowa authorities quickly morphed into the surreal when state lawmakers held hearings questioning why and how someone in the state’s employ could have so recklessly endangered the safety and security of its citizens.
DeMercurio and Wynn, minus the orange jumpsuits.
Judicial Branch officials in Dallas County said in response to this grilling that they didn’t expect Coalfire’s physical penetration testing to be conducted outside of business hours. State Sen. Amy Sinclair was quoted as telling her colleagues that “the hiring of an outside company to break into the courthouses in September created ‘significant danger, not only to the contractors, but to local law enforcement, and members of the public.’”
“Essentially a branch of government has contracted with a company to commit crimes, and that’s very troubling,” lamented Iowa state Sen. Zach Whiting. “I want to find out who needs to be held accountable for this and how we can do that.”
Those strong words clashed with a joint statement released Thursday by Coalfire and Dallas County Attorney Charles Sinnard:
“Ultimately, the long-term interests of justice and protection of the public are not best served by continued prosecution of the trespass charges,” the statement reads. “Those interests are best served by all the parties working together to ensure that there is clear communication on the actions to be taken to secure the sensitive information maintained by the judicial branch, without endangering the life or property of the citizens of Iowa, law enforcement or the persons carrying out the testing.
Matthew Linholm, an attorney representing DeMercurio and Wynn in the case, said the justice system ceases to serve its crucial function and loses credibility when criminal accusations are used to advance personal or political agendas.
“Such a practice endangers the effective administration of justice and our confidence in the criminal justice system,” Linholm told The Des Moines Register, which broke the news of the dropped charges.
While the case against Coalfire’s employees has rallied many in the cybersecurity community around the accused, not everyone sees this dispute in black-and-white. Chris Nickerson, a digital intrusion specialist and founder of LARES Consulting, said in a Twitter post Thursday that “when a company puts us in harm’s way due to their poor planning, failed sales education, inadequate project management and deplorable contract management…We shouldn’t celebrate them. We should hold them accountable.”
Asked to elaborate, Nickerson referred to a recent podcast which touched on the arrests.
“The things that concern me about this situation are more of the pieces of safety that exist across how the industry instruments doing these types of engagements,” Nickerson said. “They seem very, very reasonable and obvious once they become obvious but until then they’re completely foreign to people.”
“It’s really on the owners of the organization to educate the customer of those potential pitfalls,” Nickerson continued. “Because there isn’t a good standard. We haven’t all gotten together and institutionalized the knowledge that we have in our heads and dump it down to paper so that someone who is new to the field being tasked with this can go through and say, ‘Hey, did you ask them if the city versus the state versus the building owner and the real estate people…are all of these people in lock step?’”
CoalfireCEO Tom McAndrew seemed to address this point in our interview Thursday, saying there were two unique aspects of this particular engagement. First, although the client in this case said they did not want Coalfire to make local law enforcement aware of the ongoing engagement prior to testing the physical security of the site, it was clear after the fact that state officials never did that on their own.
More importantly, McAndrew said, there was ambiguity around who actually owned the buildings that they were hired to test.
“If you’re doing a test for the state and you walk into the building and it’s the courthouse and you’re doing a test for the court system, you’d think that they would have jurisdiction or own it, and that turned out not to be the case in this scenario because there’s some things the state owns and some things the county owns, and that was something we weren’t aware of as we did some of this work,” he said. “We didn’t understand the nuances.”
Asked what Coalfire has learned from this ordeal, McAndrew said his company is likely to insist that local, state and even federal law enforcement be informed in advance of any penetration tests, at least as far as those engagements relate to public entities.
“When we look at the contracts and we look at who’s authorized to do what…typically, if a [chief security officer] says test these IP addresses, we would say okay that’s enough,” he said. “But we’re questioning from a legal perspective at what point does that need to have legal counsel review.”
McAndrew said it’s probably time for experts from various corners of the pen testing community to collaborate in documenting best practices that might help others avoid a repeat of the scenario in Dallas County.
“There’s no standard in the industry,” he said. “When it comes to these sorts of issues in red teaming — the legal challenges and the contracts — there’s really nothing out there. There are some things that can’t be undone. There’s the mugshots that are out there forever, but even as we get the charges dropped, these are permanently going to be in the federal database. This is a permanent thing that will reside with them and there’s no legal way we’re aware of to get these charges removed from the federal database.”
McAndrew said while he remains frustrated that it took so long to resolve this dispute, he doesn’t believe anyone involved acted with malicious intent.
“I don’t think there were any bad people,” he said. “Everyone was trying to do the right things — from law enforcement to the sheriff to the judges to the county — they all had the right intentions. But they didn’t necessarily all have the right information, and possibly people made decisions at levels they weren’t really authorized to do. Normally that’s not really our call, but I think people need to be thinking about that.”
Fake Exec Tricks New York City Medical Center into Sharing Patient Info
An employee at a New York City medical center was tricked into giving out patient information by a threat actor purporting to be one of the facility’s executives.
The data was shared by an individual at community-based non-profit the VillageCare Rehabilitation and Nursing Center (VCRN) who had received what they believed to be a genuine email from a senior member of staff.
VCRN were notified on or about Monday, December 30, that a cruel deception had taken place.
In a Notice of Data Privacy Incident statement published on VCRN’s website, the company stated: “The unauthorized actor requested certain information related to VCRN patients. Believing the request to be legitimate, the employee provided the information.”
Information obtained by the threat actor included first and last names, dates of birth, and medical insurance information, including provider name and ID number for 674 patients.
VCRN said: “Once it became apparent that the email received by the employee was not a legitimate request, we immediately launched an investigation with the assistance of third-party forensic specialists to determine the full scope of this event.”
The medical center said that they weren’t aware of any personal patient information having been misused as a result of this event.
Becoming a victim of a phishing scam has led VCRN to review its cybersecurity practices.
The center said: “We take this incident and security of personal information in our care seriously. We moved quickly to investigate and respond to this incident, assess the security of relevant VCRN systems, and notify potentially affected individuals. This response included reviewing and enhancing our existing policies and procedures.”
VCRN has taken steps to notify all the patients who have potentially been impacted by the cyber-attack. A toll-free dedicated assistance phone line has been established for patients who wish to discuss any concerns they may have as a result of the incident.
The data breach has been reported to law enforcement and to the relevant regulatory authorities.
VCRN advised patients “to remain vigilant against incidents of identity theft and fraud and to review account statements, credit reports, and explanation of benefits forms for suspicious activity and report any suspicious activity immediately to your insurance company, health care provider, or financial institution.”
Cybersecurity Firm to Create 164 New Jobs in Virginia
Cybersecurity firm Expel Inc. has announced a $1.4m investment to expand its operations in Fairfax County, Virginia.
The huge injection of cash will be used to increase the size of the company’s Herndon headquarters and to create 164 new jobs in the company’s engineering, customer experience, IT, marketing, and sales departments over the next three years.
News of the planned expansion was announced by the governor of Virginia, Ralph Northam, on Tuesday.
“Virginia has emerged as a national leader in cybersecurity and continues to be at the forefront of workforce development in this rapidly-evolving industry, thanks to companies like Expel, Inc.,” said Northam.
“We are thrilled to support this homegrown Northern Virginia business as they grow and expand and look forward to their ongoing success in Herndon.”
Victor Hoskins, president and CEO of the Fairfax County Economic Development Authority (FCEDA), voiced his support for the scheme.
“The security-focused industry cluster and the talent pool around it make Fairfax County and Northern Virginia a great location for Expel, and I am delighted that my office has had the opportunity to help the company expand its footprint in the Town of Herndon.
“We appreciate the company’s vote of confidence in Herndon and Fairfax County and look forward to its continued growth here.”
The FCEDA and the Town of Herndon worked with the Virginia Economic Development Partnership to secure the project for Virginia and will support the company’s job creation through the Virginia Jobs Investment Program (VJIP).
Expel’s co-founder and CEO Dave Merkel described Fairfax County as a prime location in which to grow the business.
“There’s a fantastic pool of tech talent located in Northern Virginia, and we have close proximity to strong education institutions and major tech companies,” said Merkel.
Expel offers round-the-clock cybersecurity monitoring, providing transparent managed security both on-premises and in the cloud. The company was founded by Dave Merkel, Yanek Korff, and Justin Bajko in a barn in Virginia in 2015.
The company currently has 171 employees and 14 strategic partners, including Amazon Web Services, Microsoft Azure, CISCO, Crowdstrike, Palo Alto, and Carbon Black.
New research released yesterday by the Ponemon Institute reveals a dramatic increase in both the frequency of insider threats and their financial cost to businesses since 2018.
The report, “2020 Cost of Insider Threats: Global,” shows that the average global cost of insider threats rose by 31% in two years to $11.45m, and the frequency of incidents spiked by 47% in the same time period.
To gather data for the study, researchers talked to 964 IT and security practitioners at 204 organizations in North America, Europe, the Middle East, Africa, and Asia-Pacific. All the individuals who contributed worked at a company with a global headcount of 1,000 or more.
Researchers learned that across all organizations in the past 12 months a total of 4,716 incidents had occurred that had been caused by an insider threat.
For a more detailed analysis, researchers split the incidents into three different categories of threat: those caused unintentionally by negligent employees or contractors, those perpetrated by credential thieves bent on using insiders’ login information to gain unauthorized access to applications and systems, and those instigated by criminal and malicious insiders out to damage an organization from within.
Of the three profiles, credential thieves caused the most damage per incident, costing organizations an average of $871,000 per incident—three times more per incident than a negligent insider. However, the frequency of credential theft was 25% of all incidents, which limited the average annual cost to $2.79m per year.
Negligent employees or contractors, who were found to have caused 62% of insider threats, created the highest financial burden of the profiles, costing an average of $4.58m per year.
Malicious criminal insider threats were found to have occurred with the least frequency, making up just 14% of incidents. The financial ramifications of this rarer threat type were still significant, with researchers recording a per-incident cost of $756K and annual losses of $4.08m.
Proving the old adage “a stitch in time saves nine,” researchers found that the longer an insider threat lingers the costlier it is to rectify. Incidents that took more than 90 days to contain cost organizations $13.71m on an annualized basis, while incidents that lasted less than 30 days cost roughly half, at $7.12m.
US Arrests Prominent Harvard Academic for China Ties
A US crackdown on perceived efforts by China to unfairly acquire US talent and R&D has stepped up a notch, with charges filed against a senior Harvard academic.
Charles Lieber, the chair of Harvard University’s department of chemistry and chemical biology, was arrested on Tuesday on one count of “making a materially false, fictitious and fraudulent statement.”
As principal investigator of the Lieber Research Group at Harvard, he has received $15m in government grants to research cutting-edge nanoscience techniques. However, such funding requires disclosure of any major foreign financial conflicts of interest.
It is alleged that, since 2011, Lieber has been a “strategic scientist” at Wuhan University of Technology (WUT), and that from 2012-17 he was a “contractual participant” in Beijing’s Thousand Talents Plan, which Washington claims is designed to recruit foreign science experts to steal research secrets.
He’s said to have made millions from these endeavors but allegedly lied about his involvement in both schemes. Lieber could be facing five years behind bars for making false statements to investigators.
Notably, Lieber’s case was published by the Department of Justice (DoJ) alongside that of two alleged Chinese spies who enrolled as students at US universities to steal research material.
Yanqing Ye is in fact a PLA lieutenant who studied at Boston University’s (BU) Department of Physics, Chemistry and Biomedical Engineering from October 2017 to April 2019, allegedly stealing info for military research projects and profiling US scientists for her bosses.
Zaosong Zheng conducted cancer-cell research at Beth Israel Deaconess Medical Center in Boston from September 2018 to December 2019, but was arrested trying to smuggle 21 vials of biological research out of the country on a flight to China. It’s claimed he wanted to publish the research results under his own name.
Visa fraud carries a charge of 10 years behind bars, as does acting as a foreign agent, and smuggling goods from the US.
The US Department of the Interior (DOI) has temporarily grounded its fleet of unmanned aircraft systems (UAS) while it checks whether equipment which is manufactured by foreign companies or contains parts made abroad represents a national security risk.
Drones are used by the DOI to protect national treasures and critical resources, in tasks such as: “emergency management; fighting wildland fires; conducting search and rescue; surveying Federal land; collecting research data; and assisting law enforcement, among others.”
“The [DOI] has been a leader in deploying UAS to better achieve its goals. These efforts include assessing, collecting, and maintaining information that relates to our critical American energy, transportation and defense infrastructure,” the DOI secretary David Bernhard said.
“In certain circumstances, information collected during UAS missions has the potential to be valuable to foreign entities, organizations and governments.”
While the drones remain grounded for all but emergency operations, the department will establish procedures for identifying which are made by foreign-owned companies or contain foreign-manufactured parts. DOI chiefs are being instructed to limit funds spent on such drones.
The temporary grounding measure was first flagged back in October 2019, so the latest order, rumored earlier this month, indicates persistent national security concerns in Washington. The overall effect appears to be rooting out and sidelining foreign kit in favor of US-made products.
“With this order, the department is taking action to ensure that our minimum procurement needs account for such concerns, which include cybersecurity, technological considerations and facilitating domestic production capability,” the order continued.
China is not mentioned by name in the order, but would be an obvious target here.
One of its biggest drone makers, DJI, contributes a small number of machines to the 800-strong DOI fleet.
“DJI makes some of the industry’s most safe, secure, and trusted drone platforms for commercial operators. The security of our products designed specifically for the DOI and other US government agencies have been independently tested and validated by US cybersecurity consultants, US federal agencies including the Department of Interior and the Department of Homeland Security, which proves today’s decision has nothing to do with security,” it said in a statement.
“We are opposed to the politically-motivated country of origin restrictions masquerading as cybersecurity concerns and call for policymakers and industry stakeholders to create clear standards that will give commercial and government drone operators the assurance they need to confidently evaluate drone technology on the merits of performance, security and reliability, no matter where it is made.”
Hackers compromised dozens of United Nations (UN) servers last summer in an attack which the world body kept a secret from its own employees, according to a new report.
The attack began in mid-July 2019 in what one senior UN IT official called a “major meltdown,” affecting servers in UN offices in Vienna and Geneva and the UN Office of the High Commissioner for Human Rights (OHCHR) headquarters in Geneva.
Some 400GB is thought to have been exfiltrated by the hackers, including Active Directory lists of users. Although it’s unclear exactly what other info was taken, the servers in question could have provided access to sensitive details on UN employees, and commercial contract data, according to The New Humanitarian.
The OHCHR in particular handles highly sensitive data on human rights activists which could land subjects in deep trouble with governments back home.
According to an internal report on the incident seen by AP, the hackers exploited a Microsoft SharePoint vulnerability to access the UN network although the type of malware is unknown, as is the location of the C&C servers used to exfiltrate the data. It’s also unclear how the attackers maintained presence on the network once inside.
Most controversially, the UN seems to have used its diplomatic immunity to keep the incident a secret, despite it raising serious questions under the GDPR.
Staff were told only to reset their passwords, but not why, it is claimed.
“As the exact nature and scope of the incident could not be determined, [the UN offices] decided not to publicly disclose the breach,” said UN spokesperson Stéphane Dujarric.
The level of sophistication used and motivation for striking at the heart of the UN’s human rights efforts indicates a nation state actor, according to experts.
Traditional cybersecurity measures may not be successful against nation state hackers, meaning firms must focus on detection and response, according to Exabeam senior security engineer, Joe Lareau.
“One critical step all of these entities can take now is to monitor for tactics, techniques and procedures (TTPs) specific to various state-sponsored groups,” he added.
“Overall, we recommend building and using ‘defense in depth’ — multiple layers of controls that involve staffing, procedures, technical and physical security for all aspects of the security program.”