Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Author: admin
U.N. Hack Stemmed From Microsoft SharePoint Flaw
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Dell, HP Memory-Access Bugs Open Attacker Path to Kernel Privileges
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Collating Hacked Data Sets
Two Harvard undergraduates completed a project where they went out on the dark web and found a bunch of stolen datasets. Then they correlated all the information, and combined it with additional, publicly available, information. No surprise: the result was much more detailed and personal.
“What we were able to do is alarming because we can now find vulnerabilities in people’s online presence very quickly,” Metropolitansky said. “For instance, if I can aggregate all the leaked credentials associated with you in one place, then I can see the passwords and usernames that you use over and over again.”
Of the 96,000 passwords contained in the dataset the students used, only 26,000 were unique.
“We also showed that a cyber criminal doesn’t have to have a specific victim in mind. They can now search for victims who meet a certain set of criteria,” Metropolitansky said.
For example, in less than 10 seconds she produced a dataset with more than 1,000 people who have high net worth, are married, have children, and also have a username or password on a cheating website. Another query pulled up a list of senior-level politicians, revealing the credit scores, phone numbers, and addresses of three U.S. senators, three U.S. representatives, the mayor of Washington, D.C., and a Cabinet member.
“Hopefully, this serves as a wake-up call that leaks are much more dangerous than we think they are,” Metropolitansky said. “We’re two college students. If someone really wanted to do some damage, I’m sure they could use these same techniques to do something horrible.”
That’s about right.
And you can be sure that the world’s major intelligence organizations have already done all of this.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
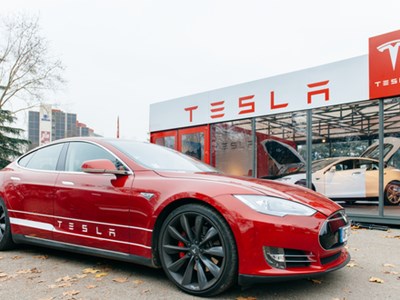
Hacker Leaks Alleged Tesla Design Secrets

A hacker has taken to Twitter to share design secrets they allegedly obtained by compromising American automotive and energy company Tesla.
Posting on the account @greentheonly on Friday night, a hacker who calls themself “Green” said that Tesla was planning to introduce new hardware to their S and X model cars.
Modifications that Green claims are in the cards include the introduction of new battery options and a suspension redesign.
According to Green, Tesla has added a wireless device charger to its two oldest car models. The charger is allegedly integrated into the center console. Green also claims to have uncovered plans for a new type of charging port.
Another interior change that the hacker says is coming to the S and X models is something Green describes as “new lumbar,” which could possibly mean a redesign of the front seats.
Aside from the cosmetic changes, Green claims that Tesla plans to introduce two new battery types into both models, which the hacker claims will be available in several configurations. Other information allegedly hacked from Tesla by Green revealed that the company plans to introduce a new suspension option.
Tesla hasn’t confirmed or denied the hacker’s findings. The company, which is based in Palo Alto, California, has not announced any plans to update the Model S or the Model X.
Following Green’s Twitter post, Tesla has however “quietly added a wireless phone charger to the list of standard features posted on its website,” according to Autoblog.com.
Tesla traditionally waits until the last minute to load information regarding new features into its computer system in a bid to avoid data leaks from occurring. Both Green and Autoblog speculate that an announcement of the new features for the X and S could possibly be around the corner.
Green wrote on Twitter: “Tesla seemed to have realized no matter what they do stuff leaks through firmware so froze releases on week 40 and just backported absolute necessary stuff to limit leakage. And now past the new year this must be hw [hardware] they put into cars now/vsoon so cannot avoid it.”
Tesla started building the Model S in 2012. Three years later, the company launched the Model X. Unique and cutting-edge in their time, both cars now compete in an expanding electric luxury car market that includes Porsche’s Taycan, the Audi E-Tron, and the Jaguar I-Pace.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Japan Considers Emergency Cybersecurity Measures Ahead of 2020 Olympics

A panel of experts from Japan’s Ministry of Internal Affairs and Communications proposed a set of emergency cybersecurity measures on Monday ahead of this year’s Olympic and Paralympic Games.
The measures were shared amid fears that Japan will experience a surge in cyber-attacks while hosting the world-famous sporting event this summer.
After making a series of recommendations, the panel called for the government to draw up plans to introduce cybersecurity training at a local government level. The panel pointed out that while almost all central government bodies in Japan have received cybersecurity training, nearly half of all local governments have not been taught how to respond to a cyber-attack.
The panel called for the government to quickly determine whether adequate security measures were in place for devices installed in the country’s transportation infrastructure and other important public facilities that may be vulnerable to cyber-attack because of their use of Internet of Things (IoT) technologies.
Any cybersecurity issues that arise following an examination of the security of these devices should be flagged and reported to administrators, who should then address the problem, advised the panel. The panel proposed that thorough cybersecurity checks be conducted on devices whose manufacturer-issued passwords have never been changed.
A further measure suggested by the panel was for any cyber-attacks that occur in Japan to be reported in a timely manner. They also called for organizations to practice information sharing.
In their emergency proposal, the experts wrote that “it is desirable to consider publishing information on cyber-attacks swiftly at the point in which leaks of personal information are suspected.”
After highlighting the risk of data leaks from using Wi-Fi services, the panel called for the government to warn businesses and individuals against sharing any personal or confidential information when using Wi-Fi.
Japan has had seven years in which to prepare for the arrival of the 2020 Summer Olympics, officially known as the Games of the XXXII Olympiad, after being selected to host the world-famous sporting event on September 7, 2013.
The event, also known as the Tokyo Olympic Games, will take place between July 24 and August 9, 2020, in the nation’s capital city. Tokyo will then host the Tokyo Paralympic Games from August 25 through September 6.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Cyber-Attack on US Water Company Causes Network Outage

A South Carolina water company is recovering from a cyber-attack that took its phone and online payment systems offline for nearly a week.
The cyber-attack on Greenville Water triggered a payment system outage that began on Wednesday, January 22. Company spokesperson Emerald Clark said 500,000 customers were affected by the incident.
An investigation has been launched into the cyber-attack, the exact nature of which is yet to be revealed by Greenville Water. It’s not yet known who targeted the water company or from where the attack was launched.
Greenville Water CEO David Bereskin said he was “fairly certain” that the utility’s data had not been compromised as a result of the incident.
“We have been preparing for potential attacks for years and put specific protections in place to ensure the safety of our data and the integrity of our water,” said Bereskin.
According to Clark, the cybersecurity incident has had little effect on data security. She said: “We have no reason to believe that any confidential information maintained on our systems have been accessed without authorization.”
Clark added that Greenville Water does not store customers’ credit card data.
According to a statement released to the media on Friday, experts “have taken immediate and appropriate action to reinforce existing security measures and to mitigate the potential impact, as well as determining its origin.”
In the statement, Clark said that the incident “has not and will not impact or compromise the safety and delivery of water that is treated and maintained by our facilities.”
When asked for comment on the cyber-attack by the Greenville News, Greenville County government affairs coordinator Bob Mihalic stated only that “Greenville County uses multiple methods of protecting data, hardware, and infrastructure from potential cyber-attacks.”
Greenville Water’s online payment system was back up and running on Monday afternoon, and its phone payment system was restored the following day. Greenville Water has assured customers that payments received late as a result of the attack will not lead to fines or the shutting off of their water supply.
“Our customer experience has been fully restored,” states Greenville Water on its website. “We are continuing our investigation and will share additional details as they become available.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Smart City Alert as Experts Detail LoRaWAN Security Issues

Security researchers are warning that the technology underpinning many smart city deployments is susceptible to a range of cyber-attacks, enabling hackers to sabotage infrastructure in potentially life-threatening raids.
IOActive’s latest research paper covers LoRaWAN, or the Long-Range Wide Area Network protocol which many low-powered IoT devices use to connect to the internet in scenarios such as smart cities, industrial IoT, smart homes, utilities, vehicle tracking and healthcare.
It claimed that the root keys used to encrypt communications between smart devices, gateways and network servers are poorly protected.
Hackers could extract keys by reverse engineering device firmware, grab hard-coded keys that ship with some open source LoRaWAN libraries, compromise vulnerable LoRaWAN network servers, or even guess the keys in some circumstances, the report claimed.
Once encryption keys are in their possession, the black hats could launch denial of service attacks, or replace legitimate with false comms data. This could cause connected infrastructure to break or even explode, putting lives at risk, IOActive claimed.
“Organizations are blindly trusting LoRaWAN because it’s encrypted, but that encryption can be easily bypassed if hackers can get their hands on the keys — which our research shows they can do in several ways, with relative ease, ” explained Cesar Cerrudo, IOActive CTO.
“Once hackers have access, there are many things they could potentially do – they could prevent utilities firms from taking smart meter readings, stop logistics companies from tracking vehicles, or prohibit hospitals from receiving readings from smart equipment. In extreme cases, a compromised network could be fed false device readings to cover up physical attacks against infrastructure, like a gas pipeline. Or to prompt industrial equipment containing volatile substances to overcorrect; causing it to break, combust or even explode.”
Worse still, the researchers claimed that there’s no way an organization could find out if its LoRaWAN network is being attacked or if encryption keys have been compromised.
That’s why IOActive has released a LoRaWAN Auditing Framework to help these firms pen test their deployments.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Hackers Begin Uploading 30 Million Cards from Wawa Breach

As many as 31 million stolen payment card records from a 2019 breach at convenience store chain Wawa could soon be on sale on a notorious dark web marketplace.
Stas Alforov and Christopher Thomas at threat intelligence firm Gemini Advisory claimed the upload of stolen data at the Joker’s Stash site began on Monday. Dubbed “BIGBADABOOM-III,” the dump has been linked to a breach at East Coast chain Wawa which was discovered in December last year.
Although the incident was revealed on December 10, attackers were apparently inside the network since early March, enabling them to make off with a huge trove of card numbers, expiration dates and cardholder names.
“Since the breach may have affected over 850 stores and potentially exposed 30 million sets of payment records, it ranks among the largest payment card breaches of 2019, and of all time. It is comparable to Home Depot’s 2014 breach exposing 50 million customers’ data or to Target’s 2013 breach exposing 40 million sets of payment card data,” Gemini Advisory wrote.
“Notably, major breaches of this type often have low demand in the dark web. This may be due to the breached merchant’s public statement or to security researchers’ quick identification of the point of compromise. However, Joker’s Stash uses the media coverage of major breaches such as these to bolster the credibility of their shop and their position as the most notorious vendor of compromised payment cards.”
At the time of writing, 100,000 card records had been uploaded to the marketplace, including state geolocation information.
The full breach trove is estimated to feature 30 million US cards and around one million from other countries, which were lifted when cardholders visited Wawa outlets during the breach period.
A press release issued by Wawa on Tuesday did not reference the size of the data loss, but explained that the firm’s payment card processor, as well as affected card brands and issuers, had been notified to heighten fraud monitoring.
The firm also clarified that no user PINs or CV2 numbers were taken, and that the breach didn’t affect ATM transactions.
“We continue to encourage our customers to remain vigilant in reviewing charges on their payment card statements and to promptly report any unauthorized use to the bank or financial institution that issued their payment card by calling the number on the back of the card,” it added.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Dell Technologies Announces Adrian McDonald as New EMEA President

Dell Technologies today announced that Adrian McDonald will become the company’s new EMEA president, effective February 3 2020.
McDonald brings over 30 years of IT leadership experience to the role and will be responsible for all businesses, including PCs, server, storage and services, across the Europe Middle East and Africa region. He will also continue in his role as global lead for the Mosaic Employee Resource Group at Dell Technologies, which represents and promotes cultural inclusion and the benefits of cultural intelligence.
“In a time of great change, Dell Technologies is ideally positioned to add value to customers and partners,” said McDonald, president EMEA, Dell Technologies.
“I’m incredibly excited for the future. We are at a tipping point for technology innovation. Computing will be more intelligent, personal and accessible in the 2020s, and this is going to have an even bigger impact on the world than the last decade, transforming how we live and work. Our customers understand this. They are not only looking to reimagine their businesses with the opportunities digital brings, but in many cases, undertake a dramatic transformation and I am looking forward to working with them and our partners to enable them to achieve this.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk