Customer Tracking at Ralphs Grocery Store

To comply with California’s new data privacy law, companies that collect information on consumers and users are forced to be more transparent about it. Sometimes the results are creepy. Here’s an article about Ralphs, a California supermarket chain owned by Kroger:

…the form proceeds to state that, as part of signing up for a rewards card, Ralphs “may collect” information such as “your level of education, type of employment, information about your health and information about insurance coverage you might carry.”

It says Ralphs may pry into “financial and payment information like your bank account, credit and debit card numbers, and your credit history.”

Wait, it gets even better.

Ralphs says it’s gathering “behavioral information” such as “your purchase and transaction histories” and “geolocation data,” which could mean the specific Ralphs aisles you browse or could mean the places you go when not shopping for groceries, thanks to the tracking capability of your smartphone.

Ralphs also reserves the right to go after “information about what you do online” and says it will make “inferences” about your interests “based on analysis of other information we have collected.”

Other information? This can include files from “consumer research firms” ­– read: professional data brokers ­– and “public databases,” such as property records and bankruptcy filings.

The reaction from John Votava, a Ralphs spokesman:

“I can understand why it raises eyebrows,” he said. We may need to change the wording on the form.”

That’s the company’s solution. Don’t spy on people less, just change the wording so they don’t realize it.

More consumer protection laws will be required.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

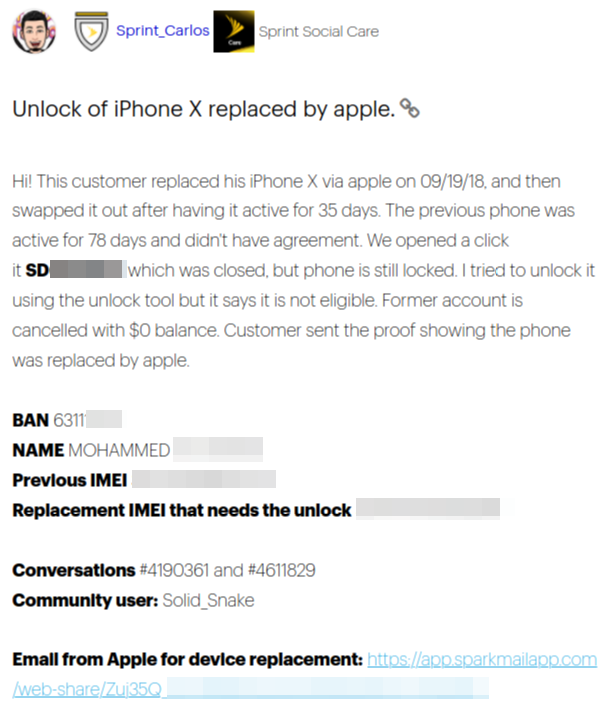
Sprint Exposed Customer Support Site to Web

Fresh on the heels of a disclosure that Microsoft Corp. leaked internal customer support data to the Internet, mobile provider Sprint has addressed a mix-up in which posts to a private customer support community were exposed to the Web.

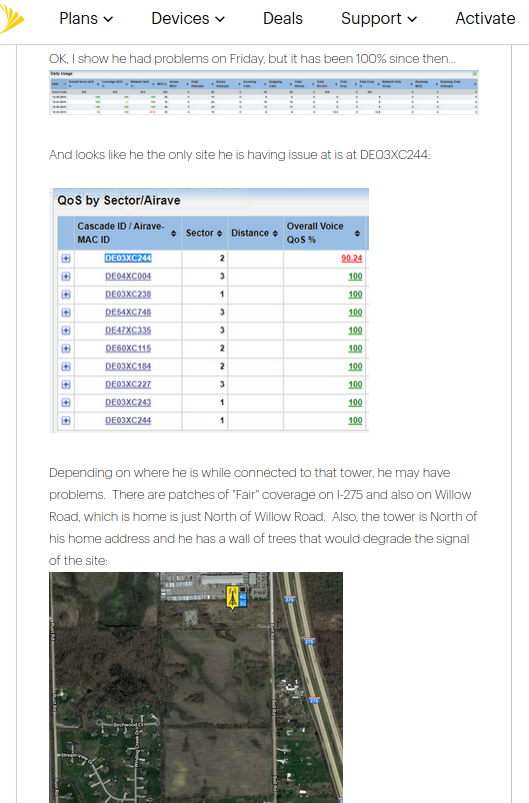
KrebsOnSecurity recently contacted Sprint to let the company know that an internal customer support forum called “Social Care” was being indexed by search engines, and that several months worth of postings about customer complaints and other issues were viewable without authentication to anyone with a Web browser.

A redacted screen shot of one Sprint customer support thread exposed to the Web.

A Sprint spokesperson responded that the forum was indeed intended to be a private section of its support community, but that an error caused the section to become public.

“These conversations include minimal customer information and are used for frontline reps to escalate issues to managers,” said Lisa Belot, Sprint’s communications manager.

A review of the exposed support forum by this author suggests that while none of the posts exposed customer information such as payment card data, a number of them did include customer account information, such customer names, device identifiers and in some cases location information.

Perhaps more importantly for Sprint and its customers, the forum also included numerous links and references to internal tools and procedures. This sort of information would no doubt be of interest to scammers seeking to conduct social engineering attacks against Sprint employees as way to perpetrate other types of fraud, including unauthorized SIM swaps or in gleaning more account information from targeted customers.

Earlier this week, vice.com reported that hackers are phishing workers at major U.S. telecommunications companies to gain access to internal company tools. That news followed a related Vice report earlier this month which found ne’er-do-wells are now getting telecom employees to run software that lets the hackers directly reach into the internal systems of U.S. telecom companies to take over customer cell phone numbers.

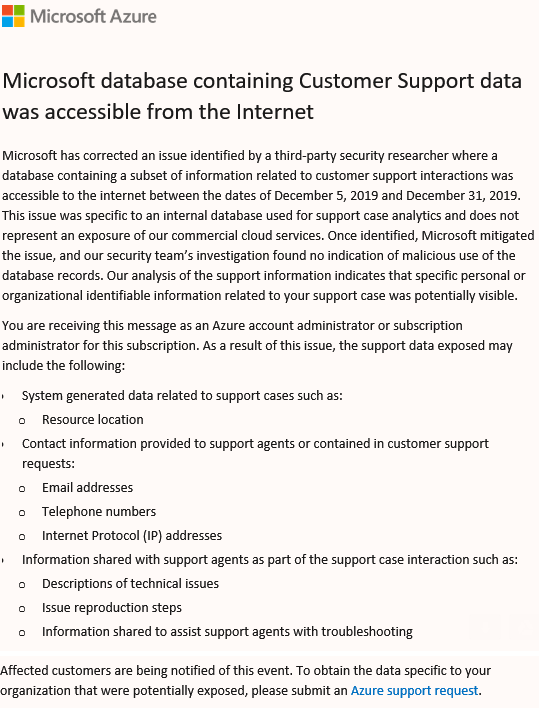
The misstep by Sprint comes just days after Microsoft acknowledged that a database containing “a subset of information related to customer support interactions was accessible to the internet between the dates of Dec. 5 and Dec. 31, 2019.” Microsoft said it was alerting individuals whose information was exposed, which included location information, email and IP addresses, telephone numbers and descriptions of technical issues.

A message Microsoft sent to customers affected by their recent leak of customer support data.

This week marked the annual observance of Data Privacy Day, an occasion in which we are reminded to be more judicious about the types of personal information we voluntarily share on social media and other Web sites. But both the Microsoft and Sprint stumbles are a reminder that billion-dollar companies very often expose this information on our behalf, even when we are doing everything within our power to safeguard it.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

SEC Publishes Cybersecurity Practices of Financial Industry

SEC Publishes Cybersecurity Practices of Financial Industry

The US Securities and Exchange Commission (SEC) has published a 10-page document detailing cybersecurity practices observed to be in use in the financial industry.

The observations were gathered by the SEC’s Office of Compliance Inspections (OCIE) and are based on thousands of examinations of broker-dealers, investment advisers, clearing agencies, national securities exchanges, and other SEC registrants.

OCIE issued the examination observations yesterday on the SEC website with the hope of providing firms with guidelines for how to strengthen their cybersecurity. 

The observations highlight certain approaches taken by market participants in the areas of governance and risk management, access rights and controls, data loss prevention, mobile security, incident response and resiliency, vendor management, and training and awareness. They also examine how companies have responded with resiliency in the wake of a cybersecurity incident. 

While acknowledging that there is no one-size-fits-all approach when it comes to cybersecurity, OCIE recommended establishing an incident response plan and contacting local authorities or the Federal Bureau of Investigation (FBI) if an attack or compromise is discovered or suspected. 

Training employees on how to detect threats was advised, along with implementing a mobile device management solution for the workplace that covered all devices used by employees under a “bring your own device” policy.

“Through risk-targeted examinations in all five examination program areas, OCIE has observed a number of practices used to manage and combat cyber risk and to build operational resiliency,” said Peter Driscoll, director of OCIE. 

“We felt it was critical to share these observations in order to allow organizations the opportunity to reflect on their own cybersecurity practices.”

To prevent data loss, OCIE recommended establishing a patch management program covering all software and hardware and verifying that the decommissioning and disposal of any hardware and software does not create system vulnerabilities.  

“Data systems are critical to the functioning of our markets, and cybersecurity and resiliency are at the core of OCIE’s inspection efforts,” said SEC chairman Jay Clayton. 

“I commend OCIE for compiling and sharing these observations with the industry and the public and encourage market participants to incorporate this information into their cybersecurity assessments.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

UK Medical Products Manufacturer Shuts Plant Following Breach

UK Medical Products Manufacturer Shuts Plant Following Breach

A British company that specializes in making skin, bone, and organ grafts has temporarily closed its manufacturing plant in America following a cybersecurity breach.

Regenerative medical technology company Tissue Regenix Group PLC said on Tuesday that its computer systems and a third-party IT service provider in the United States were accessed without authorization. No details were given regarding how the incident occurred or when the company became aware that it had been compromised.

Tissue Regenix responded to the cybersecurity incident by taking the affected system offline and shutting down operations at its plant in Texas. The company has appointed forensic cybersecurity specialists to investigate how and when the breach occurred and said that it is in talks with the relevant legal authorities. 

The cybersecurity incident is not believed to have affected any of Tissue Regenix’s operations in the UK and is not thought to have impacted the company’s financial systems. 

“Tissue Regenix has taken precautionary steps, including taking affected systems offline. This has restricted access to certain business operations, including the company’s ability in the short-term to continue manufacturing in its United States facility, which has been taken offline whilst the incident is being investigated,” said a Tissue Regenix spokesperson. 

“The company is engaged with its third-party IT service provider, the relevant legal authorities and cyber security experts to rectify the incident as quickly as possible and to minimize any impact on its operations. The time required to resolve the incident is currently unknown.”

According to Reuters, news of the breach caused the share price of Tissue Regenix to tumble by as much as 22%. 

Tissue Regenix was formed in 2006 as an offshoot of the University of Leeds. The company is based in the historical city of York. Tissue Regenix set up its base in America in the tail end of 2012. 

The medical technology product that Tissue Regenix is known for producing is a special kind of tissue that can be used to repair worn-out or diseased human body parts. The tissue has been designed in such a way that the patient’s body is unlikely to reject a graft. 

The cyber-attack has come at a particularly bad time for Tissue Regenix, which said last Wednesday that its funding is not guaranteed beyond April.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

NFL Twitter Accounts Hacked One Week Before Super Bowl

NFL Twitter Accounts Hacked One Week Before Super Bowl

The Twitter accounts of America’s National Football League (NFL) and 15 of its teams have been hacked just one week before the biggest football game of the 2019–2020 season.

The first team to be compromised was the Chicago Bears, whose account @ChicagoBears was hacked at 8:40 a.m. on Sunday morning. 

Followers were shown an image of a man with a full, dark beard who was wearing the traditional Arabic head gear of a keffiyeh and an agal together. Along with the photo, hackers posted the caption: “Welcome to our new owner @Turki_alalshikh #ProBowl #Bears100 #ChicagoBears.”

A Saudi “white hat” hacker group known as OurMine was quick to claim responsibility for the hacks, which the group said were carried out as a publicity stunt to “announce that we are back” and to “show people that everything is hackable.”

Fans of rival American football team the Detroit Lions seized the opportunity afforded by the Bears hack to propose a trade. The account @PrideofDetroit tweeted at the Bears: “Hey, while you’re still hacked @ChicagoBears, trade us Khalil Mack for a 6th rounder. Twitter is a binding contract.”

The hackers decided to run with the joke and responded with “Done for 1$.”

By 12:43 p.m. on Sunday, the Chicago Bears were back in control of their Twitter account and had posted a message apologizing to fans for the compromise. 

OurMine allegedly compromised the official Twitter account of the NFL on Monday. In a statement released yesterday, the NFL said: “On Monday, the NFL Cybersecurity department became aware of a breach of league-related social media accounts. Targeted breaches and additional failed attempts were discovered across the league and team accounts.

“The NFL took immediate action and directed the teams to secure their social media accounts and prevent further unauthorized access.”

NFL reporter Dov Kleiman began a Twitter thread of screenshots depicting all the NFL team accounts compromised in the OurMine hack. By his reckoning, a total of 15 teams were hacked, including the Green Bay Packers

Other teams to be hacked were the Kansas City Chiefs and the San Francisco 49ers, who are due to compete on February 2 in the Super Bowl LIV game, which will decide the champion for the NFL’s 2019–2020 (and 100th) season.

An anonymous individual who responded to questions from NBC News via an email account linked with OurMine would not reveal how the group carried out the hack. The individual did, however, reveal their pick for Sunday’s big game, predicting a victory for the Chiefs.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Suspected Magecart Hackers Arrested in Indonesia

Suspected Magecart Hackers Arrested in Indonesia

Three men have been arrested in Indonesia in a region-wide crackdown on gangs using the infamous Magecart digital skimming code, according to Interpol.

The law enforcement organization worked with private sector partner Group-IB to identify and analyze hundreds of e-commerce websites around the world infected with the malicious JavaScript.

Its Operation Night Fury saw Interpol’s central ASEAN Cyber Capability Desk send reports to police in the affected countries, including six in southeast Asia.

One of these was Indonesia, where three men were arrested on suspicion of running Magecart C&C servers there.

According to Interpol, the suspects are thought to have been using the stolen card details to buy luxury goods and electronics and then resell them to launder their profits.

Singaporean police have also been able to disable two further C&C servers following intelligence gleaned from the operation, while investigations in other ASEAN countries are ongoing, Interpol said.

“Strong and effective partnerships between police and the cybersecurity industry are essential to ensure law enforcement worldwide has access to the information they need to address the scale and complexity of today’s cyber threat landscape,” said Interpol director of cybercrime, Craig Jones.

“This successful operation is just one example of how law enforcement is working with industry partners, adapting and applying new technologies to aid investigations, and ultimately reduce the global impact of cybercrime.”

This could well be the first time Magecart hackers have been arrested by police. Digital skimming code is now used by multiple groups around the world, making it harder for police to tackle.

The news comes just weeks after Interpol celebrated another win: a public-private partnership with Trend Micro led to the identification of over 20,000 routers in southeast Asia infected with crypto-mining malware.

Thanks to Operation Goldfish Alpha, police managed to reduce this number by 78% and efforts are continuing to identify the remaining compromised devices.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Staff Send 130+ Emails Per Week to Wrong Recipient

Staff Send 130+ Emails Per Week to Wrong Recipient

Staff in large enterprises send 136 emails per week to the wrong person, according to new data from Tessian released to coincide with today’s Data Protection Day.

The annual event was launched 13 years by the Council of Europe to recognize the date in 1981 that signatures were invited for Convention 108, the first legally binding international treaty on data protection.

However, despite the introduction of the GDPR nearly two years ago and the filing of over 160,000 breach notifications in the intervening period, poor data protection practices still appear to be rife.

Analyzing data from its global network of clients, Tessian claimed that corporate data is sent to unauthorized or personal email accounts nearly 200,000 times a year, for enterprises of 10,000 employees and up.

For large businesses of 1000 employees, the figure is nearly 20,000, while it drops again to around 5000 for SMBs.

Tessian CEO, Tim Sadler, claimed that human error is still the leading cause of breaches today — whether staff are deliberately breaking the rules or simply being negligent.

“Everyone has an email blunder story. After all, the average worker spends over a third of their working-week on email, so mistakes are bound to happen. But we’re seeing serious repercussions beyond just embarrassment over cc-ing the wrong person – more people are exposing personal and corporate data,” he added.

“These mistakes could see your data falling into the wrong hands and your company facing the regulator’s wrath under GDPR.”

Also known as Data Privacy Day in the US and elsewhere, the event is an opportunity to raise awareness among consumers and businesses of their respective online rights and responsibilities regarding data protection.

The GDPR has already done much to promote these within the EU and beyond, the European Commission claimed in a statement issued to mark the occasion.

“According to Eurobarometer results, the highest levels of awareness among citizens are recorded for the right to access their own data (65%), the right to correct the data if they are wrong (61%), the right to object to receiving direct marketing (59%) and the right to have their own data deleted (57%),” it revealed.

“Our priority and that of everyone involved should be to foster a harmonized and consistent implementation of data protection rules throughout the EU.”

However, the legislation remains a work in progress, according to Dob Todorov, CEO of HeleCloud.

“In truth, a chasm exists between the legal language used and the IT implementation needed to support it. And, while this chasm exists, some businesses will fail to meet the data protection standards that this regulation promotes — either accidentally or through the abuse of the grey areas,” he argued.

“As regulators look to hand out more fines, they should also focus on providing pragmatic and clear guidance at a technical level, without discriminating against current or future technologies.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

UK’s IoT Law Hopes to Drive Security-by-Design

UK’s IoT Law Hopes to Drive Security-by-Design

The UK government has unveiled a new consumer IoT law designed to prohibit the sale of smart products that fail to meet three strict security requirements.

Drawn up by the Department for Digital, Culture, Media and Sport (DCMS), the proposals would ensure all IoT kit sold in the UK allows users to set unique passwords and not revert them to any factory settings.

This would seem to combat the scourge of Mirai-like malware, which finds exposed devices on the internet and cracks them open with a list of popular default password choices.

Manufacturers of IoT devices would also have to provide a public point of contact so that anyone can report vulnerabilities and have them acted on “in a timely manner.”

The same IoT kit-makers would have to explicitly state the minimum length of time a device will receive security updates at point-of-sale, allowing consumers to decide whether they’re happy with vendor promises.

However, there’s no mention of enforcing a ‘kitemark’ for consumers which would allow buyers to easily spot whether products have met a minimum standard of security and quality. Such a standard technically exists in the UK, after the British Standards Institution (BSI) introduced one in May 2018, and at a European level, with the launch of ETSI TS 103 645 around a year ago.

It’s also unclear exactly how the UK would prohibit the sale of non-compliant IoT kit, especially items which can be sourced online from China and elsewhere. The majority of the world’s smart gadgets are not manufactured in the UK.

That said, the UK is still ahead of the US in its moves to drive regulation of an industry that exposes consumers and businesses to growing cyber risk.

“Consumer IoT devices can deliver real benefits to individuals and society, but techUK’s research shows that concerns over poor security practices act as a significant barrier to their take-up. TechUK is therefore supportive of the government’s commitment to legislate for cybersecurity to be built into consumer IoT products from the design stage,” argued techUK director of markets, Matthew Evans.

“TechUK has been working on these three principles for the past four years. We support the work to ensure that they are consistent and are influencing international standards.”

Carl Wear, head of e-crime at Mimecast, claimed that the UK push could have a beneficial impact on other parts of the world, although the nature of technology innovation would require revisions to the law.

“The legislation and any accompanying guidance will then need to be re-visited rapidly and updated to maintain an adequate minimum standard of security, as necessary,” he said. “I am certain that this move by the UK will likely prompt consideration of further regulation within other jurisdictions, in order to maintain trust in their own IoT and parity with the security of others.”

The UK’s proposals follow a “world first” voluntary code of practice introduced by the government in October 2018, on which the European standard was based.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk