CES wiz-bang surveillance tech gives privacy advocates the willies.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Presidential campaign season is officially, officially, upon us now, which means it’s time to confront the weird and insidious ways in which technology is warping politics. One of the biggest threats on the horizon: artificial personas are coming, and they’re poised to take over political debate. The risk arises from two separate threads coming together: artificial intelligence-driven text generation and social media chatbots. These computer-generated “people” will drown out actual human discussions on the Internet.
Text-generation software is already good enough to fool most people most of the time. It’s writing news stories, particularly in sports and finance. It’s talking with customers on merchant websites. It’s writing convincing op-eds on topics in the news (though there are limitations). And it’s being used to bulk up “pink-slime journalism” — websites meant to appear like legitimate local news outlets but that publish propaganda instead.
There’s a record of algorithmic content pretending to be from individuals, as well. In 2017, the Federal Communications Commission had an online public-commenting period for its plans to repeal net neutrality. A staggering 22 million comments were received. Many of them — maybe half — were fake, using stolen identities. These comments were also crude; 1.3 million were generated from the same template, with some words altered to make them appear unique. They didn’t stand up to even cursory scrutiny.
These efforts will only get more sophisticated. In a recent experiment, Harvard senior Max Weiss used a text-generation program to create 1,000 comments in response to a government call on a Medicaid issue. These comments were all unique, and sounded like real people advocating for a specific policy position. They fooled the Medicaid.gov administrators, who accepted them as genuine concerns from actual human beings. This being research, Weiss subsequently identified the comments and asked for them to be removed, so that no actual policy debate would be unfairly biased. The next group to try this won’t be so honorable.
Chatbots have been skewing social-media discussions for years. About a fifth of all tweets about the 2016 presidential election were published by bots, according to one estimate, as were about a third of all tweets about that year’s Brexit vote. An Oxford Internet Institute report from last year found evidence of bots being used to spread propaganda in 50 countries. These tended to be simple programs mindlessly repeating slogans: a quarter million pro-Saudi “We all have trust in Mohammed bin Salman” tweets following the 2018 murder of Jamal Khashoggi, for example. Detecting many bots with a few followers each is harder than detecting a few bots with lots of followers. And measuring the effectiveness of these bots is difficult. The best analyses indicate that they did not affect the 2016 US presidential election. More likely, they distort people’s sense of public sentiment and their faith in reasoned political debate. We are all in the middle of a novel social experiment.
Over the years, algorithmic bots have evolved to have personas. They have fake names, fake bios, and fake photos — sometimes generated by AI. Instead of endlessly spewing propaganda, they post only occasionally. Researchers can detect that these are bots and not people, based on their patterns of posting, but the bot technology is getting better all the time, outpacing tracking attempts. Future groups won’t be so easily identified. They’ll embed themselves in human social groups better. Their propaganda will be subtle, and interwoven in tweets about topics relevant to those social groups.
Combine these two trends and you have the recipe for nonhuman chatter to overwhelm actual political speech.
Soon, AI-driven personas will be able to write personalized letters to newspapers and elected officials, submit individual comments to public rule-making processes, and intelligently debate political issues on social media. They will be able to comment on social-media posts, news sites, and elsewhere, creating persistent personas that seem real even to someone scrutinizing them. They will be able to pose as individuals on social media and send personalized texts. They will be replicated in the millions and engage on the issues around the clock, sending billions of messages, long and short. Putting all this together, they’ll be able to drown out any actual debate on the Internet. Not just on social media, but everywhere there’s commentary.
Maybe these persona bots will be controlled by foreign actors. Maybe it’ll be domestic political groups. Maybe it’ll be the candidates themselves. Most likely, it’ll be everybody. The most important lesson from the 2016 election about misinformation isn’t that misinformation occurred; it is how cheap and easy misinforming people was. Future technological improvements will make it all even more affordable.
Our future will consist of boisterous political debate, mostly bots arguing with other bots. This is not what we think of when we laud the marketplace of ideas, or any democratic political process. Democracy requires two things to function properly: information and agency. Artificial personas can starve people of both.
Solutions are hard to imagine. We can regulate the use of bots — a proposed California law would require bots to identify themselves — but that is effective only against legitimate influence campaigns, such as advertising. Surreptitious influence operations will be much harder to detect. The most obvious defense is to develop and standardize better authentication methods. If social networks verify that an actual person is behind each account, then they can better weed out fake personas. But fake accounts are already regularly created for real people without their knowledge or consent, and anonymous speech is essential for robust political debate, especially when speakers are from disadvantaged or marginalized communities. We don’t have an authentication system that both protects privacy and scales to the billions of users.
We can hope that our ability to identify artificial personas keeps up with our ability to disguise them. If the arms race between deep fakes and deep-fake detectors is any guide, that’ll be hard as well. The technologies of obfuscation always seem one step ahead of the technologies of detection. And artificial personas will be designed to act exactly like real people.
In the end, any solutions have to be nontechnical. We have to recognize the limitations of online political conversation, and again prioritize face-to-face interactions. These are harder to automate, and we know the people we’re talking with are actual people. This would be a cultural shift away from the internet and text, stepping back from social media and comment threads. Today that seems like a completely unrealistic solution.
Misinformation efforts are now common around the globe, conducted in more than 70 countries. This is the normal way to push propaganda in countries with authoritarian leanings, and it’s becoming the way to run a political campaign, for either a candidate or an issue.
Artificial personas are the future of propaganda. And while they may not be effective in tilting debate to one side or another, they easily drown out debate entirely. We don’t know the effect of that noise on democracy, only that it’ll be pernicious, and that it’s inevitable.
This essay previously appeared in TheAtlantic.com.
EDITED TO ADD: Jamie Susskind wrote a similar essay.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Sources tell KrebsOnSecurity that Microsoft Corp. is slated to release a software update on Tuesday to fix an extraordinarily serious security vulnerability in a core cryptographic component present in all versions of Windows. Those sources say Microsoft has quietly shipped a patch for the bug to branches of the U.S. military and to other high-value customers/targets that manage key Internet infrastructure, and that those organizations have been asked to sign agreements preventing them from disclosing details of the flaw prior to Jan. 14, the first Patch Tuesday of 2020.
According to sources, the vulnerability in question resides in a Windows component known as crypt32.dll, a Windows module that Microsoft says handles “certificate and cryptographic messaging functions in the CryptoAPI.” The Microsoft CryptoAPI provides services that enable developers to secure Windows-based applications using cryptography, and includes functionality for encrypting and decrypting data using digital certificates.
A critical vulnerability in this Windows component could have wide-ranging security implications for a number of important Windows functions, including authentication on Windows desktops and servers, the protection of sensitive data handled by Microsoft’s Internet Explorer/Edge browsers, as well as a number of third-party applications and tools.
Equally concerning, a flaw in crypt32.dll might also be abused to spoof the digital signature tied to a specific piece of software. Such a weakness could be exploited by attackers to make malware appear to be a benign program that was produced and signed by a legitimate software company.
This component was introduced into Windows more than 20 years ago — back in Windows NT 4.0. Consequently, all versions of Windows are likely affected (including Windows XP, which is no longer being supported with patches from Microsoft).
Microsoft has not yet responded to requests for comment. However, KrebsOnSecurity has heard rumblings from several sources over the past 48 hours that this Patch Tuesday (tomorrow) will include a doozy of an update that will need to be addressed immediately by all organizations running Windows.
Update 7:49 p.m. ET: Microsoft responded, saying that it does not discuss the details of reported vulnerabilities before an update is available. The company also said it does “not release production-ready updates ahead of regular Update Tuesday schedule. “Through our Security Update Validation Program (SUVP), we release advance versions of our updates for the purpose of validation and interoperability testing in lab environments,” Microsoft said in a written statement. “Participants in this program are contractually disallowed from applying the fix to any system outside of this purpose and may not apply it to production infrastructure.”
Original story:
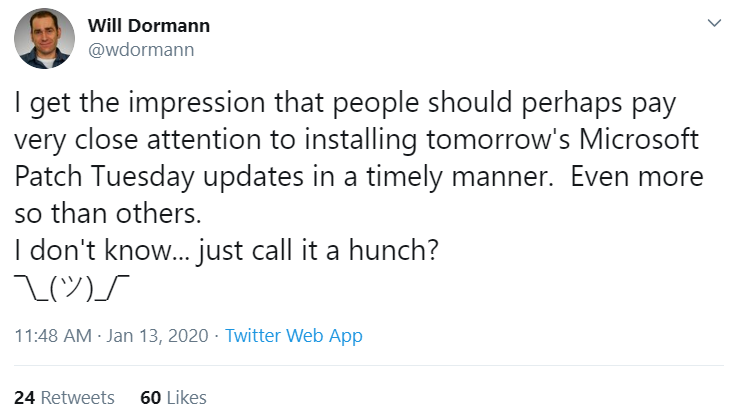
Will Dormann, a security researcher who authors many of the vulnerability reports for the CERT Coordination Center (CERT-CC), tweeted today that “people should perhaps pay very close attention to installing tomorrow’s Microsoft Patch Tuesday updates in a timely manner. Even more so than others. I don’t know…just call it a hunch?” Dormann declined to elaborate on that teaser.
It could be that the timing and topic here (cryptography) is nothing more than a coincidence, but KrebsOnSecurity today received a heads up from the U.S. National Security Agency (NSA) stating that NSA’s Director of Cybersecurity Anne Neuberger is slated to host a call on Jan. 14 with the news media that “will provide advanced notification of a current NSA cybersecurity issue.”
The NSA’s public affairs folks did not respond to requests for more information on the nature or purpose of the discussion. The invitation from the agency said only that the call “reflects NSA’s efforts to enhance dialogue with industry partners regarding its work in the cybersecurity domain.”
Stay tuned for tomorrow’s coverage of Patch Tuesday and possibly more information on this particular vulnerability.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Anyone searching for a primer on how to spot clever phishing links need look no further than those targeting customers of Apple, whose brand by many measures remains among the most-targeted. Past stories here have examined how scammers working with organized gangs try to phish iCloud credentials from Apple customers who have a mobile device that is lost or stolen. Today’s piece looks at the well-crafted links used in some of these lures.
KrebsOnSecurity heard from a reader in South Africa who recently received a text message stating his lost iPhone X had been found. The message addressed him by name and said he could view the location of his wayward device by visiting the link https://maps-icloud[.]com — which is most definitely not a legitimate Apple or iCloud link and is one of countless spoofing Apple’s “Find My” service for locating lost Apple devices.
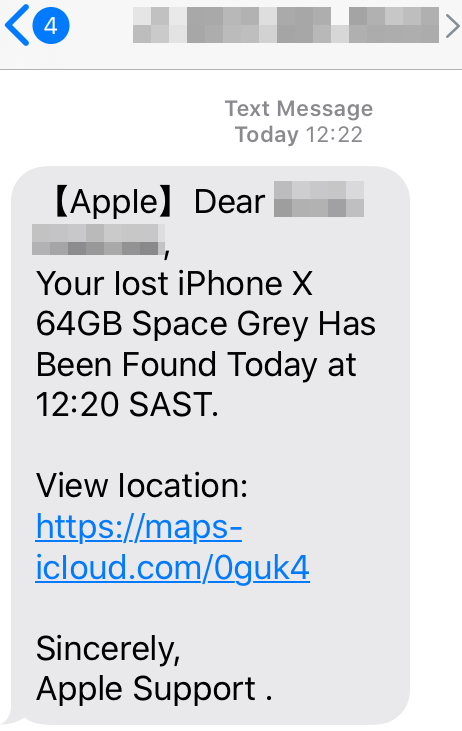
While maps-icloud[.]com is not a particularly convincing phishing domain, a review of the Russian server where that domain is hosted reveals a slew of far more persuasive links spoofing Apple’s brand. Almost all of these include encryption certificates (start with “https://) and begin with the subdomains “apple.” or “icloud.” followed by a domain name starting with “com-“.
Here are just a few examples (the phishing links in this post have been hobbled with brackets to keep them from being clickable):
apple.com-support[.]id
apple.com-findlocation[.]id
apple.com-sign[.]in
apple.com-isupport[.]in
icloud.com-site-log[.]in
Savvy readers here no doubt already know this, but to find the true domain referenced in a link, look to the right of “http(s)://” until you encounter the first forward slash (/). The domain directly to the left of that first slash is the true destination; anything that precedes the second dot to the left of that first slash is a subdomain and should be ignored for the purposes of determining the true domain name.
For instance, in the case of the imaginary link below, example.com is the true destination, not apple.com:
https://www.apple.com.example.com/findmyphone/
Of course, any domain can be used as a redirect to any other domain. Case in point: Targets of the phishing domains above who are undecided on whether the link refers to a legitimate Apple site might seek to load the base domain into a Web browser (minus the customization in the remainder of the link after the first forward slash). To assuage such concerns, the phishers in this case will forward anyone visiting those base domains to Apple’s legitimate iCloud login page (icloud.com).
The best advice to sidestep phishing scams is to avoid clicking on links that arrive unbidden in emails, text messages and other mediums. Most phishing scams invoke a temporal element that warns of dire consequences should you fail to respond or act quickly. If you’re unsure whether the message is legitimate, take a deep breath and visit the site or service in question manually — ideally, using a browser bookmark so as to avoid potential typosquatting sites.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Federal investigators on Friday arrested a Virginia man accused of being part of a neo-Nazi group that targeted hundreds of people in “swatting” attacks, wherein fake bomb threats, hostage situations and other violent scenarios were phoned in to police as part of a scheme to trick them into visiting potentially deadly force on a target’s address.
In July 2019, KrebsOnSecurity published the story Neo-Nazi Swatters Target Dozens of Journalists, which detailed the activities of a loose-knit group of individuals who had targeted hundreds of individuals for swatting attacks, including federal judges, corporate executives and almost three-dozen journalists (myself included).
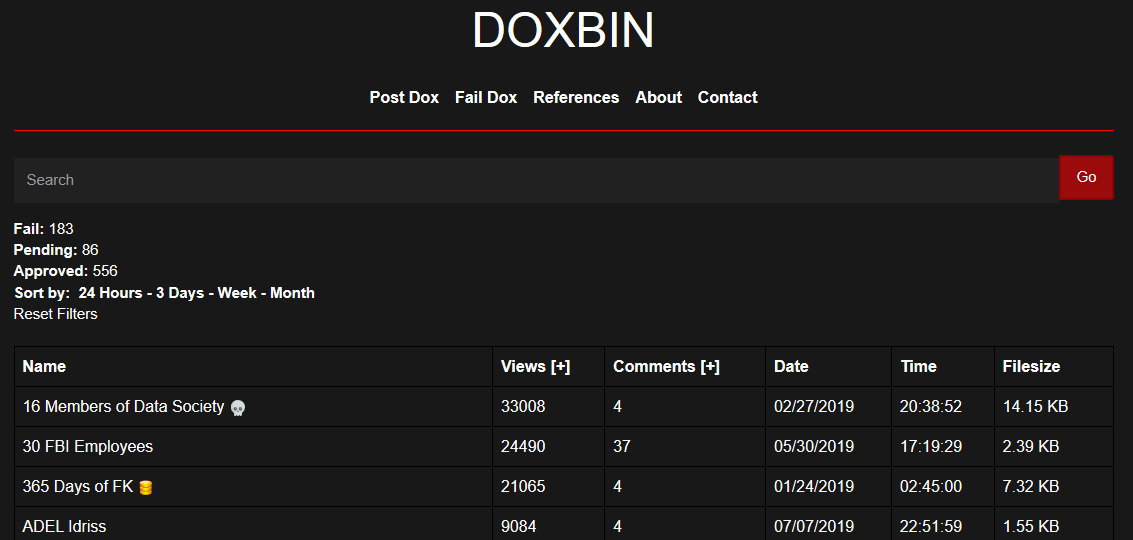
A portion of the Doxbin, as it existed in late 2019.
An FBI affidavit unsealed this week identifies one member of the group as John William Kirby Kelley. According to the affidavit, Kelley was instrumental in setting up and maintaining the Internet Relay Chat (IRC) channel called “Deadnet” that was used by he and other co-conspirators to plan, carry out and document their swatting attacks.
Prior to his recent expulsion on drug charges, Kelley was a student studying cybersecurity at Old Dominion University in Norfolk, Va. Interestingly, investigators allege it was Kelley’s decision to swat his own school in late November 2018 that got him caught. Using the handle “Carl,” Kelley allegedly explained to fellow Deadnet members he hoped the swatting would get him out of having to go to class.
The FBI says Kelley used virtual private networking (VPN) services to hide his true Internet location and various voice-over-IP (VoIP) services to conduct the swatting calls. In the ODU incident, investigators say Kelley told ODU police that someone was armed with an AR-15 rifle and had placed multiple pipe bombs within the campus buildings.
Later that day, Kelley allegedly called ODU police again but forgot to obscure his real phone number on campus, and quickly apologized for making an accidental phone call. When authorities determined that the voice on the second call matched that from the bomb threat earlier in the day, they visited and interviewed the young man.
Investigators say Kelley admitted to participating in swatting calls previously, and consented to a search of his dorm room, wherein they found two phones, a laptop and various electronic storage devices.
The affidavit says one of the thumb drives included multiple documents that logged statements made on the Deadnet IRC channel, which chronicled “countless examples of swatting activity over an extended period of time.” Those included videos Kelley allegedly recorded of his computer screen which showed live news footage of police responding to swatting attacks while he and other Deadnet members discussed the incidents in real-time on their IRC forum.
The FBI believes Kelley also was linked to a bomb threat in November 2018 at the predominantly African American Alfred Baptist Church in Old Town Alexandria, an incident that led to the church being evacuated during evening worship services while authorities swept the building for explosives.
The FBI affidavit was based in part on interviews with an unnamed co-conspirator, who told investigators that he and the others on Deadnet IRC are white supremacists and sympathetic to the neo-Nazi movement.
“The group’s neo-Nazi ideology is apparent in the racial tones throughout the conversation logs,” the affidavit reads. “Kelley and other co-conspirators are affiliated with or have expressed sympathy for Atomwafen Division,” an extremist group whose members are suspected of having committed multiple murders in the U.S. since 2017.
Investigators say on one of Kelley’s phones they found a photo of he and others in tactical gear holding automatic weapons next to pictures of Atomwaffen recruitment material and the neo-Nazi publication Siege.
As I reported last summer, several Deadnet members maintained a site on the Dark Web called the “Doxbin,” which listed the names, addresses, phone number and often known IP addresses, Social Security numbers, dates of birth and other sensitive information on hundreds of people — and in some cases the personal information of the target’s friends and family. After those indexed on the Doxbin were successfully swatted, a blue gun icon would be added next to the person’s name.
One of the core members of the group on Deadnet — an individual who used the nickname “Chanz,” among others — stated that he was responsible for maintaining SiegeCulture, a white supremacist Web site that glorifies the writings of neo-Nazi James Mason (whose various books call on followers to start a violent race war in the United States).
Deadnet chat logs obtained by KrebsOnSecurity show that another key swatting suspect on Deadnet who used the handle “Zheme” told other IRC members in March 2019 that one of his friends had recently been raided by federal investigators for allegedly having connections to the person responsible for the mass shooting in October 2018 at the Tree of Life Jewish synagogue in Pittsburgh.
At one point last year, Zheme also reminded denizens of Deadnet about a court hearing in the murder trial of Sam Woodward, an alleged Atomwaffen member who’s been charged with killing a 19-year-old gay Jewish college student.
As reported by this author last year, Deadnet members targeted dozens of journalists whose writings they considered threatening to their worldviews. Indeed, one of the targets successfully swatted by Deadnet members was Pulitzer prize winning columnist Leonard G. Pitts Jr., whose personal information as listed on the Doxbin was annotated with a blue gun icon and the label “anti-white race/politics writer.”
In another Deadnet chat log seen by this author, Chanz admits to calling in a bomb threat at the UCLA campus following a speech by Milo Yiannopoulos. Chanz bragged that he did it to frame feminists at the school for acts of terrorism.
On a personal note, I sincerely hope this arrest is just the first of many to come for those involved in swatting attacks related to Deadnet and the Doxbin. KrebsOnSecurity has obtained information indicating that several members of my family also have been targeted for harassment and swatting by this group.
Finally, it’s important to note that while many people may assume that murders and mass shootings targeting people because of their race, gender, sexual preference or religion are carried out by so-called “lone wolf” assailants, the swatting videos created and shared by Deadnet members are essentially propaganda that hate groups can use to recruit new members to their cause.
The Washington Post reports that Kelley had his first appearance in federal court in Alexandria, Va. on Friday.
“His public defender did not comment on the allegations but said his client has ‘very limited funds,’” The Post’s courts reporter Rachel Weiner wrote.
The charge against Kelley of conspiracy to make threats carries up to five years in prison. The affidavit in Kelley’s arrest is available here (PDF).
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Students in the Pittsburg Unified School District of Pennsylvania were left without internet access on Monday as the result of a ransomware attack.
With schools’ internet servers and email compromised, youngsters returning to classes after the winter break were forced to enrich their brains the old-fashioned way, through books and direct teaching.
“We will be teaching and learning like ‘back in the day,’ without laptops and internet,” wrote Pittsburg Unified School District Superintendent Janet Schulze on social media on Monday night.
“Our schools have access to student information and our phones are working.”
Alongside her message that students would be going back to “old school,” Schulze said that a ransomware attack had disabled the district’s network systems during the festive break.
According to The Mercury News, the district took all the servers affected by the attack offline, along with any servers that may have potentially been compromised.
No personal data is reported to have been accessed as a result of the incident, and normal teaching schedules were resumed on Tuesday.
“At this time, we do not have any indication that personal data/information has been compromised,” wrote Schulze.
“We are continuing to investigate and work with a cybersecurity team and experts. Since the investigation is continuing, complete findings are not available, and it is still too early for us to provide further details.”
It was reported on Tuesday that the district was working with two internet technology companies to find a remedy for the attack. Contact has also been established with attorneys who specialize in dealing with the fallout from ransomware attacks.
The latest ransomware attack is the second such incident to befall a Contra Costa County system since the new year began. On Friday, January 3, a similar attack on Contra Costa County Library System resulted in a network outage in which services at 26 branches were impacted.
Library services are yet to be restored, and visitors to the system’s website are being greeted with the message: “Our network is currently down, and patrons are unable to login at this time. We are investigating the issue and will establish service as soon as possible.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Patients of a hacked facial surgery company in Florida are being individually threatened by cyber-criminals, who are demanding money in return for not releasing stolen personal information to the public.
The Center for Facial Restoration, Inc. (TCFFR), located in Miramar, became the victim of a cyber-attack in November last year.
In a statement published on the TCFFR website, plastic surgeon and company founder Dr. Richard Davis wrote: “On November 8, 2019, I received an anonymous communication from cyber criminals stating that my clinic’s server [was] breached.”
“The hackers claimed to have ‘the complete patient’s data’ for TCFFR that ‘can be publicly exposed or traded to third parties.'”
Along with the message that his business had been compromised, Davis received a demand for an undisclosed ransom.
The ambitious cyber-criminals, not content with whatever money they may have been able to extort from the specialist rhinoplasty company, then began demanding ransoms from individual TCFFR patients.
“They demanded a ransom negotiation, and as of November 29, 2019, about 15–20 patients have since contacted TCFFR to report individual ransom demands from the attackers threatening the public release of their photos and personal information unless unspecified ransom demands are negotiated and met,” wrote Davis.
Davis believes up to 3,500 former and current patients may have been affected by the cyber-attack. Compromised data may include driving licenses, passports, home addresses, email addresses, phone numbers, patient photographs, and credit card payment receipts.
The incident was reported to the FBI’s Cyber Crimes Center on November 12, and on November 14 Davis met with the Bureau to pass on detailed information regarding the attack and the ransom demands.
Davis wrote: “The investigation is currently ongoing. The FBI requests that patients receiving ransom demands file an independent cybercrime complaint online at www.ic3.gov.”
Since the attack, Davis has installed new hard drives, firewalls, and virus/malware detection software in hopes of preventing a similar incident from happening.
“I am sickened by this unlawful and self-serving intrusion, and I am truly very sorry for your involvement in this senseless and malicious act,” wrote Davis.
The doctor published a public notice concerning the incident as the company’s data storage practices made it difficult to contact patients individually.
“Because we store PII as the scan of the patient’s intake demographic questionnaire, and not in an electronic demographic database, obtaining contact information in order to individually notify all 3,500 patients has been painstakingly slow and labor intensive, and access to the data has been hindered by ongoing IT service disruptions,” wrote Davis.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
A threat group has once again taken to the internet to publish data stolen from alleged victims who refuse to cooperate with its ransom demands.
In December 2019, the MAZE ransomware group published online a portion of the 120 GB of data they claimed to have stolen from Southwire, North America’s most prominent wire and cable manufacturer, after the company refused to pay a $6m ransom.
The data was published on the http(colon)//mazenews(dot)top/ site, which was hosted at an ISP in Ireland. Southwire subsequently filed a lawsuit in the Northern District of Georgia, USA, on December 31 against the MAZE operators and won their case, and the site was taken down.
But yesterday at around 5 p.m. ET the “mazenews” website was back up online, this time hosted out of Singapore via Alibaba.
Using an ominous black backdrop and bright red text, the website lists the companies that have allegedly been compromised. In some instances, the total amount of data that has been exfiltrated is also displayed.
On the site, MAZE states: “Represented here companies do not wish to cooperate with us, and trying to hide our successful attack on their resources. Wait for their databases and private papers here. Follow the news!”
Companies listed so far are Southwire, RBC, THEONE, Vernay, Bakerwotring, BILTON, greccoauto, Groupe Igrec, Mitch Co International, Einhell, CONTINENTALNH3, Groupe Europe Handling SAS, Auteuil Tour Eiffel, Fratelli Beretta, Randalegal, crossroadsnet, SAXBST, American tax advisory firm BST & Co, and laboratory testing facility MDL. The Florida city of Pensacola is also listed.
Downloadable files, presented as proof that a compromise has taken place, are available for Einhell, Fratelli Beretta, Crossroadsnet, MDL, BST & Co, SAXBST, Auteuil Tour Eiffel, and Southwire. Under the “proofs” category for the other companies, MAZE has written only “coming soon.”
The ransomware group claims to have exfiltrated 3 GB of data from Fratelli Beretta, and 25 GB of data each from SAXBST and BST & Co. MAZE further claims that 10% of the 120 GB it allegedly stole from Southwire is “available for downloading.”
For some unstated reason, the threat group showed mercy on alleged victim Pensacola.
“We are going to make a gift to City of Pensacola: we will not publish leaked private data, but we publish the list of leak data and hosts to proof, that we did it, we really hacked City of Pensacola,” wrote MAZE.
The city’s operational departments that MAZE claims to have compromised include the treasury, finance, risk management, executive, legal, housing, and human resources departments.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
The US made a last ditch bid to convince the British government to fall into line over Huawei this week, as newly introduced legislation proposed excluding allies from intelligence sharing agreements.
Secretary of state, Mike Pompeo, was expected to press his counterpart Dominic Raab at a meeting in Washington this week over the UK’s position on its 5G networks.
A final decision is expected to be taken by Boris Johnson’s new government later this month, but a government leak last April suggested the UK is happy to keep Huawei equipment in “non-core” parts of its networks.
That puts it at odds with a Trump administration that is trying to pressure allies into its harder line opposition to the Shenzhen-based company, which it claims is a national security risk due to its ties to the Communist Party of China.
“The security and resilience of the UK’s telecoms networks is of paramount importance,” a Foreign Office spokesperson told Reuters. “The government continues to consider its position on high-risk vendors and a decision will be made in due course.”
Also this week, Republican senator Tom Cotton introduced a new bill that would prevent Washington from sharing intelligence with any countries which allow 5G technology from Huawei to operate “within their borders.”
The legislation is seen as an attempt to put more pressure on the Five Eyes intelligence sharing alliance which includes the US, Australia, New Zealand, Canada and the UK.
Donald Trump last year declared a National Emergency to prevent “foreign adversaries” from providing equipment for its critical 5G network infrastructure. An entity list prevented US firms from selling key components to Huawei and scores of other Chinese companies.
However, its efforts to convince allies around the world to do the same has been met with mixed results, especially as blacklisting Huawei would set their development of 5G back considerably, while Trump’s “America First” rhetoric makes the US a less convincing ally.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk