Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Author: admin
Facebook Cracks Down on Deepfake Videos
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
USB Cable Kill Switch for Laptops
BusKill is designed to wipe your laptop (Linux only) if it is snatched from you in a public place:
The idea is to connect the BusKill cable to your Linux laptop on one end, and to your belt, on the other end. When someone yanks your laptop from your lap or table, the USB cable disconnects from the laptop and triggers a udev script [1, , 3] that executes a series of preset operations.
These can be something as simple as activating your screensaver or shutting down your device (forcing the thief to bypass your laptop’s authentication mechanism before accessing any data), but the script can also be configured to wipe the device or delete certain folders (to prevent thieves from retrieving any sensitive data or accessing secure business backends).
Clever idea, but I — and my guess is most people — would be much more likely to stand up from the table, forgetting that the cable was attached, and yanking it out. My problem with pretty much all systems like this is the likelihood of false alarms.
Slashdot article.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Tricky Phish Angles for Persistence, Not Passwords
Late last year saw the re-emergence of a nasty phishing tactic that allows the attacker to gain full access to a user’s data stored in the cloud without actually stealing the account password. The phishing lure starts with a link that leads to the real login page for a cloud email and/or file storage service. Anyone who takes the bait will inadvertently forward a digital token to the attackers that gives them indefinite access to the victim’s email, files and contacts — even after the victim has changed their password.
Before delving into the details, it’s important to note two things. First, while the most recent versions of this stealthy phish targeted corporate users of Microsoft’s Office 365 service, the same approach could be leveraged to ensnare users of many other cloud providers. Second, this attack is not exactly new: In 2017, for instance, phishers used a similar technique to plunder accounts at Google’s Gmail service.
Still, this phishing tactic is worth highlighting because recent examples of it received relatively little press coverage. Also, the resulting compromise is quite persistent and sidesteps two-factor authentication, and it seems likely we will see this approach exploited more frequently in the future.
In early December, security experts at PhishLabs detailed a sophisticated phishing scheme targeting Office 365 users that used a malicious link which took people who clicked to an official Office 365 login page — login.microsoftonline.com. Anyone suspicious about the link would have seen nothing immediately amiss in their browser’s address bar, and could quite easily verify that the link indeed took them to Microsoft’s real login page:
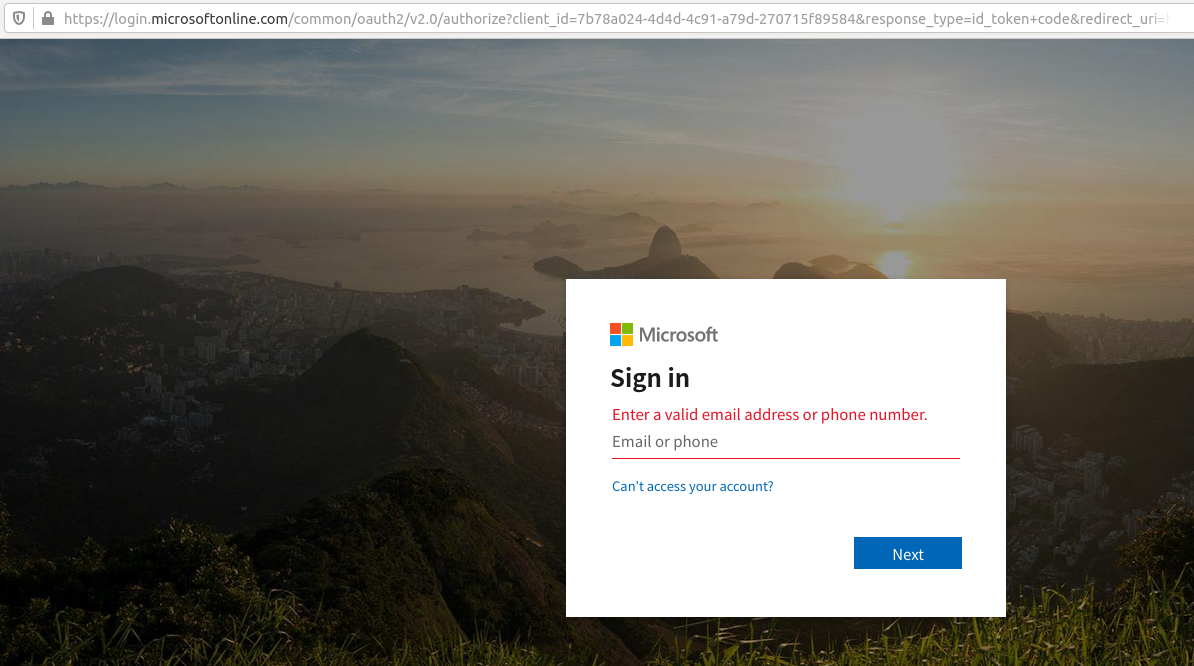
This phishing link asks users to log in at Microsoft’s real Office 365 portal (login.microsoftonline.com).
Only by copying and pasting the link or by scrolling far to the right in the URL bar can we detect that something isn’t quite right:
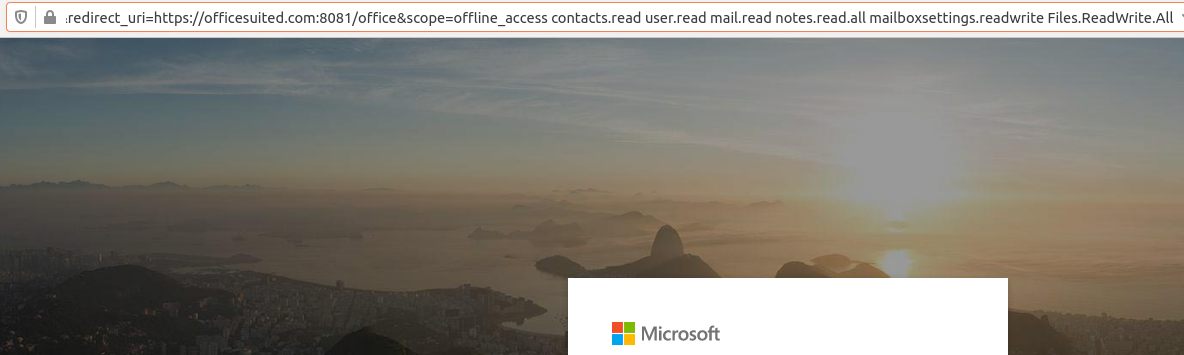
Notice this section of the URL (obscured off-page and visible only by scrolling to the right quite a bit) attempts to grant a malicious app hosted at officesuited.com full access to read the victim’s email and files stored at Microsoft’s Office 365 service.
As we can see from the URL in the image directly above, the link tells Microsoft to forward the authorization token produced by a successful login to the domain officesuited[.]com. From there, the user will be presented with a prompt that says an app is requesting permissions to read your email, contacts, OneNote notebooks, access your files, read/write to your mailbox settings, sign you in, read your profile, and maintain access to that data.
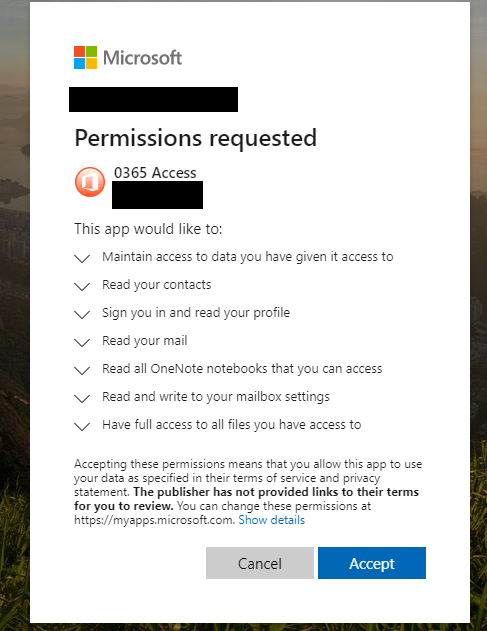
Image: PhishLabs
According to PhishLabs, the app that generates this request was created using information apparently stolen from a legitimate organization. The domain hosting the malicious app pictured above — officemtr[.]com — is different from the one I saw in late December, but it was hosted at the same Internet address as officesuited[.]com and likely signed using the same legitimate company’s credentials.
PhishLabs says the attackers are exploiting a feature of Outlook known as “add-ins,” which are applications built by third-party developers that can be installed either from a file or URL from the Office store.
“By default, any user can apply add-ins to their outlook application,” wrote PhishLabs’ Michael Tyler. “Additionally, Microsoft allows Office 365 add-ins and apps to be installed via side loading without going through the Office Store, and thereby avoiding any review process.”
In an interview with KrebsOnSecurity, Tyler said he views this attack method more like malware than traditional phishing, which tries to trick someone into giving their password to the scammers.
“The difference here is instead of handing off credentials to someone, they are allowing an outside application to start interacting with their Office 365 environment directly,” he said.
Many readers at this point may be thinking that they would hesitate before approving such powerful permissions as those requested by this malicious application. But Tyler said this assumes the user somehow understands that there is a malicious third-party involved in the transaction.
“We can look at the reason phishing is still around, and it’s because people are making decisions they shouldn’t be making or shouldn’t be able to make,” he said. “Even employees who are trained on security are trained to make sure it’s a legitimate site before entering their credentials. Well, in this attack the site is legitimate, and at that point their guard is down. I look at this and think, would I be more likely to type my password into a box or more likely to click a button that says ‘okay’?”
The scary part about this attack is that once a user grants the malicious app permissions to read their files and emails, the attackers can maintain access to the account even after the user changes his password. What’s more, Tyler said the malicious app they tested was not visible as an add-in at the individual user level; only system administrators responsible for managing user accounts could see that the app had been approved.
Furthermore, even if an organization requires multi-factor authentication at sign-in, recall that this phish’s login process takes place on Microsoft’s own Web site. That means having two-factor enabled for an account would do nothing to prevent a malicious app that has already been approved by the user from accessing their emails or files.
Once given permission to access the user’s email and files, the app will retain that access until one of two things happen: Microsoft discovers and disables the malicious app, or an administrator on the victim user’s domain removes the program from the user’s account.
Expecting swift action from Microsoft might not be ideal: From my testing, Microsoft appears to have disabled the malicious app being served from officesuited[.]com sometime around Dec. 19 — roughly one week after it went live.
In a statement provided to KrebsOnSecurity, Microsoft Senior Director Jeff Jones said the company continues to monitor for potential new variations of this malicious activity and will take action to disable applications as they are identified.
“The technique described relies on a sophisticated phishing campaign that invites users to permit a malicious Azure Active Directory Application,” Jones said. “We’ve notified impacted customers and worked with them to help remediate their environments.”
Microsoft’s instructions for detecting and removing illicit consent grants in Office 365 are here. Microsoft says administrators can enable a setting that blocks users from installing third-party apps into Office 365, but it calls this a “drastic step” that “isn’t strongly recommended as it severely impairs your users’ ability to be productive with third-party applications.”
PhishLabs’ Tyler said he disagrees with Microsoft here, and encourages Office 365 administrators to block users from installing apps altogether — or at the very least restrict them to apps from the official Microsoft store.
Apart from that, he said, it’s important for Office 365 administrators to periodically look for suspicious apps installed on their Office 365 environment.
“If an organization were to fall prey to this, your traditional methods of eradicating things involve activating two-factor authentication, clearing the user’s sessions, and so on, but that won’t do anything here,” he said. “It’s important that response teams know about this tactic so they can look for problems. If you can’t or don’t want to do that, at least make sure you have security logging turned on so it’s generating an alert when people are introducing new software into your infrastructure.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Bronze President Spies on Asia

A cyber-espionage group dubbed Bronze President has been targeting countries in South and East Asia.
Researchers at Secureworks’ Counter Threat Unit (CTU) have observed the group spying on the activities of political and law enforcement organizations and NGOs.
The threat group seems to have developed its own remote access tools, which it uses alongside publicly available remote access and post-compromise toolsets to gain entry to a network.
Using publicly available open-source tools could be a deliberate ploy by the group to cover its tracks and reduce the risk of attribution.
Once inside, the threat actors elevate their privileges and install malware on a large proportion of systems. Bronze President then runs custom batch scripts to collect specific file types and takes proactive steps to minimize detection of its activities.
The threat actors appear to be monitoring their targets as they steal data from compromised systems over a long period of time. Countries that have been targeted include India and Mongolia.
Activity from the threat actors has been observed by Secureworks’ researchers since mid-2018, but it’s is thought that the group may have started causing trouble as early as 2014.
Among the group’s phishing lures, researchers found emails suggesting an interest in national security, humanitarian, and law enforcement organizations in East, South, and Southeast Asia.
Researchers believe the Bronze President group is operating from a base within the People’s Republic of China (PRC).
Connections were found between a subset of the group’s operational infrastructure and PRC-based internet service providers. Furthermore, the group uses tools such as PlugX that have historically been leveraged by threat groups based in the PRC.
“It is likely that Bronze President is sponsored or at least tolerated by the PRC government. The threat group’s systemic long-term targeting of NGO and political networks does not align with patriotic or criminal threat groups,” wrote Secureworks’ researchers.
The operational tactics of the group indicate that the crew behind it are highly organized.
Researchers noted: “Bronze President has demonstrated intent to steal data from organizations using tools such as Cobalt Strike, PlugX, ORat, and RCSession. The concurrent use of so many tools during a single intrusion suggests that the group could include threat actors with distinct tactics, roles, and tool preferences.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Lawsuit Filed Against LifeLabs Over Data Breach

A class-action lawsuit has been filed against a Canadian laboratory testing company following a cyber-attack in which the data of 15 million of its customers was accessed by criminals.
LifeLabs reported the data breach to government partners on October 28, 2019, but waited until December 17 to notify its customers.
Sensitive information exposed in the incident may have included customers’ names, addresses, email addresses, logins, passwords, dates of birth, health card numbers, and lab test results.
The cyber-criminals who accessed the data were paid an undisclosed amount by LifeLabs in return for a promise to not make the information public.
On December 27, lawyers Peter Waldmann and Andrew Stein filed an unproven statement of claim in Ontario Superior Court in which LifeLabs is accused of breach of contract and negligence. The company is further accused of violating consumer protection laws and of violating their customers’ privacy and confidence.
The statement of claim was filed on behalf of five named plaintiffs, including lead plaintiff Christopher Sparling, who allege that LifeLabs violated their own privacy policy when they “failed to implement adequate measures and controls to detect and respond swiftly to threats and risks to the Personal Information and health records of the class members.”
It is further alleged that LifeLabs stored customers’ personal information on unsecured networks or servers, failed to implement “any, or adequate, cyber-security measures,” didn’t encrypt data, and neglected to hire or train any personnel responsible for network security management.
According to Canadian Underwriter, Waldmann and Stein are seeking more than $1.13bn in compensation for LifeLabs’ Canadian customers to make up for the mental anguish, wasted time, and damage to their credit reputation they have suffered. The plaintiffs are seeking additional punitive and moral damages.
In an open letter, LifeLabs CEO Charles Brown wrote that up to 15 million customers, almost all of them in Ontario and British Columbia, may have been affected by the data breach.
On December 18, a toll-free helpline, set up to field calls from concerned LifeLabs customers, received over 5,000 calls. According to CTV news, a second line had to be set up to deal with the volume of calls.
LifeLabs is owned by one of the biggest pension funds in Canada, the Ontario Municipal Employees Retirement System, which has $92 billion in assets.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Austria’s Foreign Ministry Hit by Cyber-Attack

The Austrian government has been hit by a cyber-attack that could be the work of a rival foreign power.
The attack, which was leveled against the country’s Foreign Ministry, began late on Saturday night. A spokesperson for the ministry described the incident as “serious” and said that experts had warned it could continue for several days.
On the same day the attack was launched, at a congress held in the city of Salzburg, Austria’s Green Party said that it was in favor of forming a coalition with the conservative People’s Party.
The ministry said that the attack had been caught early and countermeasures had immediately been put in place. The signatures and the pattern of the attack suggest that it could be the work of a state-sponsored threat actor.
“Despite all intensive security measures, there is never 100 percent protection against cyber-attacks,” the ministry said, before adding that other European countries had been affected by similar incidents in the past.
By Sunday, the ministry’s official website was once again accessible.
Commenting on the news, Hugo van den Toorn, manager of offensive security at Outpost24, said: “It is true that despite the precautions taken and all the controls in place, a motivated attacker can always find a way through an organization’s defenses. Although we see an increase in politically motivated attacks over the past few years, we should remain vigilant in blaming certain threat actors or nation-states.
“As we also see that attribution remains difficult with cyber-attacks, past attacks have taught us that adversaries will attempt to make their attacks look like other actors in an attempt to avoid taking the blame or to provoke conflicting parties.”
This latest incident in Austria follows the serious cyber-attack on the German government’s IT network, which was launched in March 2018. A group of Russian-backed threat actors known as APT28 or Fancy Bear was suspected to be behind not only that attack, but also an earlier cyber-hit on the German parliament carried out in 2015.
APT28 are similarly suspected of waging cyber-warfare on entities in Eastern Europe and in the United States.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
US Braced for Cyber Retaliation from Iran

The US government has echoed concerns from the cybersecurity industry that Iranian state hackers could respond to the assassination of a top Tehran general with attacks on US critical infrastructure (CNI).
Widely considered the second most powerful man in Iran, Qassem Suleimani was killed by a US drone strike in Baghdad on Friday.
Military and political leaders in the country have warned of retribution, while signs posted along the vast funeral procession today are reported to have read: “Harsh revenge is awaiting.”
The Department for Homeland Security (DHS) has duly issued an alert warning of a terror threat on home soil, although it admitted “at this time we have no information indicating a specific, credible threat to the homeland.”
However, an attack could come with little or no warning, with cyber a likely vector, it said.
“Previous homeland-based plots have included, among other things, scouting and planning against infrastructure targets and cyber-enabled attacks against a range of US- based targets,” the notice continued.
“Iran maintains a robust cyber program and can execute cyber-attacks against the United States. Iran is capable, at a minimum, of carrying out attacks with temporary disruptive effects against critical infrastructure in the United States.”
On Saturday, the website of the government-run American Federal Depository Library Program (FDLP) was defaced with an image of a bloodied Donald Trump. Industry experts believe things could escalate even further.
John Hultquist, director of intelligence analysis at FireEye, warned of an uptick in cyber-espionage against government entities, designed to give Tehran a geopolitical advantage, and destructive attacks on CNI.
“Iran has leveraged wiper malware in destructive attacks on several occasions in recent years. Though, for the most part, these incidents did not affect the most sensitive industrial control systems, they did result in serious disruptions to operations,” he added.
“We are concerned that attempts by Iranian actors to gain access to industrial control system software providers could be leveraged to gain widespread access to critical infrastructure simultaneously. In the past, subverting the supply chain has been the means to prolific deployment of destructive malware by Russian and North Korean actors.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Japanese Love Hotel Site Breached

A booking site for customers of Japanese “love hotels” has been hacked, raising fears over follow-on identity fraud and blackmail attempts.
In a country known for its focus on convenience, love hotels are a popular feature in towns and cities, offering a place for amorous couples to bed down for a few hours or a whole night without needing to trek back to their tiny apartments.
In such establishments, privacy is of the utmost importance, with the check-in counter often designed so that guests can pay for a room without coming face-to-face with any hotel employees.
However, the compromise at Almex, which runs the popular HappyHotels[dot]jp site, threatens to unmask those guests.
In a notice, the firm said customer data including guest email addresses, handle name, birth date and gender, telephone number, log-ins, address and credit card information could all have been swiped by attackers.
“We sincerely apologize for the inconvenience and anxiety that may have caused our customers and other concerned parties. The service has been suspended because we are currently investigating the cause and taking measures,” it added.
“This password may have been leaked at this time, so if you use the same e-mail address and password as those of other companies ‘services, please change the password of other companies’ services as soon as possible.”
Given the sensitive nature of the website, and the fact that some users may have been visiting love hotels with someone other than their partner, there’s an obvious risk of online blackmail and extortion for guests who’ve been exposed.
According to recent stats, over a third (38%) of Japanese women claimed that their husband or boyfriend has cheated on them in the past, with the figure slightly lower (31%) for women that have cheated on their partners.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Travelex Site Still Down After New Year’s Eve Attack

The websites of a major global currency exchange business are still down after a “software virus” struck the firm on New Year’s Eve last week.
London-headquartered Travelex, which describes itself as “the world’s leading foreign exchange specialist,” operates online around the world and in airports, as well as supporting travel money services for several high street lenders in the UK.
A statement on its main UK website written in English, French, Japanese, German, Dutch, Italian and Czech claims that “planned maintenance” is the cause of the “temporary” outage and that it will be back online soon.
However, a notice posted to Twitter and the firm’s dot-com site reveals a different story — that a “software virus” discovered last Tuesday has “compromised some of its services.”
“As a precautionary measure in order to protect data and prevent the spread of the virus, we immediately took all our systems offline. Our investigation to date shows no indication that any personal or customer data has been compromised,” it explained.
“We have deployed teams of IT specialists and external cybersecurity experts who have been working continuously since New Year’s Eve to isolate the virus and restore affected systems.”
The firm’s bricks-and-mortar branches are still working as normal, Travelex added, but reports suggest that both the app and its services to UK banks are impacted.
Some experts suggested ransomware as a likely cause of the incident, with the firm praised for its speedy response.
“Having a well-tested resilience plan in place that covers the technical aspects, communication with the public and clear responsibilities for handling incidents can ultimately make a difference between a costly response and maintaining customer trust,” argued Iain Kothari-Johnson, financial services Lead for cybersecurity at Fujitsu UK.
“Break-glass incident response services, where experts are on-hand to rapidly investigate and mitigate threats, can also help reduce the financial and reputational impact of this type of incident and should be considered as part of any good resilience plan.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk