Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Author: admin
Friday Squid Blogging: Giant Squid Video from the Gulf of Mexico
Fantastic video:
Scientists had used a specialized camera system developed by Widder called the Medusa, which uses red light undetectable to deep sea creatures and has allowed scientists to discover species and observe elusive ones.
The probe was outfitted with a fake jellyfish that mimicked the invertebrates’ bioluminescent defense mechanism, which can signal to larger predators that a meal may be nearby, to lure the squid and other animals to the camera.
With days to go until the end of the two-week expedition, 100 miles (160 kilometers) southeast of New Orleans, a giant squid took the bait.
As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.
Read my blog posting guidelines here.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Chrome Extension Stealing Cryptocurrency Keys and Passwords
A malicious Chrome extension surreptitiously steals Ethereum keys and passwords:
According to Denley, the extension is dangerous to users in two ways. First, any funds (ETH coins and ERC0-based tokens) managed directly inside the extension are at risk.
Denley says that the extension sends the private keys of all wallets created or managed through its interface to a third-party website located at erc20wallet[.]tk.
Second, the extension also actively injects malicious JavaScript code when users navigate to five well-known and popular cryptocurrency management platforms. This code steals login credentials and private keys, data that it’s sent to the same erc20wallet[.]tk third-party website.
Another example of how blockchain requires many single points of trust in order to be secure.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Chicago Healthcare Provider Reports Data Breach

A data breach at a Chicago healthcare provider may have exposed the personal health information of 12,578 people.
Sinai Health System was breached in a cybersecurity incident that occurred in the fall of 2019. Hackers are thought to have gained unauthorized access to the organization’s email via a phishing attack.
Patient data that was stored in the email accounts and may have been exposed included names, addresses, dates of birth, Social Security numbers, health information, or health insurance information.
The healthcare provider became aware that two of its employees had been taken in by a phishing scam that struck in October.
In a statement released by Sinai Health System on December 19, the company wrote: “Sinai Health System (Sinai) has become aware of a potential data security incident that may have resulted in the inadvertent exposure of some patients’ personal and health information.
“On October 16, 2019, forensic information technology experts determined that patient information could be at risk after an unknown third party gained unauthorized access to two employee email accounts.”
Following the discovery of the malicious attack, hospital officials took steps to secure the email accounts and reset passwords. Sinai Health System has also reviewed and revised its information security policies and procedures, including email retention procedures.
Employees of the healthcare provider were given additional cybersecurity training following the attack to reduce the risk of further breaches’ occurring. The organization has also enhanced the filtering protocols for its email accounts.
An investigation into the incident launched by Sinai Health System uncovered no evidence that any patient information had been exfiltrated or misused.
Sinai Health System wrote: “Experts performed an investigation and found no evidence that any patient information was removed from Sinai Health System’s email accounts or systems.
“Further, Sinai is not aware of any misuse of any patient’s information and has seen no indication that any patient’s information is in the hands of someone it should not be as a result of this incident.”
Information regarding the breach was submitted on December 13 to the Office for Civil Rights, which has launched its own investigation into the incident.
Sinai Health System is composed of Mount Sinai Hospital, Holy Cross Hospital, Schwab Rehabilitation Hospital, Sinai Children’s Hospital, Sinai Community Institute, Sinai Medical Group, and Sinai Urban Health Institute.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
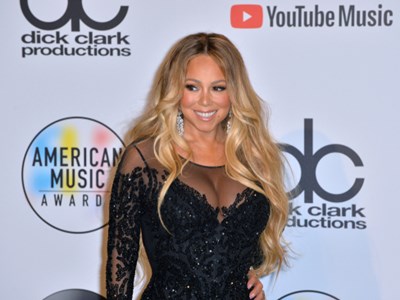
Mariah Carey’s Twitter Account Hacked

Hackers have taken over the Twitter account of five-time Grammy Award winner Mariah Carey and used it to send sexually suggestive messages referencing rapper Eminem.
Singing superstar Carey is used to being in the public eye, especially over the festive period when her massive hit “All I Want for Christmas Is You” is played the world over. However, on New Year’s Eve the phenomenally successful singer and actress hit the headlines for an entirely different reason.
According to CNN, as the curtain fell on 2019, hackers broke into Carey’s account and posted several offensive, racist, and downright lewd tweets. One tweet, reported by The Source, is said to have read: “Eminem can still hold this p***y.”
Another tweet posted by the hackers, which bizarrely received 5,463 “likes” and was retweeted 4,014 times, read “Merry Christmas You Dumb Ass N****s!”
In further tweets making references to Eminem, the hackers wrote about the rapper’s daughter and posted the comment “Eminem has a little p***s.”
It is unclear whether the remarks were an embarrassingly weak attempt at humor or a tribute to Eminem’s track “The Kids,” in which the rapper describes the most private part of his anatomy as being the size of a peanut.
The hack occurred over several hours on Tuesday afternoon, with the last tweet posted by the infantile miscreants hitting social media at 3:35 p.m.
Carey has 21.4 million followers on Twitter. The singer took the hack in good humor, responding to the incident with a tweet of her own. At 9:51 p.m. on December 31, the vocalist quipped: “I take a freaking nap and this happens?”
It’s believed that Carey was targeted by the notorious Chuckling Squad hacking group, which famously compromised the Twitter account of Twitter CEO Jack Dorsey in August after obtaining his cell phone number.
The group has also claimed responsibility for hacking other celebrity accounts, including that of actress Chloë Grace Moretz.
A Twitter spokesperson told The Hollywood Reporter: “As soon as we were made aware of the issue, we locked the compromised account and are currently investigating the situation.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Layoffs Planned at NortonLifeLock

American software company NortonLifeLock is planning to axe over 140 jobs in two states to cut costs.
According to a report published on December 30 in newspaper Community Impact, the security business plans to lay off 42 employees at their Granite Parkway site in Plano, Texas, in the coming months.
A total of 34 Plano positions are expected to be terminated by mid-January, with an additional eight roles expected to be scrapped by mid-February.
Texas isn’t the only state in which NortonLifeLock plans to cut jobs in 2020. The San Francisco Business Times reported on December 31 that roughly 100 NortonLifeLock employees based in California will lose their jobs over the next few months.
Vincent Pilette, CEO of NortonLifeLock, told the newspaper that the company is not only axing jobs but also selling off real estate in a major effort to reduce costs and help drive earnings growth.
Arizona-based NortonLifeLock was previously known as Symantec. The company underwent a rebranding after its enterprise cybersecurity business was acquired by San Jose chipmaker Broadcom for around $11bn in the summer of 2019.
In recent weeks, the Wall Street Journal has reported that NortonLifeLock’s cybersecurity rival McAfee may put in a bid to buy the company’s consumer business, challenging existing private equity bidders Permira and Advent International.
On August 8, the same day that Broadcom’s acquisition of Symantec was publicized, Symantec announced plans to lay off roughly 7 percent of its employees during fiscal year 2020.
At its Mountain View headquarters, 152 jobs were expected to be terminated, along with a further 18 positions in San Francisco and 36 roles in Culver City, Los Angeles County.
The layoffs were expected to have been completed by the end of March 2020, according to the San Francisco Chronicle.
NortonLifeLock has more than 11,000 employees worldwide and serves more than 50 million people with Norton antivirus software and LifeLock identity theft protection.
The Chronicle reported in September that the newly acquired Symantec would be closing or downsizing various facilities and data centers at an estimated cost of approximately $100m.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
US Soldiers Banned from Using TikTok

Chinese-owned video sharing app TikTok has been banned for use by US soldiers due to growing security concerns, according to reports.
Although military recruiters are using the app to encourage more young people to sign-up for service, owner ByteDance has come under increasing scrutiny in the US over its links to Beijing.
The new Defence Department guidance, seen by Military.com, points to “TikTok as having potential security risks associated with its use.
“Be wary of applications you download, monitor your phones for unusual and unsolicited texts etc., and delete them immediately and uninstall TikTok to circumvent any exposure of personal information,” it continued.
TikTok first came under fire for appearing to censor content related to pro-democracy protests in Hong Kong, and has since been the subject of an investigation by a powerful US committee.
The Committee on Foreign Investment in the United States (CFIUS) has launched an inquiry into whether the sensitive personal user data TikTok collects represents a national security risk. If it decides to turn this into a full investigation, it could spell bad news for the future of the app inside the US.
CFIUS reviews whether foreign acquisitions of US companies could harm the country’s interests. ByteDance didn’t seek the committee’s clearance when it bought US app Musical.ly (now TikTok), in 2017, so the new inquiry is apparently seen as fair game.
The US Army ban follows similar guidance from the US Navy. However, although these new rules apply to government-issued devices, soldiers could still technically use the app on their personal smartphones.
TikTok also released its first ever transparency report at the end of December. But far from alleviating concerns around its links to Beijing, the document raised more suspicions.
According to the document, it didn’t receive a single take down request from the Chinese government in the first half of 2019.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Microsoft Seizes Domains to Disrupt North Korean Hackers

Microsoft has seized scores of domains thought to have been used by a North Korean threat group to support a spear-phishing and information-stealing campaign.
The tech giant secured a court order after filing against the “Thallium” group (aka APT37), enabling it to take control of 50 domains it said were being used to execute attacks against mainly US, but also Japanese and South Korean entities.
“This network was used to target victims and then compromise their online accounts, infect their computers, compromise the security of their networks and steal sensitive information,” explained Microsoft VP of customer security and trust, Tom Burt.
“Based on victim information, the targets included government employees, think tanks, university staff members, members of organizations focused on world peace and human rights, and individuals that work on nuclear proliferation issues.”
Victims are typically hit by spear-phishing attacks using info gathered from public sources to add legitimacy.
Clicking through on these will take the victim to a spoofed website requesting account log-ins. This strategy is designed to give Thallium attackers access to their emails, contact lists, calendar appointments and anything else of interest.
The group has also been observed setting up a mail forwarding facility so that it can continue to monitor a victim’s communications even after they have updated their account password, Burt explained.
“In addition to targeting user credentials, Thallium also utilizes malware to compromise systems and steal data,” he added.
“Once installed on a victim’s computer, this malware exfiltrates information from it, maintains a persistent presence and waits for further instructions. The Thallium threat actors have utilized known malware named ‘BabyShark’ and ‘KimJongRAT’.”
The takedown follows similar operations carried out by Microsoft against groups operating from China, Russia and Iran.
Back in July last year, the firm claimed it had warned 10,000 customers that they’d been targeted by nation state attacks over the previous 12 months, including hundreds of US political organizations.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
US Coast Guard Sounds Alarm After Ransomware Attack

US maritime facilities have been on high alert over the Christmas break after the Coast Guard revealed details of a ransomware-related outage in late December.
The bulletin described a recent attack causing widespread operational disruption at a “Maritime Transportation Security Act (MTSA) regulated facility.
“Forensic analysis is currently ongoing but the virus, identified as ‘Ryuk’ ransomware, may have entered the network of the MTSA facility via an email phishing campaign. Once the embedded malicious link in the email was clicked by an employee, the ransomware allowed for a threat actor to access significant enterprise Information Technology (IT) network files, and encrypt them, preventing the facility’s access to critical files,” it explained.
“The virus further burrowed into the industrial control systems that monitor and control cargo transfer and encrypted files critical to process operations. The impacts to the facility included a disruption of the entire corporate IT network (beyond the footprint of the facility), disruption of camera and physical access control systems, and loss of critical process control monitoring systems.”
The port facility’s operations were apparently disrupted for over 30 hours as a result of the attack.
The Coast Guard urged maritime authorities to implement risk management programs according to best practices outlined in the NIST Cybersecurity Framework (CSF) and NIST Special Publication 800-82.
Specific controls it recommended include intrusion prevention/detection systems, modern virus detection, host and server monitoring, network segmentation, up-to-date IT/OT network diagrams and regular back-ups.
Experts have been warning about a major cyber-attack on port facilities for some time. Late last year, a report from the Singapore-based Cyber Risk Management (CyRiM) project warned that a ransomware campaign targeting Asia’s ports could cost the global economy as much as $110bn.
In July last year the US Coast Guard issued a marine safety alert urging vessel and facility owners and operators to improve baseline cybersecurity, following an attack on a “deep draft vessel” bound for the Port of New York and New Jersey.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
California Adopts Strictest Privacy Law in U.S.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk