Netwrix and Stealthbits Announce Merger
Netwrix and Stealthbits Announce Merger

American cybersecurity companies Netwrix and Stealthbits Technologies, Inc. announced today that they will be merging. 

The combined entity will operate as Netwrix, with Steve Dickson continuing to serve as its chief executive officer and on the company’s Board of Directors. Steve Cochran, founder and chairman of Stealthbits, will be an investor in Netwrix and will also serve on the new entity’s Board.

Terms of the transaction were not disclosed.

Netwrix has scooped up over 150 industry awards since it was founded in 2006. The new incarnation of the company will employ over 500 people and serve customers in more than 50 countries. 

“We couldn’t be more thrilled to be merging with the people and products of Stealthbits,” said Dickson.

“Our combined organization can now offer data security solutions for any organization anywhere in the world.”

The combined entity will continue to offer Netwrix’s complete portfolio of over half a dozen security solutions aimed at identifying and detecting data security risk as well as protecting against, responding to, and recovering from cybersecurity attacks.

Cochran said that the merger will give Stealthbits’ customers access to a one-stop shop for all their data protection and cybersecurity needs.

“Stealthbits has always been driven to work with our customers to solve their most challenging credential and data security requirements,” said Cochran. 

“Combining our breadth of products and depth of expertise with that of Netwrix means our customers can quickly strengthen their security posture and address multiple projects and requirements through a single provider.”

A press release announcing the merger said that it would speak to the problem of fragmented solutions in the data security market preventing organizations from building comprehensive security strategies to protect sensitive and regulated data.

“To address this challenge, Netwrix and Stealthbits are joining forces to leverage each other’s expertise to broaden product capabilities and improve user experience,” stated the release.

Stealthbits was founded by Cochran in 2001. The cybersecurity software company’s focus is on protecting an organization’s sensitive data and the credentials attackers use to steal that data. 

Last year the company won the Best Cybersecurity Company and Best Privileged Access Management Product categories in the Cybersecurity Excellence Gold Awards.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
UK Rejects Assange Extradition Request

UK Rejects Assange Extradition Request

A British court has ruled that WikiLeaks founder Julian Paul Assange should not be extradited to the United States to stand trial over the publication of thousands of classified diplomatic and military documents.

The US Department of Justice initially indicted Assange in April 2019 for conspiring with former US Army intelligence analyst Chelsea Manning to crack a password to a classified US government computer network, the Secret Internet Protocol Network (SIPRNet).

However, that charge was superseded in May 2019 by a new 18-count indictment alleging that beginning in late 2009, 49-year-old Assange and WikiLeaks actively solicited United States classified information, publishing a list of “Most Wanted Leaks” that sought classified documents. 

“Manning responded to Assange’s solicitations by using access granted to her as an intelligence analyst to search for United States classified documents, and provided to Assange and WikiLeaks databases containing approximately 90,000 Afghanistan war-related significant activity reports, 400,000 Iraq war-related significant activities reports, 800 Guantanamo Bay detainee assessment briefs, and 250,000 US Department of State cables,” said the DOJ. 

The security incident, in which many documents classified at the Secret level were exposed, was described by the DOJ as one of the largest compromises of classified information in the history of the United States.   

In Westminster Magistrates’ Court today, District Judge Vanessa Baraitser rejected the Trump administration’s request to extradite Assange to the United States on mental health grounds. 

“That extradition should be refused because it would be unjust and oppressive by reason of Mr. Assange’s mental condition and the high risk of suicide pursuant to section 91 of the EA 2003,” Baraitser said.

Referring to the opinion of Professor Michael Kopelman, medical expert and emeritus professor of neuropsychiatry at King’s College London, Baraitser said, “Taking account of all of the information available to him, he considered Mr Assange’s risk of suicide to be very high should extradition become imminent. This was a well-informed opinion carefully supported by evidence and explained over two detailed reports.”

Commenting on Baraitser’s decision, the Freedom of the Press Foundation said: “This is a huge relief to anyone who cares about the rights of journalists.

“The extradition request was not decided on press freedom grounds; rather, the judge essentially ruled the US prison system was too repressive to extradite. However, the result will protect journalists everywhere.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Microsoft: SolarWinds Attackers Viewed Our Source Code

Microsoft: SolarWinds Attackers Viewed Our Source Code

Microsoft has revealed that the nation state group behind a recent global cyber-espionage campaign managed to view some of the firm’s source code.

The tech giant has provided several updates in the wake of the discovery of the campaign, which appears to have targeted mainly US government agencies and tech firms and has been linked to Russia.

In the spirit of cross-industry collaboration, its latest notice goes into more detail about the attack on its own systems, which was discovered when the firm found evidence of the malicious SolarWinds binaries used to target others.

“Our investigation has revealed attempted activities beyond just the presence of malicious SolarWinds code in our environment,” it explained.

“We detected unusual activity with a small number of internal accounts and upon review, we discovered one account had been used to view source code in a number of source code repositories. The account did not have permissions to modify any code or engineering systems and our investigation further confirmed no changes were made. These accounts were investigated and remediated.”

Microsoft claimed that its use of open source development practices and culture internally means that it does “not rely on the secrecy of source code for the security of products.

“So viewing source code isn’t tied to elevation of risk,” it added.

“As with many companies, we plan our security with an ‘assume breach’ philosophy and layer in defense-in-depth protections and controls to stop attackers sooner when they do gain access.”

New victims of the campaign are emerging all the time.

In late December, the US Cybersecurity and Infrastructure Security Agency (CISA) issued a new alert warning that the same threat actor is using the same vector (SolarWinds Orion) to target not just federal but also state and local governments, as well as critical infrastructure and private sector organizations.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
One Million Compromised Accounts Found at Top Gaming Firms

One Million Compromised Accounts Found at Top Gaming Firms

Security researchers have warned gaming companies to improve their cybersecurity posture after discovering 500,000 breached employee credentials and a million compromised internal accounts on the dark web.

Tel Aviv-based threat intelligence firm Kela decided to investigate the top 25 publicly listed companies in the sector based on revenue.

After scouring dark web marketplaces, it discovered a thriving market in network access on both the supply and demand side.

This included nearly one million compromised accounts related to employee- and customer-facing resources, half of which were listed for sale last year.

Compromised accounts linked to internal resources like admin panels, VPNs, Jira instances, FTPs, SSOs, developer-related environments and more were found in virtually all of the top 25 gaming companies studied.

This could put these firms at risk of customer data theft, corporate espionage, ransomware and more. Kela said it had tracked ransomware attacks on four gaming companies in recent months.

“Credentials to internal resources of recently attacked companies – such as VPN, website management portals, admin, Jira and more – were put up for sale and hence were available for any potential attacker prior to the cyber-attacks that occurred,” it added.

“We also detected an infected computer (bot) which had credential logs to plenty of sensitive accounts that could be accessed by attackers upon purchase: SSO, Kibana, Jira, adminconnect, ServiceNow, Slack, VPN, password-manager and poweradmin of the company – all on a single bot. This strongly suggests that it’s used by an employee of the company with administrator rights. This highly valuable bot was available for sale for less than $10.”

Elsewhere, the researchers found half-a-million gaming employee credentials exposed on the dark web after breaches at third-party firms, many of which were available for free.

These could also provide attackers with a useful foothold in victim networks, they warned.

Kela urged gaming companies to invest in ongoing monitoring of their digital assets across the dark web, as well as enhanced staff training on things like password management, and deployment of multi-factor authentication (MFA).

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

NYSE to Delist Chinese Telcos on National Security Grounds

NYSE to Delist Chinese Telcos on National Security Grounds

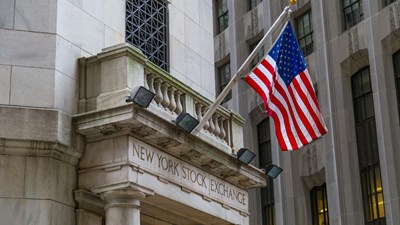
The New York Stock Exchange (NYSE) has begun delisting three Chinese telecoms giants because of their alleged ties to the country’s military.

The exchange released a brief statement on December 31 outlining the process, which came in response to an executive order signed by outgoing President Donald Trump in November last year.

The three affected companies are China Telecom, one of the world’s largest telcos, China Mobile and China Unicom Hong Kong. All are based in the People’s Republic (PRC) and make the vast majority of their revenue outside the US.

“The order prohibits, beginning 9:30 a.m. eastern standard time on January 11, 2021, any transaction in publicly traded securities, or any securities that are derivative of, or are designed to provide investment exposure to such securities, of any Communist Chinese military company, by any United States person,” the note explained.

Trump’s November executive order claimed that Beijing is increasingly “exploiting United States capital” to modernize its military. Even Chinese companies which appear to be private in fact are conscripted into supporting these strategic goals, it said.

“Through the national strategy of military-civil fusion, the PRC increases the size of the country’s military-industrial complex by compelling civilian Chinese companies to support its military and intelligence activities,” it alleged. 

“Those companies, though remaining ostensibly private and civilian, directly support the PRC’s military, intelligence and security apparatuses and aid in their development and modernization.”

As a result, these and other Chinese firms listed on US exchanges constitute an “unusual and extraordinary threat” to US national security and foreign policy and the country’s economy.

Other Chinese firms set for the same treatment include Huawei and surveillance giant Hikvision.

Last month a new bill was passed by the House of Representatives which will require all foreign firms to comply with US auditing rules or delist from the country’s exchanges. This could lead to a number of Chinese firms pulling out, as Beijing has been refusing such scrutiny on national security grounds for over a decade.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Military Cryptanalytics, Part III

The NSA has just declassified and released a redacted version of Military Cryptanalytics, Part III, by Lambros D. Callimahos, October 1977.

Parts I and II, by Lambros D. Callimahos and William F. Friedman, were released decades ago — I believe repeatedly, in increasingly unredacted form — and published by the late Wayne Griswold Barker’s Agean Park Press. I own them in hardcover.

Like Parts I and II, Part III is primarily concerned with pre-computer ciphers. At this point, the document only has historical interest. If there is any lesson for today, it’s that modern cryptanalysis is possible primarily because people make mistakes

The monograph a while to become public. The cover page says that the initial FOIA request was made in July 2012: eight and a half years ago.

And there’s more books to come. Page 1 starts off:

This text constitutes the third of six basic texts on the science of cryptanalytics. The first two texts together have covered most of the necessary fundamentals of cryptanalytics; this and the remaining three texts will be devoted to more specialized and more advanced aspects of the science.

Presumably, volumes IV, V, and VI are still hidden inside the classified libraries of the NSA.

And from page ii:

Chapters IV-XI are revisions of seven of my monographs in the NSA Technical Literature Series, viz: Monograph No. 19, “The Cryptanalysis of Ciphertext and Plaintext Autokey Systems”; Monograph No. 20, “The Analysis of Systems Employing Long or Continuous Keys”; Monograph No. 21, “The Analysis of Cylindrical Cipher Devices and Strip Cipher Systems”; Monograph No. 22, “The Analysis of Systems Employing Geared Disk Cryptomechanisms”; Monograph No.23, “Fundamentals of Key Analysis”; Monograph No. 15, “An Introduction to Teleprinter Key Analysis”; and Monograph No. 18, “Ars Conjectandi: The Fundamentals of Cryptodiagnosis.”

This points to a whole series of still-classified monographs whose titles we do not even know.

EDITED TO ADD: I have been informed by a reliable source that Parts 4 through 6 were never completed. There may be fragments and notes, but no finished works.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk