Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Author: admin
Ransomware and IP Theft: Top COVID-19 Healthcare Security Scares
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
How the SolarWinds Hackers Bypassed Duo’s Multi-Factor Authentication
This is interesting:
Toward the end of the second incident that Volexity worked involving Dark Halo, the actor was observed accessing the e-mail account of a user via OWA. This was unexpected for a few reasons, not least of which was the targeted mailbox was protected by MFA. Logs from the Exchange server showed that the attacker provided username and password authentication like normal but were not challenged for a second factor through Duo. The logs from the Duo authentication server further showed that no attempts had been made to log into the account in question. Volexity was able to confirm that session hijacking was not involved and, through a memory dump of the OWA server, could also confirm that the attacker had presented cookie tied to a Duo MFA session named duo-sid.
Volexity’s investigation into this incident determined the attacker had accessed the Duo integration secret key (akey) from the OWA server. This key then allowed the attacker to derive a pre-computed value to be set in the duo-sid cookie. After successful password authentication, the server evaluated the duo-sid cookie and determined it to be valid. This allowed the attacker with knowledge of a user account and password to then completely bypass the MFA set on the account. It should be noted this is not a vulnerability with the MFA provider and underscores the need to ensure that all secrets associated with key integrations, such as those with an MFA provider, should be changed following a breach.
Again, this is not a Duo vulnerability. From ArsTechnica:
While the MFA provider in this case was Duo, it just as easily could have involved any of its competitors. MFA threat modeling generally doesn’t include a complete system compromise of an OWA server. The level of access the hacker achieved was enough to neuter just about any defense.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Another Massive Russian Hack of US Government Networks
The press is reporting a massive hack of US government networks by sophisticated Russian hackers.
Officials said a hunt was on to determine if other parts of the government had been affected by what looked to be one of the most sophisticated, and perhaps among the largest, attacks on federal systems in the past five years. Several said national security-related agencies were also targeted, though it was not clear whether the systems contained highly classified material.
[…]
The motive for the attack on the agency and the Treasury Department remains elusive, two people familiar with the matter said. One government official said it was too soon to tell how damaging the attacks were and how much material was lost, but according to several corporate officials, the attacks had been underway as early as this spring, meaning they continued undetected through months of the pandemic and the election season.
The attack vector seems to be a malicious update in SolarWinds’ “Orion” IT monitoring platform, which is widely used in the US government (and elsewhere).
SolarWinds’ comprehensive products and services are used by more than 300,000 customers worldwide, including military, Fortune 500 companies, government agencies, and education institutions. Our customer list includes:
- More than 425 of the US Fortune 500
- All ten of the top ten US telecommunications companies
- All five branches of the US Military
- The US Pentagon, State Department, NASA, NSA, Postal Service, NOAA, Department of Justice, and the Office of the President of the United States
- All five of the top five US accounting firms
- Hundreds of universities and colleges worldwide
I’m sure more details will become public over the next several weeks.
EDITED TO ADD (12/15): More news.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
SolarWinds Hack Could Affect 18K Customers
The still-unfolding breach at network management software firm SolarWinds may have resulted in malicious code being pushed to nearly 18,000 customers, the company said in a legal filing on Monday. Meanwhile, Microsoft should soon have some idea which and how many SolarWinds customers were affected, as it recently took possession of a key domain name used by the intruders to control infected systems.
On Dec. 13, SolarWinds acknowledged that hackers had inserted malware into a service that provided software updates for its Orion platform, a suite of products broadly used across the U.S. federal government and Fortune 500 firms to monitor the health of their IT networks.
In a Dec. 14 filing with the U.S. Securities and Exchange Commission (SEC), SolarWinds said roughly 33,000 of its more than 300,000 customers were Orion customers, and that fewer than 18,000 customers may have had an installation of the Orion product that contained the malicious code. SolarWinds said the intrusion also compromised its Microsoft Office 365 accounts.
The initial breach disclosure from SolarWinds came five days after cybersecurity incident response firm FireEye announced it had suffered an intrusion that resulted in the theft of some 300 proprietary software tools the company provides to clients to help secure their IT operations.
On Dec. 13, FireEye published a detailed writeup on the malware infrastructure used in the SolarWinds compromise, presenting evidence that the Orion software was first compromised back in March 2020. FireEye didn’t explicitly say its own intrusion was the result of the SolarWinds hack, but the company confirmed as much to KrebsOnSecurity earlier today.
Also on Dec. 13, news broke that the SolarWinds hack resulted in attackers reading the email communications at the U.S. Treasury and Commerce departments.
On Dec. 14, Reuters reported the SolarWinds intrusion also had been used to infiltrate computer networks at the U.S. Department of Homeland Security (DHS). That disclosure came less than 24 hours after DHS’s Cybersecurity and Infrastructure Security Agency (CISA) took the unusual step of issuing an emergency directive ordering all federal agencies to immediately disconnect the affected Orion products from their networks.
ANALYSIS
Security experts have been speculating as to the extent of the damage from the SolarWinds hack, combing through details in the FireEye analysis and elsewhere for clues about how many other organizations may have been hit.
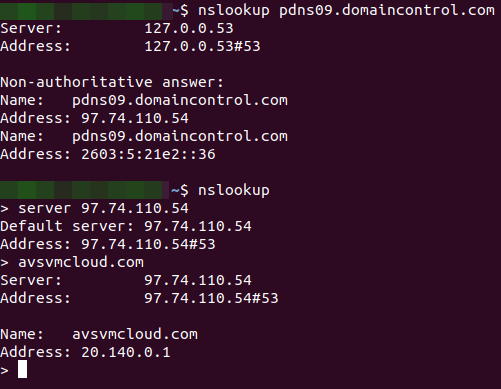
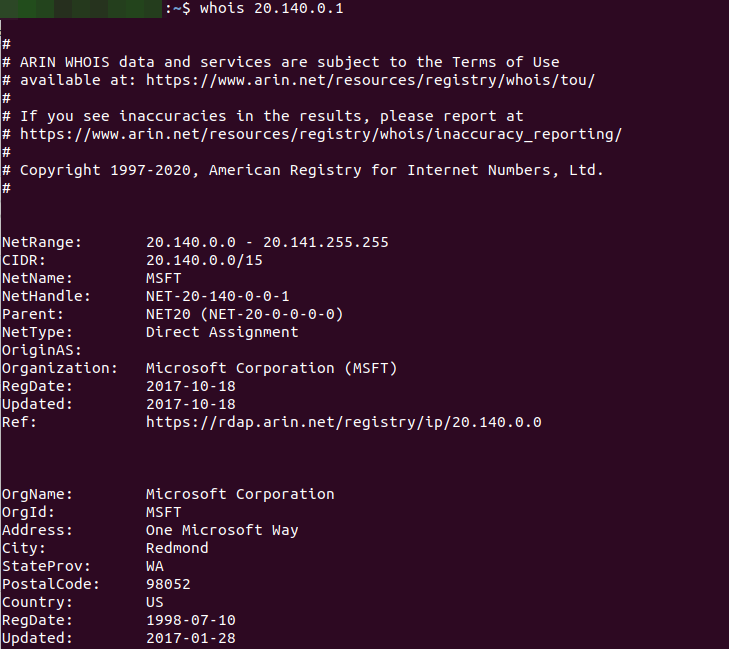
And it seems that Microsoft may now be in perhaps the best position to take stock of the carnage. That’s because sometime on Dec. 14, the software giant took control over a key domain name — avsvmcloud[.]com — that was used by the SolarWinds hackers to communicate with systems compromised by the backdoored Orion product updates.
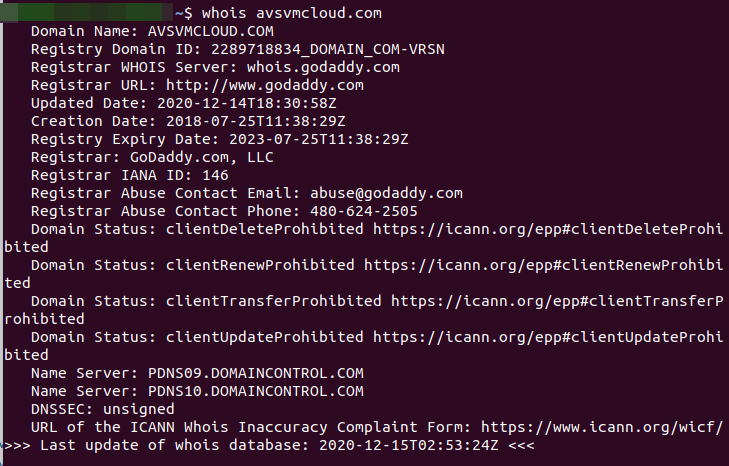
Armed with that access, Microsoft should be able to tell which organizations have IT systems that are still trying to ping the malicious domain. However, because many Internet service providers and affected companies are already blocking systems from accessing that malicious control domain or have disconnected the vulnerable Orion services, Microsoft’s visibility may be somewhat limited.
Microsoft has a long history of working with federal investigators and the U.S. courts to seize control over domains involved in global malware menaces, particularly when those sites are being used primarily to attack Microsoft Windows customers.
Microsoft dodged direct questions about its visibility into the malware control domain, suggesting those queries would be better put to FireEye or GoDaddy (the current domain registrar for the malware control server). But in a response on Twitter, Microsoft spokesperson Jeff Jones seemed to confirm that control of the malicious domain had changed hands.
“We worked closely with FireEye, Microsoft and others to help keep the internet safe and secure,” GoDaddy said in a written statement. “Due to an ongoing investigation and our customer privacy policy, we can’t comment further at this time.”
FireEye declined to answer questions about exactly when it learned of its own intrusion via the Orion compromise, or approximately when attackers first started offloading sensitive tools from FireEye’s network. But the question is an interesting one because its answer may speak to the motivations and priorities of the hackers.
Based on the timeline known so far, the perpetrators of this elaborate hack would have had a fairly good idea back in March which of SolarWinds’ 18,000 Orion customers were worth targeting, and perhaps even in what order.
Alan Paller, director of research for the SANS Institute, a security education and training company based in Maryland, said the attackers likely chose to prioritize their targets based on some calculation of risk versus reward.
Paller said the bad guys probably sought to balance the perceived strategic value of compromising each target with the relative likelihood that exploiting them might result in the entire operation being found out and dismantled.
“The way this probably played out is the guy running the cybercrime team asked his people to build a spreadsheet where they ranked targets by the value of what they could get from each victim,” Paller said. “And then next to that they likely put a score for how good the malware hunters are at the targets, and said let’s first go after the highest priority ones that have a hunter score of less than a certain amount.”
The breach at SolarWinds could well turn into an existential event for the company, depending on how customers react and how SolarWinds is able to weather the lawsuits that will almost certainly ensue.
“The lawsuits are coming, and I hope they have a good general counsel,” said James Lewis, senior vice president at the Center for Strategic and International Studies. “Now that the government is telling people to turn off [the SolarWinds] software, the question is will anyone turn it back on?”
According to its SEC filing, total revenue from the Orion products across all customers — including those who may have had an installation of the Orion products that contained the malicious update — was approximately $343 million, or roughly 45 percent of the firm’s total revenue. SolarWinds’ stock price has fallen 25 percent since news of the breach first broke.
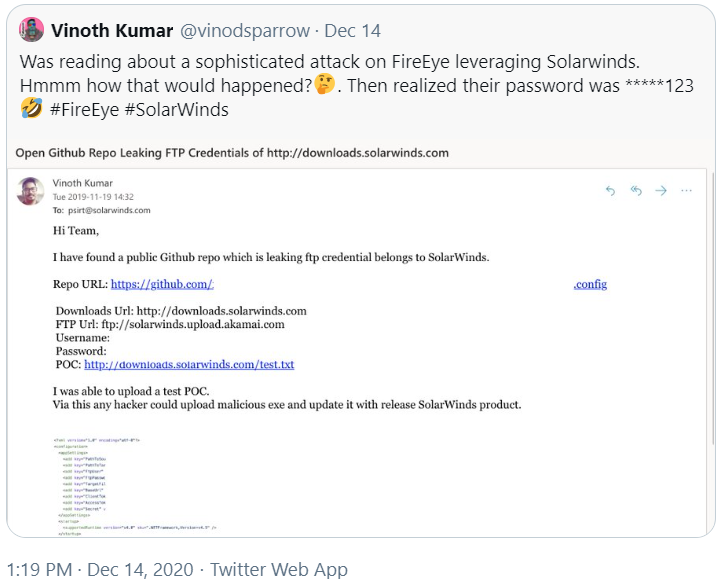
Some of the legal and regulatory fallout may hinge on what SolarWinds knew or should have known about the incident, when, and how it responded. For example, Vinoth Kumar, a cybersecurity “bug hunter” who has earned cash bounties and recognition from multiple companies for reporting security flaws in their products and services, posted on Twitter that he notified SolarWinds in November 2019 that the company’s software download website was protected by a simple password that was published in the clear on SolarWinds’ code repository at Github.
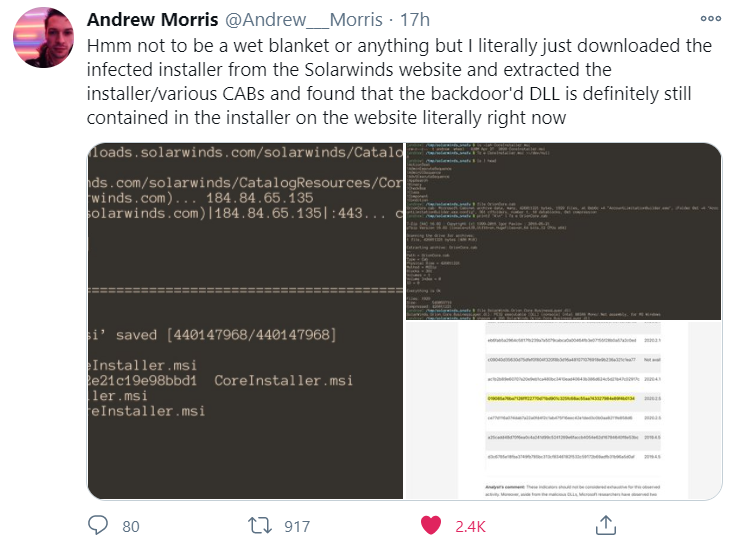
Andrew Morris, founder of the security firm GreyNoise Intelligence, on said that as of Tuesday evening SolarWinds still hadn’t removed the compromised Orion software updates from its distribution server.
Another open question is how or whether the incoming U.S. Congress and presidential administration will react to this apparently broad cybersecurity event. CSIS’s Lewis says he doubts lawmakers will be able to agree on any legislative response, but he said it’s likely the Biden administration will do something.
“It will be a good new focus for DHS, and the administration can issue an executive order that says federal agencies with regulatory authority need to manage these things better,” Lewis said. “But whoever did this couldn’t have picked a better time to cause a problem, because their timing almost guarantees a fumbled U.S. response.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Pornhub Removes All Unverified Content

One of the internet’s most popular purveyors of pornography has removed all unverified content from its website.
Pornhub said it took the step last week in an effort to combat the rising tide of Child Sexual Abuse Material (CSAM) flooding the internet. Unverified uploaders have been banned from posting new content, and downloads have been eliminated.
Currently, only content partners and people within the site’s Model Program can upload content to Pornhub. However, the site plans to implement a verification process in the new year that will allow any user to upload content “upon successful completion of identification protocol.”
Announcing the changes on their website, Pornhub compared their approach to verification with that of other companies with a huge online presence.
“As part of our policy to ban unverified uploaders, we have now also suspended all previously uploaded content that was not created by content partners or members of the Model Program. This means every piece of Pornhub content is from verified uploaders, a requirement that platforms like Facebook, Instagram, TikTok, YouTube, Snapchat and Twitter have yet to institute,” announced Pornhub.
The company said that its efforts to combat the appearance of illegal content on its site had “been effective.”
“Over the last three years, Facebook self-reported 84 million instances of child sexual abuse material. During that same period, the independent, third-party Internet Watch Foundation reported 118 incidents on Pornhub,” stated the site.
“That is still 118 too many, which is why we are committed to taking every necessary action.”
Pornhub closed their announcement by stating that “all social media platforms share the responsibility to combat illegal material.”
The content purge follows the recent creation of Pornhub’s Trusted Flagger Program, an initiative that empowers 40 non-profit organizations to alert the site of content they think may violate Pornhub’s terms of service.
Partner organizations have a direct line to the site’s moderation team, and any content flagged by a Trusted Flagger is disabled immediately.
Pornhub voluntarily partnered with the National Center for Missing & Exploited Children (NCMEC) to report incidents of CSAM that appear on its site. In early 2021, NCMEC will release the total number of CSAM incidents reported on Pornhub.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
US Jails Journalists’ Cyber-Stalker

A cyber-stalker from Arizona who joined up with a neo-Nazi group to harass and threaten journalists, advocates, and other targets has been sentenced to prison.
Johnny Roman Garza admitted to conspiring with other members of the Atomwaffen Division to deliver menacing messages to journalists online and in person, sometimes targeting their homes. The campaign was created to intimidate individuals who had exposed anti-Semitic behavior.
The 21-year-old confessed to affixing a threatening poster to the bedroom window of a prominent Jewish journalist and editor on January 25, 2020. Along with the victim’s name and address, the poster showed a man holding a Molotov cocktail and wearing a skull mask while standing in front of a burning house.
According to court documents, the act was part of a coordinated plot against multiple targets that Garza said was designed to “have them all wake up one morning and find themselves terrorized by targeted propaganda.”
In September, Queen Creek resident Garza pleaded guilty to one count of interfering with federally protected activities because of religion, one count of conspiracy to mail threatening communications, and one count of cyberstalking.
In his plea agreement, Garza admitted to conspiring with other defendants via an encrypted online chat group to identify journalists and advocates that the group could threaten.
The group focused primarily on journalists and advocates who were people of color and/or of the Jewish faith.
Appearing before US District Judge John Coughenour on December 9, Garza said he committed the crimes after failing in with a bad crowd.
According to the Omaha World Herald, Garza told Coughenour that when committing the crimes, he was “in a time of darkness and isolation” that allowed “rebellious and resentful” influences to impact his decisions.
“Very unfortunately, I fell in with the worst crowd you can probably fall in with, a very self-destructive crowd at the least,” said Garza.
Garza’s defense attorney, Seth Apfel, said that since committing his crimes, his client had “not just disavowed the views that he had, but really embraced a new way of being.”
Coughenour sentenced Garza to 16 months in prison and three years of supervised release.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Combat Online Predators Act Clears US House

Legislation to enhance federal criminal penalties for adults convicted of cyber-stalking children has been passed to America’s President Donald Trump for signature.
The Combat Online Predators Act seeks to amend the federal criminal code to increase the maximum prison term for a stalking offense by an additional five years if the victim is under 18 years of age. It also requires the attorney general to create a report detailing best practices for the enforcement of state, local, tribal, and federal stalking laws in the United States.
The bill was first introduced in November 2017. It was passed by the House of Representatives in 2018 with broad bipartisan support and unanimously passed in a modified form by the Senate.
However, time ran out before the House could vote on the altered version of the bill and send it to the president for signature.
The bill was subsequently reintroduced and passed by the Senate last October. Now it is finally with the president after winning the approval of the House of Representatives last week.
Under current law, it is a federal crime for an individual to harass or intimidate another individual, in person or online, in a way that causes them to fear that they may be physically harmed or places them in significant emotional distress.
The maximum criminal penalty for stalking is five years in prison. A ten-year custodial sentence may be imposed if the defendant causes serious physical injury to the victim or uses a dangerous weapon.
If signed into law, the bill would increase the maximum penalties for stalking to 10 years and 15 years, respectively. Adult defendants convicted of stalking a minor could be incarcerated for a total of 15 years.
The bill was inspired by the experience of the Zezzo family of Pennsylvania, whose teenaged daughter was cyber-stalked on social media by the 51-year-old father of one of her friends.
“As families have navigated through the COVID-19 pandemic, children are spending more time online and in front of a web cam,” Tony Zezzo, father of the victim, told Times Leader.
“Individuals who stalk and cyber-stalk our children are taking advantage of these new tools and opportunities to exploit children. This legislation has never been more critical than it is today.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Outpost24 Announces Completion of €19m Funding Round

Cybersecurity assessment provider Outpost24 has announced it has closed a new funding round worth SEK 200m (€19m).
The company said the funding, which was led by asset manager Swedbank Rohur and Nordic equity investment firm Alcur Fonder, will enable it to expand its offering and services worldwide.
This comes amid a growth in demand for cloud based security solutions in the past 12 months, with organizations forced to shift to a remote working model.
Outpost24 aims to help organizations identify, assess and prioritize IT vulnerabilities through risk-based insights. In recent years the Swedish firm, which is owned by Monterro, has grown its operations in Europe and the US with the acquisitions of SecludIT and Pwnie Express.
Peter Larsson, managing partner at Monterro and chairman of the board of Outpost24 commented: “This funding round, done during a global pandemic, is a vote of confidence in our full stack security assessment vision. Having seen what a great technology and team we’ve built, our investors are onboard with our mission to help enterprise companies automate cyber hygiene and reduce risks.”
Martin Henricson, CEO of Outpost24 said: “As malware and phishing attacks continue to make their way through corporate defense, there’s a real need for companies to level up cyber-hygiene through continuous assessment and unified security insights. I’m excited to embark on the next stage of growth for Outpost24 by helping our customers meet their risk reduction goals and achieve greater efficiency.”
Last week, cloud security provider Orca Security announced a $55m Series B fund round to expand its cloud security and compliance capabilities.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Data Leak Exposes Details of Two Million Chinese Communist Party Members

Sensitive data of around two million members of the Communist Party of China (CPC) have been leaked, highlighting their positions in major organizations, including government agencies, throughout the world.
According to reports from The Australian newspaper, featured in the Economic Times, the information includes official records such as party position, birthdate, national ID number and ethnicity. It revealed that members of China’s ruling party hold prominent positions in some of the world’s biggest companies, including in pharmaceutical giants involved in the development of COVID-19 vaccines like Pfizer and financial institutions such as HSBC.
The investigation by The Australian centred around the data leak, which was extracted from a Shanghai server in 2016 by Chinese dissidents.
It noted that CPC members are employed as senior political and government affairs specialists in at least 10 consulates, including the US, UK and Australia, in the eastern Chinese metropolis Shanghai. The paper added that many other members hold positions inside universities and government agencies.
The report emphasized there is no evidence that spying for the Chinese government or other forms of cyber-espionage have taken place.
In her report, The Australian journalist and Sky News host Sharri Markson commented: “What’s amazing about this database is not just that it exposes people who are members of the Communist Party, and who are now living and working all over the world, from Australia to the US to the UK, but it’s amazing because it lifts the lid on how the party operates under President and Chairman Xi Jinping.
“It is also going to embarrass some global companies who appear to have no plan in place to protect their intellectual property from theft, from economic espionage.”
In September, the Cybersecurity and Infrastructure Security Agency (CISA) and the US Department of Justice issued a joint advisory warning US government agencies and private sector companies to be on high alert for cyber-attacks by threat actors affiliated with the Chinese Ministry of State Security (MSS).
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk