Bonus Naked Security Podcast minisode – listen now!
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
A Kosovan hacker, imprisoned in the United States for stealing personal data belonging to US military and government personnel and sending it to the Islamic State of Iraq and the Levant (ISIL), has been granted compassionate release.
Ardit Ferizi was sentenced to 20 years in prison in September 2016 after he confessed to providing material support to a designated foreign terrorist organization and to accessing a protected computer without authorization.
Ferizi’s case made headlines for being the first-ever hacking conviction in the United States’ War on Terror.
The 24-year-old hacker, known online as “Th3Dir3ctorY,” was arrested in Kuala Lumpur, Malaysia, in 2015 at the age of 19 and extradited to the United States in January 2016.
According to court documents, Ferizi admitted that in June 2015 he gained system administrator-level access to a server that hosted the website of an electronics company located in Arizona. The website contained databases with personally identifiable information (PII) belonging to tens of thousands of the company’s customers.
Ferizi searched the databases for PII belonging to US military members and other government personnel, stealing information belonging to approximately 1,300 such individuals. He then passed it on to Junaid Hussain, a now-deceased ISIL recruiter and attack facilitator.
The hacker admitted that he gave the data to Hussain with the understanding that ISIL would use it to “hit them [the United States] hard.”
A document containing the stolen data was published on Twitter on August 11, 2015, by Hussain. Inside the document was the statement, “We are in your emails and computer systems, watching and recording your every move, we have your names and addresses, we are in your emails and social media accounts, we are extracting confidential data and passing on your personal information to the soldiers of the khilafah, who soon with the permission of Allah will strike at your necks in your own lands!”
Last week, federal judge Leonie Brinkema of the Eastern District of Virginia ordered the release of convicted cyber-criminal Ferizi after he submitted a handwritten motion stating that his obesity and asthma made him vulnerable to COVID-19.
Brinkema ordered Ferizi to spend two weeks in quarantine, after which time he will be deported to his native Kosovo, where he will remain on supervised release for 10 years.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Norwegian police have blamed Russian advanced persistent threat (APT) group Fancy Bear for the summer cyber-attack on Norway’s single-chamber parliament, the Storting.
In what was described as “a significant attack” by the parliament’s director, Marianne Andreassen, unauthorized individuals managed to gain access to the email accounts of several elected members of parliament and to some accounts belonging to parliament employees on August 24.
On September 1, the Storting confirmed that a limited number of accounts had been compromised and that varying amounts of data had been downloaded by the attackers. Some of the compromised accounts belonged to members of Norway’s main opposition party, the Labour Party.
Two weeks later, Norway’s foreign minister, Ine Eriksen Soereide, laid the blame for the attack squarely at Russia’s door.
Speaking on October 13, Soereide said: “This is a serious event that hit our most important democratic institution. Based on the information available to the government, it is our assessment that Russia stood behind this activity.”
The attack was reported to Norway’s Police Security Service (PST) by the Storting on September 1, which subsequently launched an investigation.
On December 8, the PST announced that a brute-force attack had been executed to break into user accounts of the Storting’s email system and that “sensitive content has been extracted from some of the affected email accounts.”
Investigators found that the actor tried to “move further into the Storting’s computer systems” but was not successful.
Police concluded that the hit on the Storting was part of a larger campaign nationally and internationally that has been going on since at least 2019.
“The analyses show that it is likely that the operation was carried out by the cyber actor referred to in open sources as APT28 and Fancy Bear,” stated the PST.
“This actor is linked to Russia’s military intelligence service GRU, more specifically their 85th Special Services Center (GTsSS).”
The PST said that the attack confirmed that insecure passwords used for private and business email accounts expose both individuals and the Storting as a parliamentary institution and that two-factor authentication and settings could prevent similar attacks from occurring.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
A California man who admitted hacking into the computer system of Japanese gaming giant Nintendo and leaking proprietary data has been sentenced to three years in prison.
Palmdale resident Ryan S. Hernandez, now aged 21, was still a minor when he and an associate used a phishing technique to steal the credentials of a Nintendo employee in 2016.
The credentials were exploited to access and download confidential files relating to the company’s games and consoles, which were then leaked to the public. Pre-release information about the anticipated Nintendo Switch console was among the data leaked.
In 2017, FBI agents contacted Hernandez, also known as Ryan West and by his online moniker “RyanRocks,” and his parents regarding the hack. Despite promising agents that he would not engage in any further cyber-criminal activity, Hernandez went on to hack into multiple Nintendo servers and steal confidential information about video games, developer tools, and gaming consoles from at least June 2018 to June 2019.
The indiscreet hacker boasted about his crimes on Twitter and Discord, the group-chatting platform that was originally built for gamers. He even created an online chat forum, eponymously named “Ryan’s Underground Hangout,” where he chatted with people about Nintendo products, shared some of the data he had stolen from the company, and highlighted possible vulnerabilities in Nintendo’s computer network.
Hernandez’ activities did not go unnoticed by the FBI, who searched his home in June 2019 and seized circumvention devices used to access pirated video games and software. Agents also seized numerous computers and hard drives, upon which were discovered thousands of confidential files belonging to Nintendo.
Forensic analysis of devices belonging to Hernandez revealed that the teen had used the internet to amass a collection of over 1,000 videos and images depicting minors engaged in sexually explicit conduct. This cache of child sexual abuse material was stored and sorted in a folder directory labeled “Bad Stuff.”
In January 2020, Hernandez pleaded guilty to computer fraud and abuse and to possession of child pornography and agreed to pay $259,323 in restitution to Nintendo. On December 1, Hernandez, who will now be required to register as a sex offender, was sentenced to three years in prison followed by seven years of supervised release.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Just over three-quarters of cybersecurity professionals have said they expect to see an increase in DNS-related security threats over the next few weeks.
In preparation, three in five (59%) have altered their DNS security methods in the run up to the holiday season, according to a new report from the Neustar International Security Council (NISC).
However, 29% have reservations around their ability to respond to DNS attacks, likely attributed to the shifting and complex DNS threat landscape, as some users admitted to having been hit by at least one DNS attack in the past year, including DNS spoofing/cache poisoning (28%), DNS tunneling (16%) and zombie domain attacks (15%).
“Acting as the internet’s address book and backbone of today’s digital services, it’s unsurprising that DNS is an increasingly appealing vector for malicious actors, particularly as more consumers turn to websites during peak online shopping periods,” said Rodney Joffe, chairman of NISC, SVP and fellow, Neustar.
“When successful, DNS attacks can have damaging repercussions to an organization’s online presence, brand and reputation. A domain hijacking attack, for example, can result in hackers taking control of a company’s domain and using it to host malware or launch phishing campaigns that evade spam filters and other reputational protections. In a worst-case scenario, this type of attack can even lead to an organization losing its domain altogether.”
In an email to Infosecurity, Jack Mannino, CEO at nVisium, flagged the threat of DNS tunneling as being a popular exfiltration technique “because DNS is frequently allowed for egress traffic.”
Mannino said: “Understanding your DNS traffic and having visibility into attacks is important because many command and control systems use DNS for this purpose, and attackers can exfiltrate data over the protocol through attacks like SQL injection as well, evading firewalls and filtering appliances.”
During September and October 2020, DDoS (22%) was ranked as the greatest concern for security professionals, followed by system compromise (19%) and ransomware (17%). During this period, organizations have focused most on increasing their ability to respond to vendor or customer impersonation (58%), targeted hacking (54%) and IP address hacking (52%).
Joffe said it was positive that organizations are aware of the severity of DNS attacks, but it is also important that they continue to take proactive steps to protect themselves and their customers against the different threats.
“This should involve regular DNS audits and constant monitoring to ensure a thorough understanding of all DNS traffic and activity,” he said.
“Crucially, DNS data can also provide organizations with timely, actionable and important threat insights, allowing them to not only protect against DNS-related threats, but also mitigate the vast majority of malware, viruses and suspicious content before critical systems are infiltrated.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
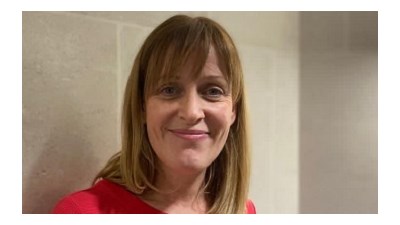
Angela McLaren has been announced as the new assistant commissioner of the City of London Police, with responsibility for economic and cybercrime.
McLaren joins from Police Scotland, where she was the executive lead for organized crime, counter terrorism and intelligence. “I feel privileged to be joining such a talented team of individuals who are already leading the way in preventing and detecting economic and cybercrime, and look forward to working with them to protect the public against these threats,” McLaren said.
“Both fraud and cybercrime present real and increasing threats to communities; this has been particularly evident in the last year, as more people have been confined to their homes, relying on technology to live their lives. Unfortunately, criminals continue to exploit this situation, often targeting the most vulnerable within our society, and this must stop.”
The appointment follows the announcement of the City of London Police being named as the national lead force for cybercrime, which prompted the creation of a new assistant commissioner role to specifically oversee the significantly greater responsibilities the force now holds within the NPCC cybercrime portfolio.
Ian Dyson, City of London police commissioner, said protecting organizations and individuals from fraudulent activity, including cybercrime, is a priority for the City of London Police looking ahead to 2021, “and assistant commissioner McLaren will be instrumental in what I am sure will be a success.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Operational technology (OT) security company Claroty has announced the appointments of Adi Weisz as VP of engineering and Brian Dunphy as VP of product management as the firm looks to continue its growth and innovation in the field of industrial cybersecurity.
Weisz joins Claroty from Lusha and brings 20 years of technology experience to the role, having previously served at firms such as Fornova, Gigya and AfterDownload. He will be in charge of building and maintaining Claroty’s product offerings as well as building and developing a modern, effective and efficient engineering organization.
“I chose to join the elite team of professionals at Claroty to help companies focus on their business without sacrificing security,” said Weisz. “In the world of cybersecurity today, there is no more challenging yet rewarding arena to be in than that of OT infrastructure, where the stakes couldn’t be higher.”
As VP of product management, Dunphy will be responsible for identifying and driving key product improvements. He has 25 years of cybersecurity industry experience and most recently led product management for RSA’s NetWitness Platform.
“OT is the next cyber-battleground as there is no higher value target for threat actors – just imagine the potential impact of a compromised production line, water utility or chemical plant,” Dunphy said. “I joined Claroty because it has been an early pioneer in a space that has an enormous impact on the world. We are not just securing OT systems; we are protecting the lifeblood that powers enterprises’ core functionalities and all of our daily lives.”
Commenting on the appointments, Claroty CEO Yaniv Vardi, said: “We’re thrilled to have Adi and Brian join us here at Claroty. Their enthusiasm for our mission combined with their deep industry expertise are great assets to our company leadership and product development.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
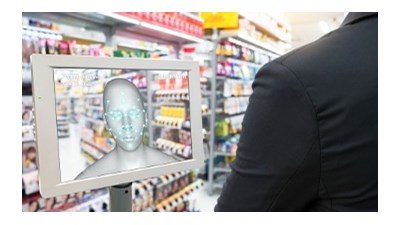
Rights groups have expressed serious concerns over reports that a UK supermarket chain recently completed a trial of controversial facial recognition technology.
The Southern Co-operative, whose stores cover 10 counties across the south of England, revealed the trial in a little noticed update dated two months ago. However, recent media coverage has spurred interest from privacy campaigners.
London-based Privacy International said it has written to the chain requesting urgent assurances over its partnership with UK startup Facewatch. Describing its technology as a cloud-based facial recognition system designed to safeguard businesses against crime, it says the tech “sends you instant alerts when subjects of interest enter your business premises.”
Aside from concerns over whether the Co-op’s use of Facewatch complied with strict data protection and privacy laws, the rights group wants to know whether the trial may have exposed innocent shoppers to unwarranted police scrutiny.
“In October 2020, Privacy International urged authorities in the UK to investigate evidence that Facewatch is offering to transform its crime alerting system into another surveillance network for UK police forces, by offering them the ability to ‘plug-in’ to the system. We are still awaiting responses,” it said.
“We are concerned that such a deployment at Southern Co-op stores – even at trial level – could mean that, in order to purchase essential goods, people might be in effect left with no choice but to submit themselves to facial recognition scans.”
An October blog penned by the supermarket chain’s loss prevention officer, Gareth Lewis, explained that the trial covered a select number of stores that had experienced high levels of crime. Customers were made aware of the trial by “distinctive signage,” and no facial images are stored “unless they have been identified in relation to a crime.” He claimed this made it GDPR-compliant.
Ray Walsh, digital privacy expert at ProPrivacy, raised similar concerns to Privacy International.
“The problem with allowing private businesses to use real-time scanning is that the facial recognition cameras could theoretically become part of constant real-time surveillance leveraged by the police or other government agencies, of the like seen in countries such as China,” he argued.
“These systems mean everyone who ventures out in public is being constantly scanned. It is vital for regulation on the use of facial recognition to offer transparency over how the general public’s data is collected, stored, processed and transported to ensure privacy and data security.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
The National Cyber Security Centre (NCSC) has announced its annual CyberFirst Girls Competition is now open for registrations, with a mission to inspire the next generation of young women to pursue a career in the industry.
Although set-up as an off-shoot of GCHQ to advise and protect UK organizations from cyber-threats, one of the NCSC’s other core goals is to help address chronic cybersecurity skills shortages in the UK.
According to government figures published in March, 48% of businesses have a basic cyber-skills gap. This is defined as those in charge of cybersecurity lacking “the confidence to carry out the kinds of basic tasks laid out in the government-endorsed Cyber Essentials scheme, and are not getting support from external cybersecurity providers.”
What’s more, 25% of firms said that such gaps prevent them from achieving their business goals. The industry is also woefully lacking in diversity: just 15% of the cyber-workforce is female versus 28% in the wider digital sector, the report claimed.
The CyberFirst Girls Competition offers female students in Year 8 in England and Wales, Year 9 in Northern Ireland and S2 in Scotland the opportunity to test their skills in a “fun but challenging” environment.
Teams of four students participate in an online qualifier lasting 10 days, before a regional semi-final round and then the grand final on April 26 2021.
The opening of registrations comes hot on the heels of another initiative from the NCSC: EmPower Cyber Week. Running last week, the event saw scores of schools from around the country participate in virtual presentations designed to show pupils aged 12-13 what careers in cybersecurity look like.
Topics including coding, cryptography and logic were delivered in a highly accessible manner. For example, a “Popstars and Passwords” track taught students to create strong passwords using three random words and their favourite pop stars. A “Python Mind Reader” course used the eponymous programming language to create a simple game.
“The NCSC is committed to creating an environment where cybersecurity can thrive, and we’re pleased that our drives to reach school-aged children are inspiring the next generation of cyber-experts,” said NCSC deputy director for cyber-growth, Chris Ensor.
“The CyberFirst program looks to offer pupils and students as many chances as possible to develop valuable cyber-skills – and we would strongly encourage girls to register for next year’s CyberFirst Girls competition.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
The development of an Internet of Things (IoT) threat hunting framework enabled the discovery of over a billion attacks.
Speaking at Black Hat Europe, TXOne threat researchers Mars Cheng and Patrick Kuo discussed the threat hunting framework they had developed for IoT malware.
They explained that they had created the framework as they had noticed the increase of DDoS attacks, as well as “the weapons including IoT malware and botnets” and Cheng said that, according to research, 20% of attacks in 2020 were related to IoT.
They said the benefits of using an automated threat hunting system include:
They said their IoT hunting service is capable of analyzing 20 terabytes of traffic across IoT and ICS. “We do not need to dedicate a lot of powerful machines to do the processing to help cut down on costs,” Cheng said. It has been able to detect 1.2 billion attacks, including detecting 70 million malicious IP addresses and 15 million suspicious domains, as well as a possible 1.4 million botnet devices.
“If we count back all the way to early 2019, we analyzed 45TB of data,” Cheng said, and they were able to distinguish 70 million suspicious domains. The countries with the most devices tied up in botnets were Vietnam with 1.6 million, China with 1.3 million and India with one million. The most attacked countries were the USA with 316 million attacks, more than double for India with 155 million attacks.
Asked by Infosecurity if they were surprised by the number of attacks they found, the speakers they said they were, as it can typically take one to two days to analyze malware and understand what kind of malware it is and its behaviors. “With so much unknown malware, we need to spend time to analyze,” Cheng said.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk