Online Journals Flagged as Election Threat
Online Journals Flagged as Election Threat

Americans were warned today that online journals may be used to spread lies and sow social discord in the buildup to the 2020 presidential election. 

The warning was issued in a joint public service announcement by the Federal Bureau of Investigation (FBI) and the Cybersecurity and Infrastructure Security Agency (CISA). It came as part of a series of announcements detailing threats that could impact the election’s outcome. 

Voters were warned that foreign actors may share articles containing misinformation in journals that appear to have the backing of academia. CISA and the FBI said that such underhanded tactics had been deployed by America’s foreign adversaries in the past.

“Foreign intelligence services have used online journals, including some with a global reach, to exacerbate disunity and dysfunction in the United States while also misinforming or misleading readers,” stated the warning. 

Other potential sources of disinformation designed to incite division and obfuscate the truth could include websites and social media. 

“Foreign intelligence services have been known to use websites, including pseudo-academic online journals, to disseminate articles with misleading or unsubstantiated information,” states the warning.

“Such sites could be employed during the 2020 election season in an attempt to manipulate public opinion, increase societal divisions, cause widespread confusion, discredit the electoral process, and undermine confidence in US democratic institutions.”

Americans were told that disinformation ranging from unverified claims to outright propaganda could be created and laundered through a variety of online sources to damage or boost the reputations of the candidates. 

The FBI and CISA mooted several topics that might be targeted with misinformation campaigns that exploit online journals. Specifically, they warned Americans to be wary of pseudo-academic journals “making claims of voter suppression, amplifying reports of real or alleged cyberattacks on election infrastructure, asserting voter or ballot fraud, and spreading other information intended to convince the public of the election’s illegitimacy.”

To avoid being duped, American internet users were urged to discount content making claims that cannot be substantiated and to seek out information only from verified and trustworthy sources.

CISA and the FBI asked the public to fact check before sharing any content, and to report suspicious content where possible.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
LinkedIn Password Thief Jailed

LinkedIn Password Thief Jailed

A cyber-criminal who hacked into multiple tech companies and stole 117 million LinkedIn passwords has been sentenced to more than seven years in prison by a US district judge. 

Yevgeniy Alexandrovich Nikulin was found guilty by a jury in July this year of breaching the internal networks of LinkedIn, Dropbox, and the now defunct social networking company Formspring. 

The 32-year-old Russian national exfiltrated the user databases of the companies he compromised, then sold the information on the dark net. 

The malicious hacker compromised all three companies in the spring of 2012, breaking into LinkedIn between March 3 and March 4. He gained access to the company’s internal network by infecting the laptop of an employee with malware that enabled him to exploit the victim’s VPN.

Nikulin stole LinkedIn user data that included millions of usernames, passwords, and emails, then used it to launch spear-phishing attacks against employees at other companies. One company he skewered with this strategy was Dropbox. 

After breaching the account of a Dropbox employee, Nikulin was able to access a folder containing company data between May 14 and July 25, 2012. Court documents state the bad actor stole data on 68 million Dropbox users. 

Using the same ruse, Nikulin was also able to spear the account of an engineer working for Formspring. Between June 12 and June 29, 2012, the cyber-criminal is believed to have accessed the records of 30 million Formspring users.

Nikulin was also found guilty of hacking his way into WordPress.com parent company Automattic, though no evidence of data theft from this company was found. 

Trial documents show that Nikulin was resident in Moscow when he committed these offenses. The information he swiped was advertised for sale on the dark net in 2015 and 2016 by various traders in illegal data. 

The Russian national was arrested while on holiday in Prague in October 2016 as part of an international operation involving the FBI. He was extradited to the United States in 2017. 

On Wednesday, US District Judge William Alsup sentenced Nikulin to 88 months in prison. Alsup said he hoped the sentence would deter others from committing similar crimes.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Technical and Cost Concerns of Passwordless Authentication Bother Security Leaders

Technical and Cost Concerns of Passwordless Authentication Bother Security Leaders

The majority of businesses believe passwordless authentication is a step in the right direction, but are concerned over cost, storage of data and user adoption.

According to research of 750 IT and security professionals LastPass, the concept of reducing password related risks by enabling users to login to devices and applications without the need to type in a password is appealing, as technologies such as biometric authentication, single-sign-on (SSO) and federated identity are adopted instead of traditional passwords.

The research found 85% of respondents agree their organization should look to reduce the number of passwords that individuals use on a daily basis, while 95% of respondents surveyed said there are risks to using passwords which could contribute to threats in their organization, including human factors such as password reuse.

The top benefits of a passwordless authentication model included better security (69%), as well as time (54%) and cost (48%) saved, and ability to access from any location (53%).

However, 43% cited cost, 41% storage of data required and 40% time to migrate as the main challenges to implement passwordless, while 72% think that end users in their organization would prefer to continue using passwords, as it is what they are used to.

“As many organizations transition to a long-term remote work culture, giving your employees the tools and resources to be secure online in their personal lives as well as in the home office is more important now than ever,” said Gerald Beuchelt, CISO at LogMeIn.

Asked if he felt that cost, storage of data and user adoption were significant enough reasons for this to not be adopted, over security, Dan Panesar, director for UK and Ireland at Securonix, said in today’s digital world, most organizations rely on a heavy online presence to drive revenue and profit, so the login experience for these customers is critical.

“Once the users have found what they want to purchase, they want to get through and login quickly, but they also need to know that their data is safe: these users are also employees, so implementing innovative solutions for customers to drive profits should be the same for employees,” he said.

“There are always high profile data breaches involving customer data being leaked or stolen. This not only has an impact financially from a regulatory perspective, but also the reputational damage it can do to the brand. These financial and reputational threats should more than mitigate any challenges or concerns around costs, storage or user adoption.”

Patrick Hunter, sales engineering director for EMEA at One Identity, said that technological advances have now allowed us to truly consider alternatives for the first time, and facial recognition and other biometrics are good as a form of authentication when used in conjunction with a second factor such as a PIN.

“I would never advocate for a single authentication factor for accounts with privileged account access, whether that is a password or a passwordless alternative,” he said. “It goes without saying that all generic privileged accounts need to have their authentication mechanism locked away completely and only accessible with multiple forms of authentication.”

Hunter claimed some organizations are too complex and too large to implement this level of change though, as “they have too many systems, too many applications, too many SaaS services and, my experience shows, they don’t always know all the applications that have been purchased with a credit card in the world of Shadow IT.”

He said: “Organizations that embrace new authentication technology are still pioneers in my opinion, they are the brave souls willing to risk their data and the wrath of their users to use innovative ways to keep the bad guys out: but there will still be passwords in their organizations, no matter what they try.”

Javvad Mallik, security awareness advocate at KnowBe4, said common threats posed by passwords should not warrant a roll out of passwordless authentication, and as an industry “we should be mindful of how we roll it out, and not implement large-scale sudden change; rather take a measured approach, starting perhaps with a small set of applications within the organization, understanding the impact, then moving on to others.”

Likewise, Stuart Sharp, VP of solution engineering at OneLogin, said passwordless isn’t just about improving security, it’s as much about making sure you are offering end users the same seamless, modern experience with authentication that they expect and demand from all their online experiences.

“The best passwordless options don’t require organizations to store additional data but instead leverage biometric authentication options that come with almost all smartphones, laptops and tablets,” Sharp said. “The biometric data is stored on the device, not by the organization, so there is no single target that hackers can go after to harvest fingerprints or face IDs.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
ISF Outlines the Key Skillsets of Modern CISOs

ISF Outlines the Key Skillsets of Modern CISOs

Modern chief information officers (CISOs) must demonstrate agility and the ability to learn new skills as organizations increasingly embark on ambitious digital transformation programs. This is according to the Information Security Forum’s (ISF)’s latest digest, Becoming a Next Generation CISO, which has outlined the key traits security leaders must exhibit in the modern age, in which their roles are becoming ever more crucial.

Following a range of surveys and interviews held with over 40 CISOs, the ISF set out six differentiating characteristics required for individuals in these posts to successfully advance the discipline of information security in today’s increasingly evolving and digitalized world. These are: balancing opportunity with risk, demonstrating leadership, managing incidents and crises, finding their own voice, dealing with regulatory volume and handling technology.

This approach has primarily been brought about by three major external forces, which have reshaped the role of CISOs according to the report. These are firstly the rush to digital technology, which has substantially changed the way organizations operate in regard to working practices and interactions with customers and suppliers.

The second is the overwhelming regulatory burden, with recent legislation such as the EU General Data Protection Regulation (GDPR) making compliance a focal issue in boardrooms.

The third is disruptive events, which have the knock on effect of enforcing change on organizations at high speed. The archetypal example of this is the COVID-19 pandemic this year, which has forced companies to re-orientate around secure remote working practices.

Steve Durbin, managing director at the ISF, commented: “As digital transformation drives organizations to become more agile and responsive, the CISO faces demands to quickly prove their worth as an enabling force, while protecting the business in an increasingly turbulent risk environment. Becoming a next-generation CISO requires an individual to embrace and master new skills and disciplines, making themselves indispensable, future-proof and highly sought after.”

“The CISO is coming under pressure from many different directions. Whether this is external, internal or personal, these forces have combined to create a situation that demands a new approach – one that the next-generation CISO is pioneering. Being a next-generation CISO is an extremely rewarding position that allows an individual to become a pivotal member of their organization, involved in and advising on almost every level. This role will be welcomed almost anywhere as more and more organizations turn their focus to the risks and opportunities of the evolving digital world.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
#DTXNOW: Time to Remove Security from IT

#DTXNOW: Time to Remove Security from IT

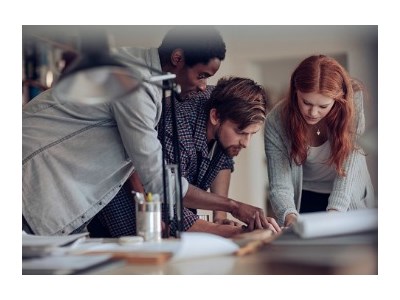
Speaking on a session titled “Is top level security possible on a shoestring budget?” as part of Digital Transformation Expo, security specialists were asked by moderator Jeremy White what their top tips were on what not to do, and how to run security more efficiently.

Asked on what their recommendations were on the one thing businesses should not be doing to operate a cybersecurity system on a shoestring, Simon Honey, cybersecurity and data protection companies advisor at the Institute of Directors, said it is “having people who don’t know what they are doing running the process.” He said he has found this situation over and over again, as IT people think security is about stopping viruses and making better firewalls, “but it is more than that, you’ve got to think about culture, you’ve got to think about security as in the whole culture of the business.”

John Rouffas, CISO of Bink, said it is about being able to “impart what the critical knowledge is with people within the organization, and to supplement that with your knowledge and supplement that together to make it work.” He said the last thing you want is for you or the company to make assumptions for you, as that can cause problems. “Security really is an organism; it grows and needs to be helping the whole time, and it is very much a journey.”

Looking at tips to run security more efficiently, Rouffas said the most important thing is to look at the people you have and leverage what they have and what you’re doing, as they are the people who use these tools on a day-to-day basis, and as there is a chance you’re going to bring in something new, “bring them in together and be inclusive as to where you’re going.”

Honey recommended having a three year road map, and know what you have to do now and in the first few months, first six months, first year, two years and three years “and in every year, review it.”

He said with that in place, even though you may change plans as new ideas and technologies emerge, having a strategy “gives you an idea of where you want to go and how you’re going to do it, and ultimately, how much you should have as a budget each year.”

Earlier in the discussion, Honey said too many businesses believe IT and security are the same, and it is best to address that and look for solutions to support security “which can mostly cost around £10-20,000,” and will not cost more than £50,000.

Discussing the idea of moving the CISO out of IT, Honey said most companies believe that cybersecurity belongs in IT, but it does not, and it should be outside of IT, and in one instance the reporting line had been moved for the CISO to report directly to the chief operating officer. “The CISO should be on par with the CIO, and quite often the CIO is not part of the board, and not there to give advice when things go wrong, while a CISO is called to the board every time they meet, to give an update on security,” he said. This is because a CISO can react quickly to when something happens, and when the CEO asks for a report the CISO can provide this too. “This also means that if a crisis does occur, like a hack, the board are aware of it pretty quickly.”

Rouffas said there is a misunderstanding as to where the CISO needs to fit, and he has seen some cases where the CISO reports to the CTO, and that creates a conflict of interest as “you’re trying to tell the IT people ‘this is how you’re supposed to deploy systems, here are the controls that you need to have and this is what you need to do to make them secure’.” However the CTO will say “I’m not going to let that happen as it will not work anymore.” This causes a situation where you work on something bigger, and get into disagreements.

“Ultimately it [security] needs to be part of the board, and be empowered to be able to react as quickly and responsibly as they possibly can,” Rouffas said.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
#DTXNOW: Managing Uncertainty to Build Lasting Resilience in Security Teams

#DTXNOW: Managing Uncertainty to Build Lasting Resilience in Security Teams

IT and security teams must learn how to navigate to uncertain environments in order to build lasting resilience, according to Jordan Schroeder, deputy MD & managing CISO at Hefestis, speaking during a session at the virtual Digital Transformation EXPO. This concept is especially relevant given the current context: “2020 could easily be called the year of uncertainty,” he noted.

This requires a significant mindset shift within the industry: “Uncertainty can be particularly frustrating because we rely on some sense of certainty to achieve our goals. But we can achieve our goals without needing certainty, and that’s how we build resilience,” observed Schroeder.

The first stage is to abandon the notion of shoulds – a preconception of what is supposed to happen. Security teams should instead base their operations around dealing with new realities, working out the small iterative steps in technologies and practices required.

Schroeder also noted that when new technology is exposed to people, this creates a situation of ‘perfect uncertainty’, due to the unpredictability of human behaviors. It is impossible to even predict what effect controls that are put in place in these technologies will have; for example, people may find ways to get round them or find a way to use controls to do what they want it to do.

How to tackle uncertainties is something that’s become commonplace in other contexts. Schroeder gave the example of children’s birthday parties: instead of trying to plan an outcome, parents instead will put in place a range of ideas that might work and watch how the children interact with them. Those that lead to good outcomes and behaviors will then be encouraged, whereas things that are not successful will be removed and discouraged.

“Resilience is moving forward without being able to map what success is going to look like and letting go of your preconceptions,” Schroeder added.

He applied this principle to IT, and the common scenario of server patching, outlining that admins often delay the introduction of patches when they are available because they are afraid that they may go wrong and subsequently be blamed for the failure by management. Instead of assigning blame when something goes wrong, an approach of testing and learning what does and doesn’t work should become the norm.

In the second part of the session, Schroeder was joined by Lisa Forte, partner at Red Goat Cyber Security, to discuss this concept of resilience further. They firstly highlighted the Maersk NotPetya ransomware attack of 2017, and pondered whether its response should be regarded as the Gold standard for other organizations to follow. While the company was wholly unprepared for the attack, its “hyper-transparency” in releasing the details of the incident and learning how to protect themselves better, should be applauded. Schroeder commented: “They had an interconnectedness in their networks and systems that they didn’t predict, and it’s huge to know that they had this vulnerability.”

Forte added: “You proceed with a course of action, but you have to have the confidence and the flexibility to say this isn’t working, we’ve got to quickly think on our feet, and we’ve got to change it.”

They went on to analyze how organizations should handle the issue of insider threats. Rather than the blaming ‘bad apples’ as is often the case, companies should take on a much more nuanced overview of situation. Schroeder noted: “For a lot of people, there errors are a result of something else within an organization – from management, their environment, the tasks they’re doing, their supervisors, the culture of the company – all of these things can contribute to the actions of the end user.”

Forte added: “If you’ve got an insider threat that’s manifested, it’s the end symptom of a chronic disease that’s in your organization.”

Creating a culture of flagging suspicious behaviors amongst staff within organizations is therefore a critical aspect of preventing insider threats. However, this is rarely the case. Forte highlighted research she worked on last year showed that there would invariably be no reporting of senior members of staff, regardless of how suspicious their behavior is.

To address this issue, an environment in which all staff are empowered to raise issues, regardless of their place within a company’s hierarchy. Schroeder said for this to happen “the senior management needs to very explicit that this is OK, that they are open to that feedback.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Experts Warn of $15m Global BEC Campaign

Experts Warn of $15m Global BEC Campaign

Security experts have discovered a major new Business Email Compromise (BEC) campaign that has already stolen over $15 million from a possible 150 organizations.

Israeli incident response specialist Mitiga was first called in after a multimillion-dollar transaction went awry, according to head of research, Andrey Shomer.

It appears that a cyber-criminal was monitoring email communications between a corporate buyer and seller, and at the last minute, stepped in to impersonate the seller, sending over new wire payment instructions.

“Upon investigation, Mitiga’s incident response team identified rogue domains through which the threat actor’s emails were sent. These domains were similar to the buyer’s and seller’s own domains, but with minor changes which were difficult to notice. For example, if the original domain was ‘buyer.com,’ the rogue domain was ‘buyerr.com’,” Shomer explained.

“All the malicious domains utilized in this BEC attack were registered through a GoDaddy-owned domain registrar called Wild West Domains.”

The attackers linked Office 365 email accounts to these domains to add legitimacy to their communications and fly under the radar of email security filters.

They achieved an initial foothold into a victim organization by sending phishing emails to senior executives. Once an account was hijacked, they would set up a forwarding rule to automatically send any emails to their own accounts.

“This provided the threat actor with full visibility of the transaction and allowed for the introduction of the fake domain at just the right moment, i.e., when the wire transfer details were provided,” said Shomer.

“The threat actor then used filtering rules to discreetly move messages originating from certain email addresses from the inbox folder into a concealed folder. This was done to hide unwanted communication from the actual mailbox owner, for example, emails expressing concern from the legitimate parties — thereby extending the time to discovery of the attack in order to complete obfuscation of the wire transfer.”

All the 150 domains discovered in this campaign are registered with Wild West Domains and ape legitimate businesses. They’re each connected to one of 15 Office 365 accounts.

BEC cost global organizations $1.8 billion in 2019, over half the $3.5 billion total for cybercrime losses, according to the FBI.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Twitter Shutters 130 Iranian Accounts Trying to Disrupt Presidential Debate

Twitter Shutters 130 Iranian Accounts Trying to Disrupt Presidential Debate

Twitter has shut down over 100 fake Iranian accounts it said were focused on “disrupting” online chatter about the first Presidential debate on Tuesday night.

In a series of tweets, the social media site claimed it was tipped off by the FBI about the 130 likely state-backed accounts.

“We identified these accounts quickly, removed them from Twitter, and shared full details with our peers, as standard. They had very low engagement and did not make an impact on the public conversation. Our capacity and speed continue to grow, and we’ll remain vigilant” it continued.

“As standard, the accounts and their content will be published in full once our investigation is complete. We’re providing this notice to keep people updated in real time about our actions. We wish to thank the FBI for their assistance.”

Ironically, the accounts themselves didn’t need to do much to disrupt what was already a chaotic spectacle. The debate itself has been widely criticized as the worst in living memory, thanks in a large part to near-continuous hectoring and interruptions from the President himself.

This is by no means the first time Twitter has been forced to take action to suspend coordinated activity from accounts originating in Iran. In June last year it took down nearly 5000 state-backed accounts, for example.

The social network has also been stepping up its policing of content ahead of the US elections in November, mindful of the potential backlash it faces if the platform is used to spread disinformation or give one side an unfair advantage.

Last month it announced new measures designed to improve the security of accounts belonging to lawmakers, candidates and others.

It has also come in for criticism from Trump himself after the President tweeted several times to falsely claim mail voting would be “substantially fraudulent,” leading  Twitter to place warning labels on his content.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Swatch Group Hit by Likely Ransomware Attack

Swatch Group Hit by Likely Ransomware Attack

The world’s largest watchmaker, Swatch Group, has admitted it suffered a cyber-attack over the weekend which forced the shut-down of IT systems.

“Swatch Group confirms that it has identified clear signs of a developing cyber-attack on some of its IT systems during the weekend,” a brief statement confirmed.

“For security reasons, the group immediately took action and shut down precautionary some of its IT systems, which affected some operations. The situation will return to normal as soon as possible.”

Given the extreme action that the firm’s IT department was forced to take and the fact that it disrupted some operations in doing so, ransomware would seem to be the prime candidate.

The Swiss-headquartered multi-national is home to 18 individual brands including the eponymous Swatch, launched in the 1980s, and major names such as Tissot, Omega and Longines. It made over $2 billion in sales in the first half of 2020, making it an attractive potential target for ransomware attackers.

Dean Ferrando, lead systems engineer EMEA at Tripwire, argued that it’s encouraging the watchmaker at least managed to detect the attack early on and took action to limit its impact.

“Malware doesn’t just suddenly appear on systems. It has to get there through exploited vulnerabilities, phishing, or other means. While we tend to focus on the malware/ransomware itself, the best way to avoid becoming a victim is to prevent the infection in the first place,” he continued.

“The best way to prevent ransomware infections is to address the infection vectors by patching vulnerabilities, ensuring systems are configured securely, and preventing phishing. When these preventive foundational controls fail, there needs to be a continuous monitoring tool in place to detect the signs of a compromise.”

The incident came in the same week that one of America’s largest healthcare providers, UHS, and one of the world’s biggest shipping firms, CMA CGM, admitted they were hit by separate ransomware attacks.

Unlike Swatch Group, these firms appeared to fare less well in spotting the attack. UHS was forced to down its entire network, causing widespread disruption for patients, for example.

In a separate report this week, Microsoft warned that ransomware groups are now making wide sweeps of the internet looking for vulnerable entry points in organizations to attack. Some raids take just 45 minutes from initial compromise to ransom, it claimed.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk