Cyber-Attack Grounds Flights in Alaska
Cyber-Attack Grounds Flights in Alaska

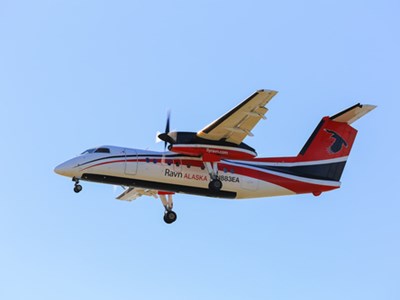
RavnAir Group was forced to ground flights on Saturday following a cyber-attack on the Alaskan company’s computer network.

In a statement released on Saturday morning, RavnAir wrote: “On Friday, December 20th, RavnAir Group experienced a malicious cyber-attack on our company’s IT network.”

The nature of the attack was not disclosed; however, the company did reveal that threat actors specifically targeted the small airline’s turboprop-powered regional airliner the De Havilland Canada DHC-8 aircraft, commonly known as the Dash 8.

As a result of the incident, the airline had to disconnect its entire Dash 8 maintenance system and the back-up system.

All RavnAir Alaska Dash 8 flights that were scheduled to take place on Saturday, December 21, a crucial day of travel in the busy holiday season, were affected. 

PenAir flights and RavnAir Connect flights were unaffected by the incident, as they were able to run on back-up systems.

RavnAir wrote: “While we continue to work with the FBI, other authorities, and a cybersecurity company to restore affected systems, we are proactively cancelling all RavnAir Alaska Dash 8 flights until 12 noon today, and we expect to experience other schedule cancellations and delays within the RavnAir Alaska (Dash 8 Aircraft) network throughout the rest of the day because the cyber-attack forced us to disconnect our Dash 8 maintenance system and its back-up.”

According to news site WKRN, RavnAir spokesperson Debbie Reinwand said that 260 passengers were affected by the malicious cyber-attack. Six flights were cancelled, including the 1:30 p.m. flight from Unalaska to Anchorage.  

Disappointed customer Dennis Ede, who was due to take that 1:30 p.m. flight, told KUCB radio: “I’m not happy about it. If I can’t get out today, I’ll try to get out tomorrow. I’m trying to get home to Seattle to see my family for Christmas.”

Two further flights were cancelled on Saturday due to adverse weather conditions.

“We will be trying to add flights where we can over the next two days,” wrote RavnAir in a statement released at 1 p.m. Sunday, December 22.

“We have, where possible, re-booked passengers on other flights.”

RavnAir Group serves 100 different communities in Alaska from its headquarters in Anchorage. Many of the communities who fly with RavnAir are inaccessible by road.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Citrix Vulnerability Puts 80K Companies at Risk

Citrix Vulnerability Puts 80K Companies at Risk

A critical flaw has been discovered in two Citrix products, placing 80,000 companies in 158 countries at risk. 

The easily exploitable vulnerability could allow attackers to obtain direct access to a company’s local network and to access a company’s credentials. 

It could also be used to launch denial of service and phishing attacks and to implant malware that could lead to cryptocurrency mining. 

Positive Technologies expert Mikhail Klyuchnikov found the vulnerability in Citrix Application Delivery Controller (formerly known as NetScaler ADC) and in Citrix Gateway (formerly known as NetScaler Gateway).

This vulnerability affects all supported versions of the products, and all supported platforms, including Citrix ADC and Citrix Gateway 13.0, Citrix ADC and NetScaler Gateway 12.1, Citrix ADC and NetScaler Gateway 12.0, Citrix ADC and NetScaler Gateway 11.1, and also Citrix NetScaler ADC and NetScaler Gateway 10.5.

What makes the weakness especially dangerous is that it can be used to launch an attack that does not require access to any accounts, meaning it can be mounted by any external attacker.

Depending on the specific configuration, Citrix applications can be used for connecting to workstations and critical business systems (including ERP). In almost every case, Citrix applications are accessible on the company network perimeter, and are therefore the first to be attacked. 

This newly unearthed vulnerability allows any unauthorized attacker to not only access published applications, but also attack other resources of the company’s internal network from the Citrix server. 

Citrix is notifying customers and channel partners about this potential security issue, for which a fix is still forthcoming. 

The company has urged customers to upgrade all of their vulnerable appliances to a fixed version of the appliance firmware as soon as it is released. It has also set up an alert system, which customers can subscribe to so that they will learn as quickly as possible when a fix has been found.

Dmitry Serebryannikov, director of the security audit department at Positive Technologies, said: “Citrix applications are widely used in corporate networks. This includes their use for providing terminal access of employees to internal company applications from any device via the Internet. 

“Considering the high risk brought by the discovered vulnerability, and how widespread Citrix software is in the business community, we recommend information security professionals take immediate steps to mitigate the threat.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Canadian Banks Spoofed in 2-Year Phishing Attack

Canadian Banks Spoofed in 2-Year Phishing Attack

Researchers have unearthed a two-year phishing campaign targeting bank customers in Canada. 

Fourteen banks, including CIBC, TD Canada Trust, Scotiabank, and the Royal Bank of Canada (RBC) were spoofed in a large-scale operation that involved multiple look-alike domains. 

The attack starts by sending legitimate-looking emails containing a PDF attachment. The attachment uses what appears to be an official bank logo, as well as an authorization code.

Victims are told that they need to renew their digital certificate so that they can continue to access online banking. When the victim clicks on any of the URLs that appear in the attached document, they are led to a phishing page asking them to enter their banking credentials.

The intricate scam was uncovered by researchers at Check Point Research, who wrote: “Looking into the detected artifacts revealed an ongoing phishing attack that has been going after customers of Canadian banks for at least two years. 

“By sending highly convincing emails to their targets, constantly registering look-alike domains for popular banking services in Canada and crafting tailor-made documents, the attackers behind this were able to run a large-scale operation and remain under the radar for a long time.”

In the case of RBC, although the phishing website looks identical to the bank’s genuine RBC express login page, the attackers actually invested little time in constructing the deceptive replica. 

“They simply took a screenshot of the official website and added invisible text boxes on top of the input fields to harvest the victim’s credentials,” wrote researchers.

Linguistic clues led the researchers to discover the longevity of the scammers’ cruel charade.

Researchers wrote: “There were multiple variants of the PDF attachments, with slight differences between them. However, some of the textual instructions they contained were repetitive, used unique phrasing and appeared in more than one document. 

“This allowed us to hunt for more samples and find related PDFs dating back to 2017.”

The phishing website that appeared in the PDF attachments resolved to a Ukrainian IP address, which researchers found was hosting more domains impersonating RBC in addition to other banks.

Commenting on the scam, senior security strategist at Synopsys Jonathan Knudesn said he felt it was time users wised up.

“Users should understand the capabilities of phishers; they should know that anyone can construct a web site that looks just like the real thing, and anyone can get a legitimate certificate for a fake web site.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Londoner Escapes Jail Time After Blackmailing Apple

Londoner Escapes Jail Time After Blackmailing Apple

A Londoner who blackmailed Apple threatening to factory reset hundreds of millions of iCloud accounts has been sentenced at Southwark Crown Court.

Kerem Albayrak, 22, from North London, demanded that the tech giant give him $75,000 in crypto-currency or a thousand $100 iTunes gift cards in return for deleting what turned out to be a non-existent database of 319 million ‘accounts.’

In March 2017, he emailed Apple Security with the threat, subsequently sending the team a link to a video of himself accessing two seemingly random iCloud accounts.

It turned out that those accounts and others he had access to were from previously compromised third-party services that were mainly inactive, according to the National Crime Agency (NCA).

Apple contacted the NCA following its receipt of the blackmail demand and officers swooped on Albayrak’s house on March 28, seizing his smartphone, computer and hard drive. After examining his phone records they linked him to a hacker group known as “Turkish Crime Family.”

He pleaded guilty to two counts of unauthorized acts with intent to impair the operation of or prevent/hinder access to a computer, and one count of blackmail.

However, Albayrak escaped jail time, after the court handed down a two-year suspended sentence, 300 hours of unpaid work and a six-month electronic curfew.

“Albayrak wrongly believed he could escape justice after hacking in to two accounts and attempting to blackmail a large multi-national corporation. During the investigation, it became clear that he was seeking fame and fortune. But cyber-crime doesn’t pay,” argued NCA senior investigating officer, Anna Smith.

“The NCA is committed to bringing cyber-criminals to justice. It is imperative victims report such compromises as soon as possible and retain all evidence.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Twitter Bins Thousands of State-Backed Saudi Accounts

Twitter Bins Thousands of State-Backed Saudi Accounts

Twitter has been forced to suspend thousands of accounts linked to state-backed campaigns driven by Saudi Arabia and designed to influence public opinion, it has revealed.

The social networking site claimed in a new blog post on Friday that 5929 accounts had been removed for “violating our platform manipulation policies.”

“These accounts represent the core portion of a larger network of more than 88,000 accounts engaged in spammy behavior across a wide range of topics. We have permanently suspended all of these accounts from the service,” Twitter said.

“In order to protect the privacy of potentially compromised accounts repurposed to engage in platform manipulation, and in response to researcher feedback requesting that we pre-filter unrelated spam, we have not disclosed data for all 88,000 accounts.”

By liking, retweeting and replying to posts, these inauthentic and hijacked accounts apparently amplified messages favorable to the Saudis.

Twitter claimed the coordinated activity could be traced back to a Saudi social media marketing company known as Smaat.

“Our in-house technical indicators show that Smaat appears to have created, purchased, and/or managed these accounts on behalf of — but not necessarily with the knowledge of — their clients,” it explained. “We have permanently suspended Smaat’s access to our service as a result, as well as the Twitter accounts of Smaat’s senior executives. Smaat managed a range of Twitter accounts for high-profile individuals, as well as many government departments in Saudi Arabia.”

Those Smaat employees appear to have used automated third-party tools to amplify non-political content in large volumes; a tactic apparently designed to disguise the more important political content from moderators.

Twitter has been busy this year removing state-backed attempts to manipulate public opinion for geopolitical advantage. It June it shut down 5000 Iranian and Russian accounts accused of doing so, and in August it was the turn of China, which had 1000 accounts suspended for spreading propaganda about Hong Kong.

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk

Zynga Breach Hit 173 Million Accounts

Zynga Breach Hit 173 Million Accounts

Nearly 173 million usernames and passwords were compromised when a leading gaming developer was breached in September, it has emerged.

Zynga burst on the gaming scene when its Farmville title became a hit a decade ago. It followed this success with Words with Friends, a hugely popular Scrabble-like word game it acquired.

Although Zynga acknowledged the breach at the end of September, several weeks after hackers struck, notification site HaveIBeenPwned now has the official figure on how many accounts were affected.

It claimed in an update late last week that a total of 172.9 million unique email addresses, along with usernames and passwords, were compromised in the attack. On the plus side, passwords were stored as salted SHA-1 hashes, which makes them much harder to monetize.

News of the breach went public at the end of September when notorious cyber-criminal “Gnosticplayers” claimed to have obtained data on over 218 million users.

At the time, Zynga responded by urging users not to share passwords across multiple accounts, and to ensure they create “a unique and strong” credential for all of their online accounts.

“Cyber-attacks are one of the unfortunate realities of doing business today. We recently discovered that certain player account information may have been illegally accessed by outside hackers,” it said at the time.

“We understand that account information for certain players of certain Zynga games may have been accessed. As a precaution, we have taken steps to protect certain players’ accounts from invalid logins, including but not limited to where we believe that passwords may have been accessed.”

Tim Dunton, MD of Nimbus Hosting, argued that social gaming customers are prime targets for data theft.

“All online game organizations need to ensure cybersecurity measures are a top priority in their company culture, to avoid this kind of attack happening in the future,” he added.

“They need to focus on adopting safe, modern and frequently updated IT servers, which are immune to leaking information, even to the most advanced of criminal cyber-specialists.”

Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk