Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Author: admin
Twitter Fixes Bug that Enabled Takeover of Android App Accounts
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Podcast: What We’ve Learned from the Year of the Breach
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Wawa Stores Plagued by Malware Since March

Payment processing systems at Wawa, the American chain of convenience and fuel stores, have been harboring malware that steals credit card information for nine months.
In an open letter published online yesterday, Wawa CEO Chris Gheysens announced that the malware had potentially been operating at all of Wawa’s 842 locations across Pennsylvania, New Jersey, Delaware, Maryland, Virginia, Washington, DC, and Florida since March.
“Our information security team discovered malware on Wawa payment processing servers on December 10, 2019, and contained it by December 12, 2019,” wrote Gheysens.
“This malware affected customer payment card information used at potentially all Wawa locations beginning at different points in time after March 4, 2019, and until it was contained.”
By April 22, the malware is thought to have spread to most Wawa stores.
An investigation launched by Wawa into the incident discovered that payment card information, including debit and credit card numbers, expiration dates, and cardholder names, had been exposed as a result of the long-running cyber-attack. ATM cash machines in Wawa stores were not impacted.
In a statement released to the press yesterday, Wawa said that it “is not aware of any unauthorized use of any payment card information as a result of this incident.”
Wawa has said it took “immediate steps after discovering this malware and believes it no longer poses a risk to customers.” However, no details have been revealed as to what type of malware was used in the prolonged card-skimming attack or how it gained a foothold in Wawa’s payment processing systems.
Gheysens apologized for the breach, and assured all customers impacted that they “will not be responsible for fraudulent charges related to this incident.”
Jonathan Deveaux, head of enterprise data protection at comforte AG, commented: “Details are unclear regarding the type of malware installed on the Wawa payment processing servers, however, if the payment card data was protected in real-time with security tokenization, exfiltration of data from Wawa databases would have contained worthless tokens for the bad actors.
“Instead, when data is left in its clear-text form, credit and debit card numbers are exposed, which can put millions of payment card holders in a bad position.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Malicious Email Exploits Greta Thunberg, Christmas, and Children

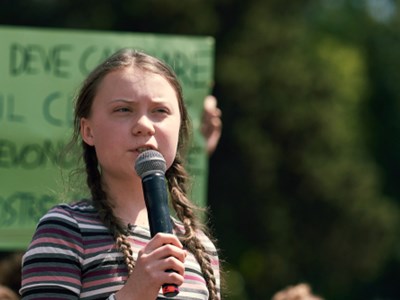
A malicious email campaign that exploits the notoriety of youthful Swedish climate crisis activist Greta Thunberg has been discovered by multiple research teams.
Threat actors constructed an email that appears to invite the recipient to participate in a demonstration being held to protest the lack of government action being taken to protect the natural environment.
The email purports to be from environmental activist Greta Thunberg. In a bid to appear more authentic, the sign-off references a genuine accolade recently awarded to Thunberg—being named Time Person of the Year 2019.
The email states that the time and location of the non-existent demonstration are included in a Microsoft Word document “Support Greta Thunberg.doc,” which is attached to the email. When the victim opens the document, the Emotet malware is installed on their computer.
Emotet is a banking Trojan that has been around since 2014 and has recently made a significant comeback. In the 2019 Q3 Threat Report by Proofpoint, researchers found that Emotet accounted for nearly 12% of all malicious emails in that quarter.
As if exploiting the positive actions of a teenager and public concern over the future of the planet wasn’t enough, the emotionally manipulative scammers stooped even lower by throwing Christmas and children into the mix.
The content of the malicious email reads: “Merry Christmas. You can spend Christmas Eve looking for gifts for children. They will tell you Thank you only that day. But the children will thank you all their lives if you come out for the biggest demonstration in protest against the inaction of the government in connection with the climate crisis.”
Proofpoint researchers who detected this festive incarnation of Emotet wrote: “This campaign serves as a reminder that attackers won’t hesitate to target people’s best intentions during this holiday season.”
Sickeningly, the threat actors appeared to be specifically targeting .edu domains used by students.
“We saw more .edu domains attacked than domains associated with any specific country,” wrote Proofpoint researchers.
Versions of the same malicious email have been doing the rounds in a variety of languages, including Spanish, Italian, French, and Polish.
The one positive takeaway is that the threat actors’ topic of choice signals growing global awareness of Thunberg and the issues for which she advocates.
Proofpoint researchers noted that the campaign “serves as a mark of how significant environmental awareness has become and how well-known Greta Thunberg is globally.”
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
100% Rise in Number of UK Businesses Paying Hacking Ransoms

New research into the attitudes and beliefs of cybersecurity professionals has identified a sharp rise in the number of businesses paying up when stung by a ransomware attack.
The 2019 Global Security Attitude Survey Report by California cybersecurity technology company CrowdStrike shows that the number of global organizations paying ransoms from supply-chain attacks has more than doubled from 14 to 39 percent in the past year.
In the UK, over the same time period, the number of businesses coughing up their money after being held to ransom by threat actors has increased by 100 percent from 14 percent to 28 percent.
On a more positive note, it takes UK organizations on average 39 hours to detect an adversary, versus a sluggish global average of 120 hours.
Over three-quarters (77 percent) of survey respondents admitted that their organization had experienced a supply-chain attack at least once at some point in time, up from 66 percent in 2018. However, compared to last year, more businesses said that they were prepared for such an incident.
Over half (52 percent) of those hit by a software supply-chain attack in 2019 had a comprehensive strategy in place at the time, compared to only just over a third (34 percent) 12 months ago.
“Reacting with speed to next-generation, persistent and pervasive threats requires the power of the cloud and crowdsourced data on the real threats facing organizations, whether they are malicious files or from file-less behaviors,” said John Titmus, senior director, sales & solution engineering, EMEA region, CrowdStrike.
“The solution to these threats lies within the power of the cloud and AI to leverage vast data sets to spot indicators of attack before those attacks break out and become breaches. Then organizations react at the speed required to beat organized cybercriminals and nation-state adversaries.”
The 2019 Global Security Attitude Survey Report is based on responses from 1,900 senior IT decisionmakers and professionals from across the US, Canada, UK, Mexico, Middle East, Australia, Germany, Japan, France, India, and Singapore, working in a wide range of industries. Responses were recorded in the fall of 2019.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
UK Police in the Dock as Device Losses Soar 150%

UK police officers and staff reported on average four lost or stolen devices every day over the most recent financial year, according to newly released data.
Think tank Parliament Street received Freedom of Information (FOI) requests from 22 forces across the country to better understand their risk exposure from mobiles, tablets, laptops, radios, USBs and other devices.
In total, 2600 of these devices were reported lost or stolen over the past three financial years, with around half (1360) reported in the financial year 2018-19.
This amounts to an increase in lost/stolen devices of 150% from the 544 reported missing in 2016-17.
The worst offender was West Midlands Police, which reported 1012 missing devices over the three-year period. This included 16 laptops, 112 mobile phones and 884 police radios, 494 of which went missing last year.
There was a big drop-off before second-placed Staffordshire Police, which reported 277 lost or stolen devices, and third-placed Greater Manchester Police (225).
Those which saw the biggest increase in missing equipment between 2016 and 2019 were Gwent Police, which reported a 2500% jump, Norfolk and Suffolk Constabulary (1,500%) and Durham (200%).
Absolute Software VP EMEA, Andy Harcup, argued that most of these devices would have contained sensitive data on police investigations, including confidential information about criminals, suspects and victims.
“Everyone recognizes the loss of laptops and mobiles in the line of duty is inevitable, so it’s vital that forces have the necessary systems in place to track and freeze equipment when it falls into the wrong hands,” he added.
“This approach can help improve cybersecurity standards, protect the privacy of individuals and prevent criminals and opportunistic thieves from misusing police devices and stealing data.”
It’s not just the police that are exposed to cyber-risk related to device loss. UK government workers reported over 500 lost or stolen devices over the past year, while at the Ministry of Defence, missing device reports soared 300% over the past two years.
It’s unclear whether the majority of devices reported lost or stolen by the police were password protected, encrypted, and/or fitted with device wipe capabilities, according to best practices.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Data Leak Exposes 267 Million Facebook Users

A database of 267 million Facebook user IDs, phone numbers, and names was left exposed online for a fortnight thanks to another cloud misconfiguration, according to researchers.
The trove was likely to have been the result of an illegal scraping operation carried out by cyber-criminals, according to consultant Bob Diachenko and researchers at Comparitech.
“One possibility is that the data was stolen from Facebook’s developer API before the company restricted access to phone numbers in 2018. Facebook’s API is used by app developers to add social context to their applications by accessing users’ profiles, friends list, groups, photos, and event data. Phone numbers were available to third-party developers prior to 2018,” explained Comparitech’s Paul Bischoff.
“Diachenko says Facebook’s API could also have a security hole that would allow criminals to access user IDs and phone numbers even after access was restricted. Another possibility is that the data was stolen without using the Facebook API at all, and instead scraped from publicly visible profile pages.”
The researchers warned that such a large database of sensitive information could be used in major spam, phishing and smishing campaigns.
The database itself was first indexed on December 4, with the data posted on a hacker forum eight days later. Diachenko discovered it on December 14 and notified the ISP managing the IP address, and five days later it was made unavailable.
The original leak came about because of a misconfigured Elasticsearch cluster.
This is just the latest in a long line of data leaks stemming from unsecured cloud databases. In November personal data on over one billion individuals harvested by data enrichment companies was found exposed.
Then in December, over one billion email-password “combos” were found in a similar way by Diachenko. They’re thought to have been stolen or bought by hackers.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Court’s Opinion Good News for EU-US Data Flows

An EU court ruling yesterday has raised questions over the validity of the Privacy Shield data sharing framework between Europe and the US, although it confirmed the legality of standard contractual clauses (SCCs), with caveats.
The opinion of advocate general (AG) of the EU Court of Justice, Henrik Saugmandsgaard Øe, stems from the infamous Facebook-Max Schrems case in which a complaint by the latter claimed that transfer of his data from the EU to the US by the social network infringed his privacy rights.
That led to the end of the Safe Harbor data sharing agreement between the EU and US in 2015, because the latter’s bulk surveillance programs, as revealed by Edward Snowden, were considered to imperil Europeans’ privacy rights without providing any adequate cause of redress.
The new opinion issued by the advocate general indicates the EU still has concerns over Safe Harbor’s successor, Privacy Shield.
“According to the advocate general, the resolution of the dispute in the main proceedings does not require the court to rule on the validity of the ‘privacy shield’ decision, since that dispute concerns only the validity of Decision 2010/87,” a statement from the Court of Justice noted.
“Nevertheless, the advocate general sets out, in the alternative, the reasons that lead him to question the validity of the ‘privacy shield’ decision in the light of the right to respect for private life and the right to an effective remedy.”
However, SCCs are still a valid and legal way to transfer data to and from a “third country” (i.e. one outside the EU), despite the US surveillance regime, the opinion found.
The caveat is that data protection authorities in the trading bloc must keep an eye on the conditions within these third countries.
There is an obligation on them “to suspend or prohibit a transfer when, because of a conflict between the obligations arising under the standard clauses and those imposed by the law of the third country of destination, those clauses cannot be complied with.”
Overall, this is good for business and will ease fears about data flows post-Brexit as the UK will effectively become a third country at that time, according to experts.
“The advocate general’s opinion that the EU SCCs remain valid will be welcomed by business on both sides of the Atlantic, as the SCCs are one of the key mechanisms that underpin transfers of personal data to countries outside of the EU, including to the US,” said Bridget Treacy, partner at law firm Hunton Andrews Kurth.
“Despite the continuing validity of the SCCs, the AG points out that businesses that rely on the clauses still need to assess whether the recipient can comply with the clauses in relation to each particular transfer, and suspend transfers when that is not the case. Furthermore, EU data protection supervisory authorities have the power to suspend data transfers pursuant to the SCCs when an adequate level of protection for personal data cannot be provided in light of local laws and practices in the recipient country.”
The AG’s decision is not legally binding, but the European Court of Justice, which is hearing the case next year, usually follows the same thinking.
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk
Twitter trolls attack epileptics with seizure-inducing images
Premium Domain Names – transcom.uk
Transcom ISP – The UK’s Best Business ISP
DoubleCheck any website at doublecheck.uk